
BIDO
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
android-securityeducationmachine-learning+3
2
whatishope/bidoImage-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 cossas/certitude
CERTITUDE - A python package to classify URLs as malicious or benign
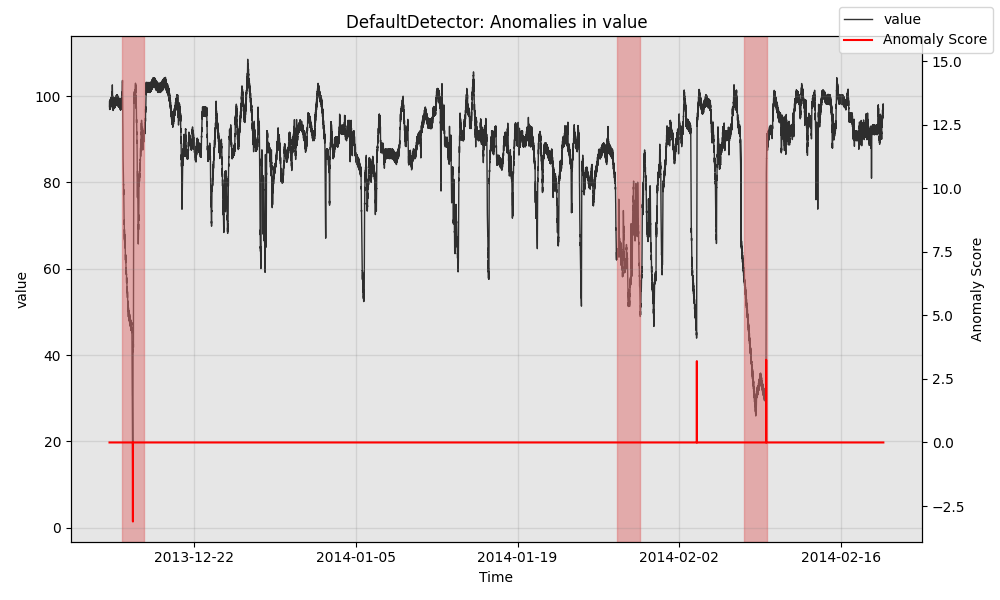 salesforce/merlion
End-to-end Python framework for time series intelligence, offering anomaly detection, forecasting, change point detection, AutoML, ensembles, and…
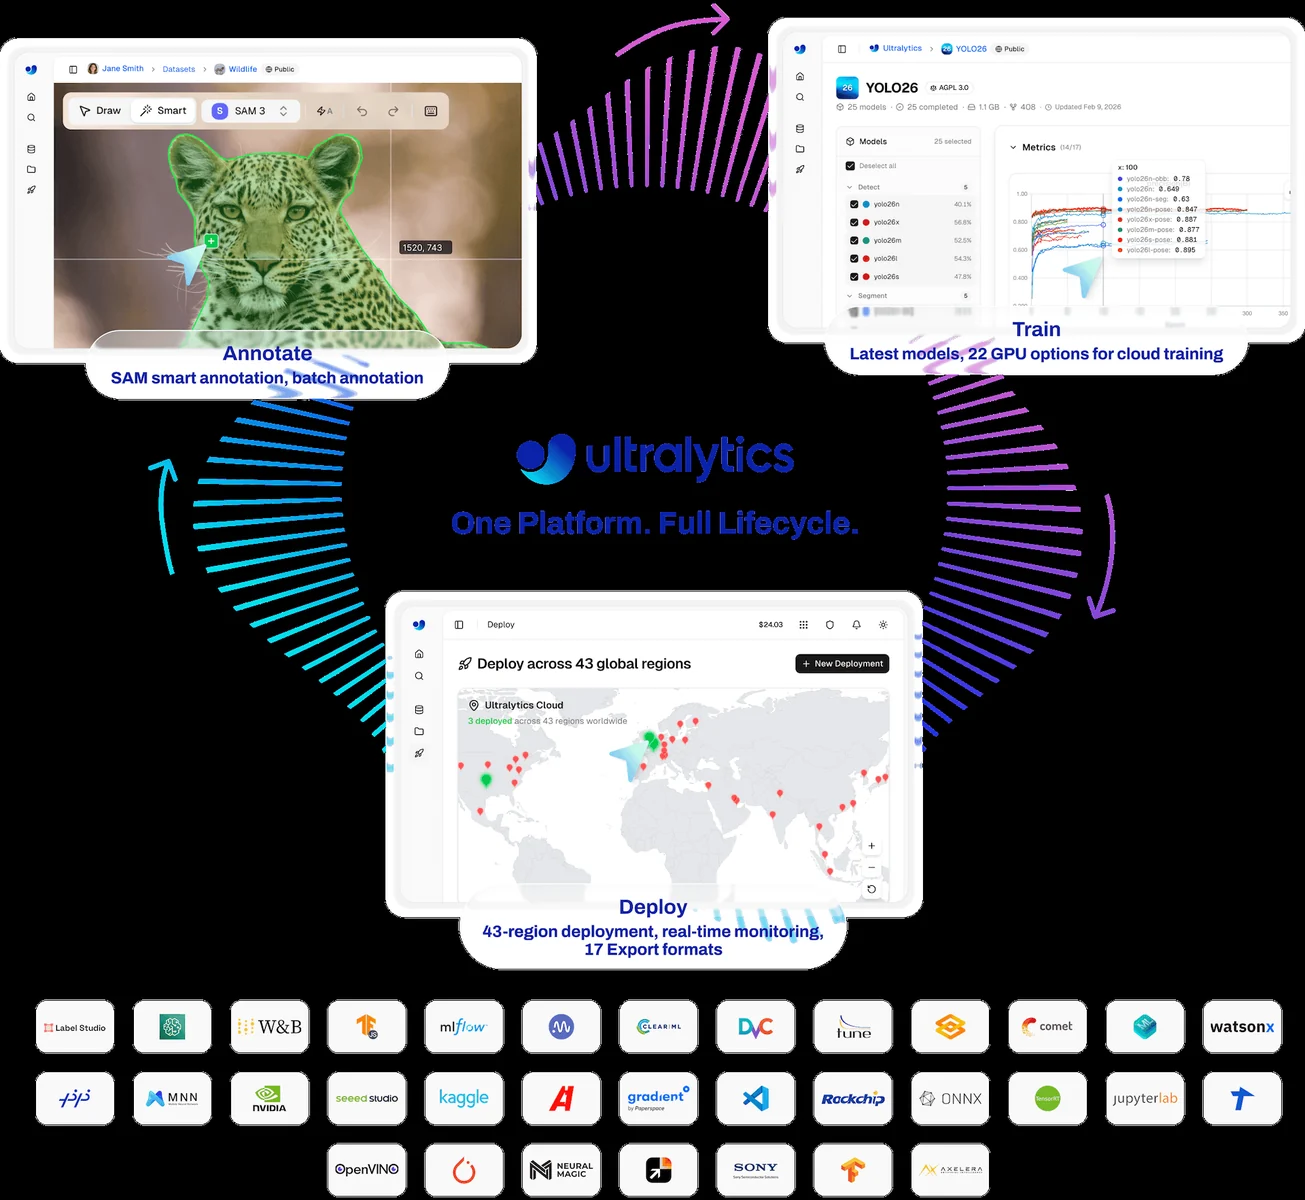 ultralytics/ultralytics
Deep learning framework for object detection, segmentation, classification, pose estimation, and tracking using pre-trained YOLO models and…
 p-e-w/heretic
Fully automatic censorship removal for language models
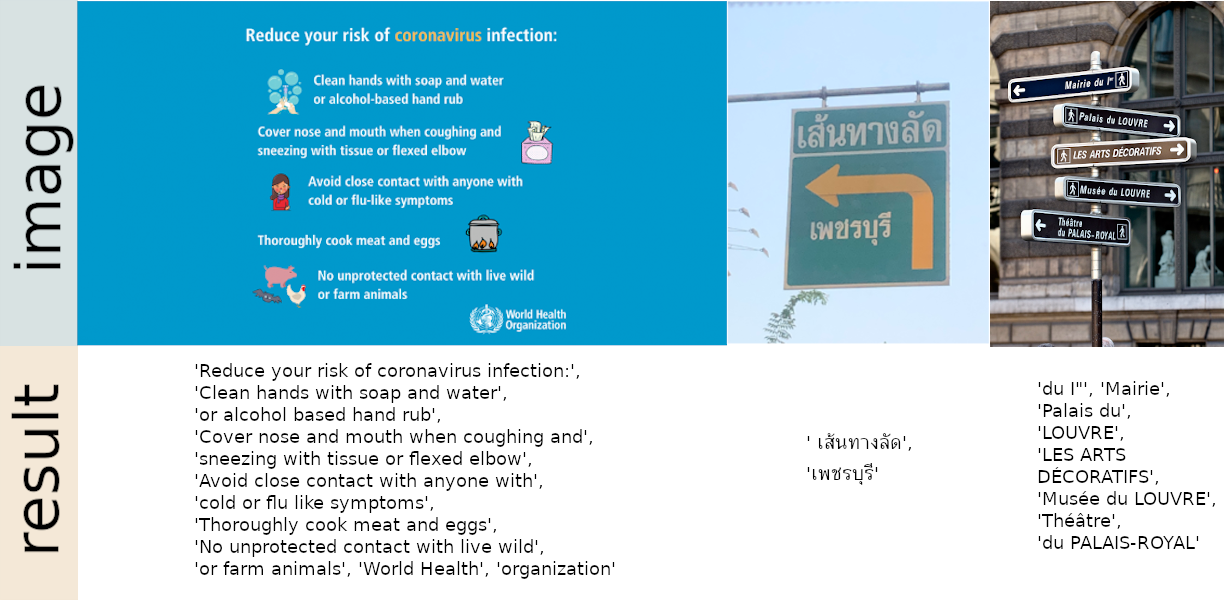 jaidedai/easyocr
Ready-to-use OCR with 80+ supported languages and all popular writing scripts including Latin, Chinese, Arabic, Devanagari, Cyrillic and etc.
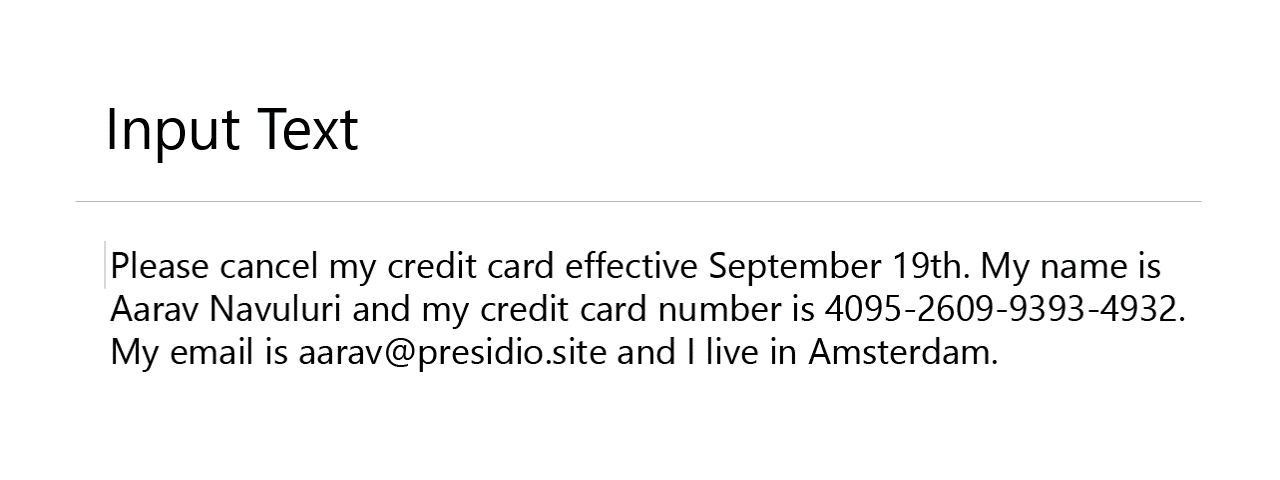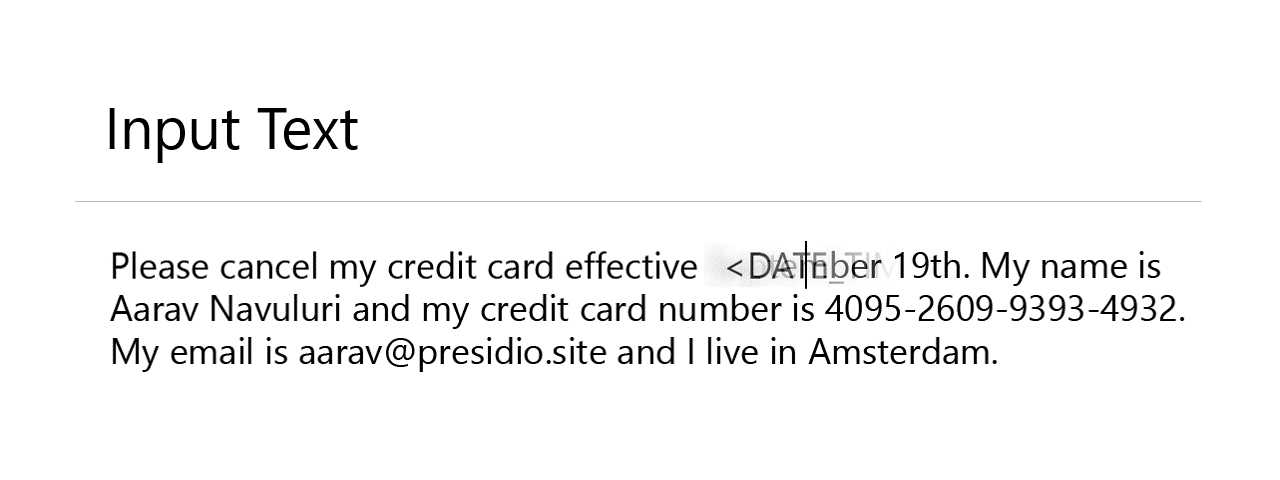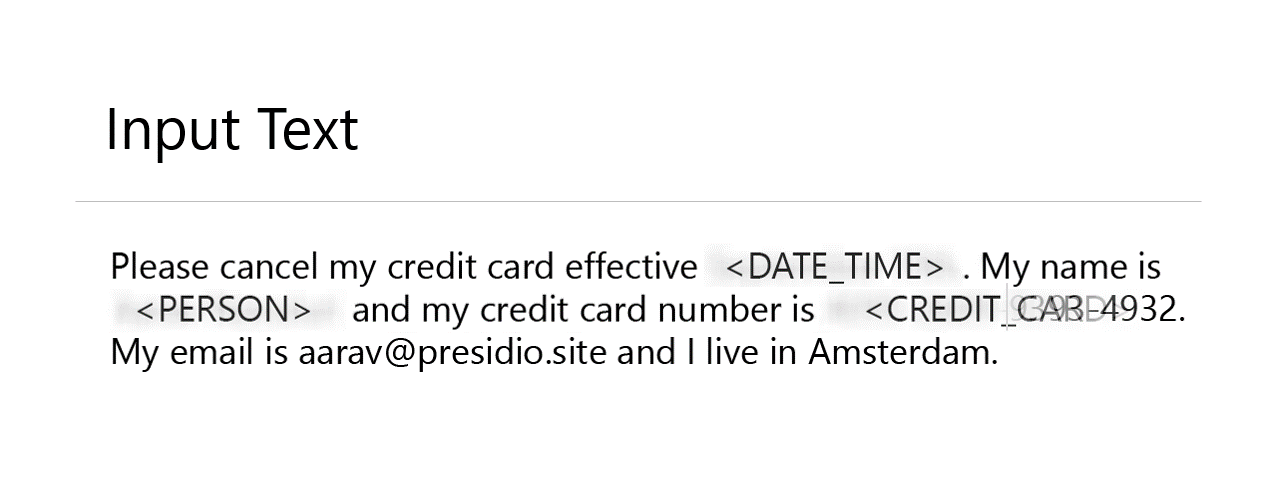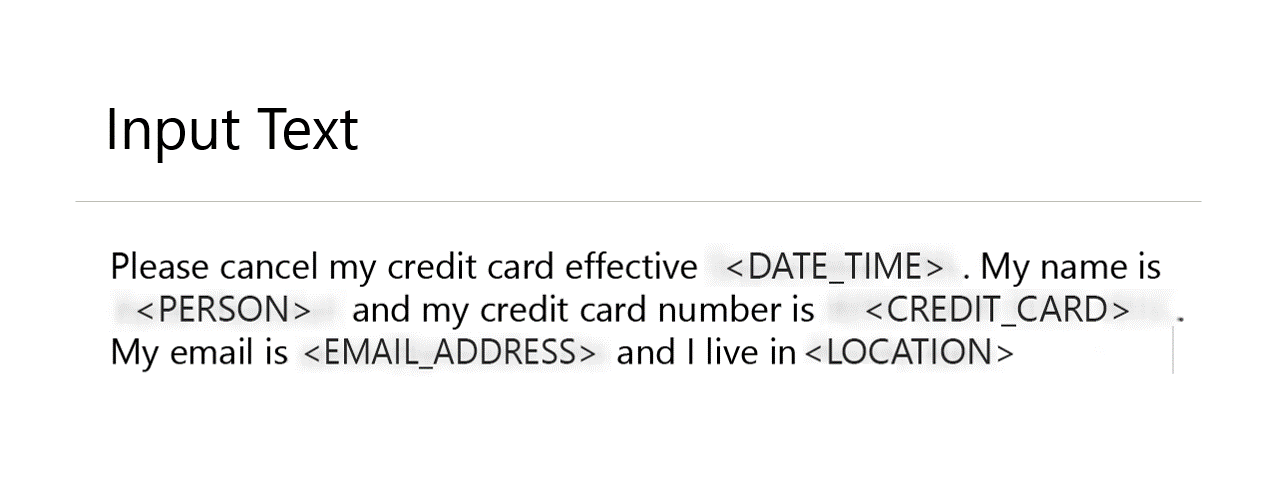 data-privacy-stack/presidio
An open-source framework for detecting, redacting, masking, and anonymizing sensitive data (PII) across text, images, and structured data. Supports…
 nvidia-nemo/guardrails
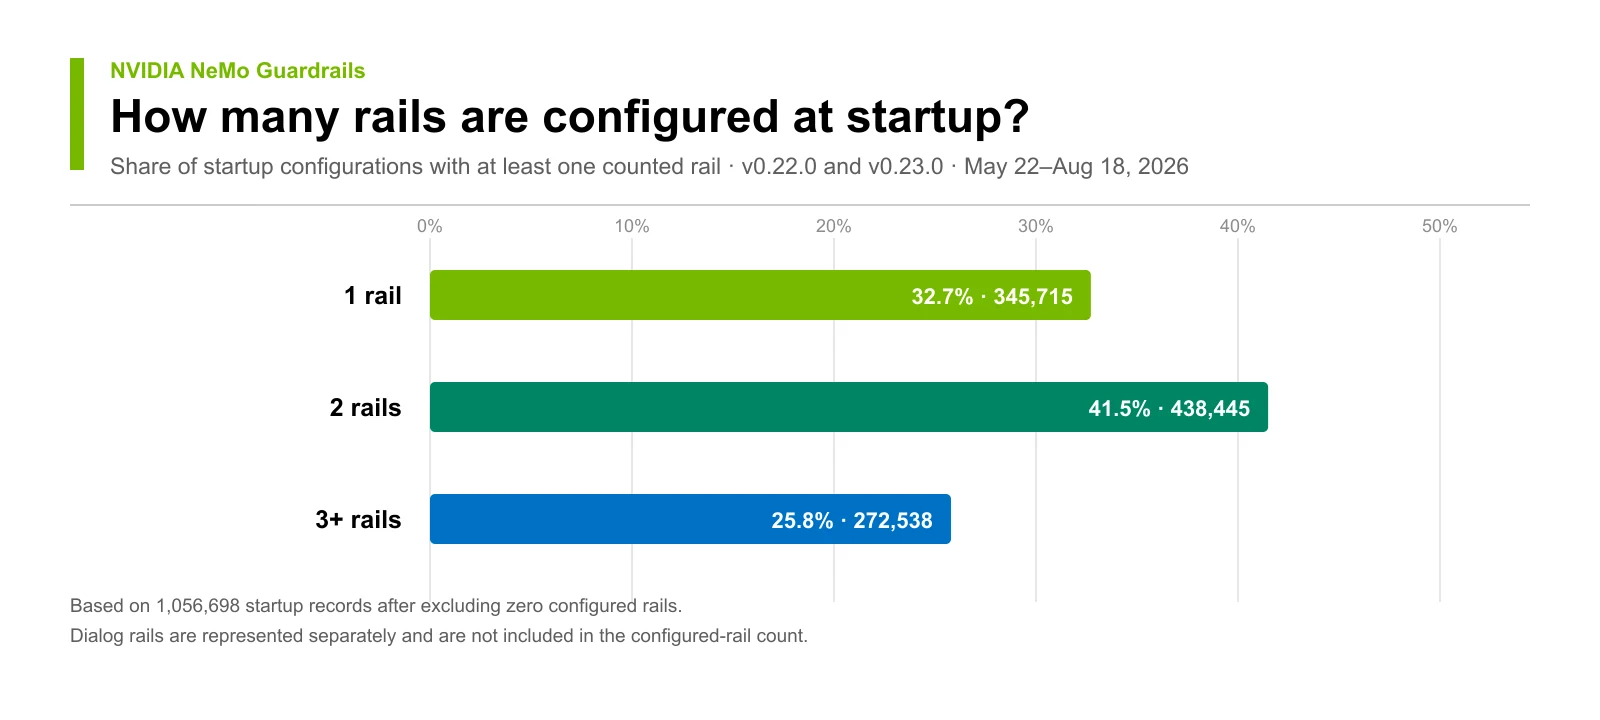
Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask…
 microsoft/pyrit
Open-source framework for red-teaming generative AI systems: automate attack prompts, score model responses, and audit behavior to identify security…
 trusted-ai/aif360
A comprehensive set of fairness metrics for datasets and machine learning models, explanations for these metrics, and algorithms to mitigate bias in…
 seldonio/alibi-detect
Algorithms for outlier, adversarial and drift detection
 bishopfox/eyeballer
Convolutional neural network for analyzing pentest screenshots
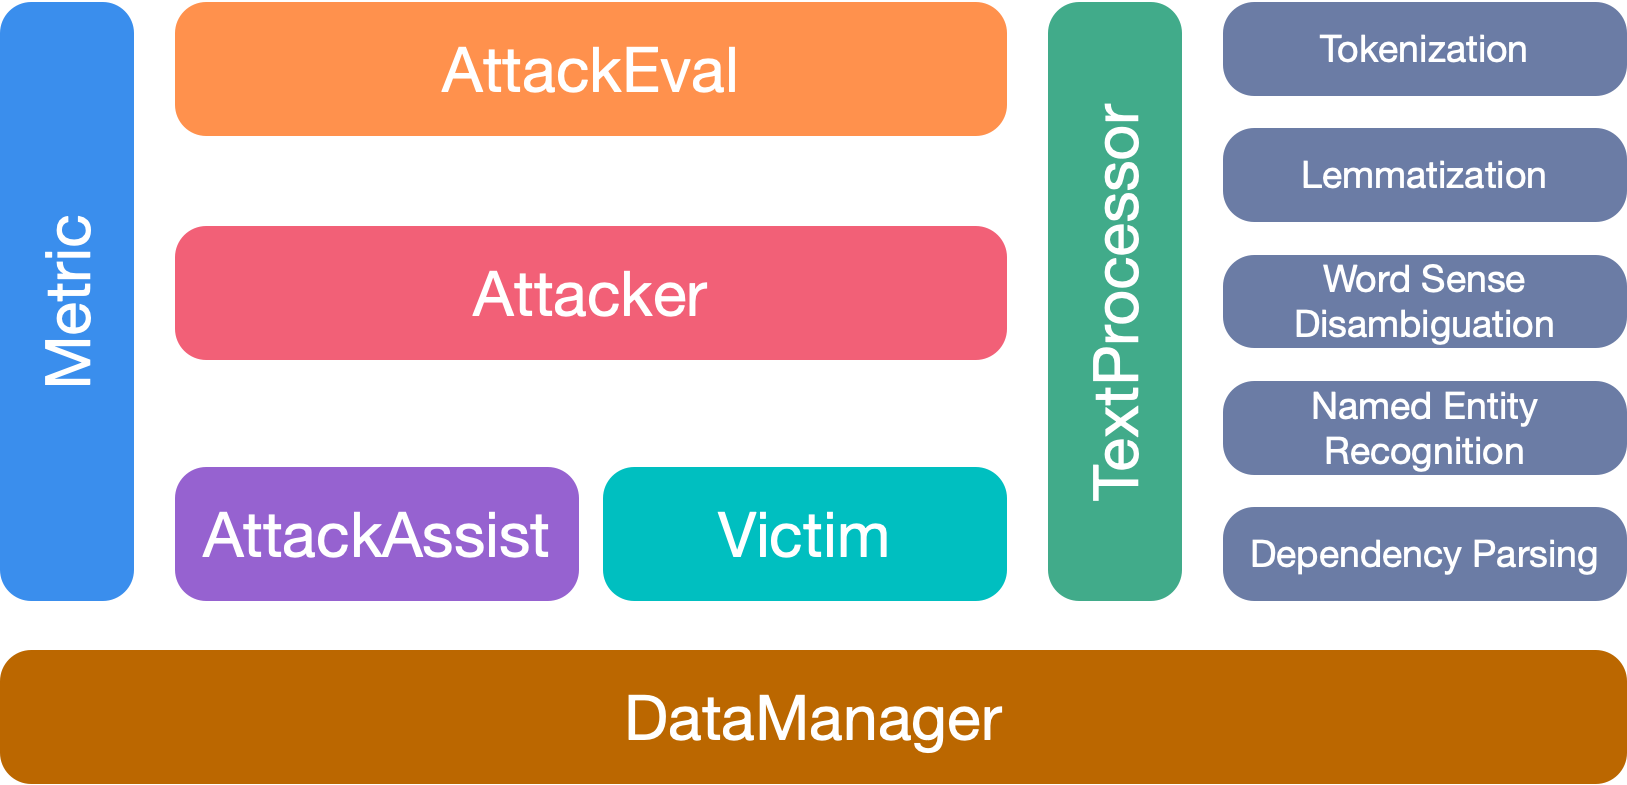 thunlp/openattack
An Open-Source Package for Textual Adversarial Attack.
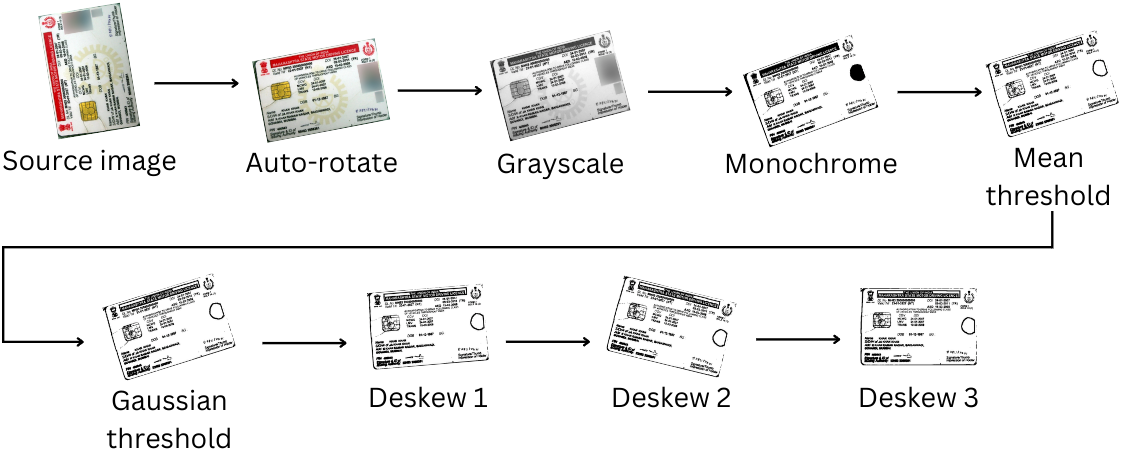 redhuntlabs/octopii
An AI-powered Personal Identifiable Information (PII) scanner.
 0xsojalsec/uncensored-ai
Fully automatic censorship removal for language models
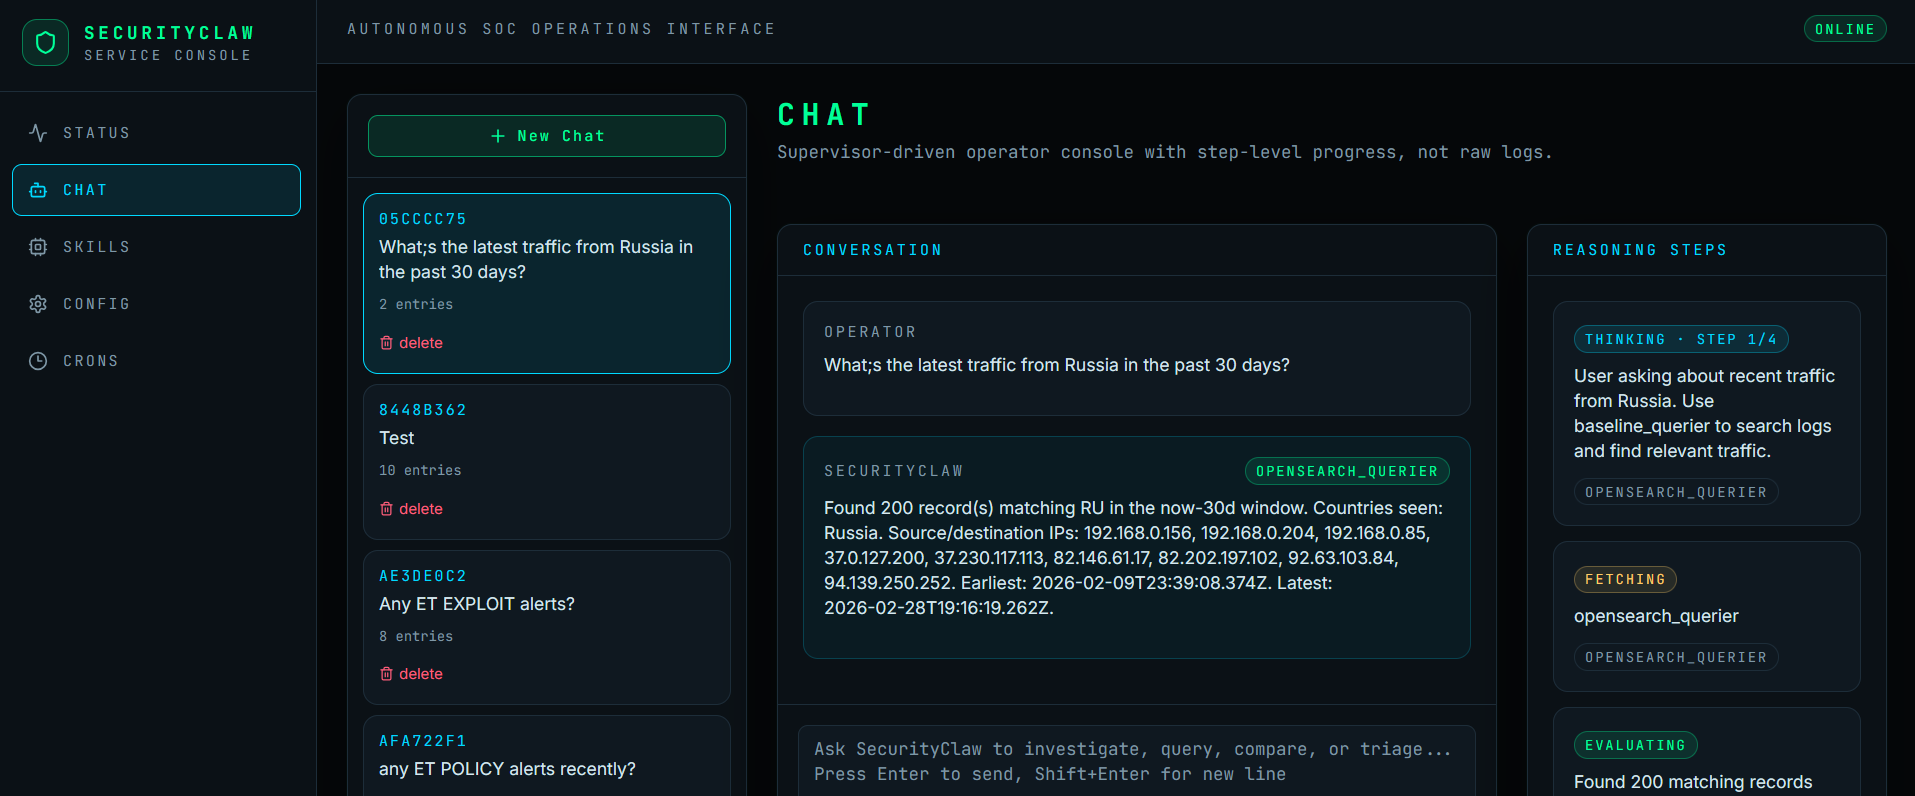 securityclaw/securityclaw
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
 ait-aecid/logdata-anomaly-miner
This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…