

oss-fuzz-gen
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
ai-securitydevsecopsdynamic-code-analysis+3
google/oss-fuzz-genLLM powered fuzzing via OSS-Fuzz.
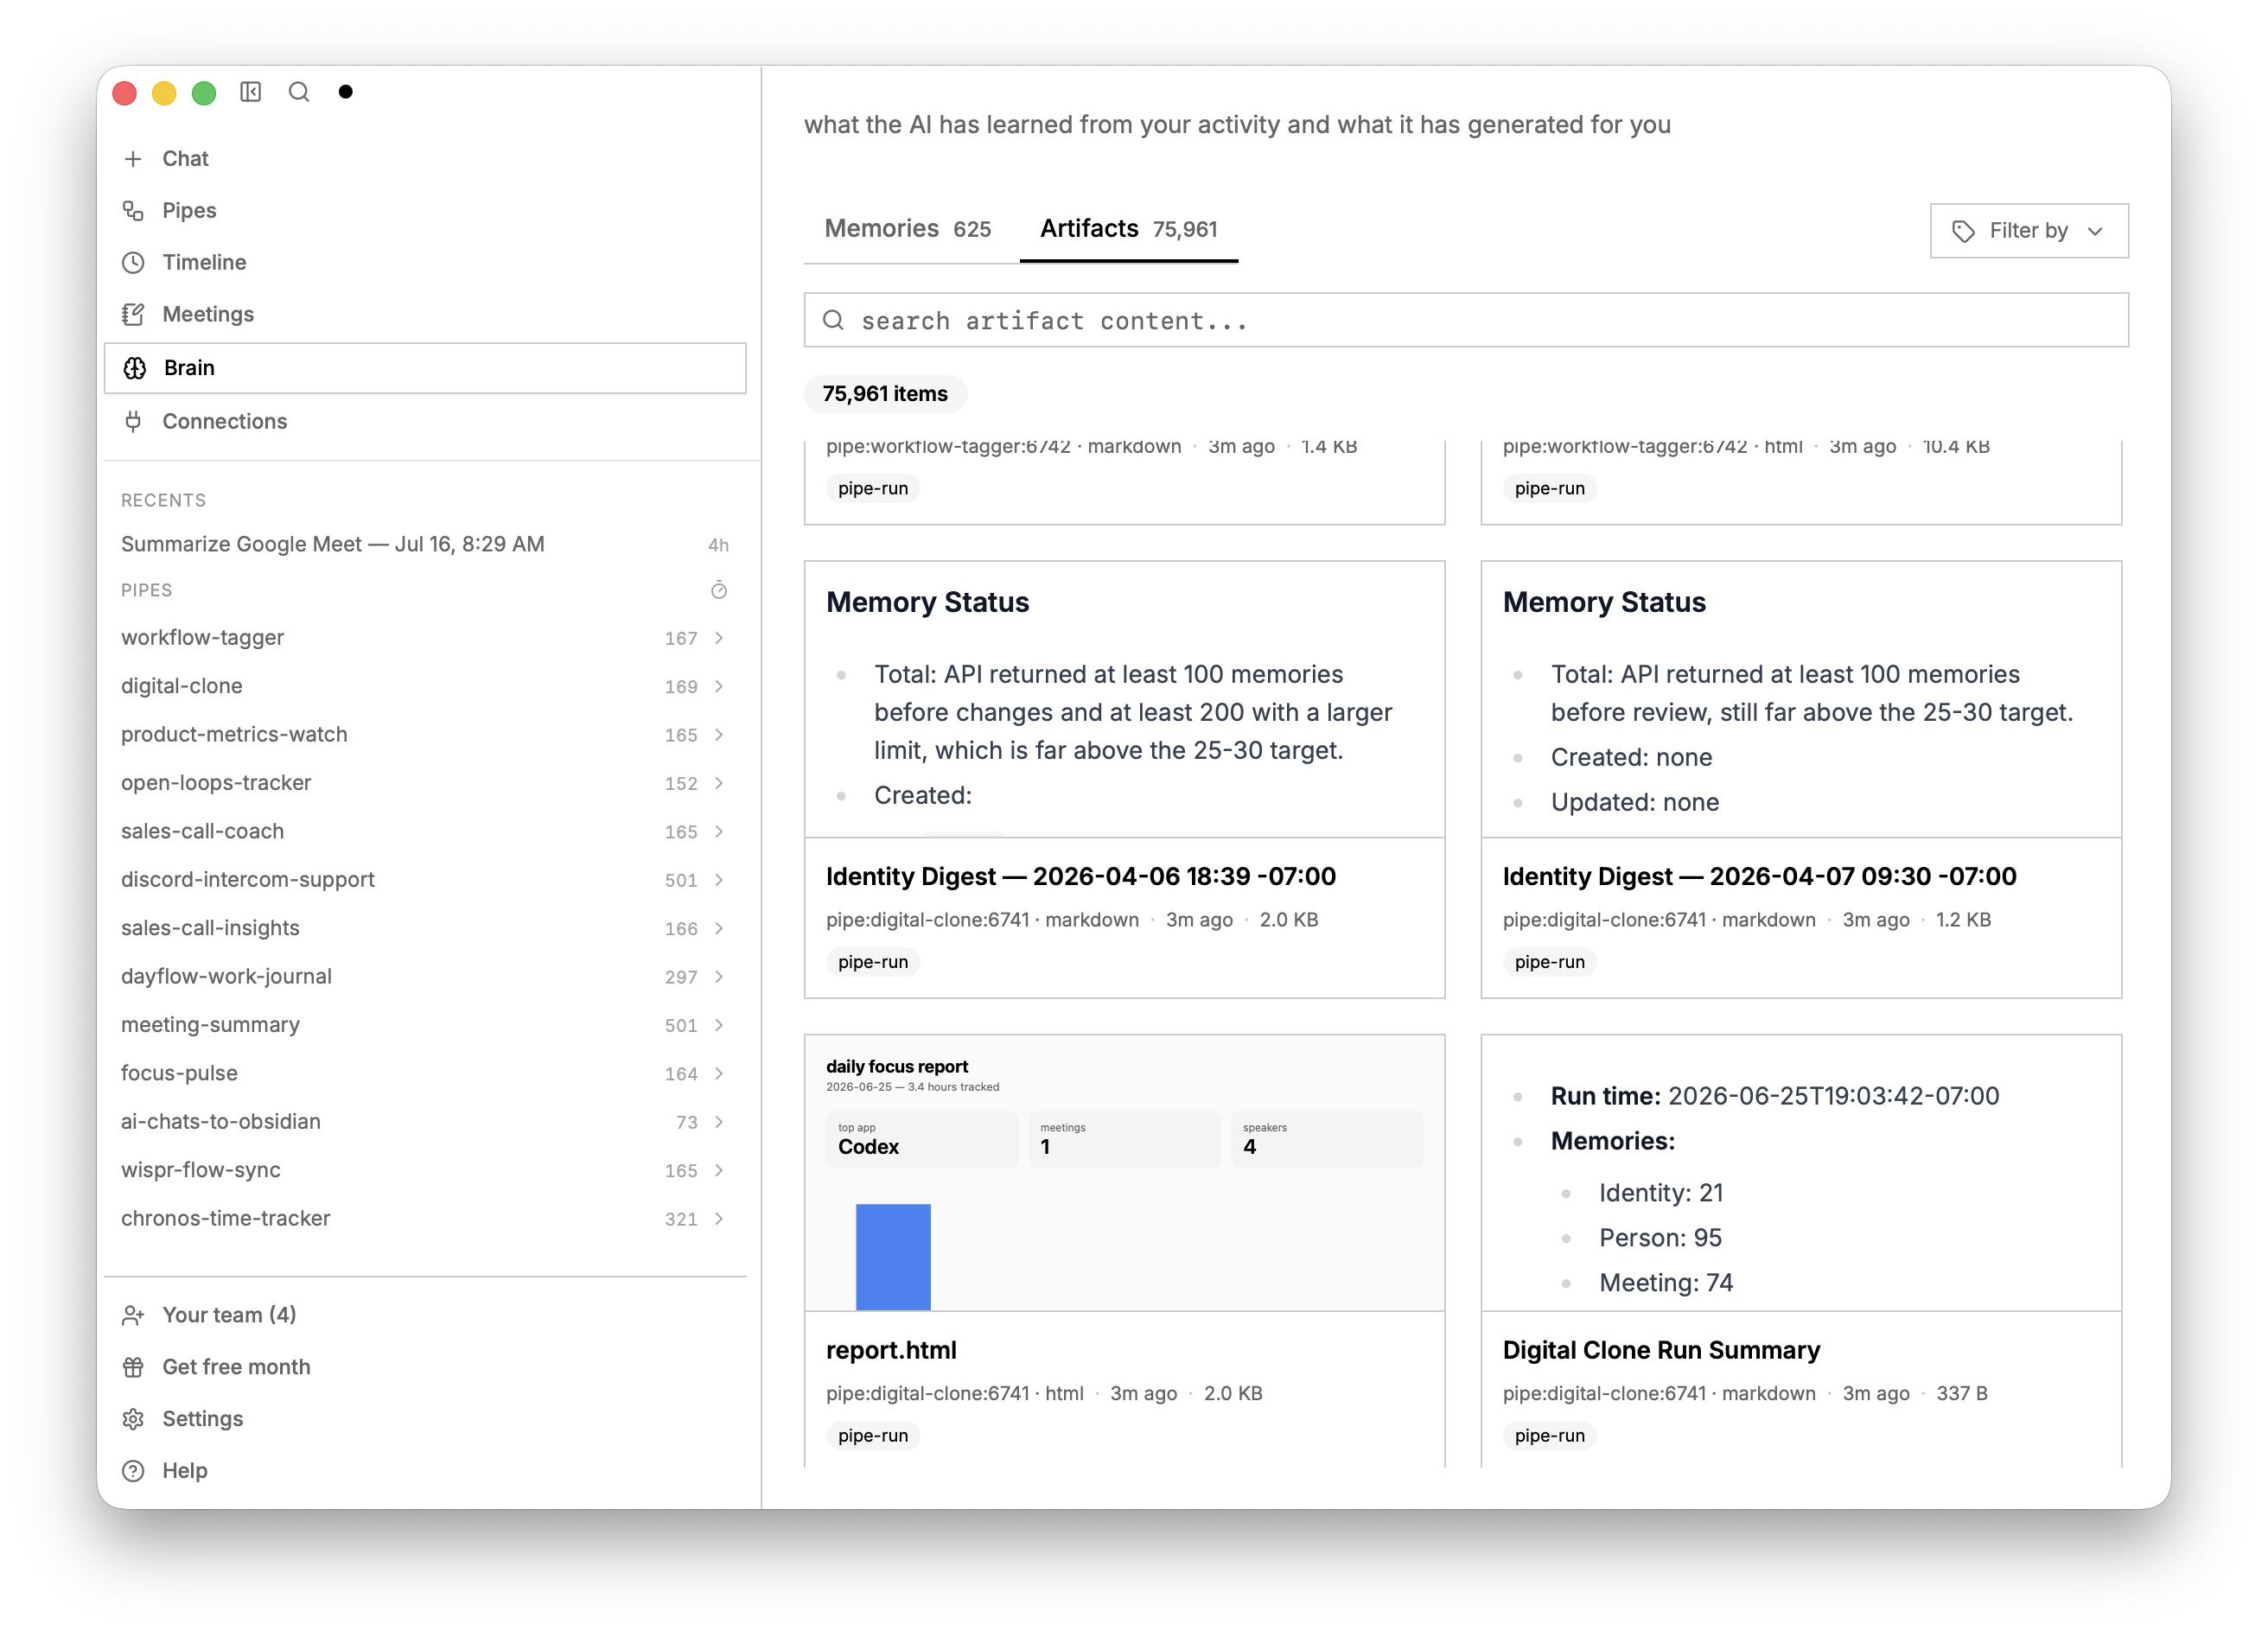 screenpipe/screenpipe
YC (S26) | Open Computer History | Continuously record your company computer work, map your workflows, help you find work worth automating, and power…
 giovannigatti/cve-bench
A benchmark for evaluating AI agents on fixing real-world security vulnerabilities.
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
 nousresearch/hermes-agent
The agent that grows with you
 delvelabs/batea
AI-based, context-driven network device ranking