
BotLens
 ua-spectral/botlens
Research artifact and MCP server that audits security and privacy concerns in third-party Discord bots via large-scale review analysis, LLM labeling,…
crawlereducationinformation-gathering+5
ua-spectral/botlensResearch artifact and MCP server that audits security and privacy concerns in third-party Discord bots via large-scale review analysis, LLM labeling,…
 jefffffffu/priv-qdnn
Research codebase for privacy evaluation of quantized neural networks: trains target/shadow models under PTQ/QAT and runs membership-inference…
 itm-kitware/alignment-cage-challenge-2
CybORG CAGE 2 environment updated for the paper "Alignment of Autonomous Cyber Defense Agents via Adaptive Policy Shaping"
 maureille/agentic-pcap
Benchmark code and interactive results for autonomous network-attack detection by tool-using LLM agents investigating raw PCAPs.
 yashubitra/mobile-intrusion-detection-system
Unsupervised deep autoencoder that flags anomalous mobile traffic: 25,000+ HTTP/HTTPS flows intercepted from a live iOS device with mitmproxy,…
 ukanwat/guardrebind
Research code, benchmark and defense for target rebinding attacks that trick LLM safety guards into grading forged decoy content, plus segment-max…
 lzh0082-cloud/code-detection
Replication package studying how LLM vulnerability auditors defer to static-analysis evidence, with a tree-sitter C/C++ front end, controlled…
 seclog-open/seclog
Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…
 suels-group/beyond_asr
Research code for measuring jailbreak attack success rates (ASR and stepwise ASR) against LLMs, with implementations of attacks such as GCG and…
 crypto-unict/ghostfacempc
Reference implementation of privacy-preserving face recognition using replicated secret sharing in MP-SPDZ, with quantized GhostFaceNet inference,…
 tencent-hunyuan/diagsafe
Diagnostic LLM safety benchmark with 3,489 bilingual prompts, an 84-label taxonomy, and prompt-level rubric judging for explainable, fine-grained…
 hanxi19/black_hole_attack_for_vector_database
Research implementation of the Black-Hole Attack that poisons vector database indexes via centrality-driven hubness, with FAISS pipelines and…
 happytotoro116/ghidra-llm-pipeline
Deterministic PyGhidra extraction, triage, and local LLM compiler-backend pipeline for C reimplementation.
 gmh5225/malicious-code-detection-bugu
AI-based malicious code detection and obfuscation system with microservices for detection, packing, and code confusion, plus user and admin services.
 nawaralseelawi/pvbrf-id
Simulation code and results for a private, verifiable, Byzantine-robust federated intrusion detection protocol using secret sharing, Merkle audits…
 cosmosyi/autocontrol-arena
Automated framework for frontier AI safety evaluation that synthesizes executable, pressure-rich test environments to uncover latent risks in…
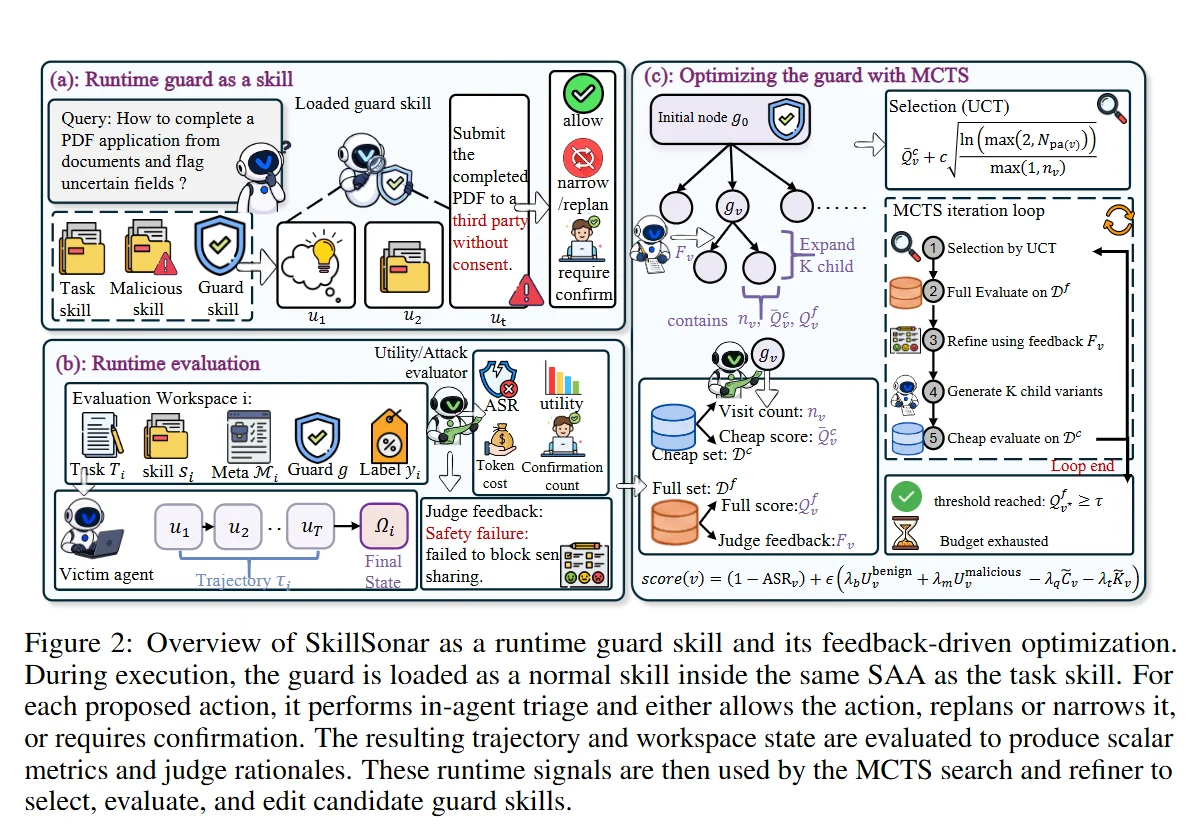 yxf203/defense-as-skill
Runtime guard skill that detects and blocks malicious skill-induced attacks in skill-augmented agents, with an MCTS loop that evolves the guard…
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.