
MADLIRA
 dkhuuthe/madlira
Malware detection using learning and information retrieval for Android
android-securitymachine-learningmalware-analysis+1
dkhuuthe/madliraMalware detection using learning and information retrieval for Android
 openclaw/openclaw
The AI that really does things. Any OS. Any Platform. The lobster way. 🦞
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
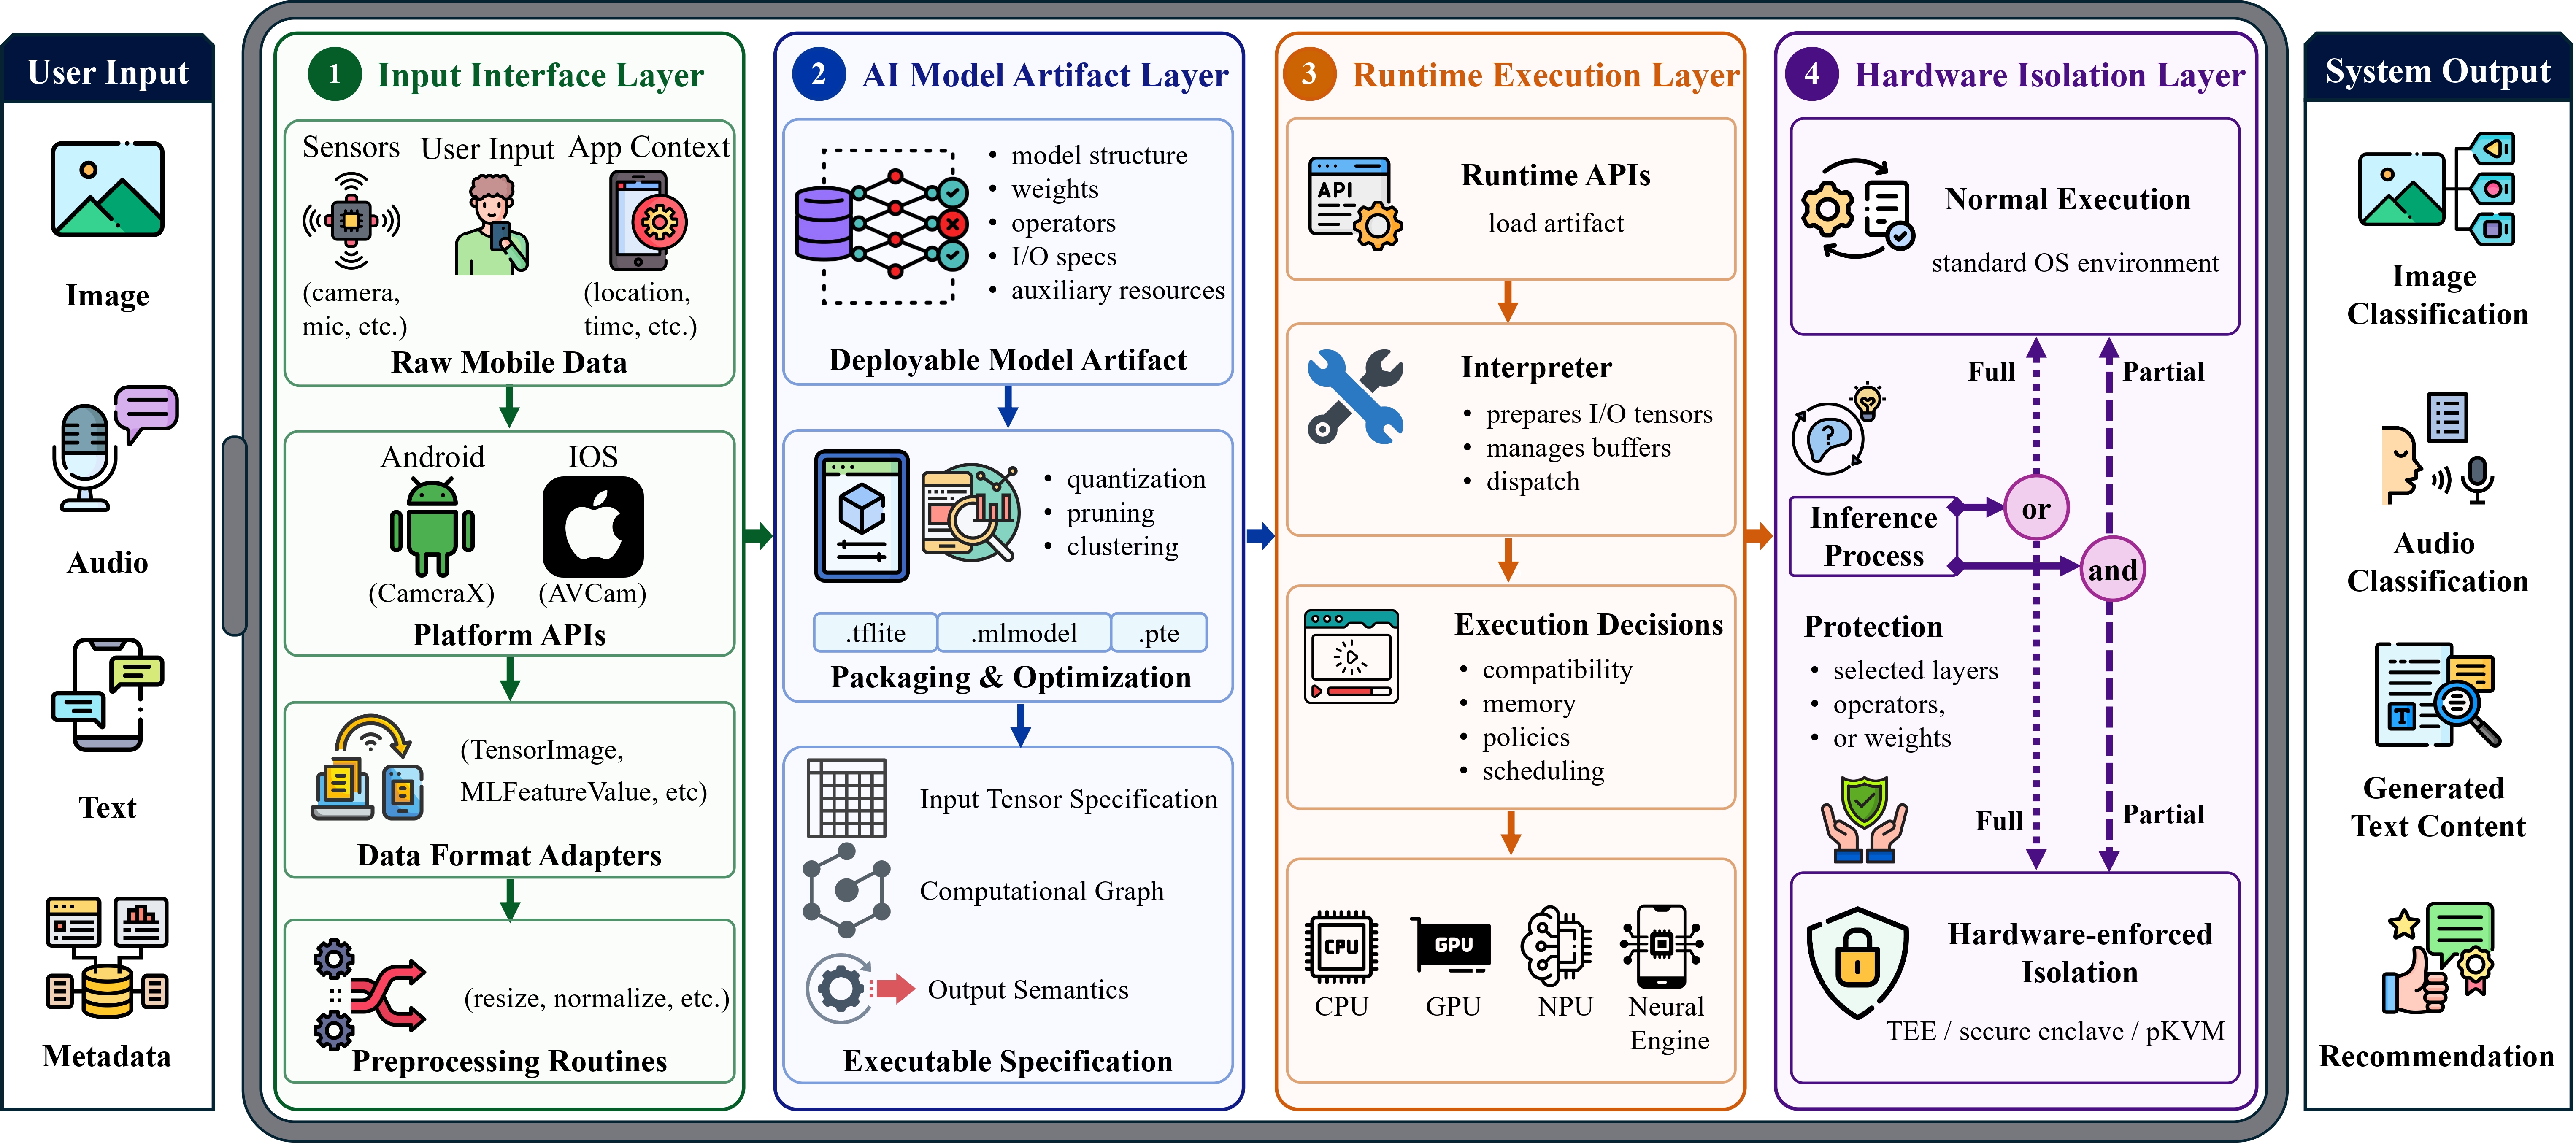 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 user1342/droiddetective
A machine learning malware analysis framework for Android apps.
 qbnasasn/google-tensor-chips
Google Tensor Cracks
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 hydradragonantivirus/hydradragonav-mobile
Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
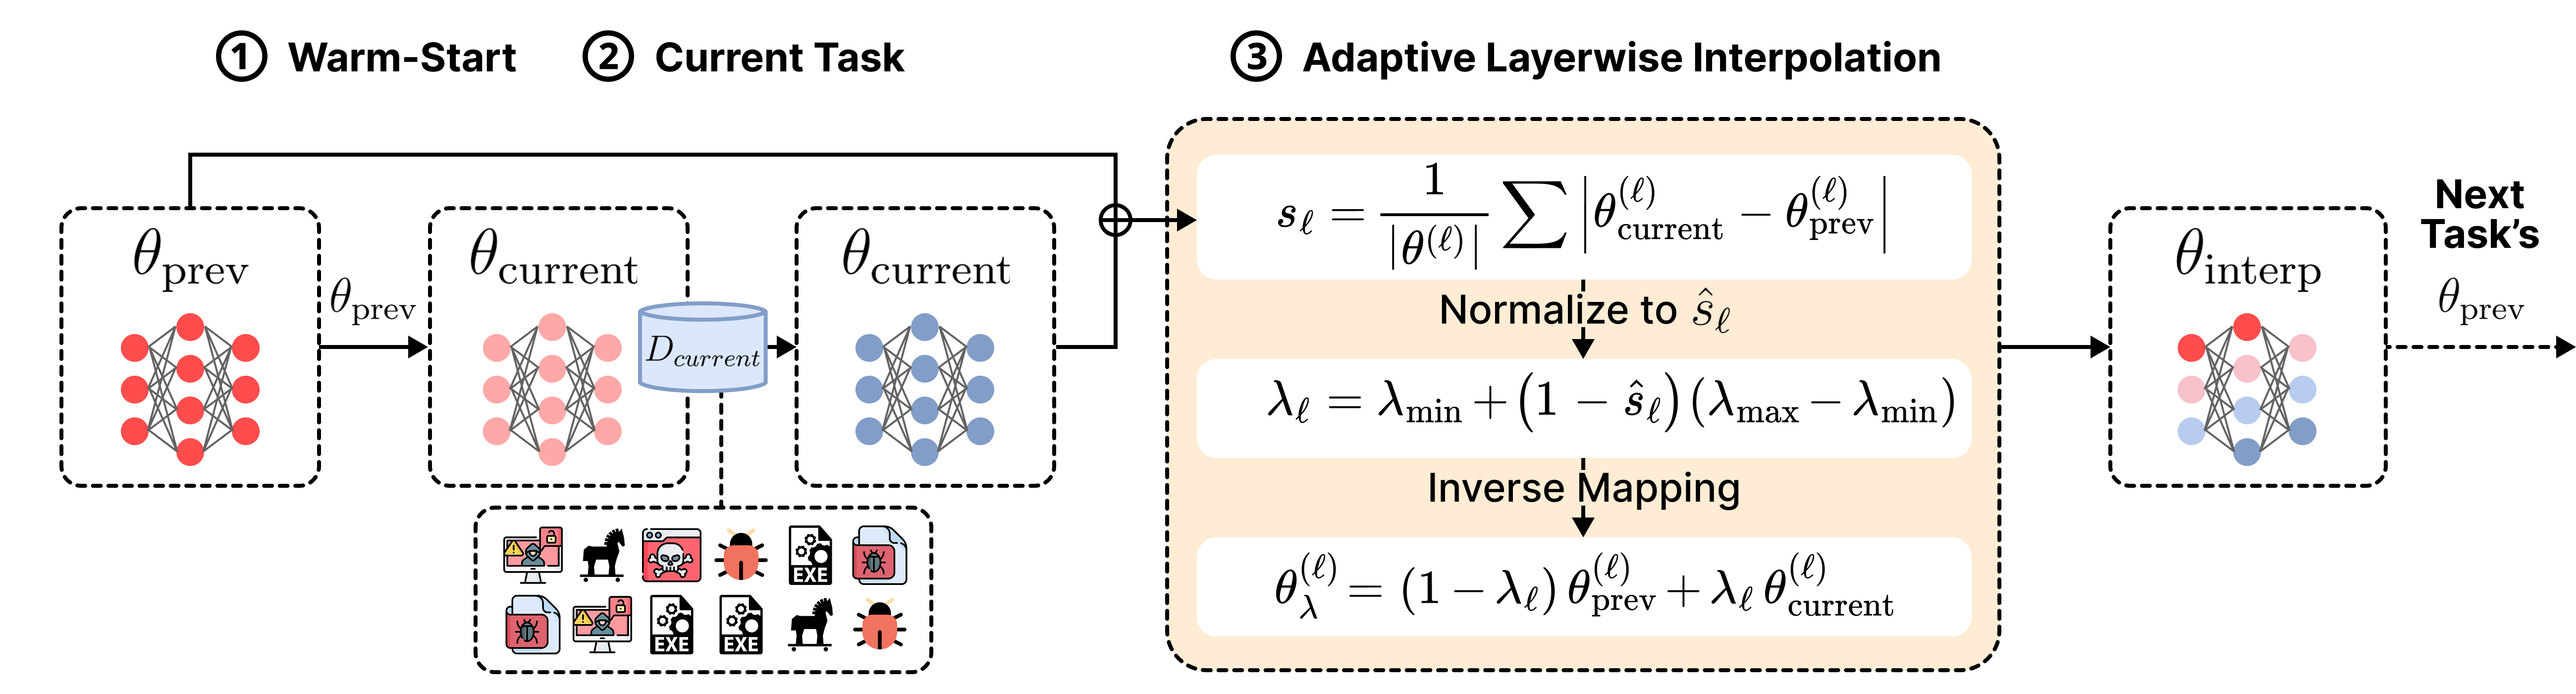 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…