

Apkx-Hunter
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
android-securityinformation-gatheringmachine-learning+7
103
syscallx-18113/apkx-hunterC-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 albertan017/llm4decompile
Reverse Engineering: Decompiling Binary Code with Large Language Models
 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
 certcc/certfuzz
This project contains the source code for the CERT Basic Fuzzing Framework (BFF) and the CERT Failure Observation Engine (FOE).
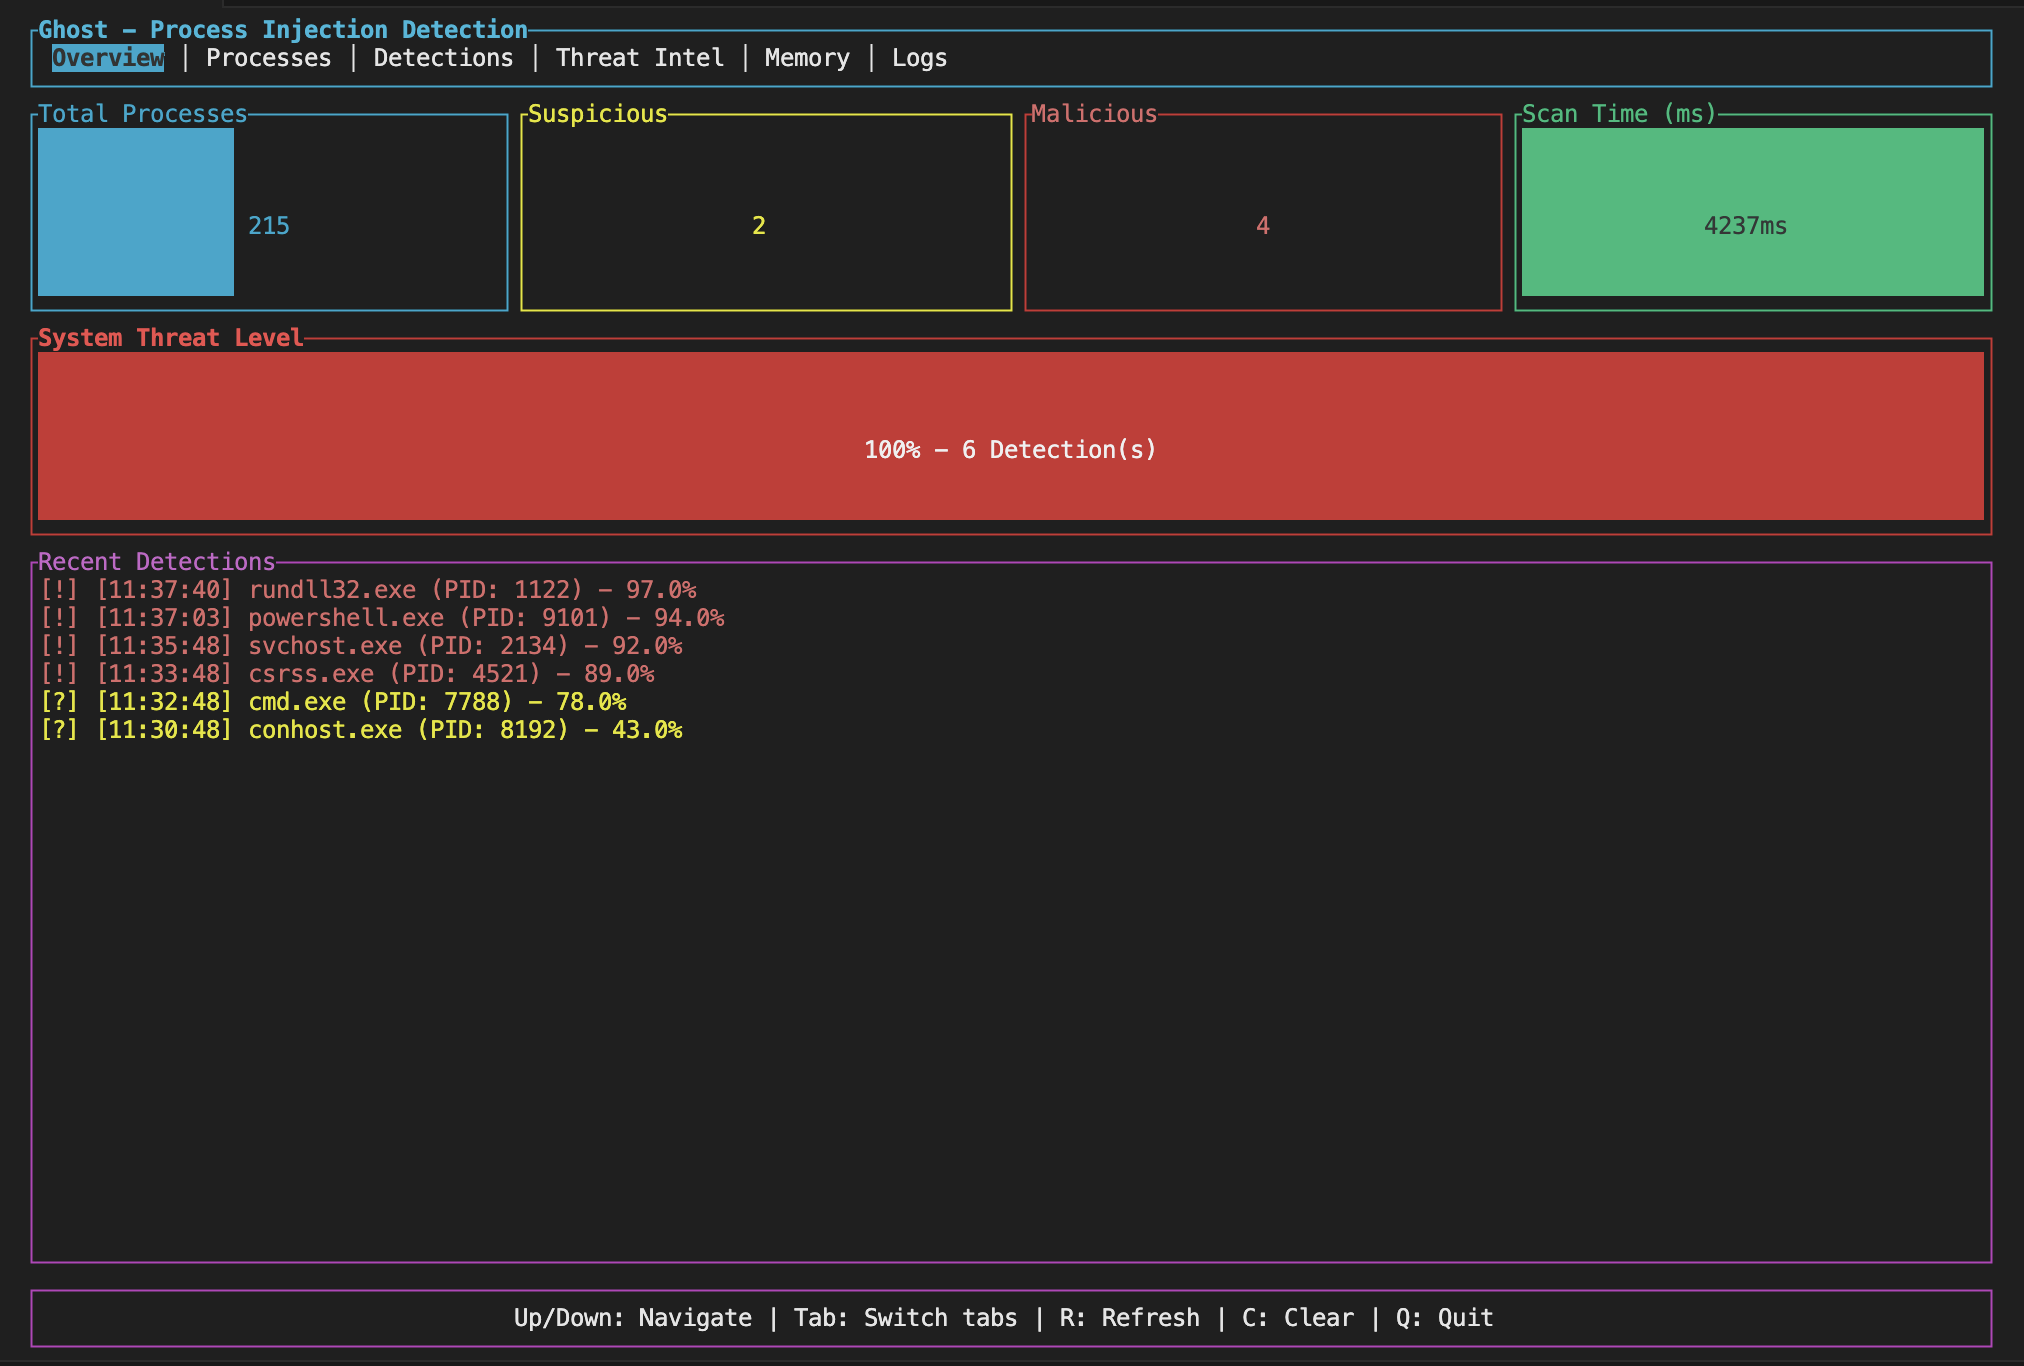 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
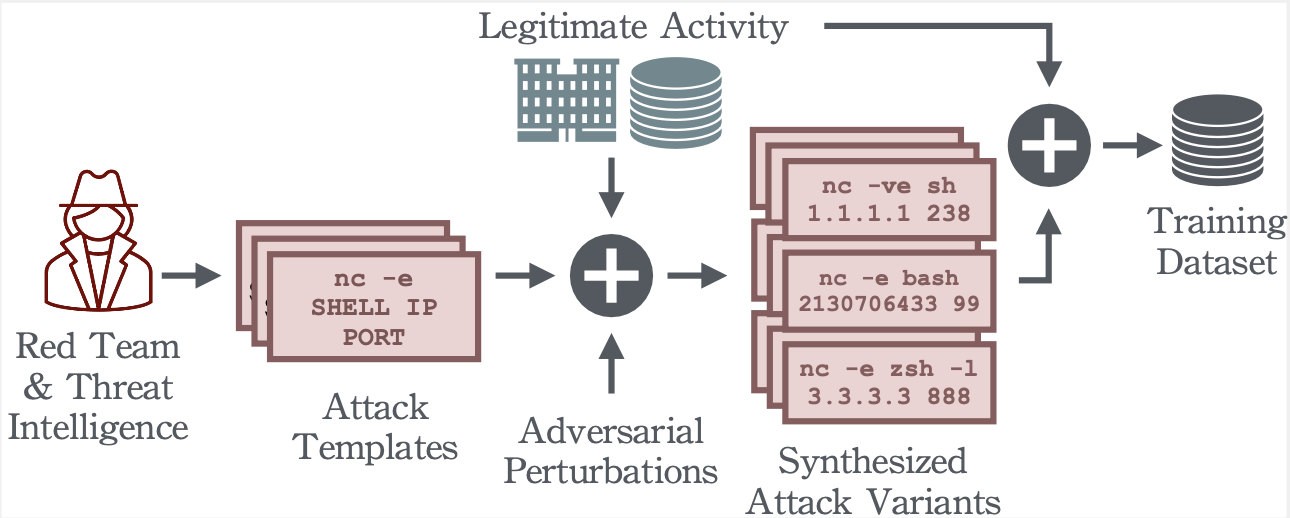 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 mazen160/shennina
Automating Host Exploitation with AI
 secml/secml
A Python library for Secure and Explainable Machine Learning Documentation available @ https://secml.gitlab.io Follow us on Twitter @…