
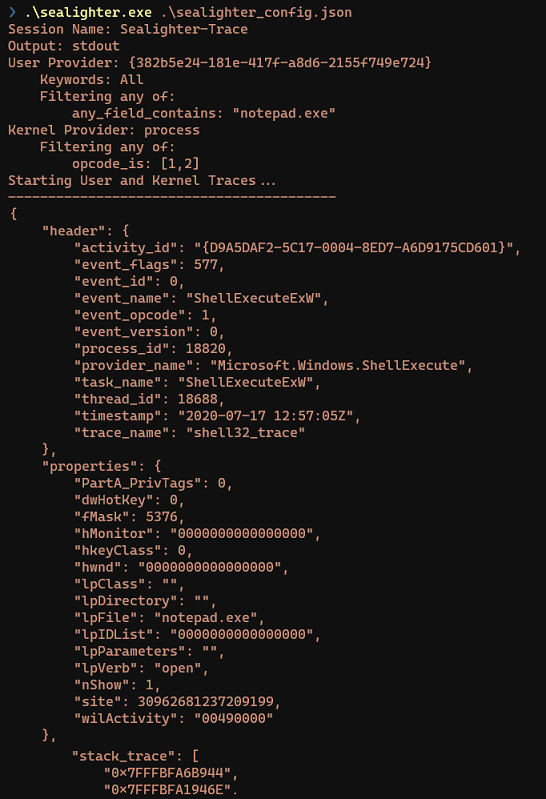
Sealighter
 pathtofile/sealighter
ETW and WPP tracing tool for security research. Subscribes to multiple providers, auto-parses events to JSON, and supports advanced filtering,…
forensicslog-analysis
pathtofile/sealighterETW and WPP tracing tool for security research. Subscribes to multiple providers, auto-parses events to JSON, and supports advanced filtering,…
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
 kolya5544/bearftp
Honeypot FTP server written in .NET Core (C#) for both Linux and Windows.
 kacos2000/evtx_log_browser
Evtx Log (xml) Browser
 fireeye/pywintrace
Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
 forensicmatt/rswindowsthingies
Rust-based Windows forensic toolkit for real-time MFT monitoring, event log streaming, and channel enumeration, enabling live system analysis and…
 boostedchaos/fleet-cve-scanner
An open-source, single-script CVE scanner for RMM-managed fleets. Pure PowerShell 7 — joins your RMM software inventory against NVD, CISA KEV, EPSS…
 ion28/bluespawn
An Active Defense and EDR software to empower Blue Teams
 threathunters-io/qlog
ETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…
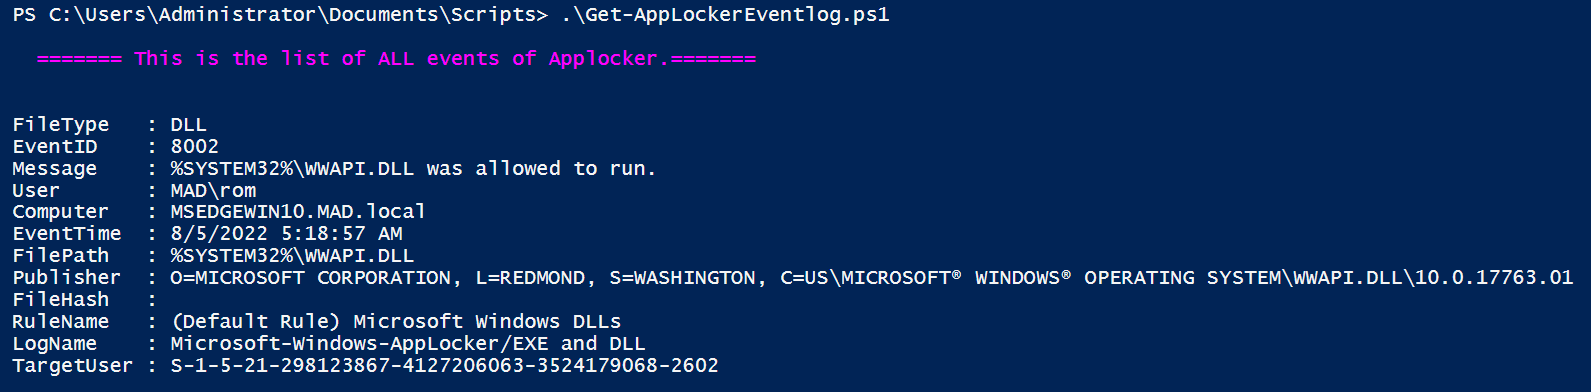 romaissaadjailia/get-applockereventlog
This is a repo for fetching Applocker event log by parsing the win-event log
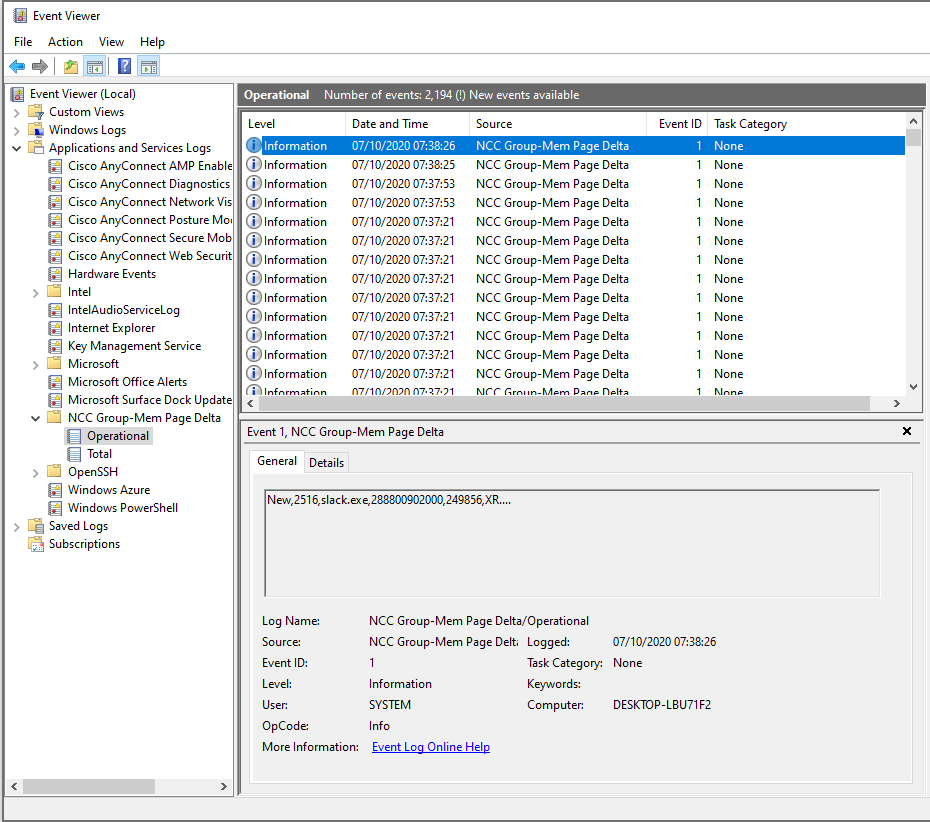 nccgroup/windowsmempagedelta
A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
 mingchen-script/cve-2020-1472-visualizer
PowerShell script to scan Windows Event Logs for CVE-2020-1472 indicators (events 5827-5831), export to CSV, and generate Excel pivot tables for…
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
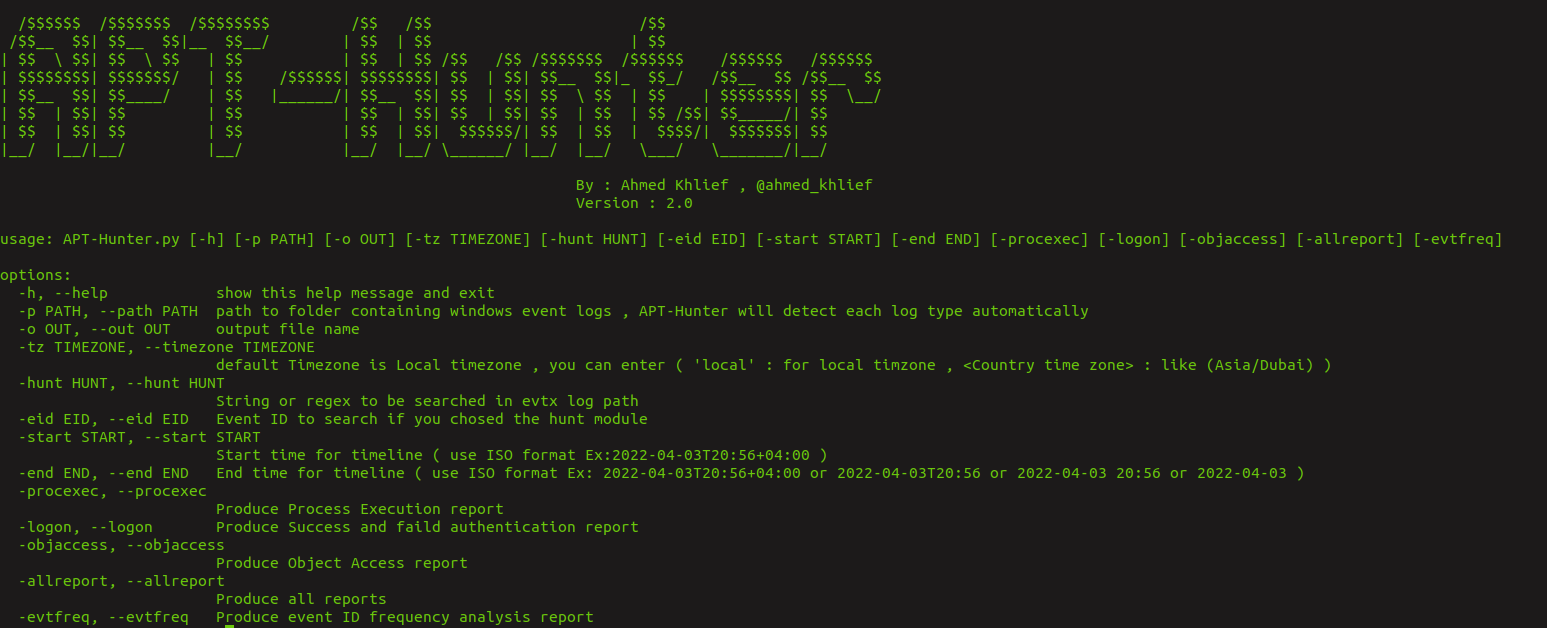 ahmedkhlief/apt-hunter
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…
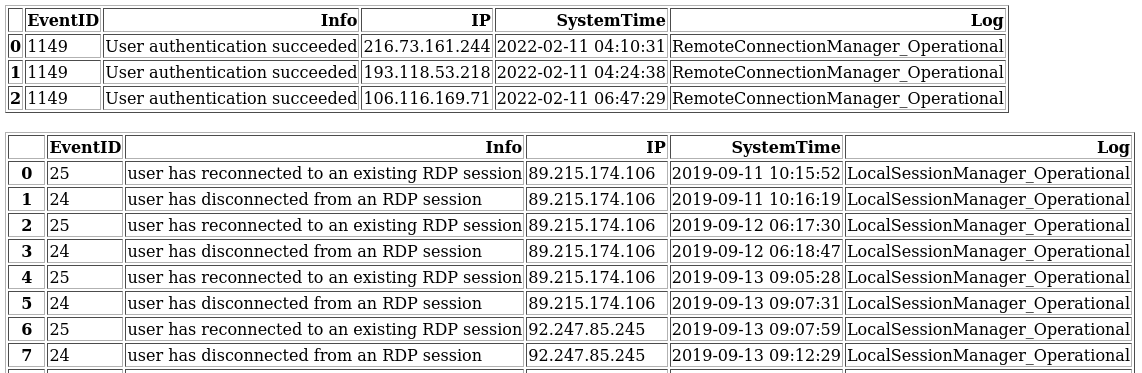 georgi-i/winevt_logs_analysis
Parses Windows .evtx logs to identify remote connections and public IPs by analyzing EventIDs related to remote logins and sessions.
 invictus-ir/alfa
Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…