
fleet-cve-scanner
An open-source, single-script CVE scanner for RMM-managed fleets. Pure PowerShell 7 — joins your RMM software inventory against NVD, CISA KEV, EPSS…

An open-source, single-script CVE scanner for RMM-managed fleets. Pure PowerShell 7 — joins your RMM software inventory against NVD, CISA KEV, EPSS…

A curated list of awesome Security Hardening techniques for Windows.

Read-only N-able N-central CVE-2026-18556/CVE-2026-18577 post-exploitation IoC hunter for Windows endpoints

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

Zabbix Template to monitor for Windows Event Viewer event's related to Netlogon Elevation of Privilege Vulnerability - CVE-2020-1472. Monitors event…

Single-binary scanner for CVE-2021-44228 (Log4Shell) that detects vulnerable log4j versions in JAR/WAR/EAR files and applies mitigation patches by…

Search Windows forensic artifacts, see where each one lives on disk, and copy the KAPE command to collect it. Also builds collection scripts and…

Audits Windows event log settings against best-practice guidelines and Sigma-rule detectability, with automated configuration for DFIR readiness.

MDE/MDI Defender setup for Ludus

Monitors Windows Security logs for failed RDP attempts and automatically blocks abusive IPs via Windows Firewall, with configurable thresholds and…

PowerShell script to scan Windows Event Logs for CVE-2020-1472 indicators (events 5827-5831), export to CSV, and generate Excel pivot tables for…

Scans Windows IIS logs for signs of CVE-2025-53770 & CVE-2025-53771

Vulnerability scanner and mitigation patch for Log4j2 CVE-2021-44228

Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…

Audix is a PowerShell tool to quickly configure the Windows Event Audit Policies for security monitoring

Honeypot FTP server written in .NET Core (C#) for both Linux and Windows.

Technical write-up and analysis of PrintNightmare (CVE-2021-1675 / CVE-2021-34527), covering RCE/LPE exploitation, detection via Windows event logs,…

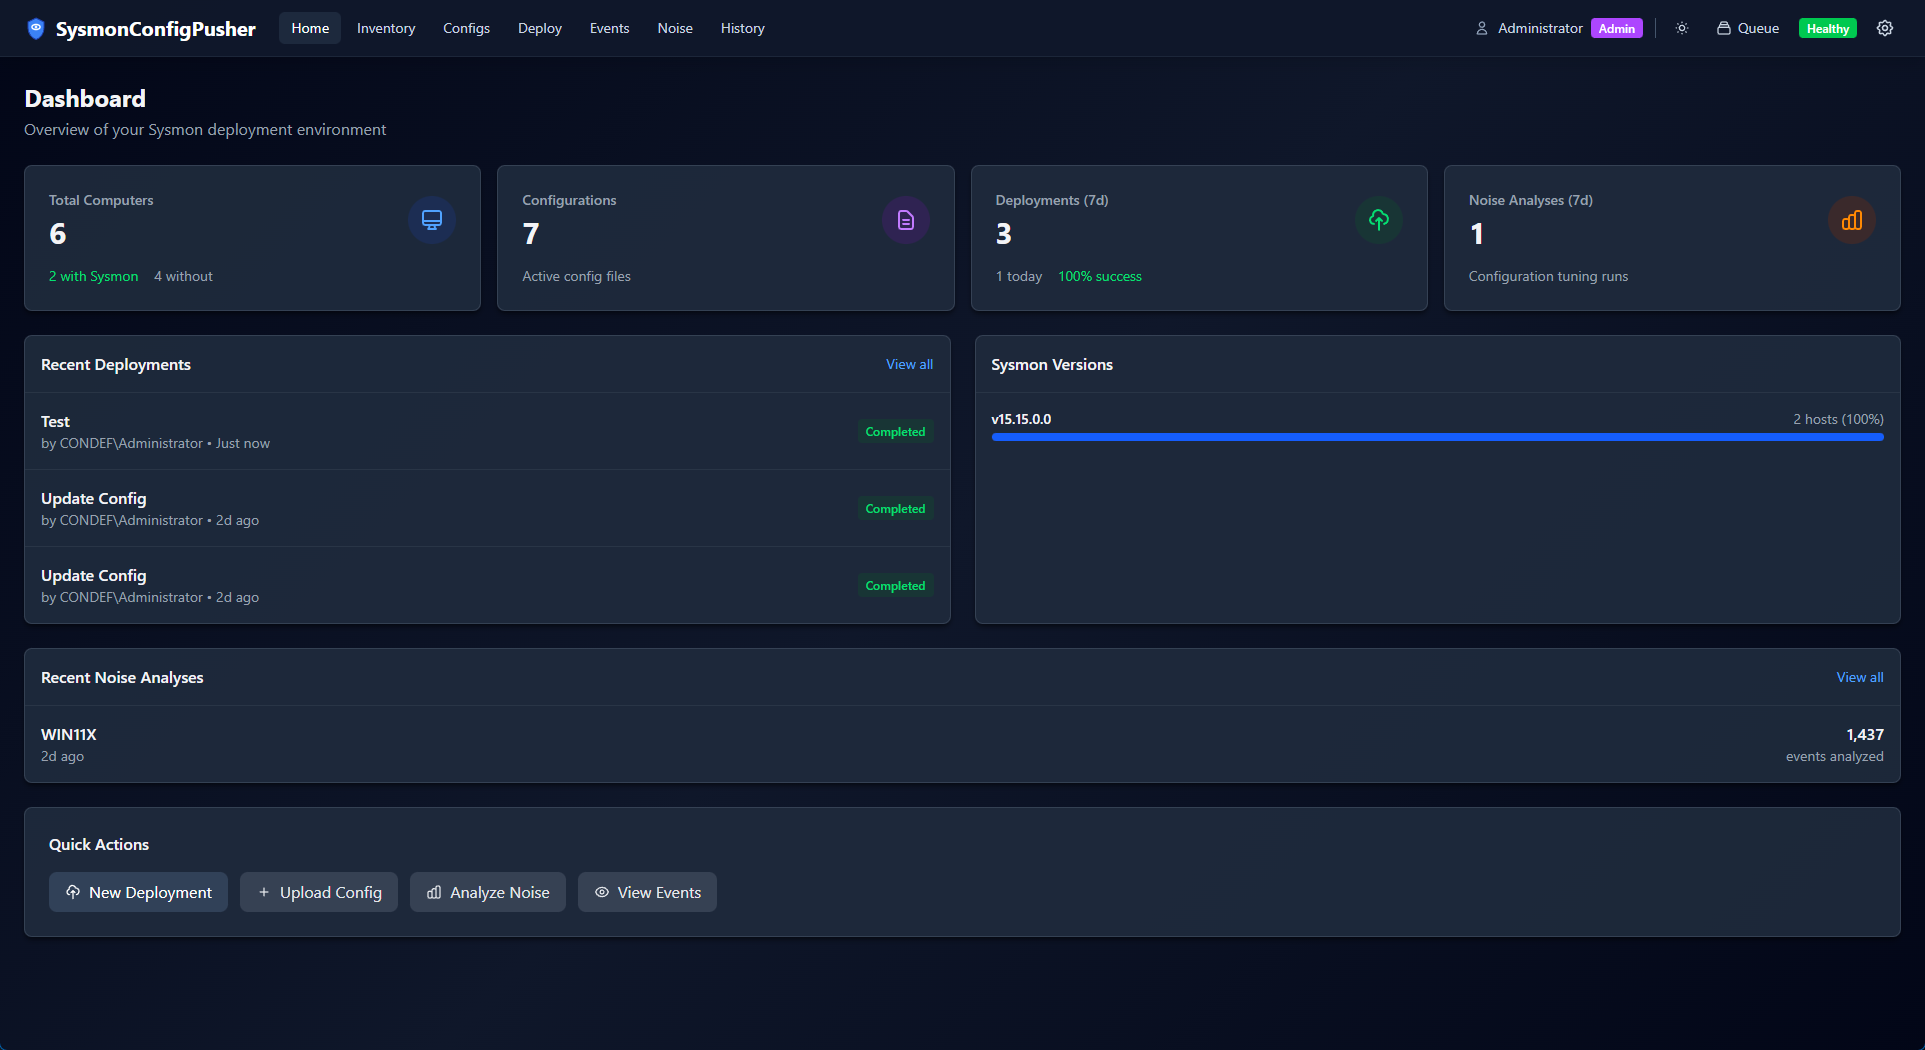
Web-based tool for managing and deploying Sysmon configurations across Windows endpoints via agentless (WMI/SMB) or agent-based methods, with remote…