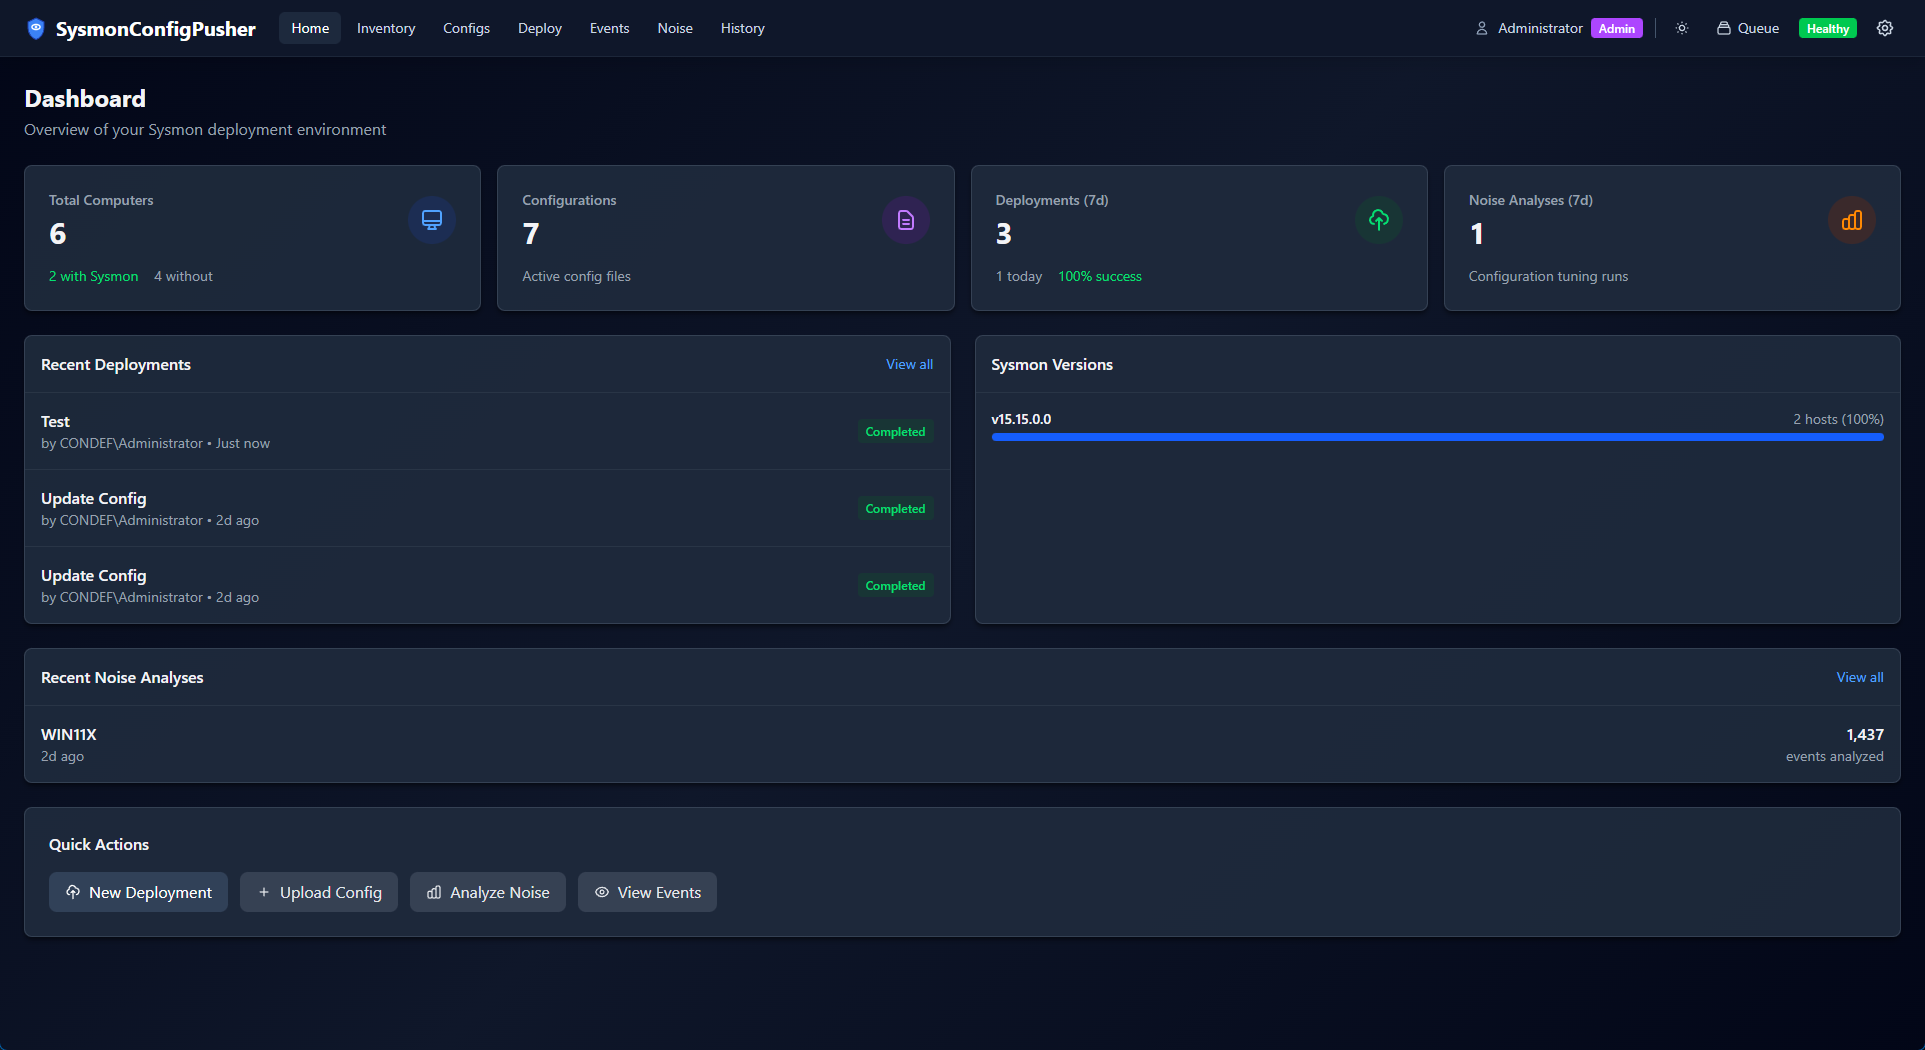

SysmonConfigPusher2
Web-based tool for managing and deploying Sysmon configurations across Windows endpoints via agentless (WMI/SMB) or agent-based methods, with remote…

Web-based tool for managing and deploying Sysmon configurations across Windows endpoints via agentless (WMI/SMB) or agent-based methods, with remote…

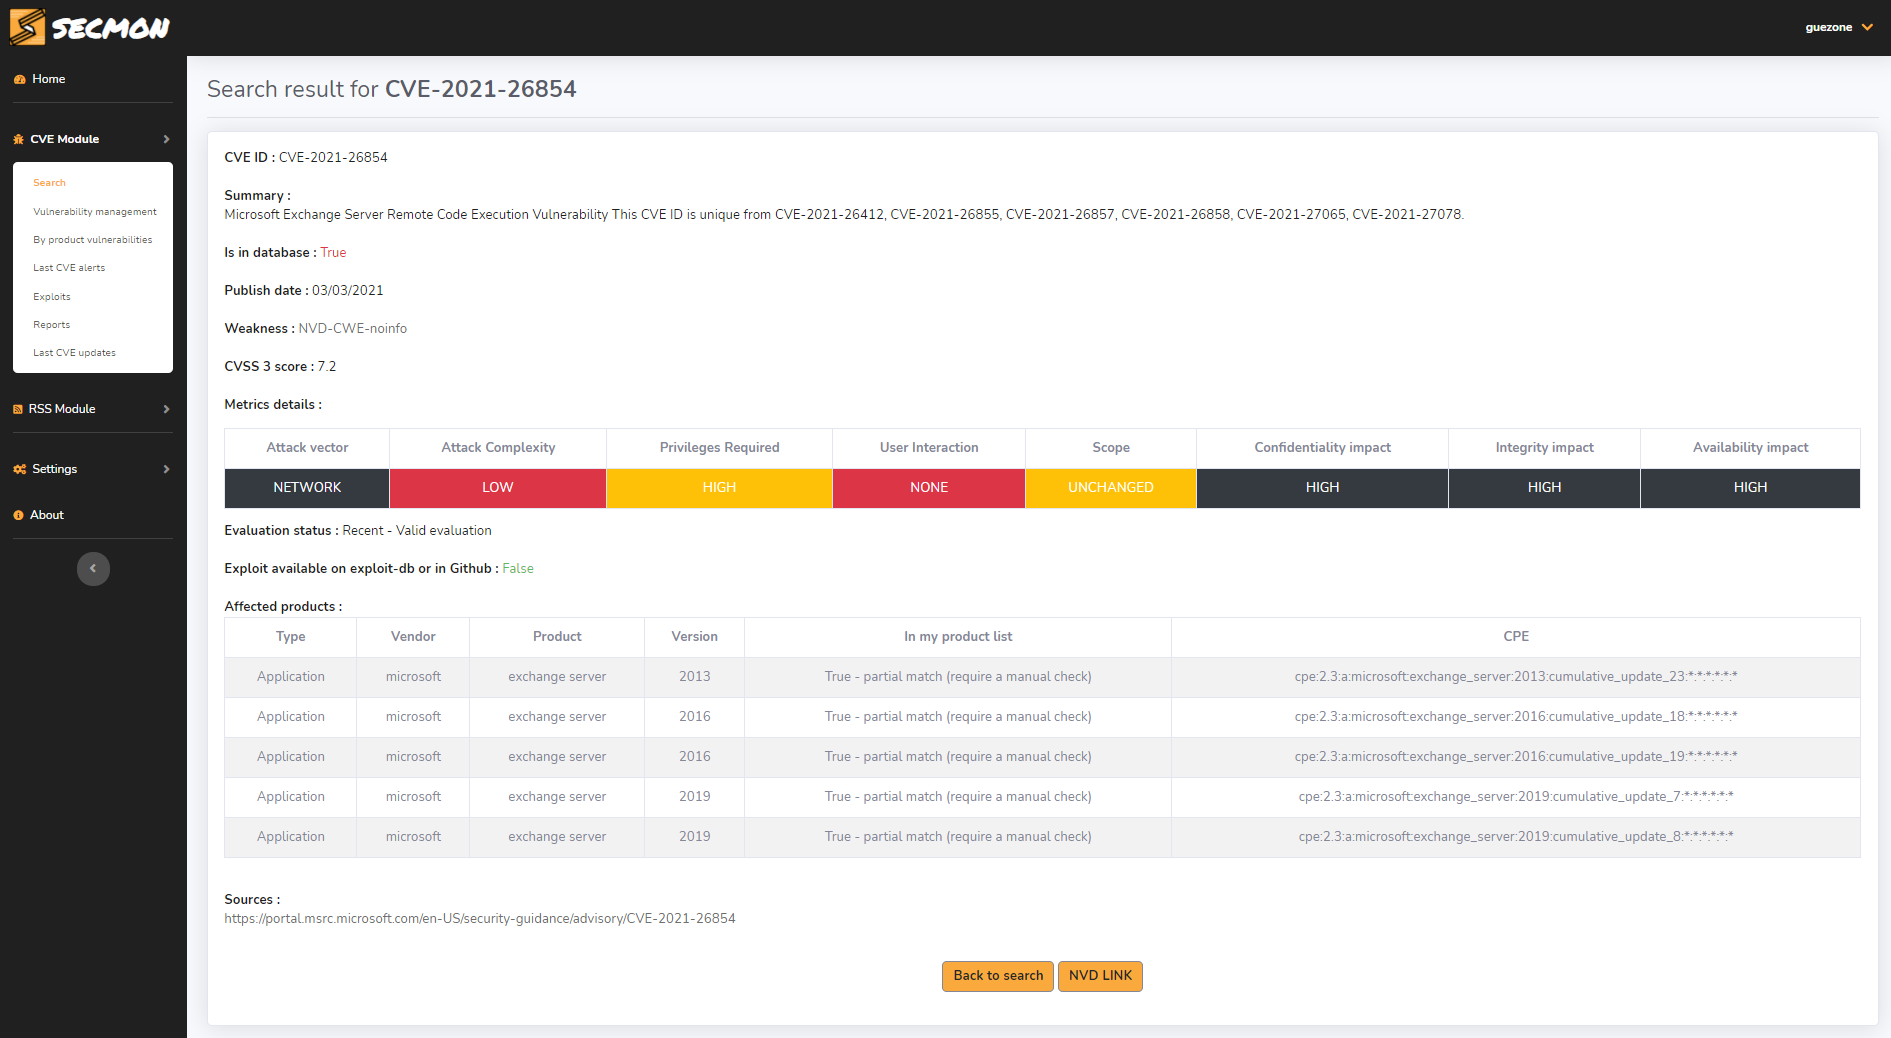
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.

CVE-2025-31324 & CVE-2025-42999 vulnerability and compromise assessment tool

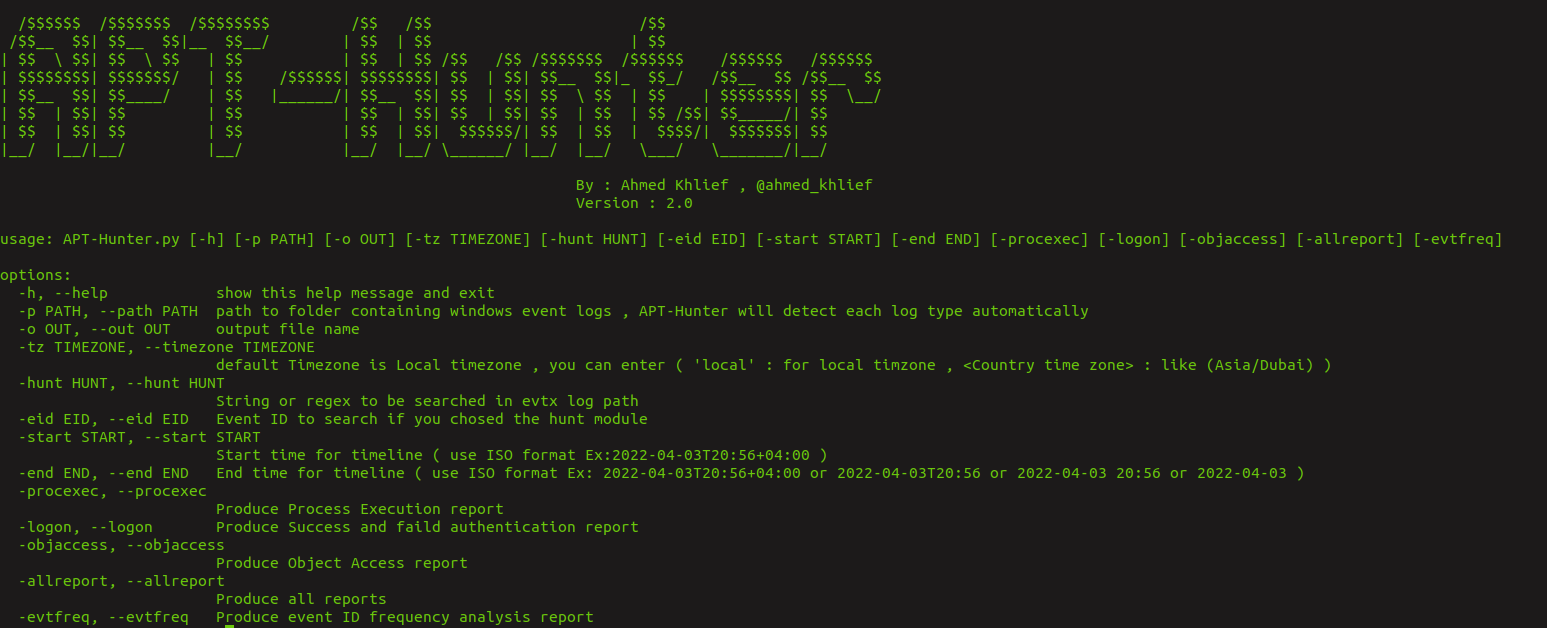
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…

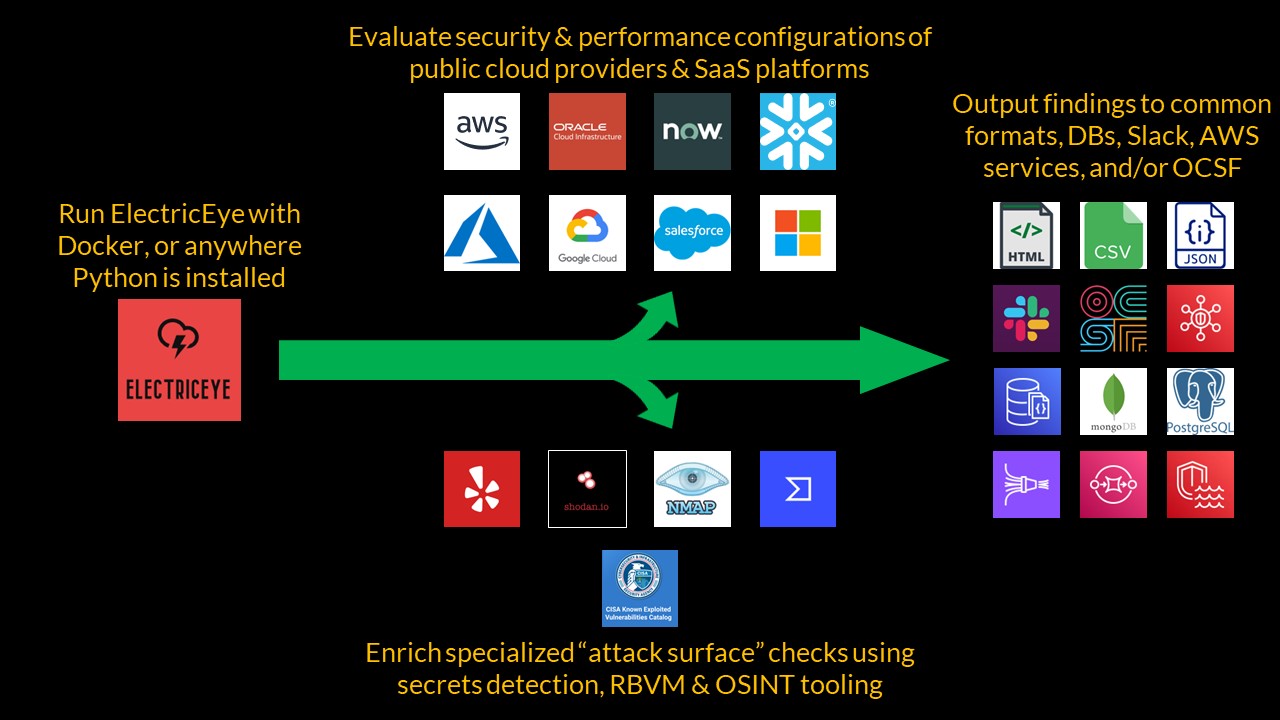
ElectricEye is a multi-cloud, multi-SaaS Python CLI tool for Asset Management, Security Posture Management & Attack Surface Monitoring supporting…

Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…

A little tool for detecting suspicious privileged NTLM connections, in particular Pass-The-Hash attack, based on event viewer logs.

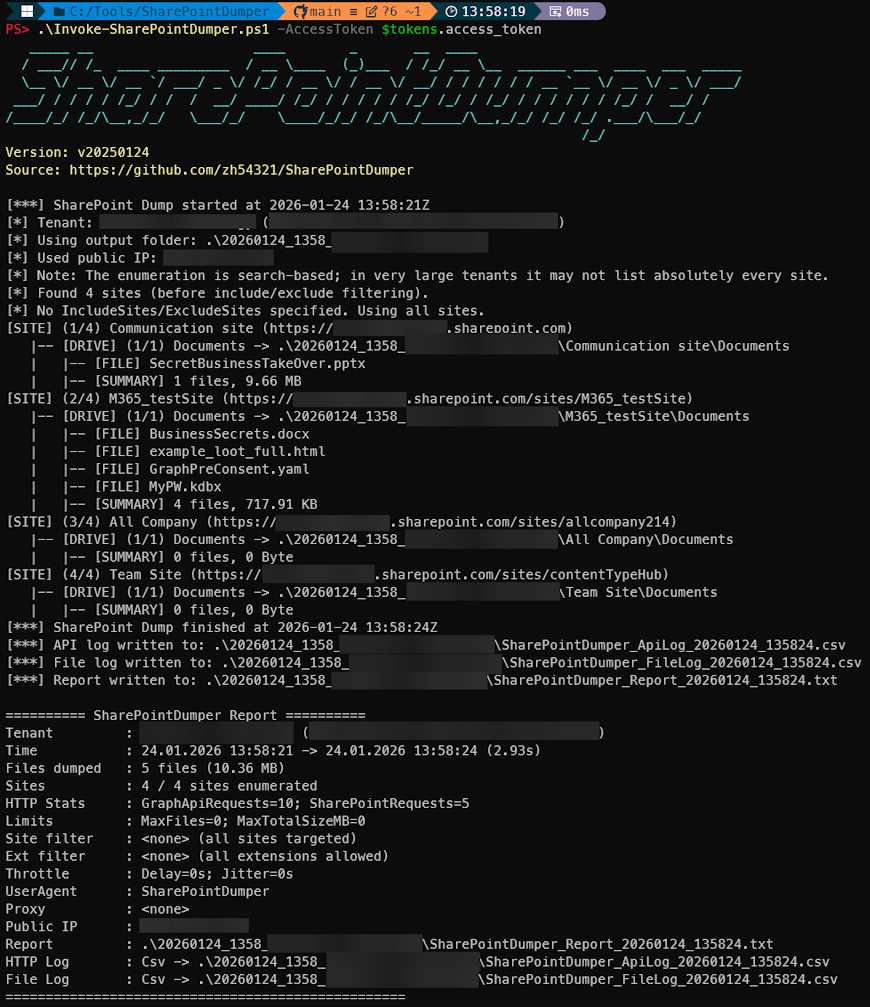
PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…

Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…

Security research tool for PaperCut CVE-2026-81578 & CVE-2026-82078

Query high-fidelity cloud detections for known threat actors across AWS, Azure, and GCP using CloudTrail logs and custom threat intelligence rules.

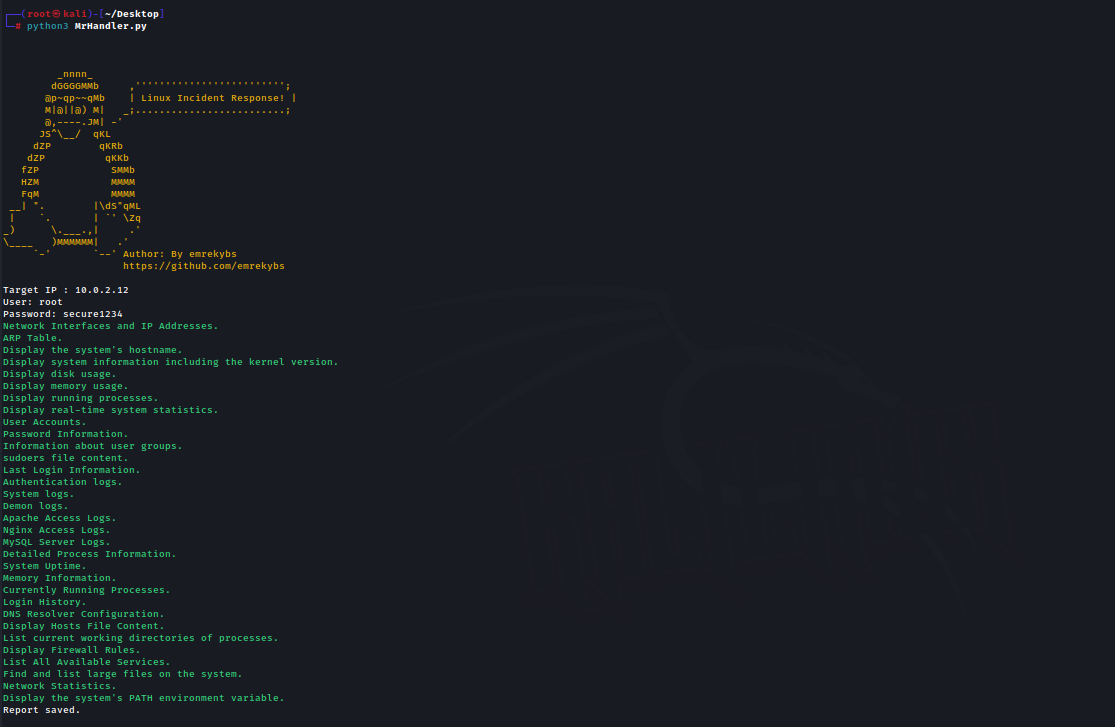
SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…

A ProcessMonitor visualization application written in rust.

Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…

Lightweight, secure control plane & real-time web dashboard in Crystal for Linux firewalld and NetworkManager host security.

CVE-2016-4999

Tool to dive Apache logs for evidence of exploitation of CVE-2018-7600

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…