
Aegis-releases
 adarsh14734/aegis-releases
Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…
ai-securityauthentication-authorizationconfiguration-auditing+5
adarsh14734/aegis-releasesSandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…
 shoucheng3/asf__karaf_cve-2022-22932_4-3-5
Modulith runtime with hot deployment, dynamic configuration, JAAS-based RBAC, and centralized logging. Supports REST/API, web, and Spring Boot…
 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!
 gmh5225/gatekeeper
Self-hosted SSH access gateway in Go with OIDC/LDAP auth, RBAC, MFA, session recording, audit export, encryption at rest, IP rules, and policy…
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 aker-gateway/aker
SSH bastion/jump host/jumpserver
 limo57640-crypto/cpanel-cve-41940-detector
Read-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.
 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
 secdev02/cyber-decoy
Experimental Decoy Broker
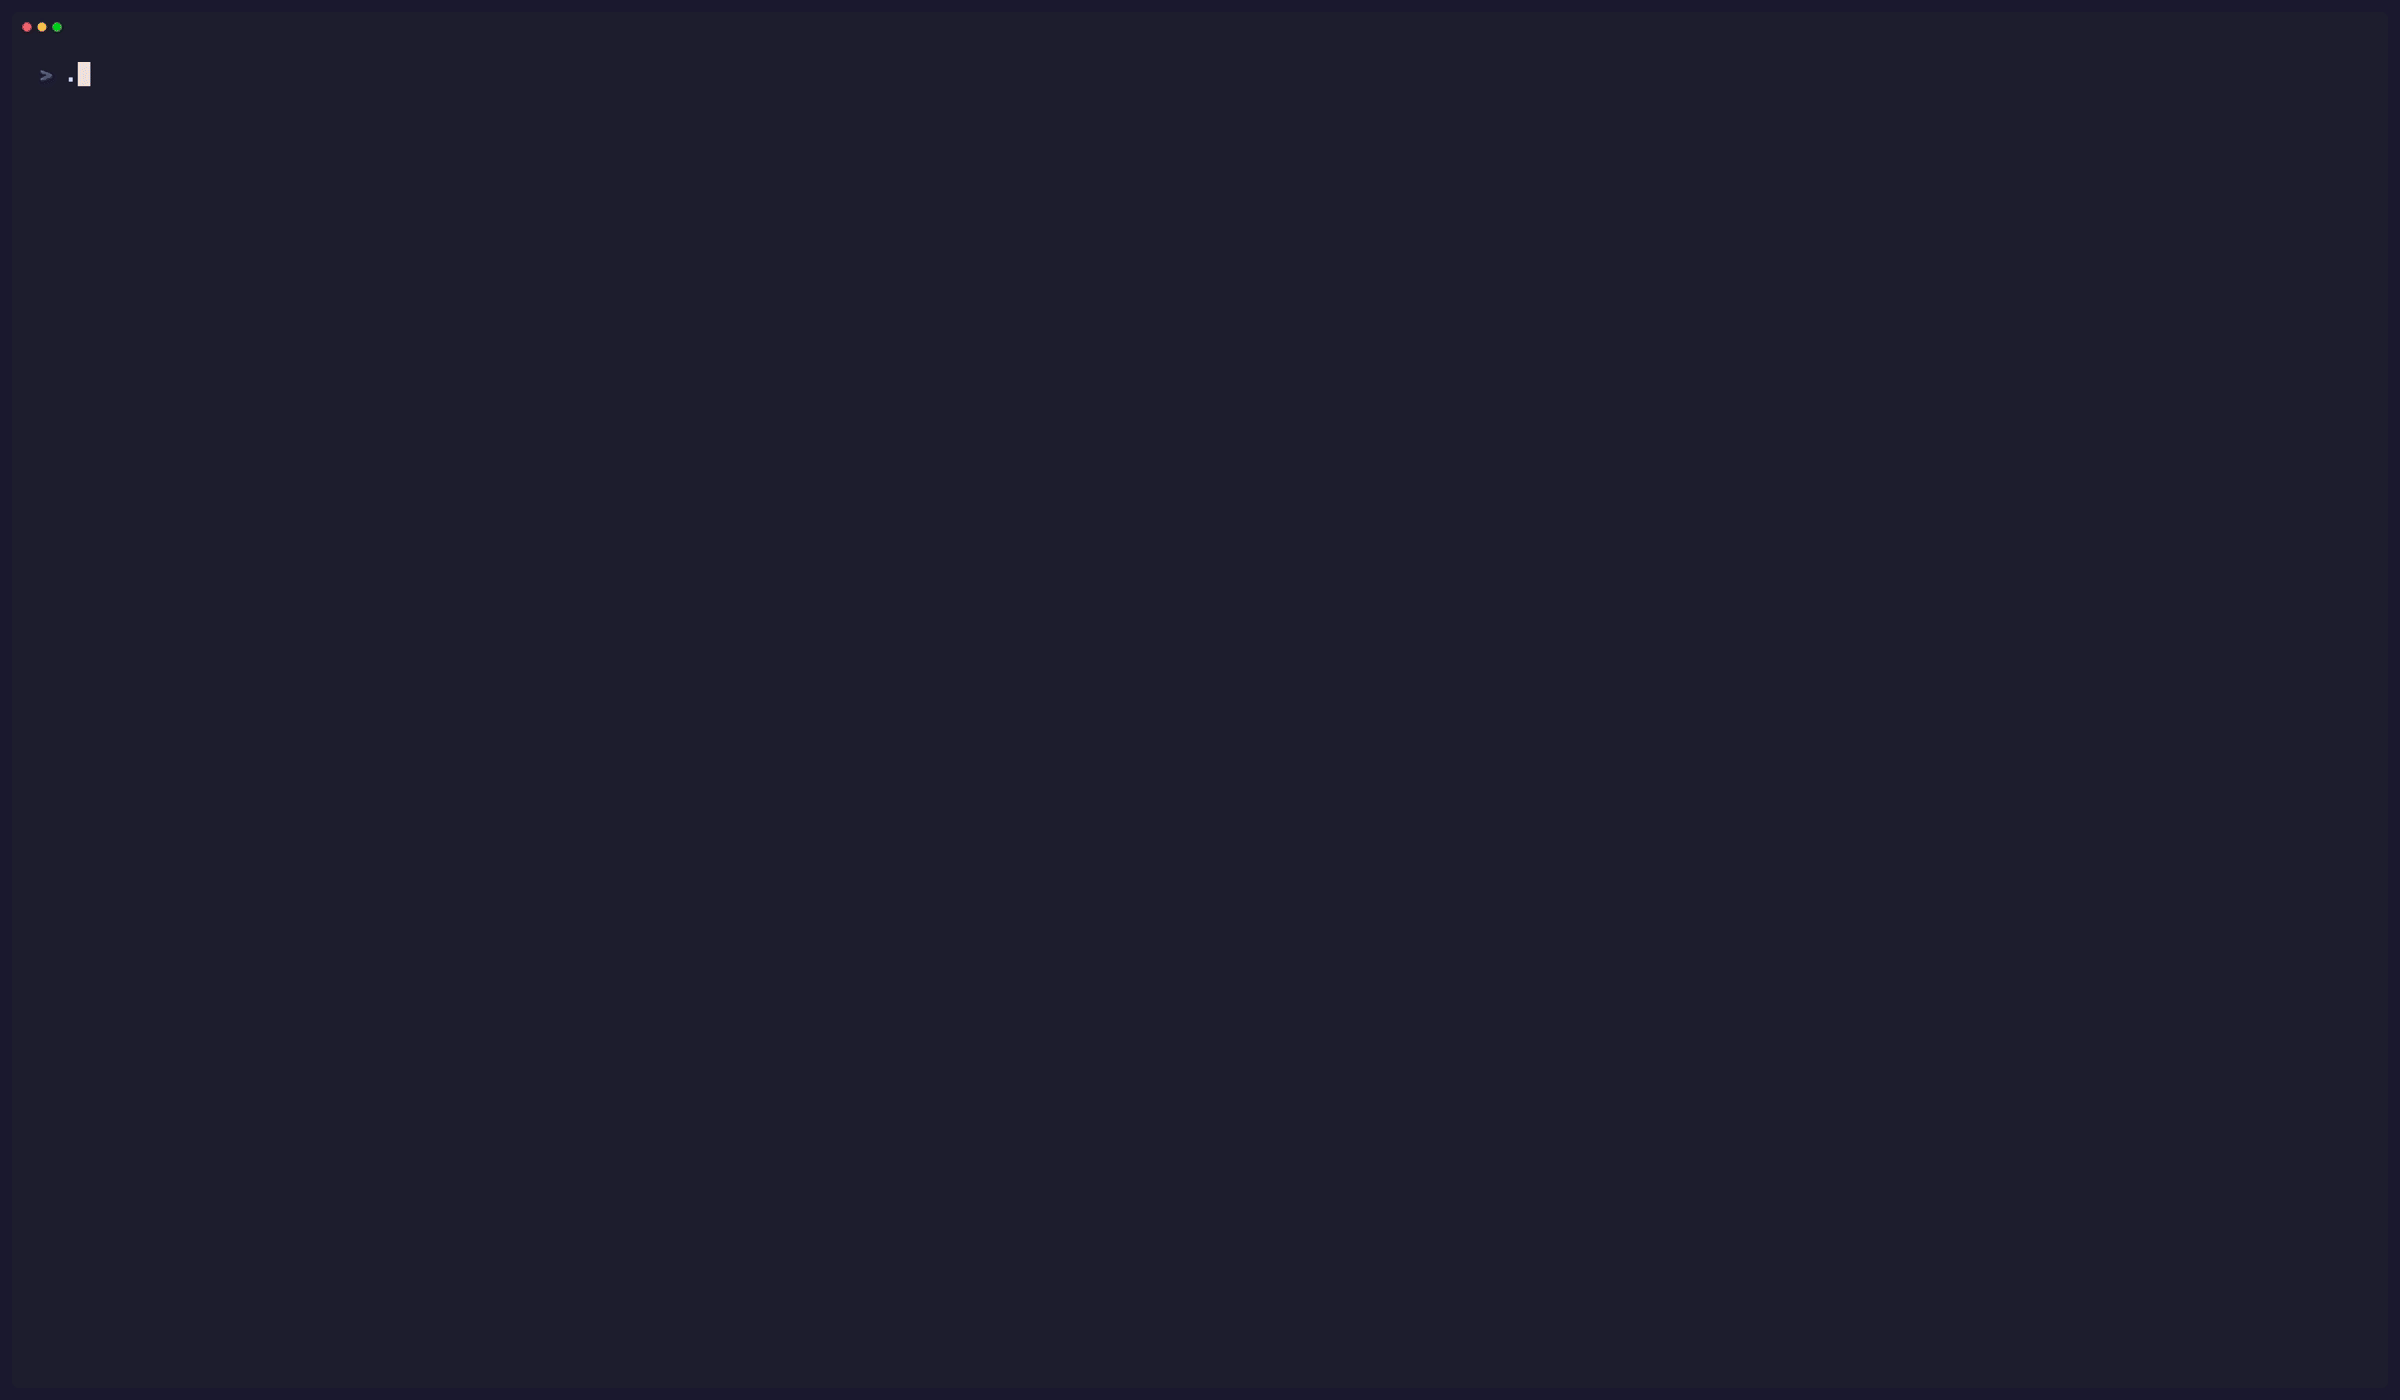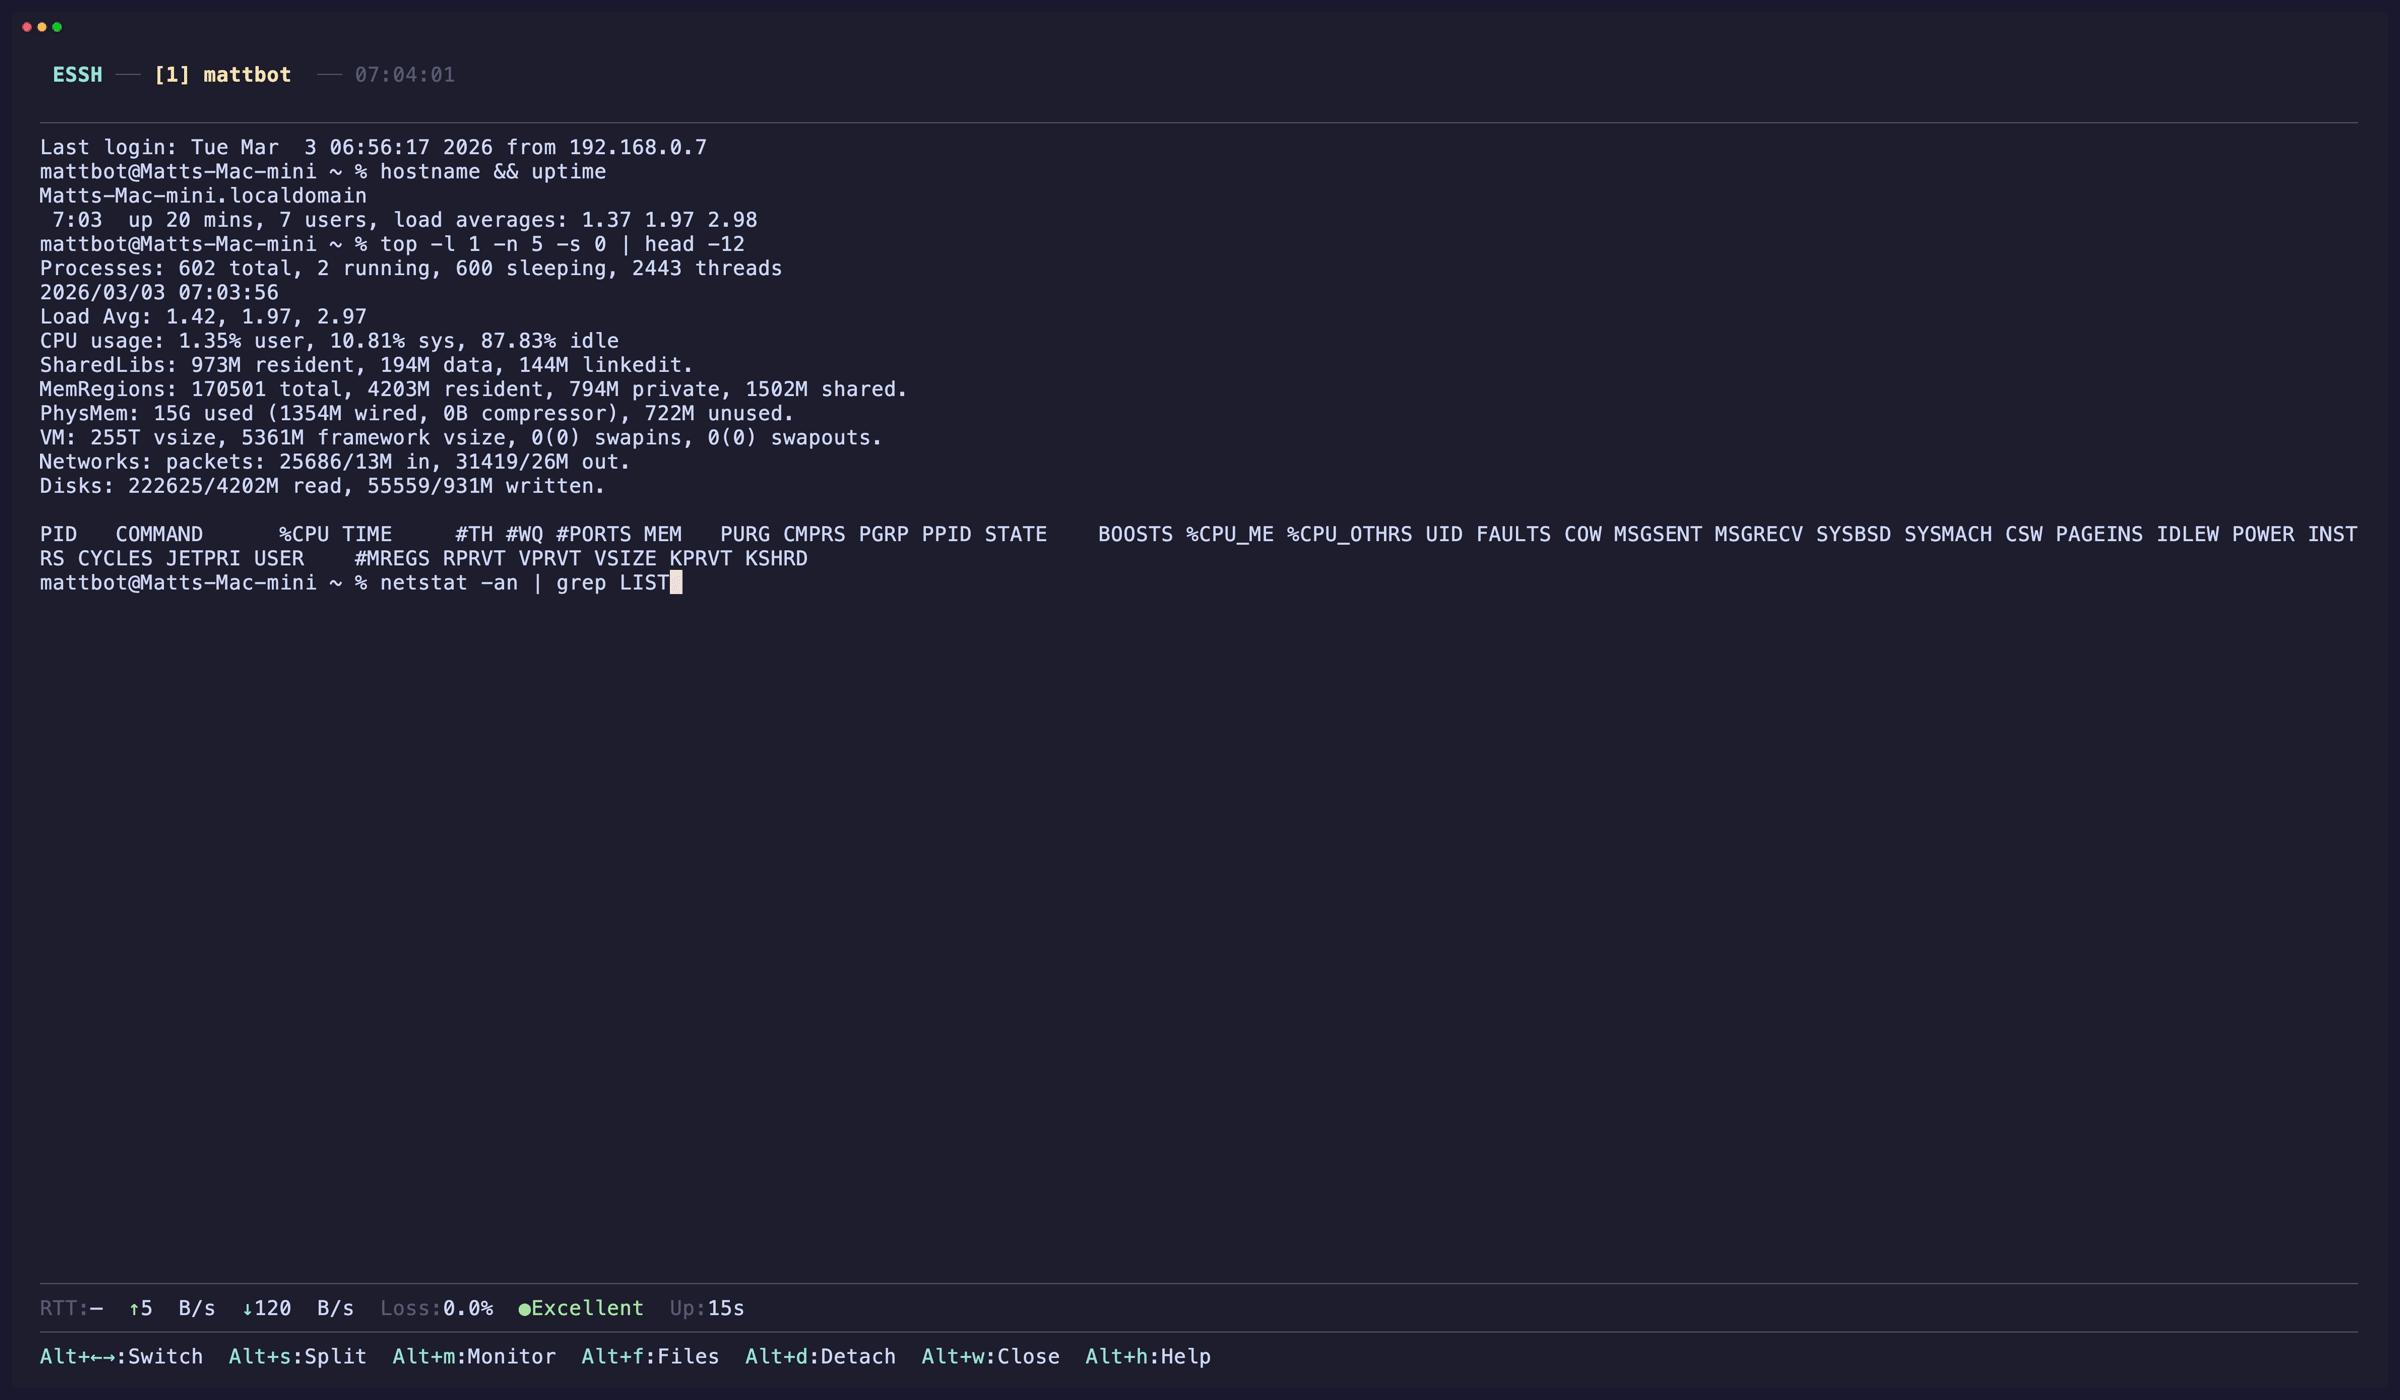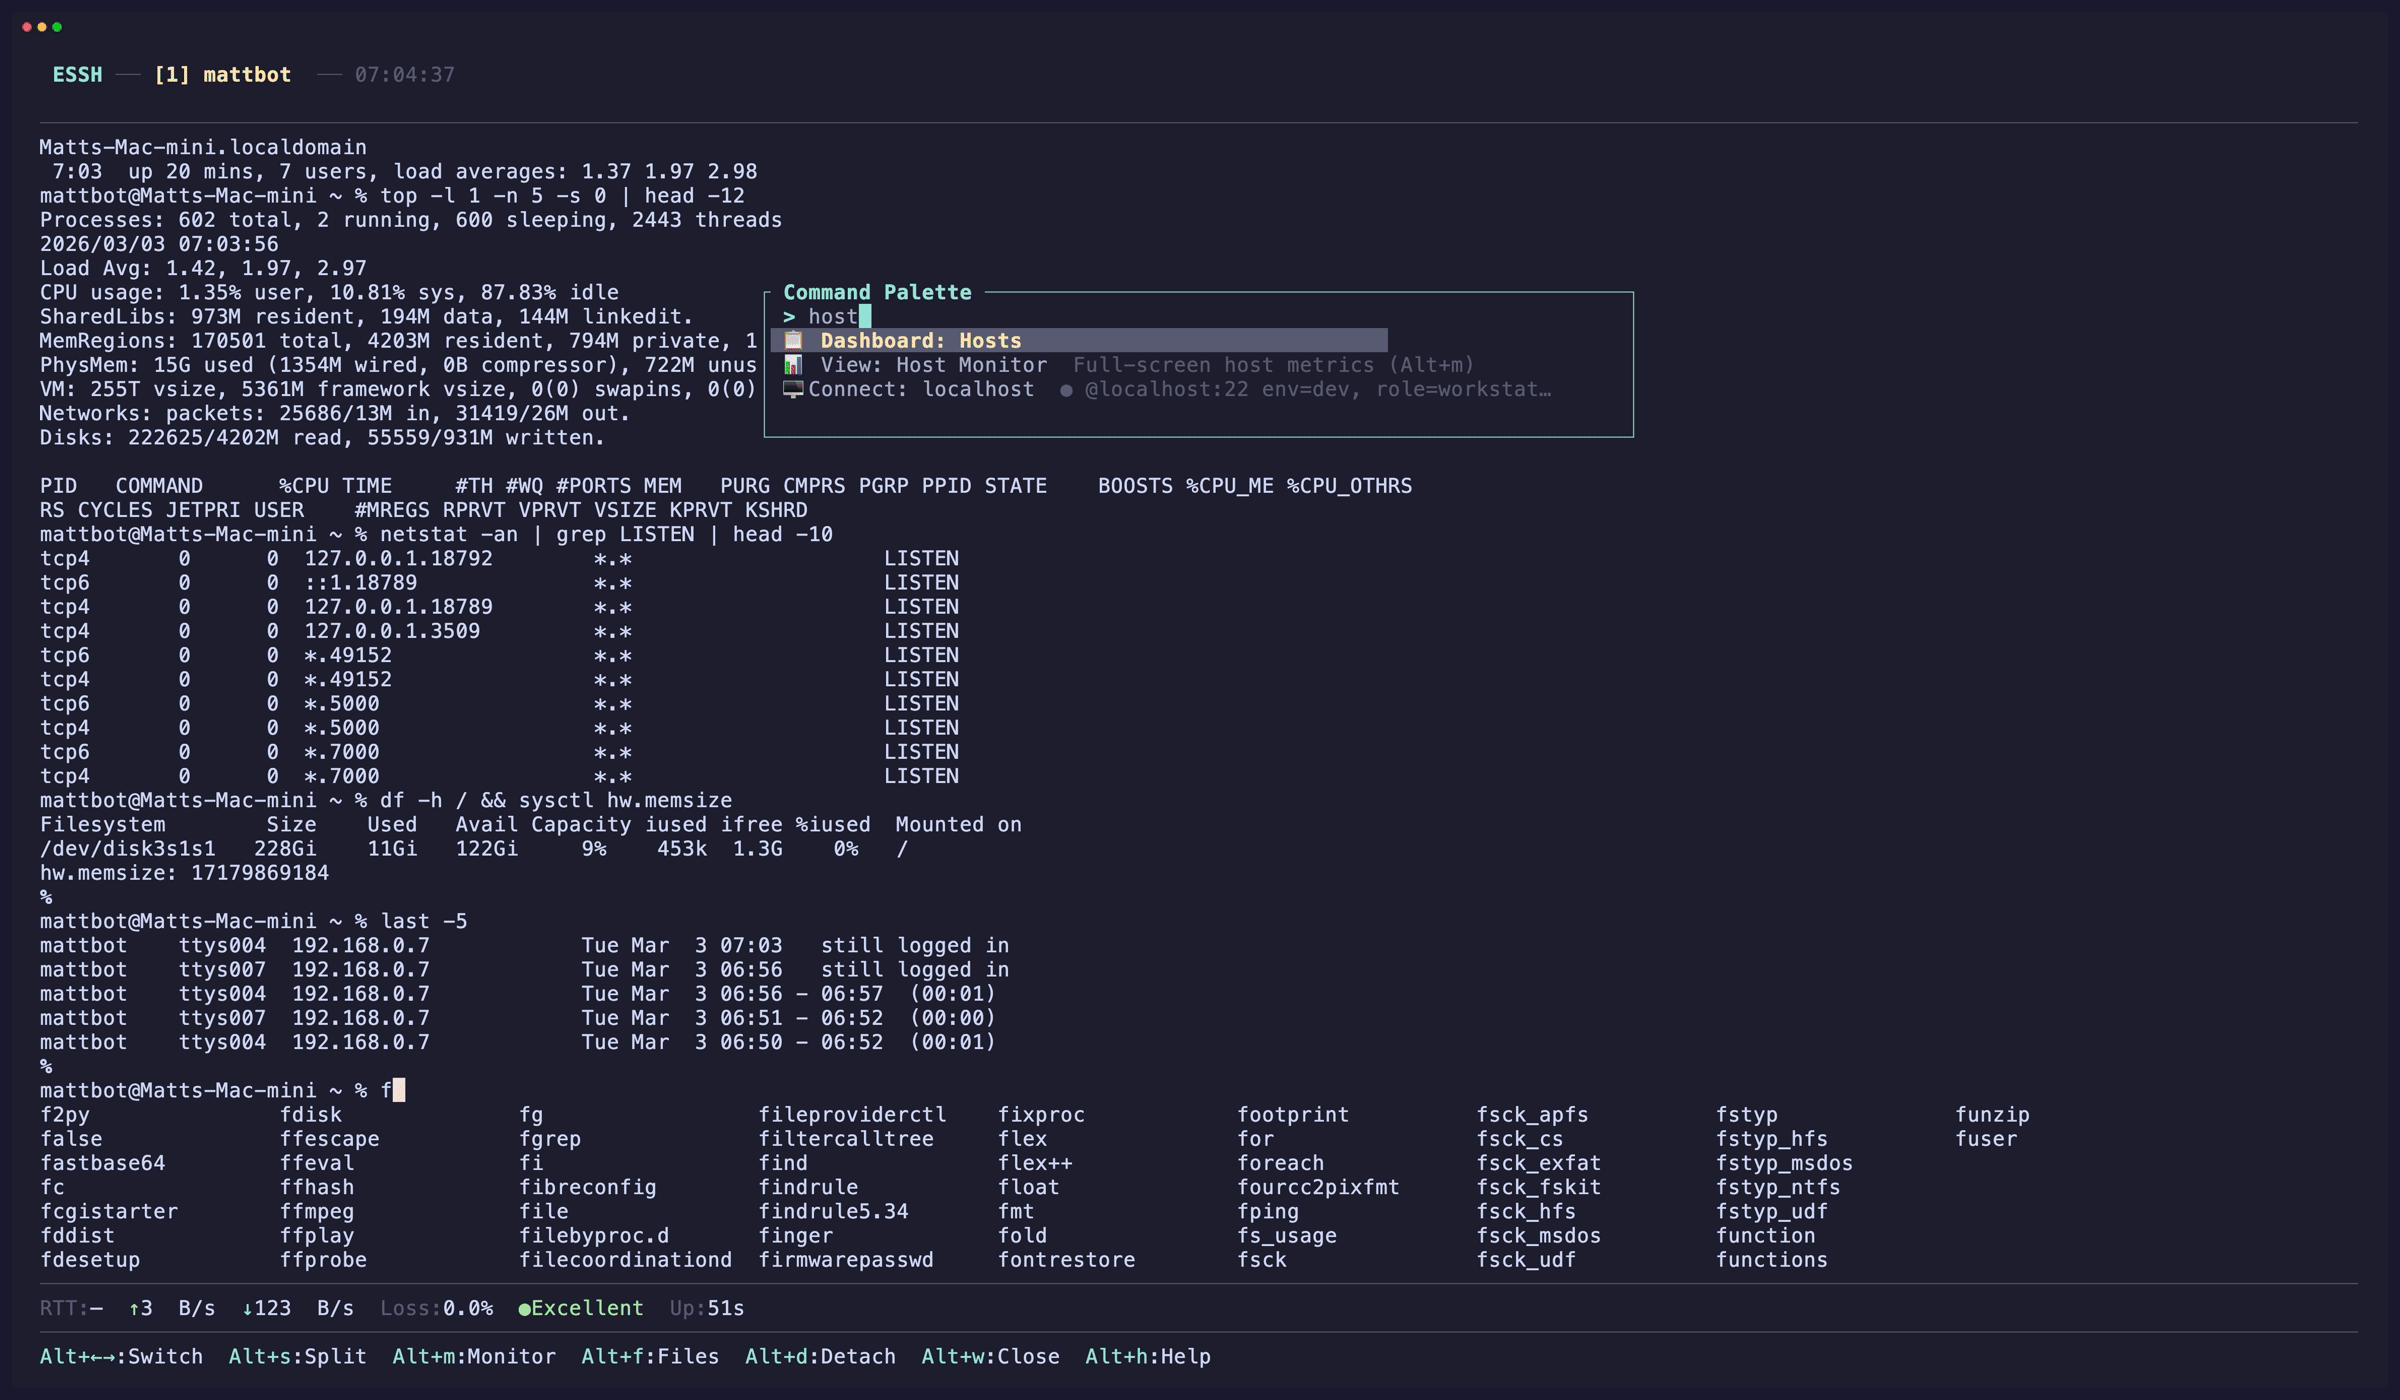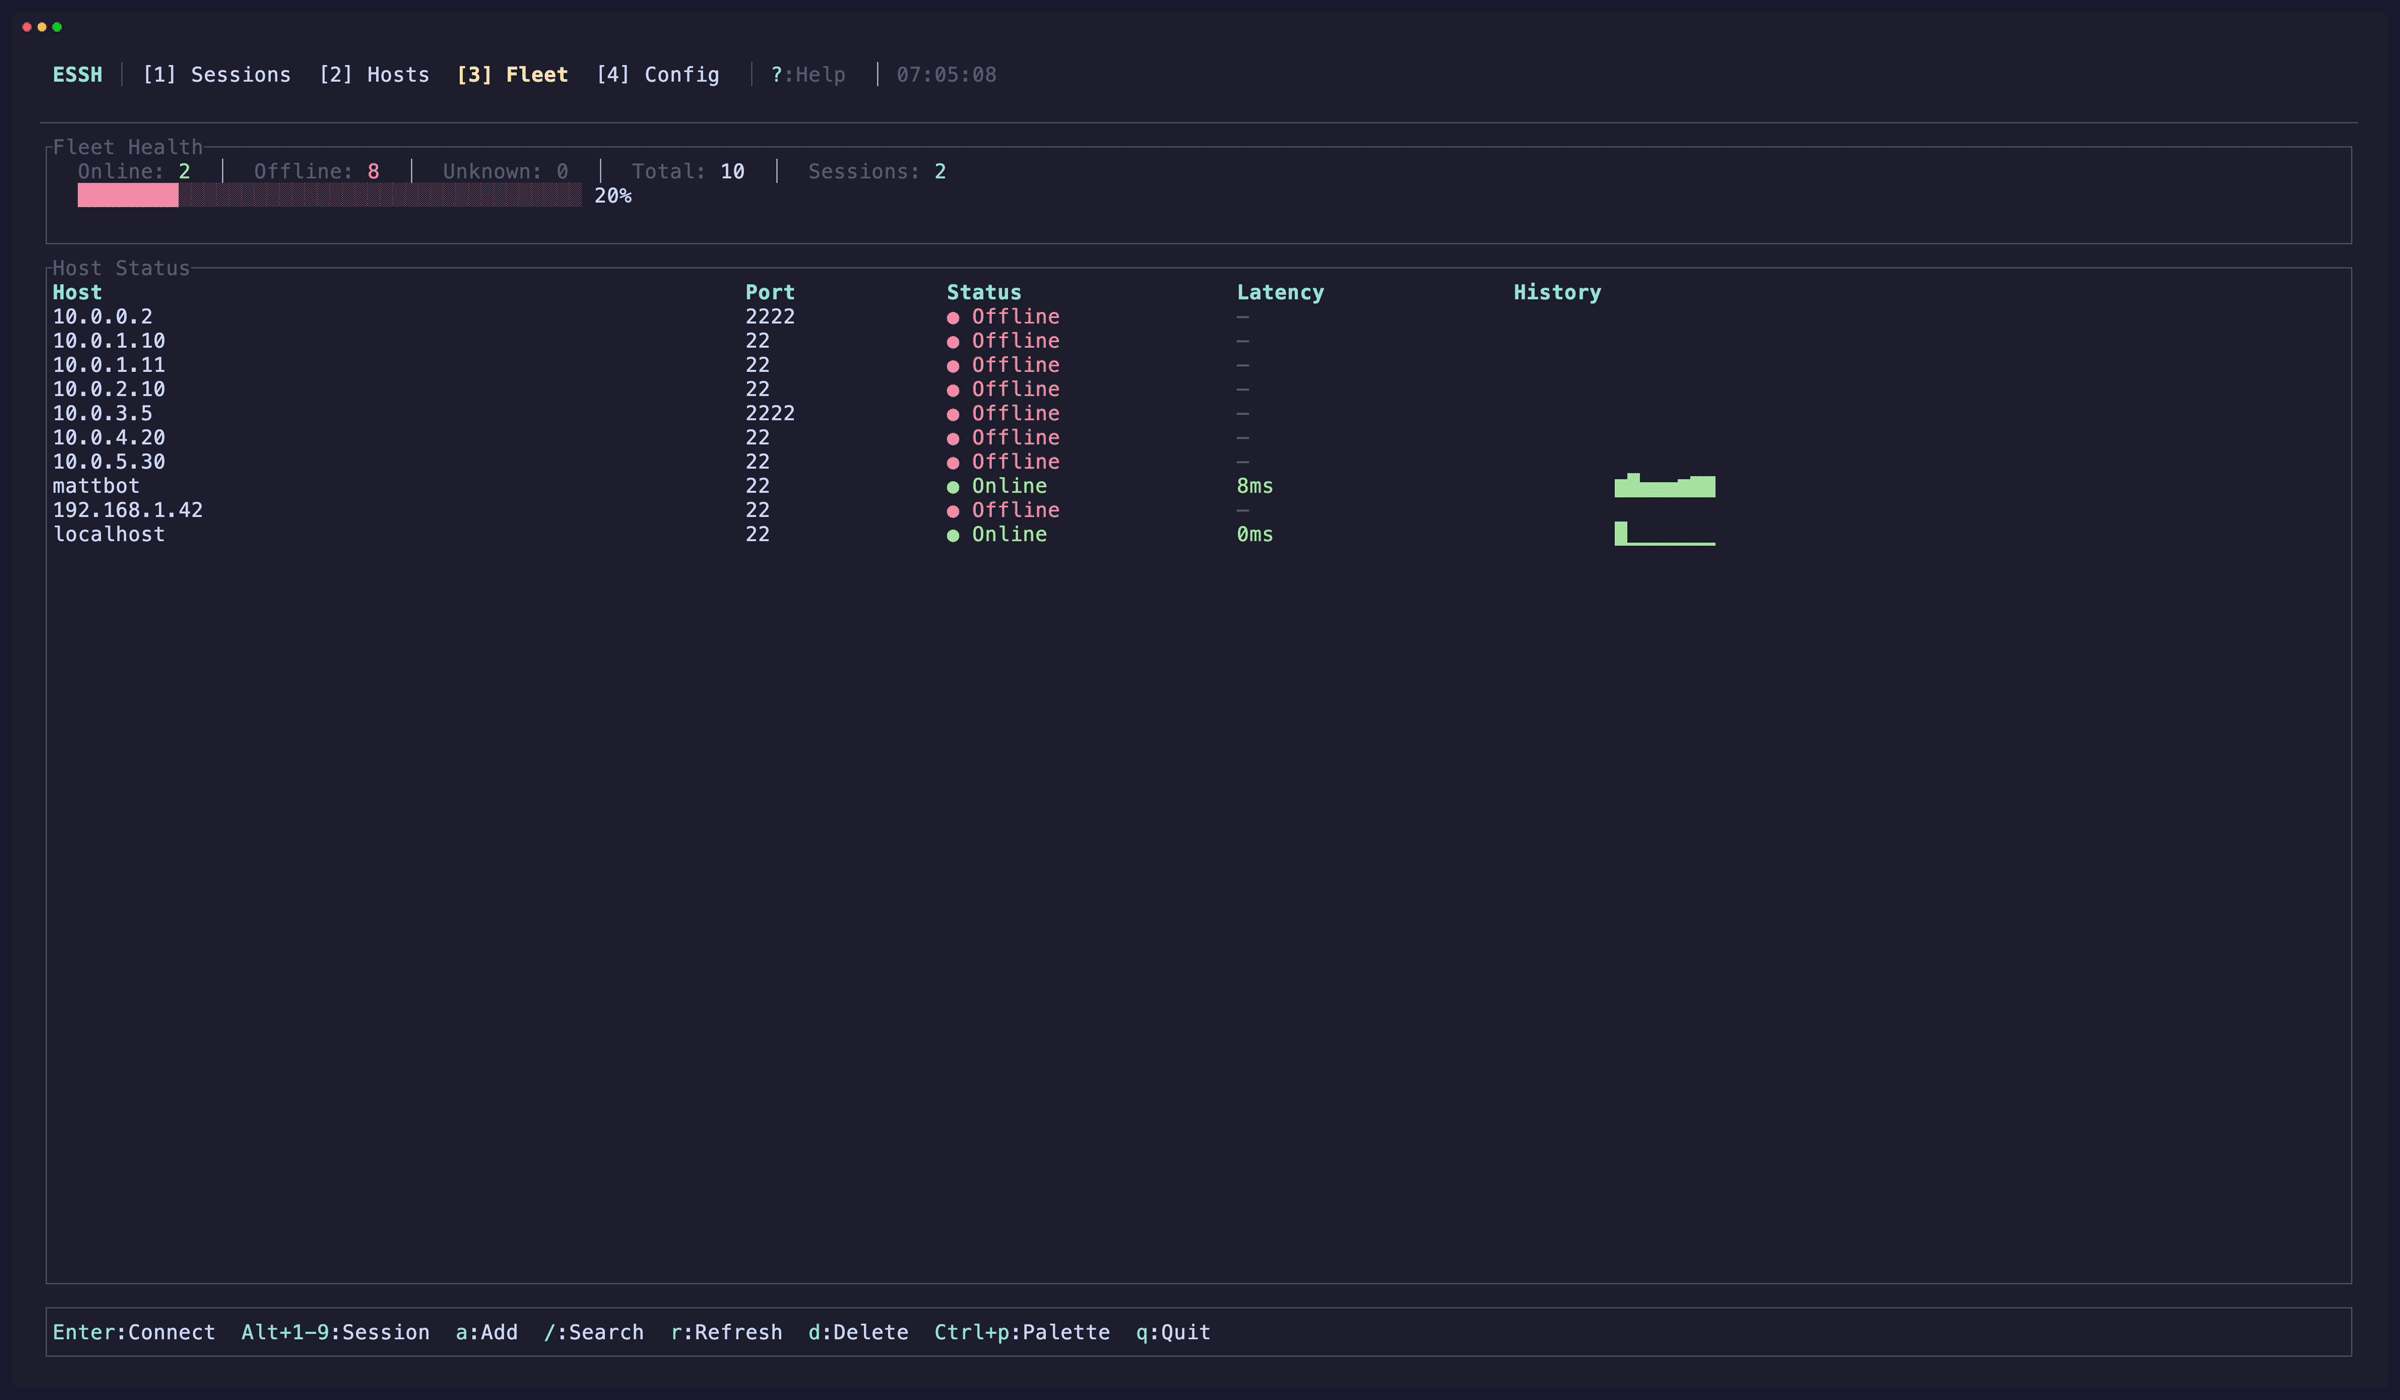 matthart1983/essh
Enhanced SSH client with TUI — manage connections, keys, and sessions
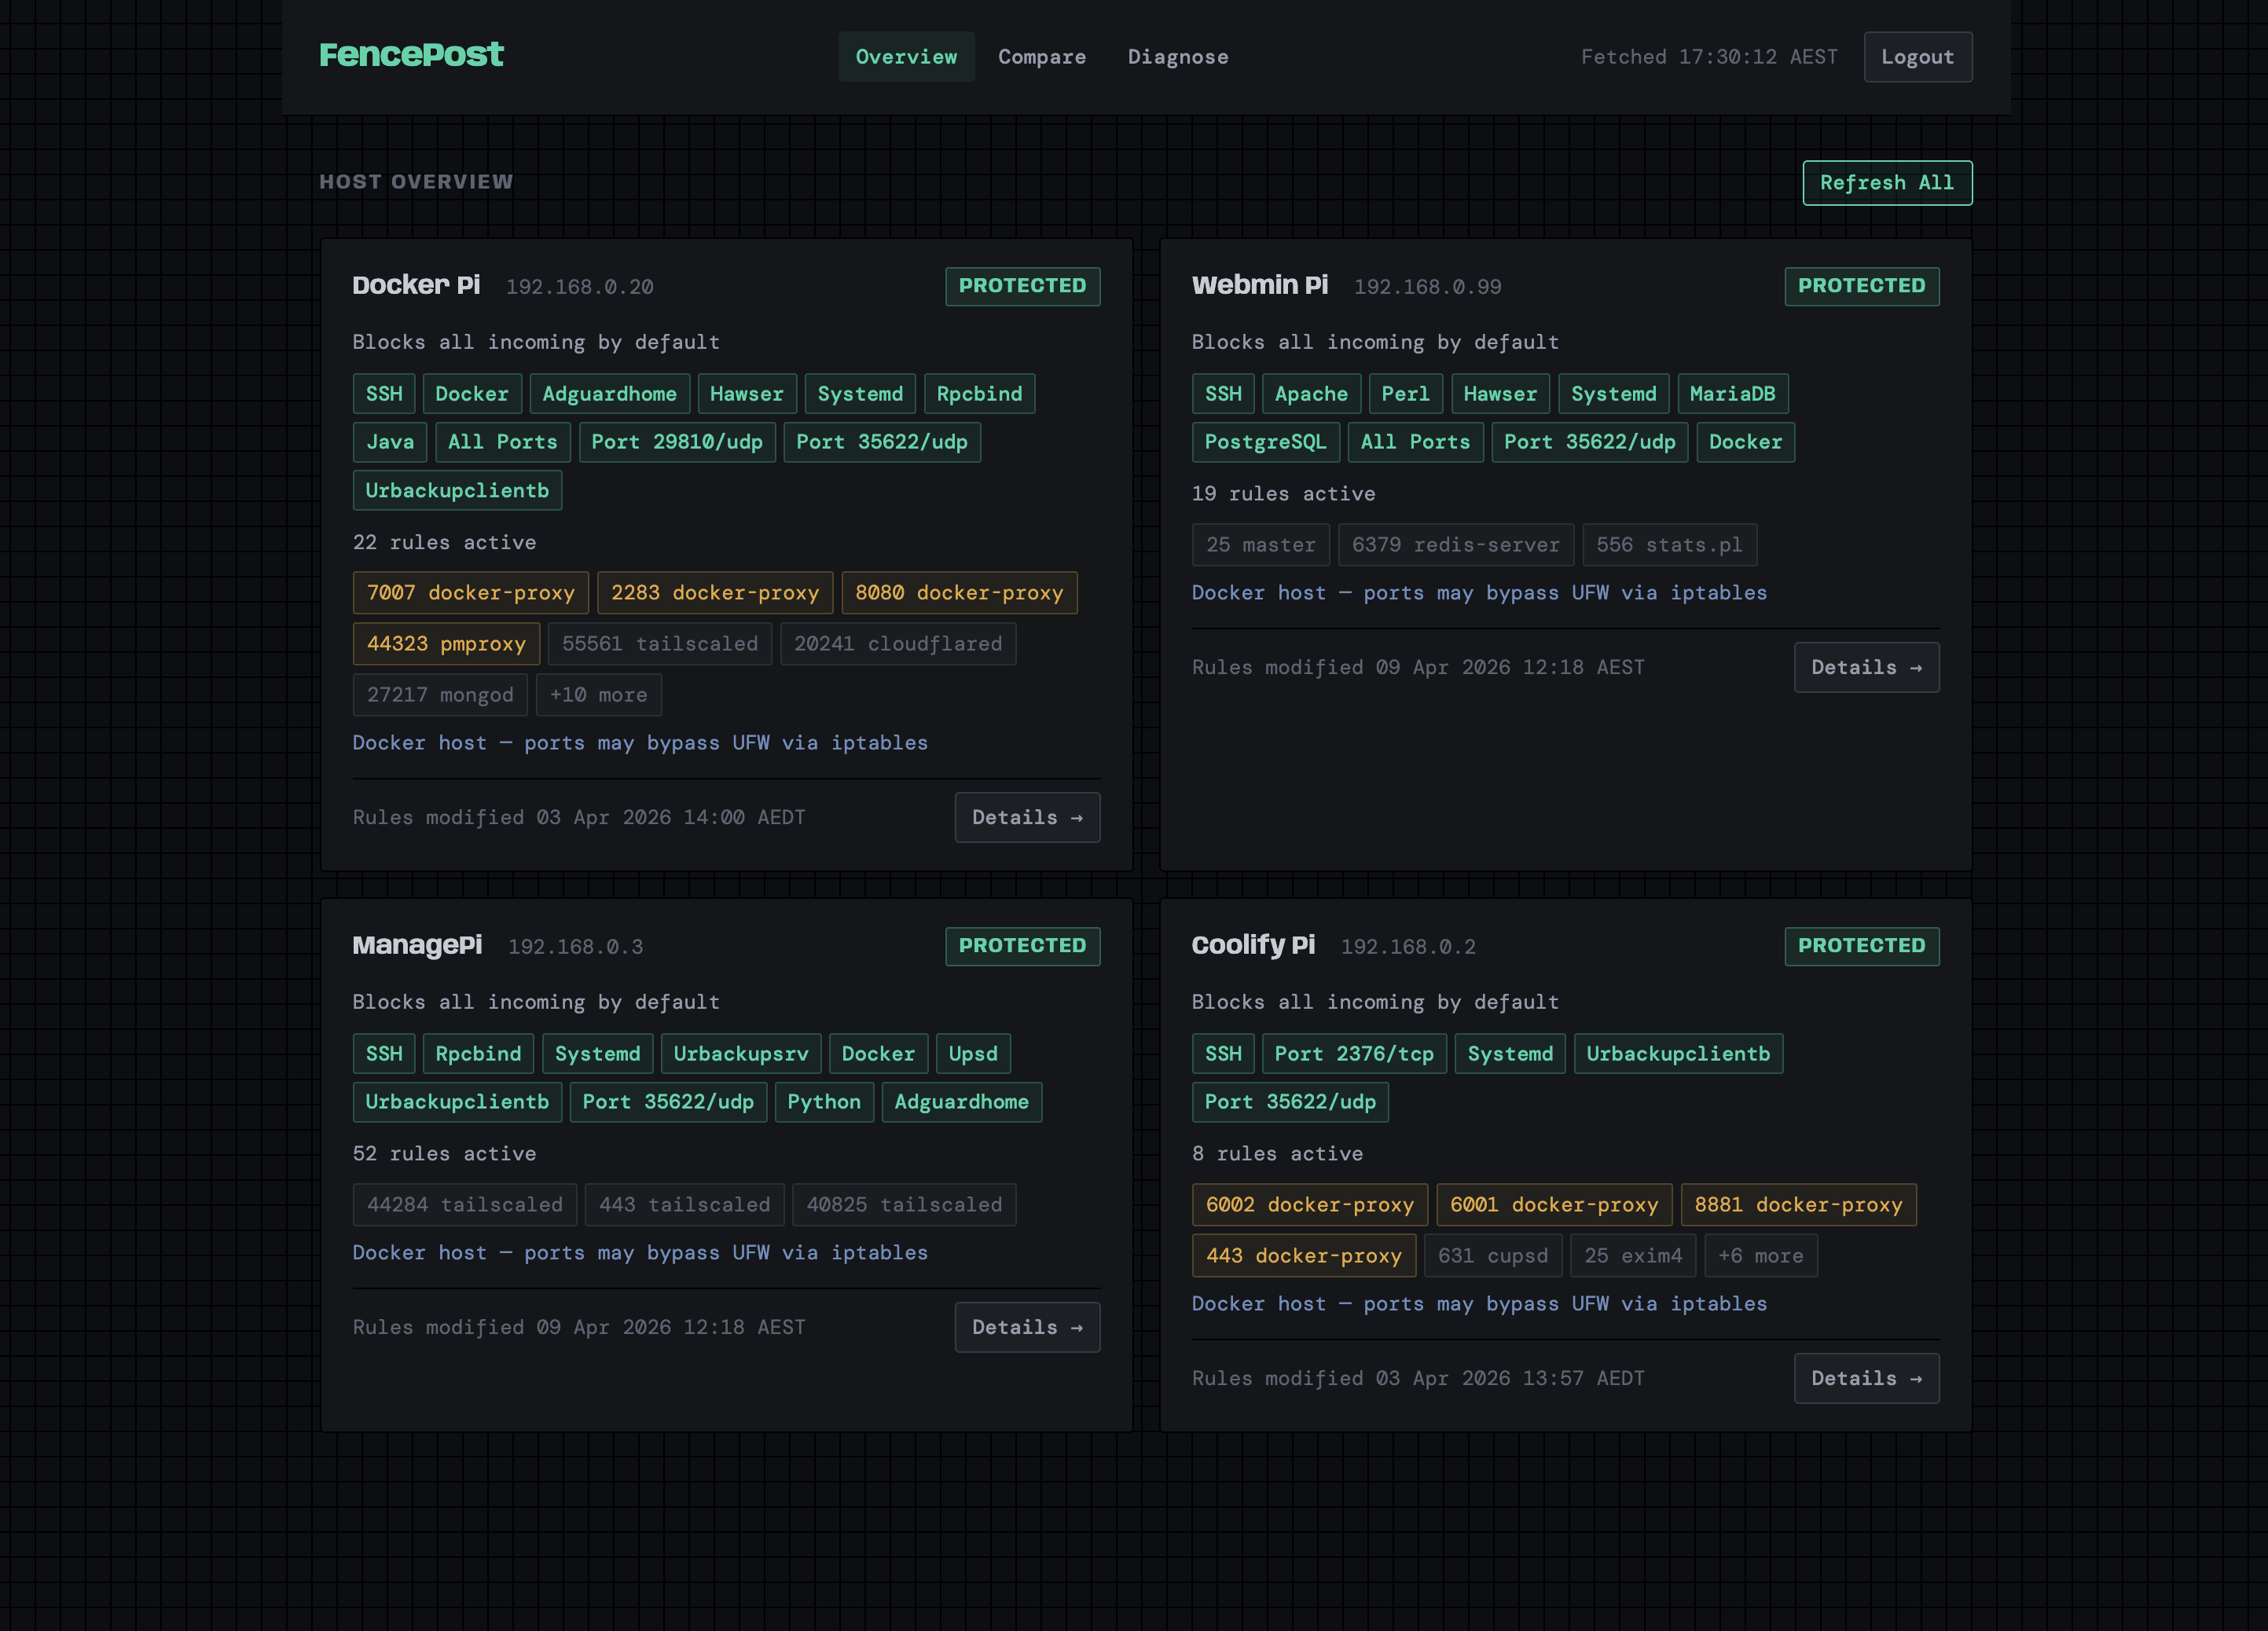 seriocomic/fencepost
Multi-host UFW firewall dashboard — explains rules in plain English, detects security gaps, and provides connection diagnostics
 tnich/honssh
HonSSH is designed to log all SSH communications between a client and server.
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 jconeby/elastic-peak-dashboards
PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…
 g0tmi1k/kippo-g0tmi1k
Medium-interaction SSH honeypot that logs brute force attacks and full attacker shell interactions, with customization options to reduce…
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
 alisha-chaudhary/ssh-enum
This project explores whether modern OpenSSH reveals valid usernames through subtle response or timing differences. CVE-2016-6210 user enumeration…