
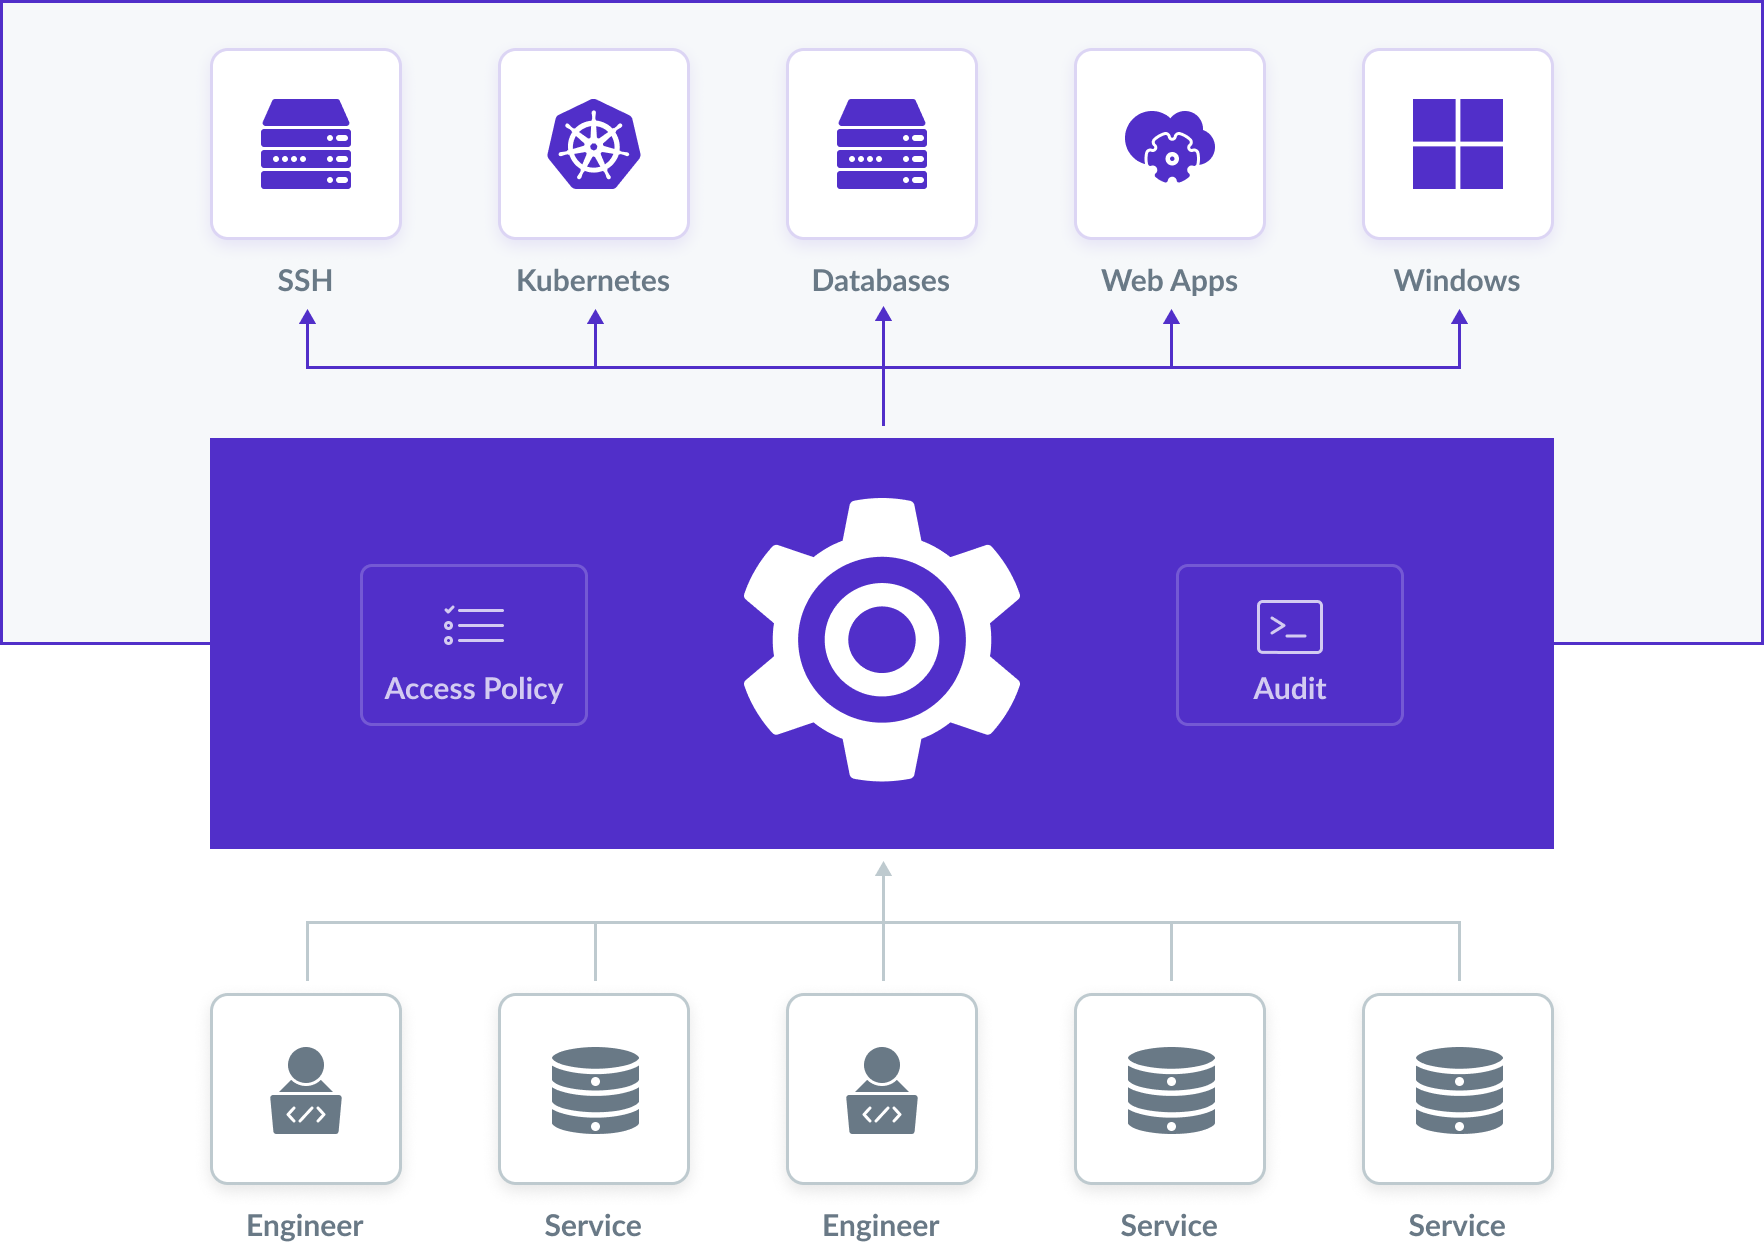
teleport
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
api-securityauthentication-authorizationcloud-security+7
21.1k
gravitational/teleportThe easiest, and most secure way to access and protect all of your infrastructure.
 justicerage/freedomfighting
A collection of scripts which may come in handy during your freedom fighting activities.
 dshield-isc/dshield
Installs and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to…
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 tnich/honssh
HonSSH is designed to log all SSH communications between a client and server.
 g0tmi1k/kippo-g0tmi1k
Medium-interaction SSH honeypot that logs brute force attacks and full attacker shell interactions, with customization options to reduce…
 jaksi/sshesame
An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
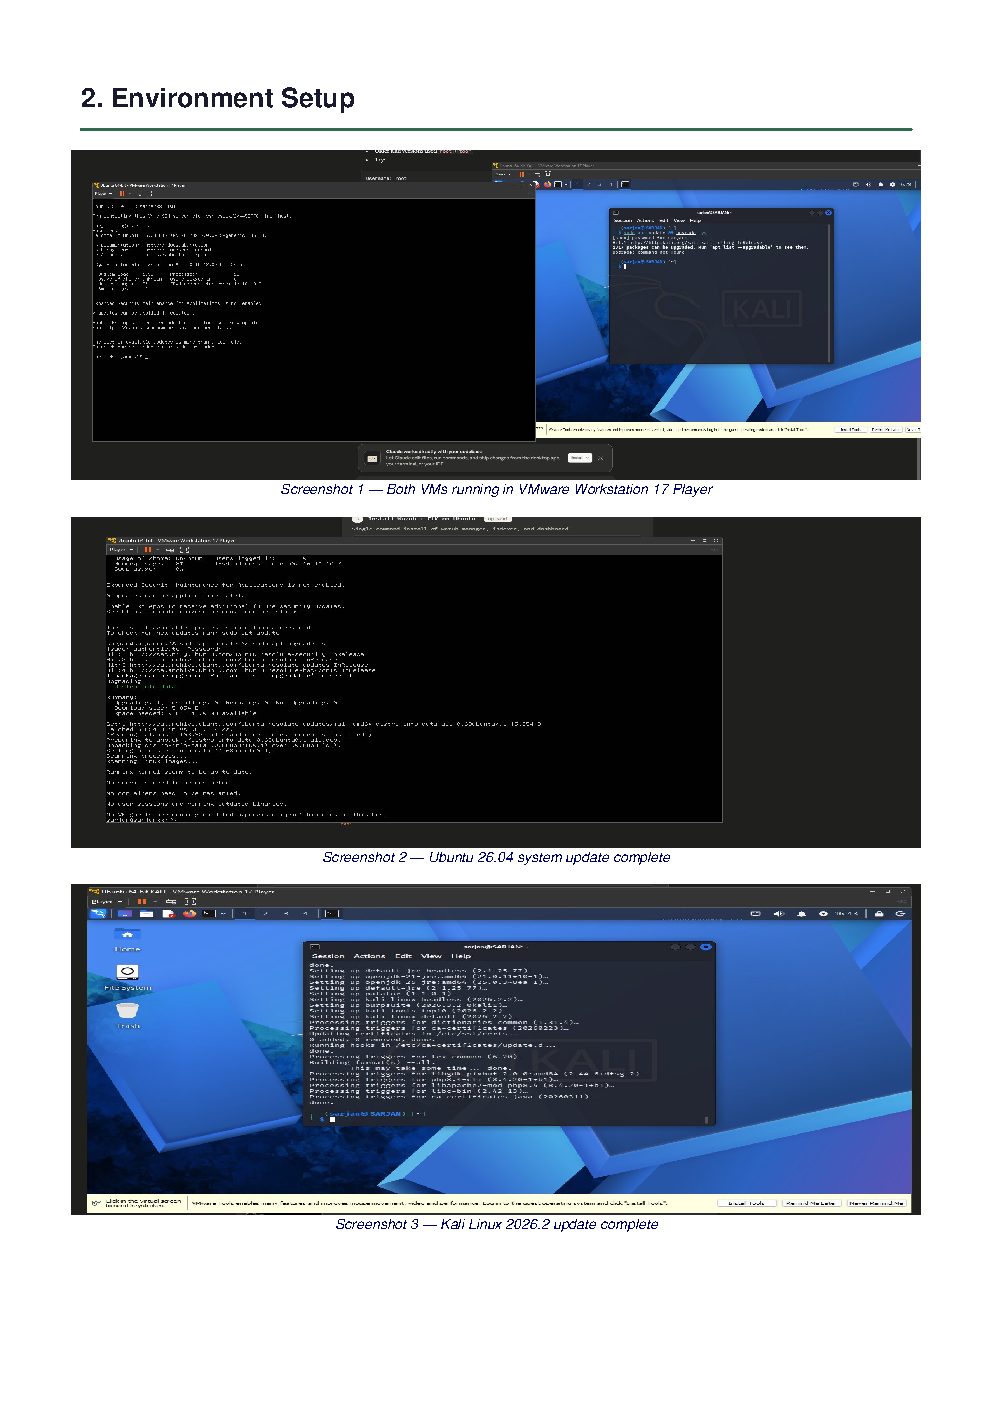 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
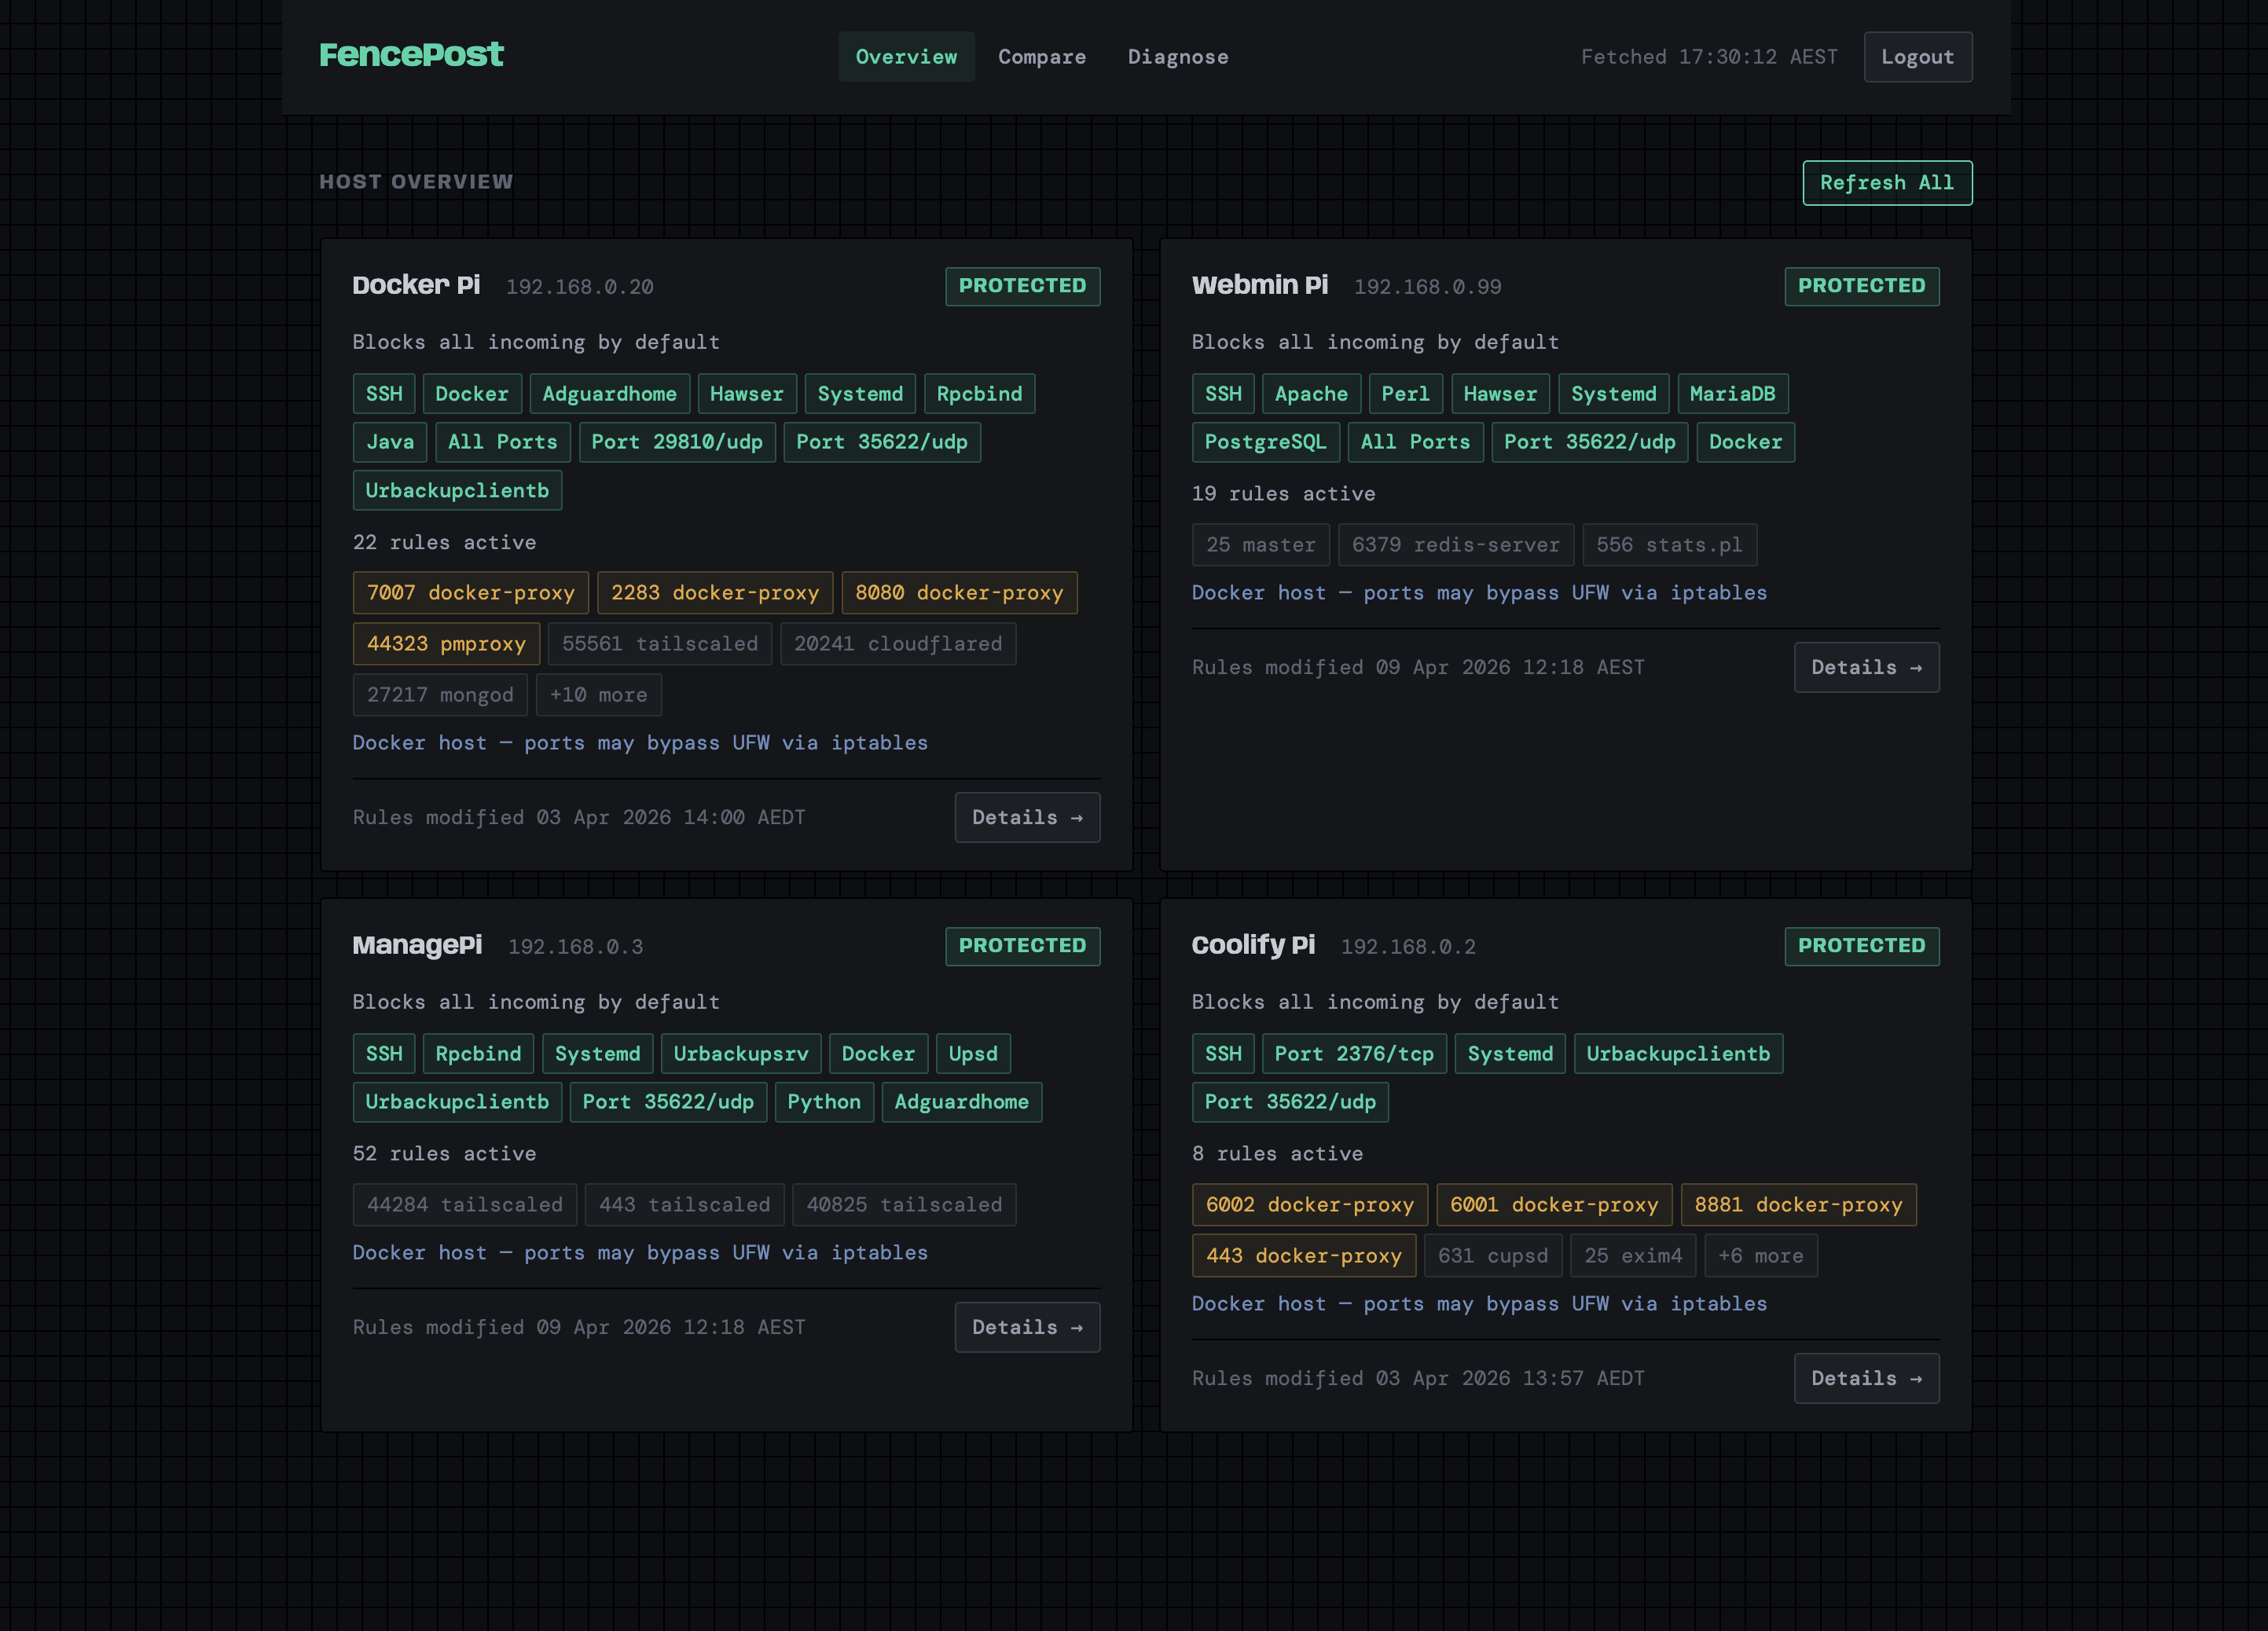 seriocomic/fencepost
Multi-host UFW firewall dashboard — explains rules in plain English, detects security gaps, and provides connection diagnostics
 aker-gateway/aker
SSH bastion/jump host/jumpserver
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
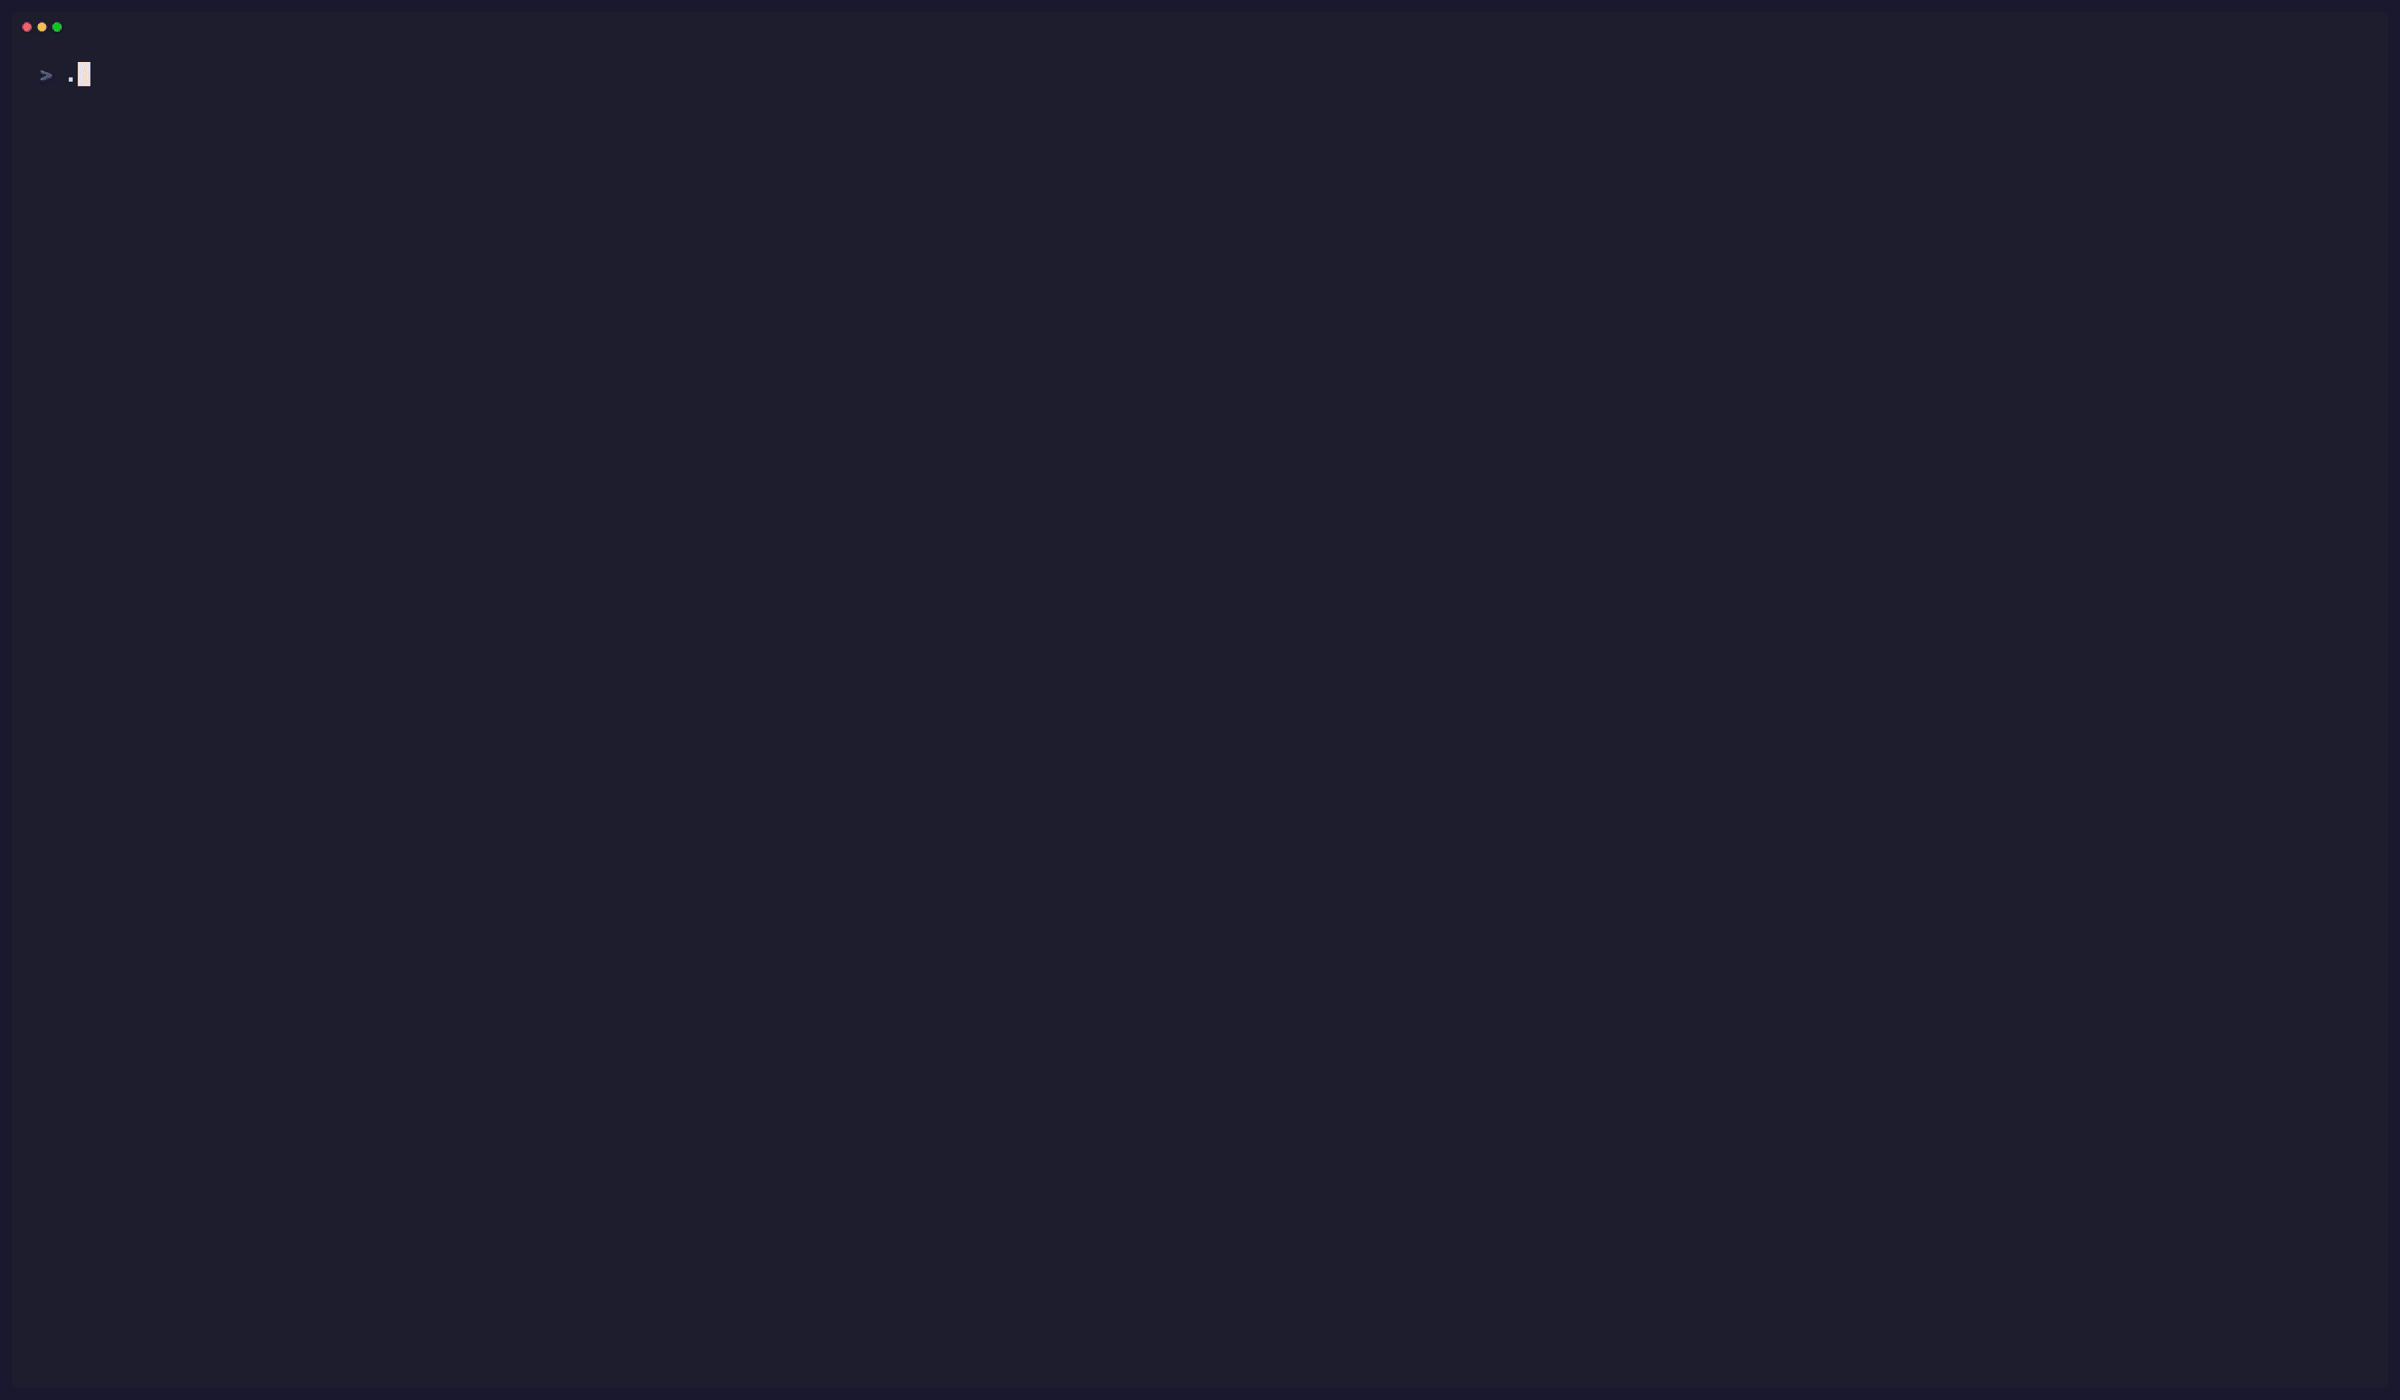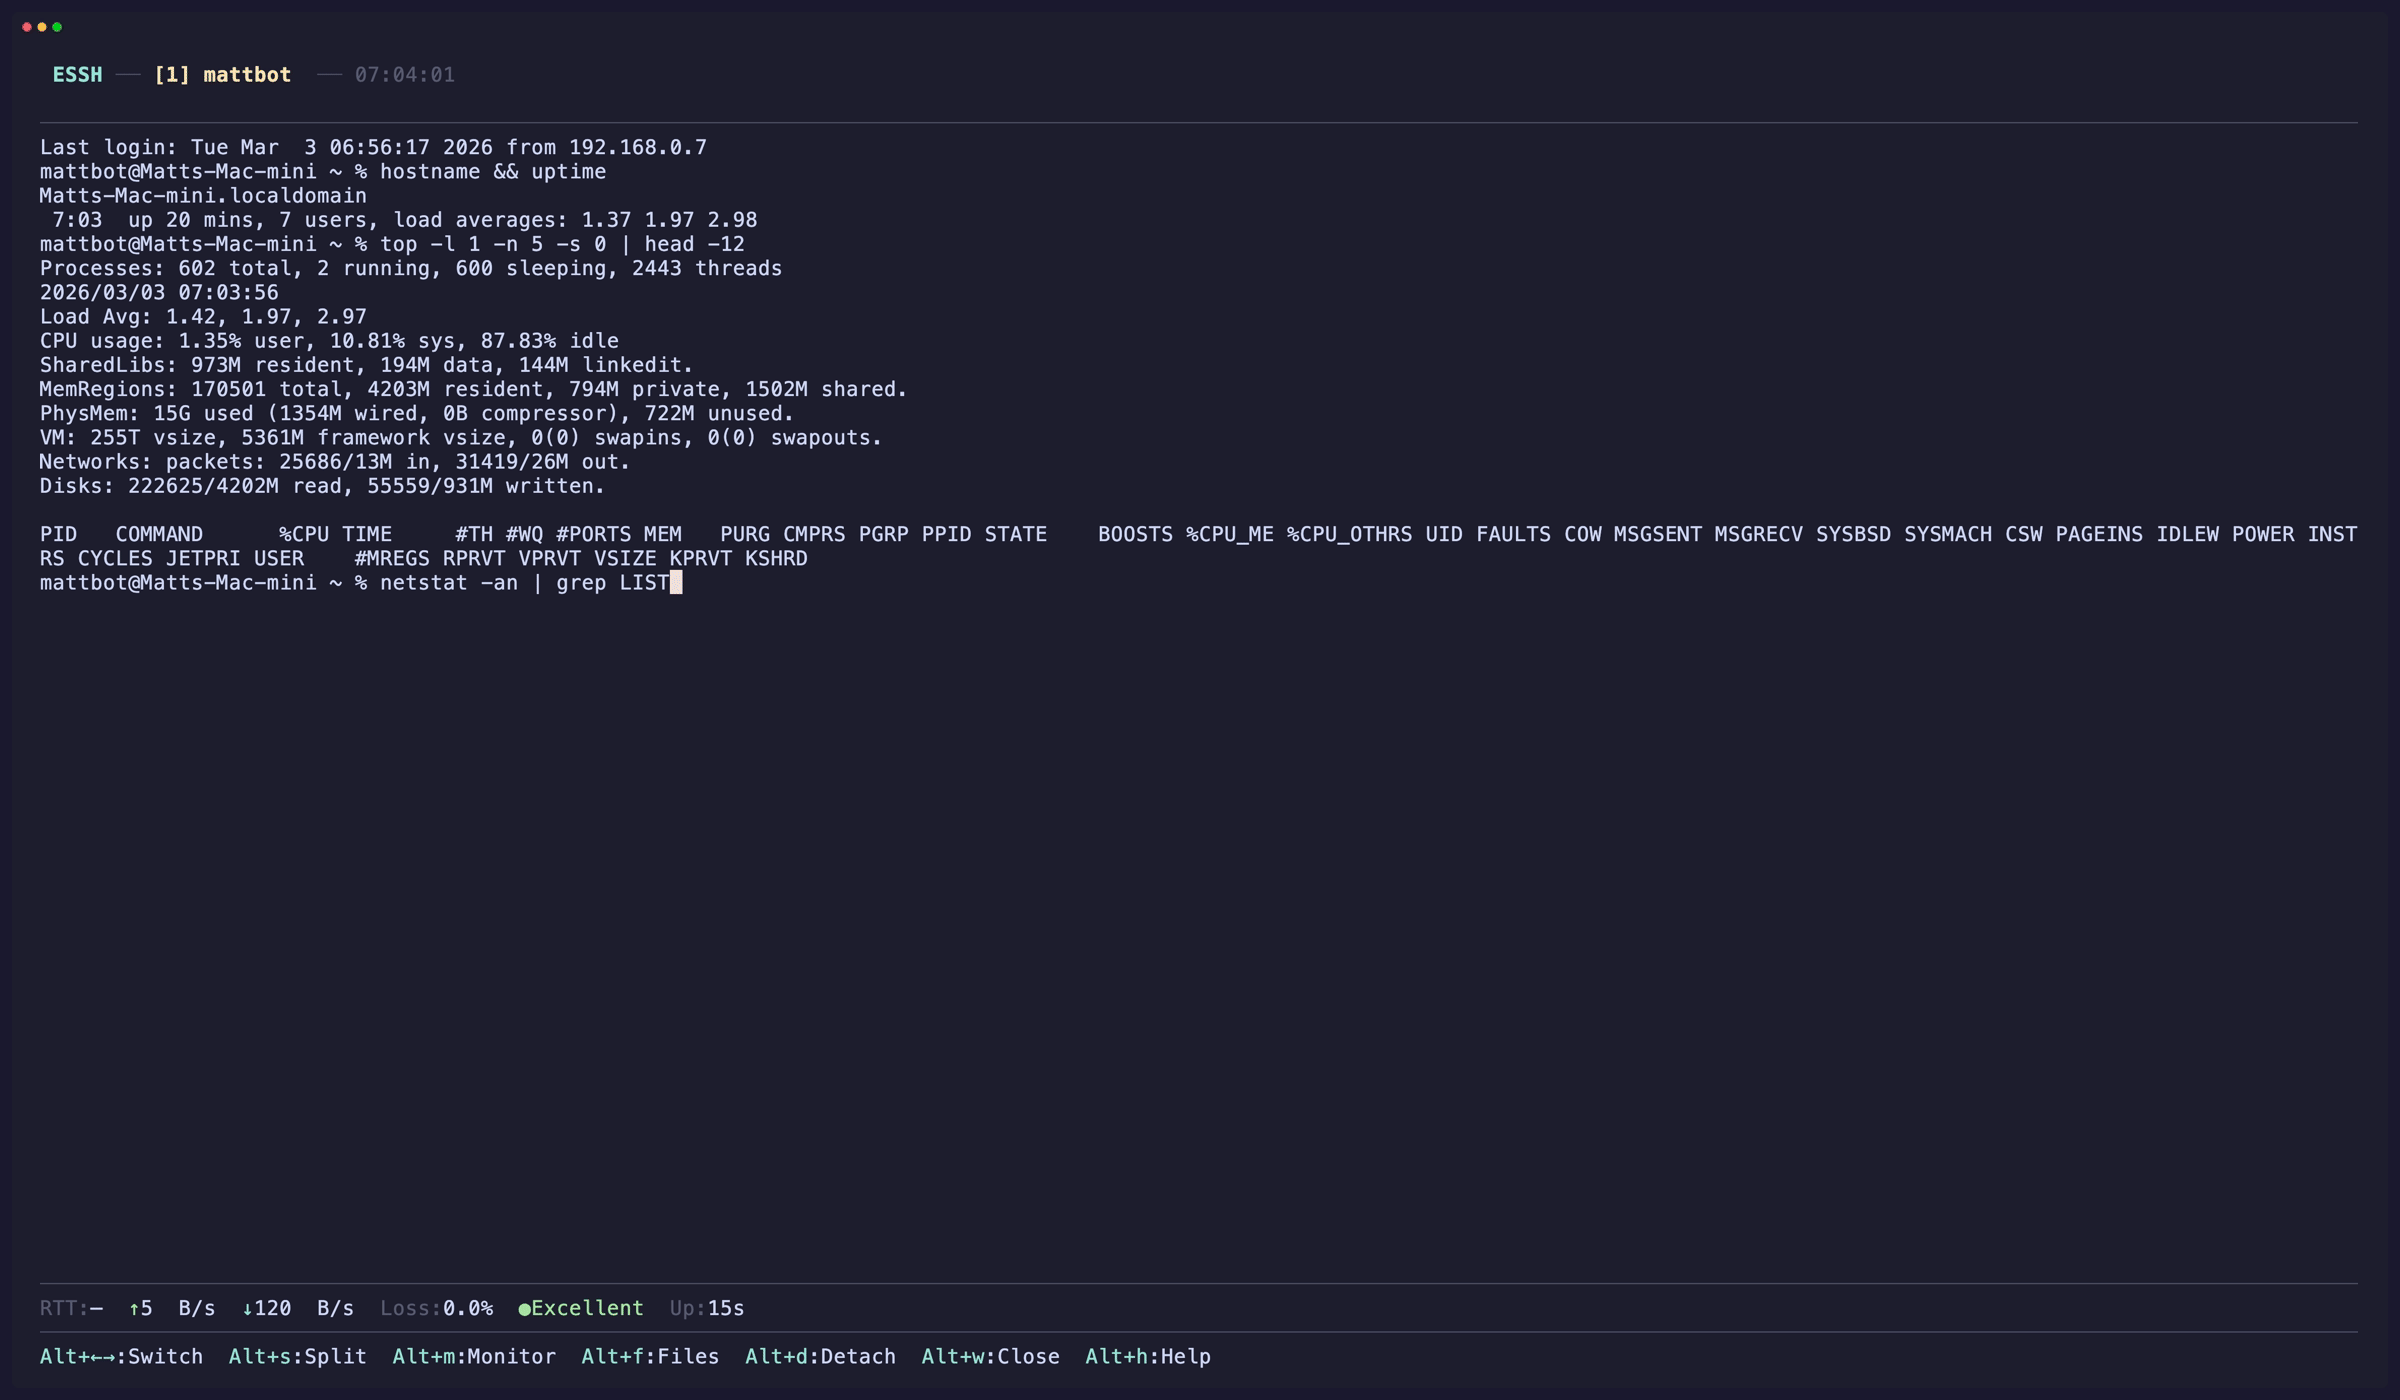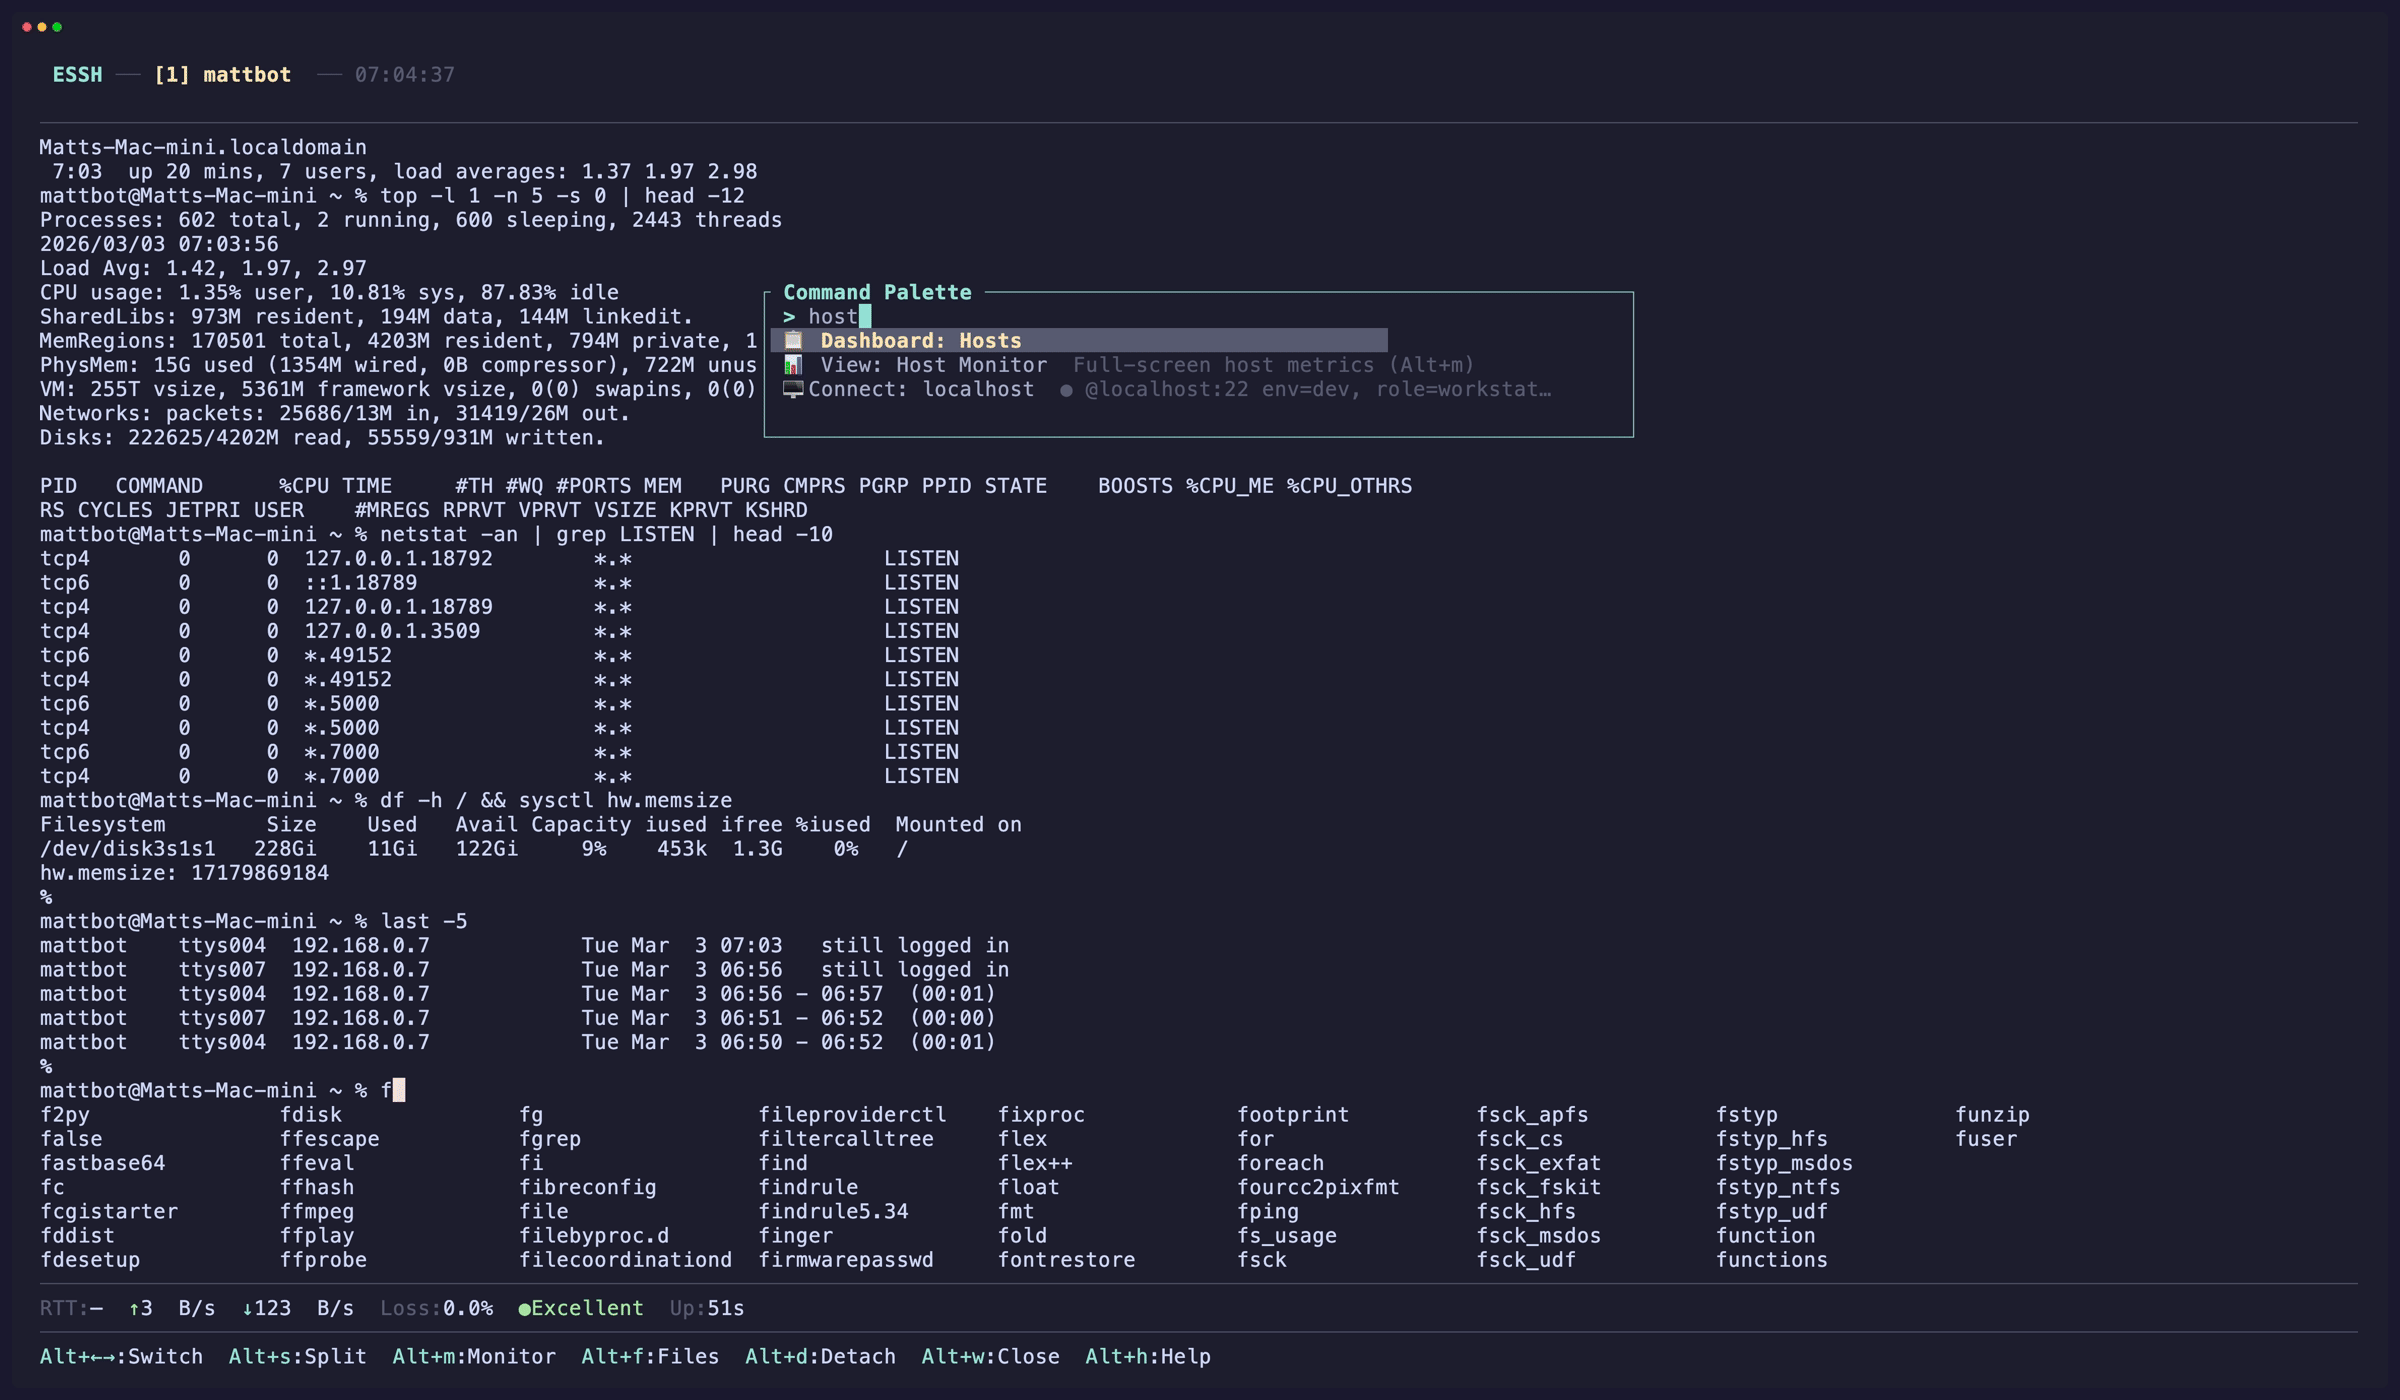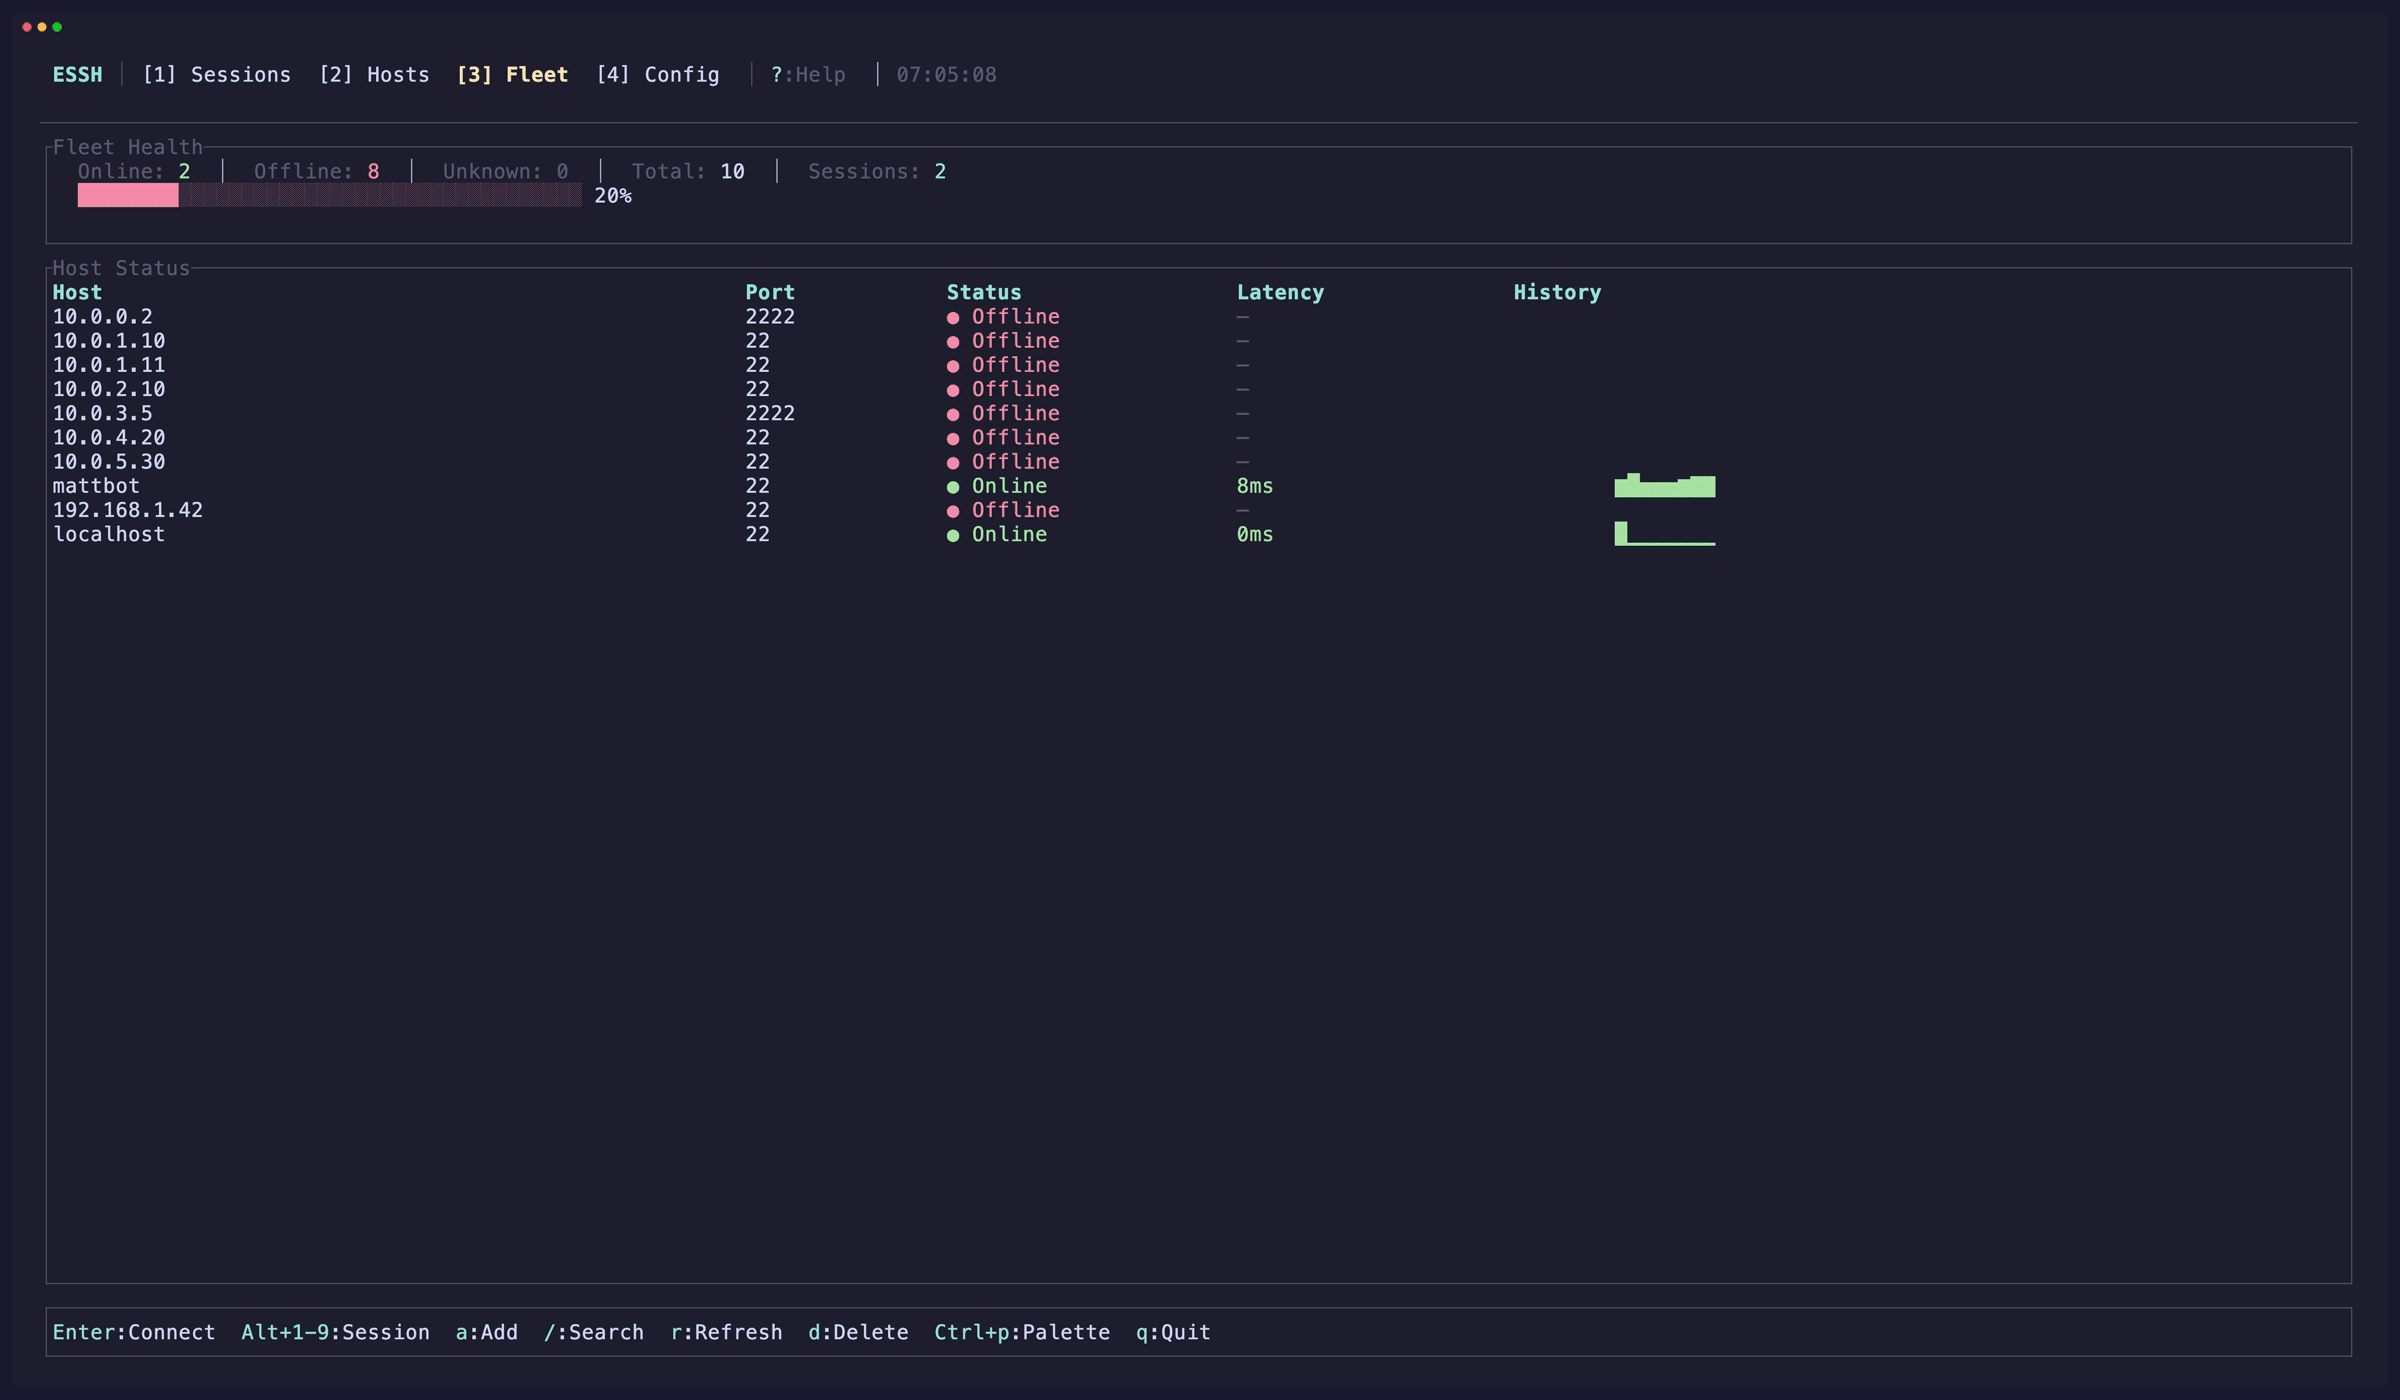 matthart1983/essh
Enhanced SSH client with TUI — manage connections, keys, and sessions
 adarsh14734/aegis-releases
Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…
 shoucheng3/asf__karaf_cve-2022-22932_4-3-5
Modulith runtime with hot deployment, dynamic configuration, JAAS-based RBAC, and centralized logging. Supports REST/API, web, and Spring Boot…
 gmh5225/gatekeeper
Self-hosted SSH access gateway in Go with OIDC/LDAP auth, RBAC, MFA, session recording, audit export, encryption at rest, IP rules, and policy…
 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.