
etl-parser
 airbus-cert/etl-parser
Event Trace Log file parser in pure Python
digital-forensicsforensicslog-analysis+1
156
airbus-cert/etl-parserEvent Trace Log file parser in pure Python
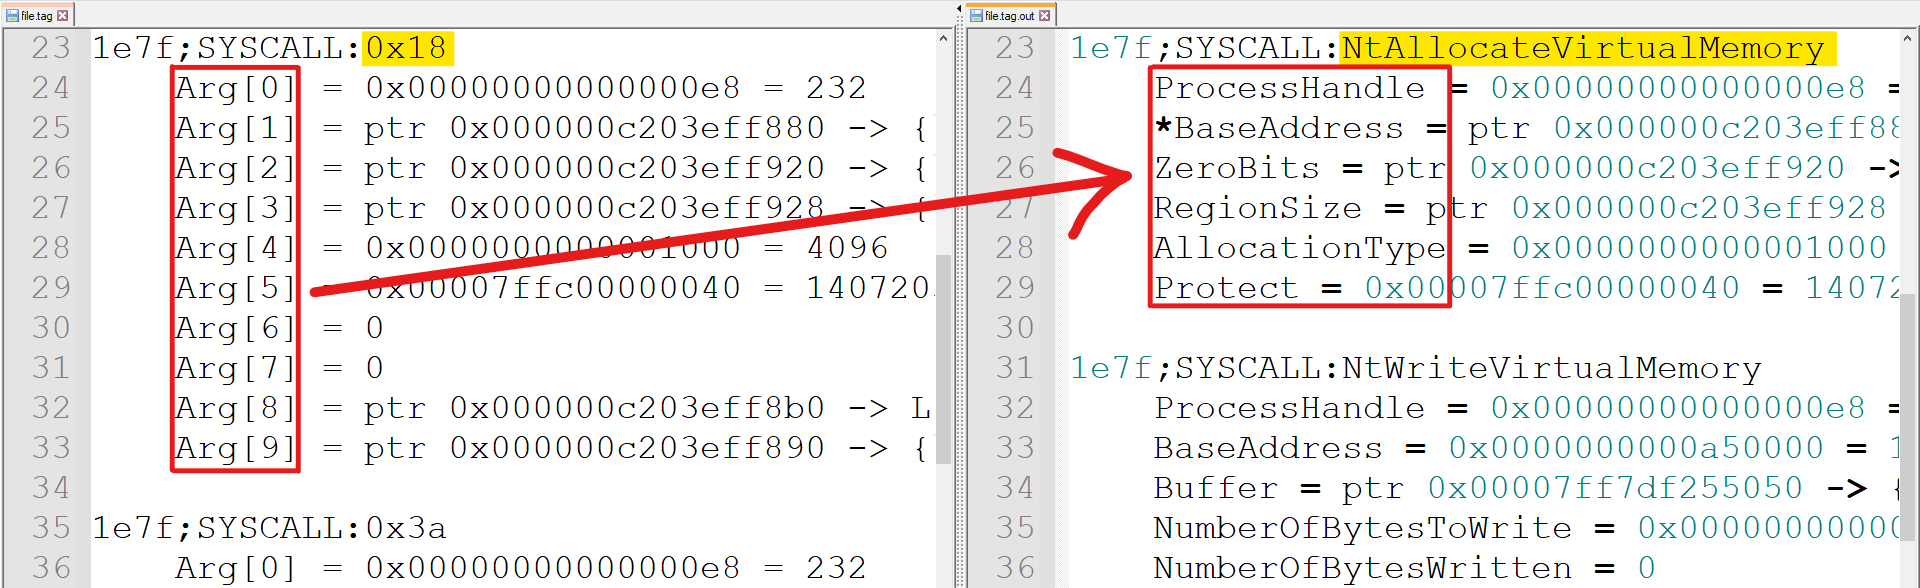 goatmilkkk/tinyprocessor
A post-processing script for TinyTracer
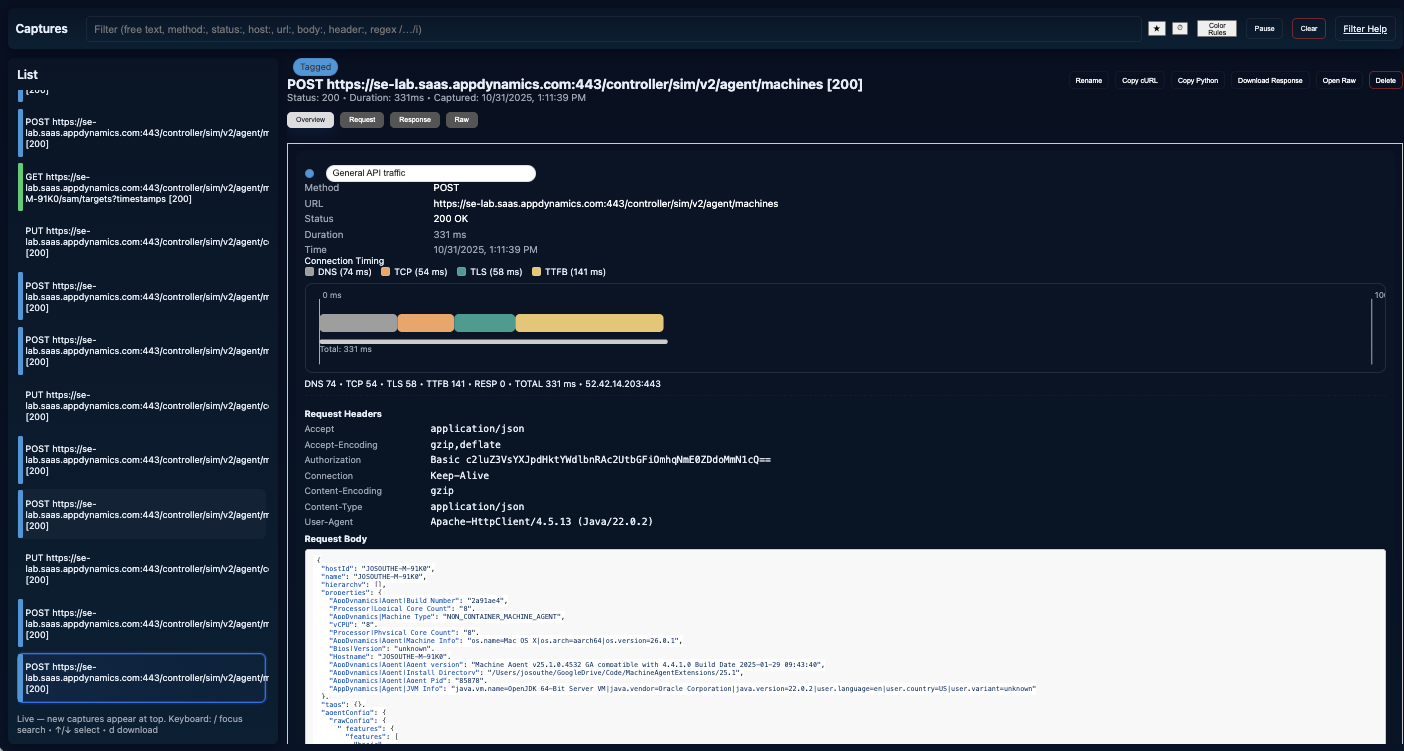 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
 cristhiansm0/txdxcristhian_2023-cve-38831
CVE-2023-38831 WinRAR lab: detection with Sysmon/Wazuh, reverse engineering with Ghidra, patch analysis, and remediation.
 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 jschicht/logfileparser
Parser for $LogFile on NTFS
 viliuskraujutis/androidbroadcastsmonitor
A tool to subscribe to receive all standard Android broadcasts on your Android device.
 target/strelka-ui
Strelka Web UI for File Submission and Analysis
 forensicxlab/vision-procmon
A ProcessMonitor visualization application written in rust.
 sh1n0g1/z9
Detects PowerShell-based malware artifacts from event logs and performs static analysis on PowerShell scripts to identify malicious activity.
 bfurkanyildiz/android-rce-analizi
Android CVE-2024-0044, 43093, 23706 zafiyet analizi ve PoC lab ortamı