CVE-2021-44228---detection-with-PowerShell

PowerShell-based scanner to detect Log4j CVE-2021-44228 vulnerability by searching directories and log files for exploitation indicators.

PowerShell-based scanner to detect Log4j CVE-2021-44228 vulnerability by searching directories and log files for exploitation indicators.

This script is used to perform a fast check if your server is possibly affected by CVE-2021-44228 (the log4j vulnerability).

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…

Web-based Traffic and Cybersecurity Network Traffic Monitoring


Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…

Dshell is a network forensic analysis framework.

A modern and elegant dashboard for network traffic visualization and analysis.

Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…

Passive DNS Capture and Monitoring Toolkit

A collection of scripts which may come in handy during your freedom fighting activities.

Find phishing kits which use your brand/organization's files and image.

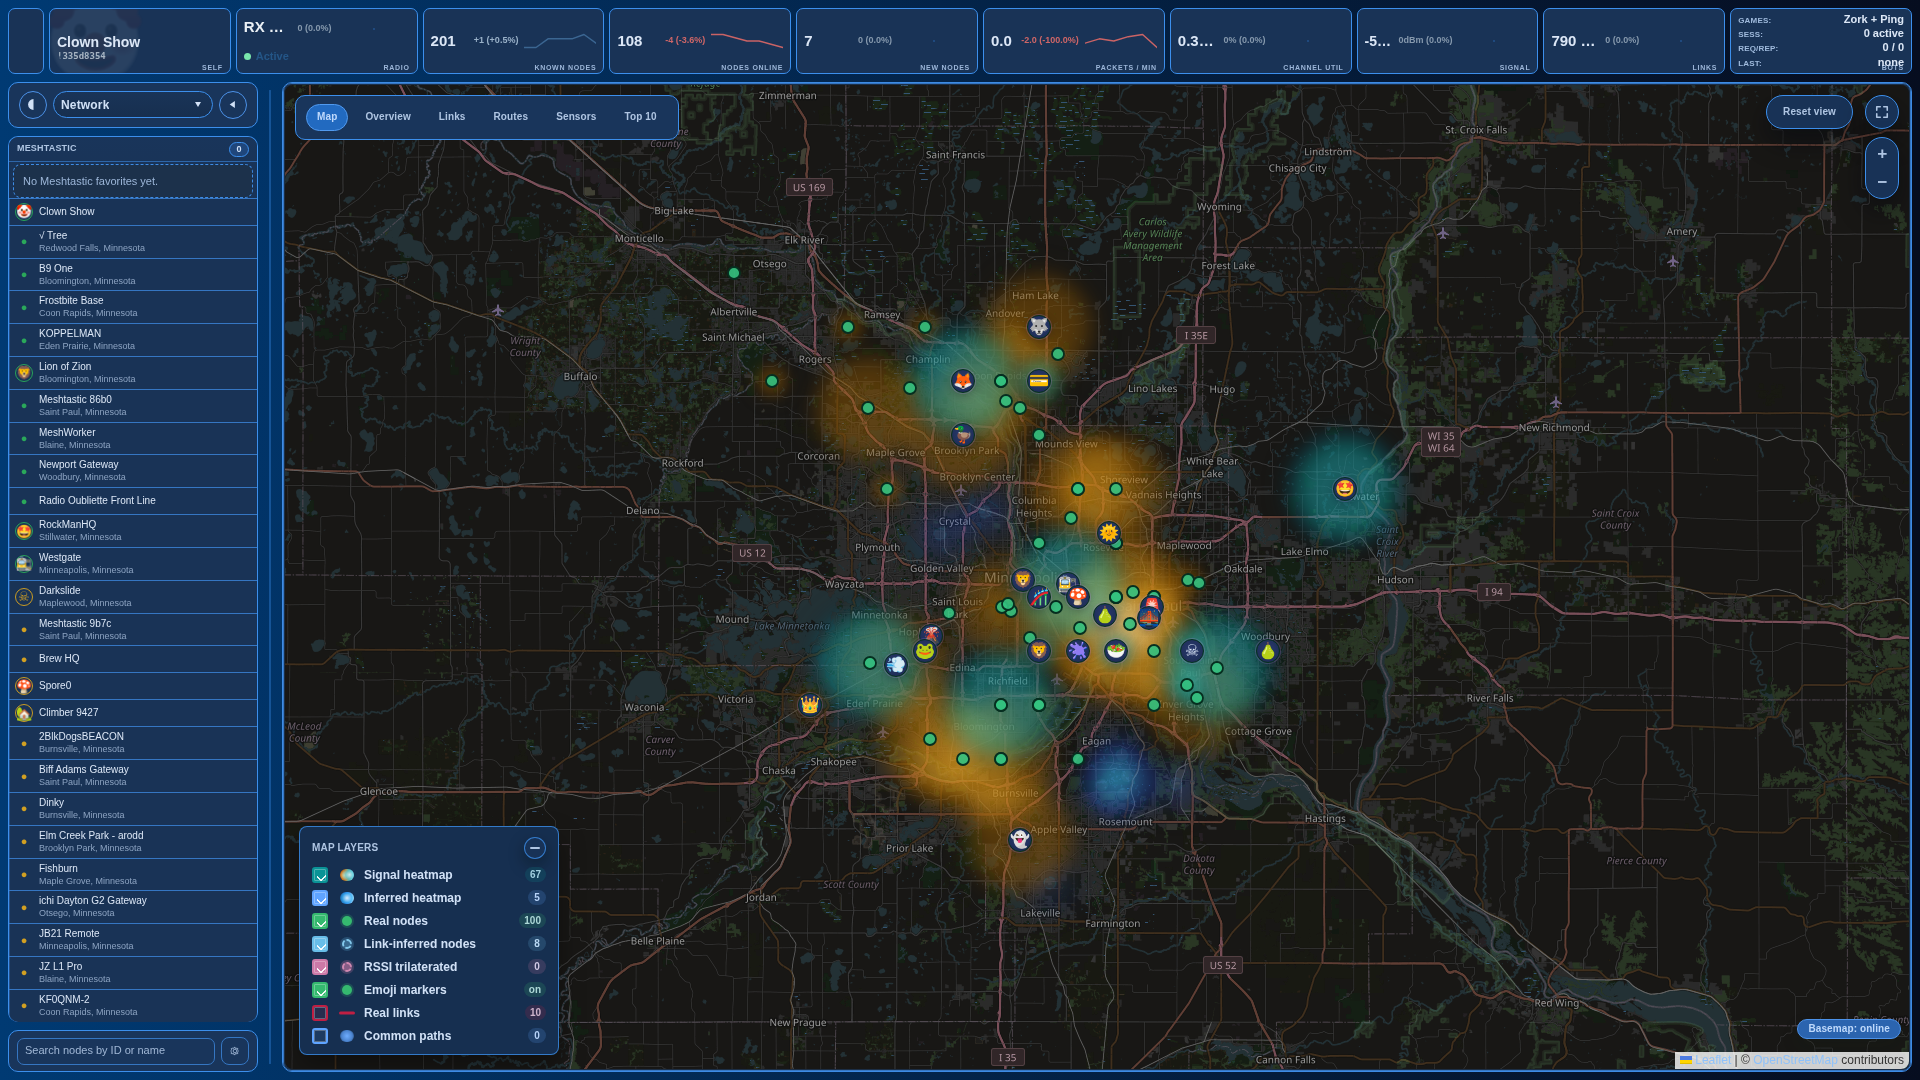
Single-page web dashboard for Meshtastic mesh networks with live network mapping, packet analysis, chat, sensor telemetry, and topology…

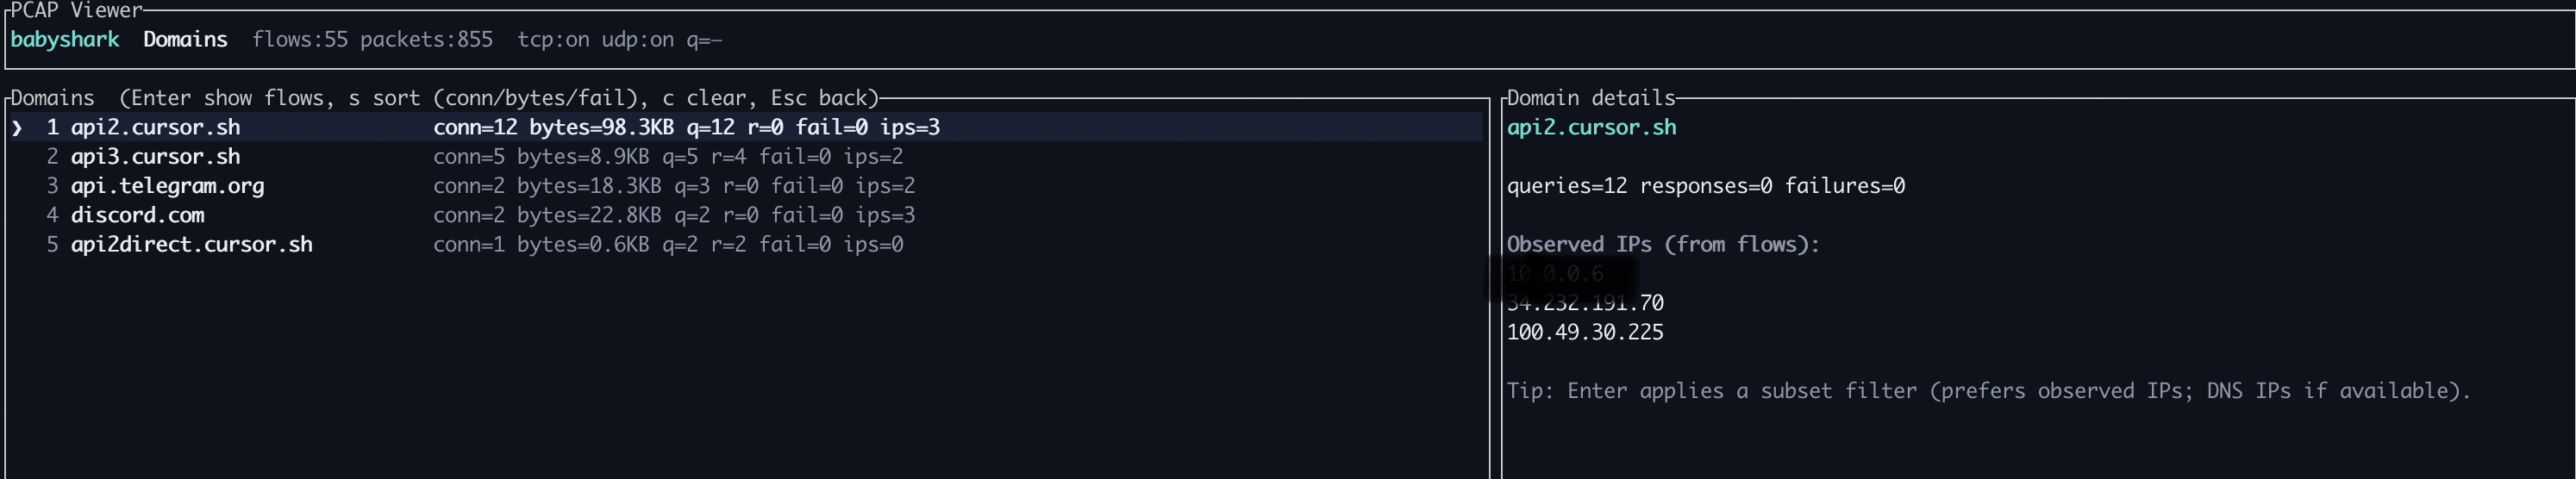
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.

An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.

Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…

create cypher create statements for neo4j out of netstat files from multiple machines