
community-id-spec
 corelight/community-id-spec
An open standard for hashing network flows into identifiers, a.k.a "Community IDs".
digital-forensicsincident-responseintrusion-detection+4
198
corelight/community-id-specAn open standard for hashing network flows into identifiers, a.k.a "Community IDs".
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 nccgroup/reactor
Runs custom filters on Elasticsearch and alerts on matches
 ttlab-research/awesome-wazuh
🛡️Awesome lists about all kinds of interesting topics of Wazuh XDR/SIEM
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
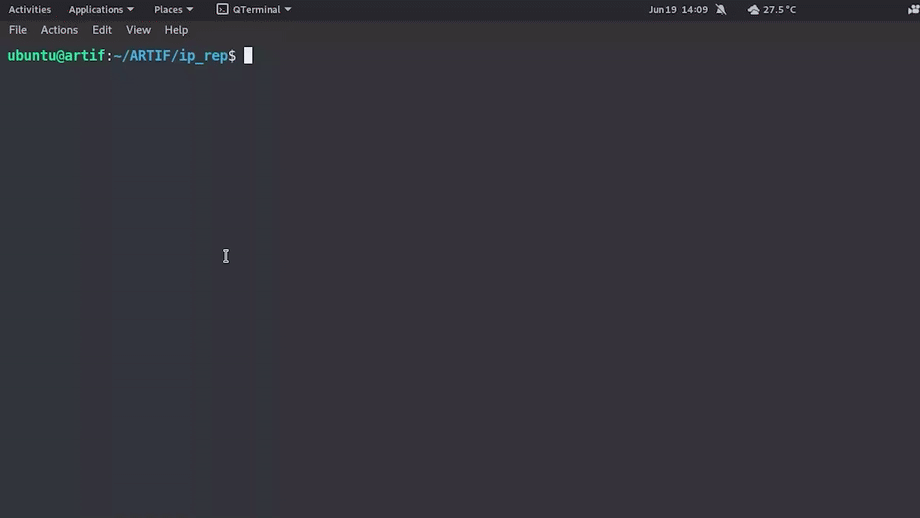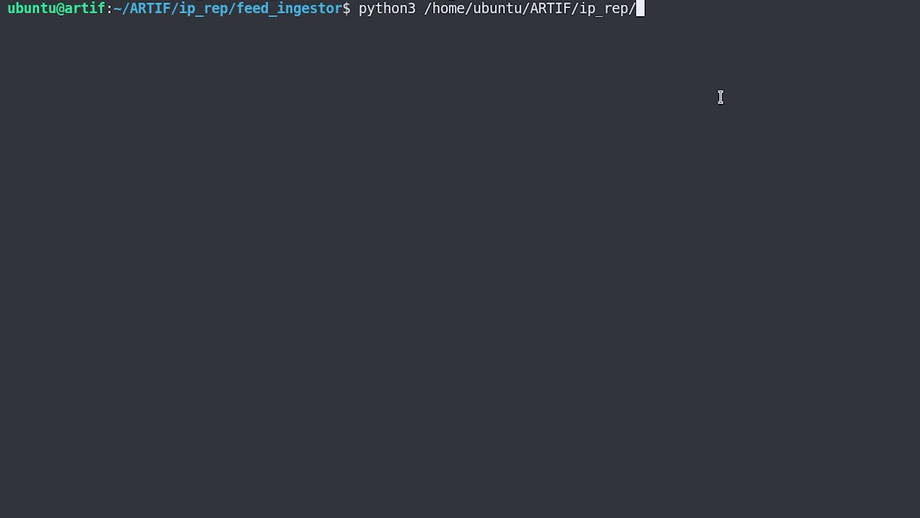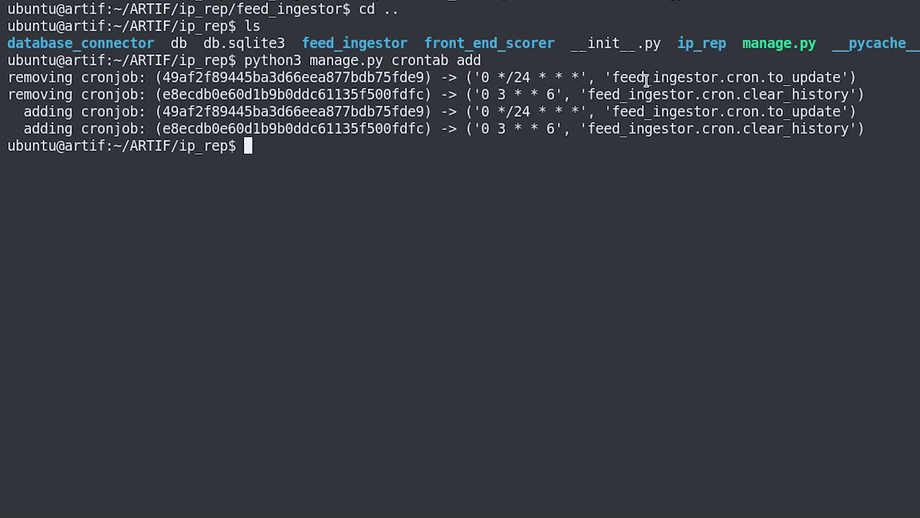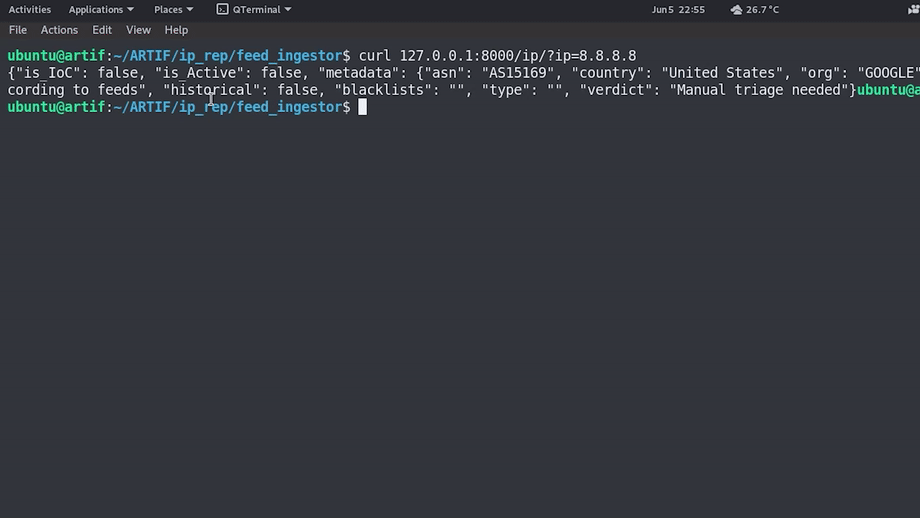 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 scarredmonk/sysmonsimulator
Sysmon event simulation utility which can be used to simulate the attacks to generate the Sysmon Event logs for testing the EDR detections and…
 intel-xeon/cve-2021-44228---detection-with-powershell
PowerShell-based scanner to detect Log4j CVE-2021-44228 vulnerability by searching directories and log files for exploitation indicators.
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
 mitre/brawl-public-game-001
Data from a BRAWL Automated Adversary Emulation Exercise
 nccgroup/mortimer
A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
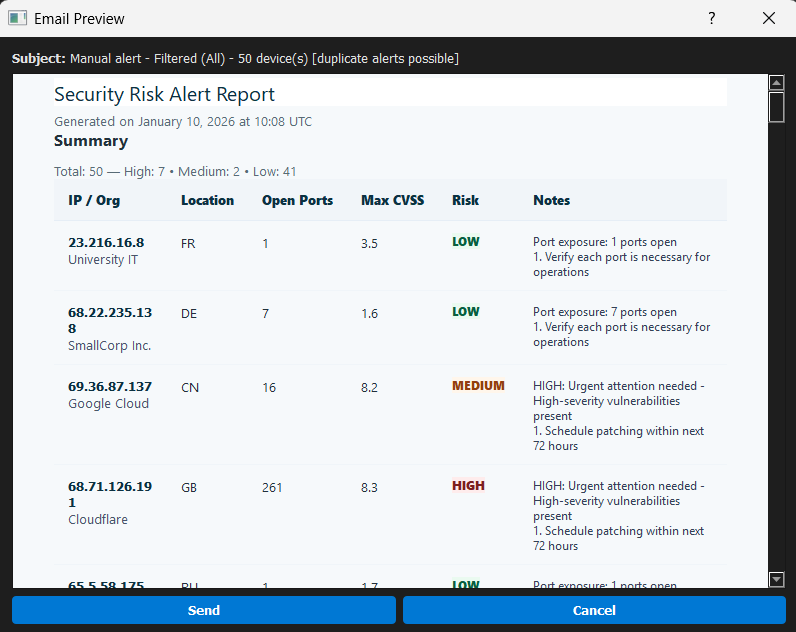 eclipsemanic/threatsentry-ai
ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…
 corelight/zeek-community-id
Zeek support for Community ID flow hashing.
 freeguy-6/dmz-security-monitoring-hardening
CY376 Blue Team project — pfSense DMZ, Suricata IDS/IPS, and automated host hardening against CVE-2014-6271
 lucadibello/network-attack-detection
Advanced detection of port scanning, DoS and malware attacks using Machine Learning techniques