

hawk
 t0pcyber/hawk
Powershell Based tool for gathering information related to O365 intrusions and potential Breaches
cloud-infrastructure-securitycloud-securitydigital-forensics+3
9491 year ago
t0pcyber/hawkPowershell Based tool for gathering information related to O365 intrusions and potential Breaches
 nccgroup/impossibletravelloganalysis
Basic log analysis tool to detect impossible travel via IP address geographic information
 danieleperera/onioningestor
An extendable tool to Collect, Crawl and Monitor onion sites on tor network and index collected information on Elasticsearch
 corelight/zeek-endpoint-enrichment
Zeek log enrichment tool that adds host information and known entity references to enhance network security monitoring and incident response.
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 abdulrhmanalfaifi/fennec
Artifact collection tool for *nix systems
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
 sap8899/reportly
AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
 alb-uss/secmon
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.
 ab2pentest/macosthreattrack
Bash tool used for proactive detection of malicious activity on macOS systems.
 thelightscope/thelightscope
TheLightScope
 corelight/icanntld
Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
 wortell/log4j
Repo containing all info, scripts, etc. related to CVE-2021-44228
 swimlane/soc-faker
A python package for use in generating fake data for SOC and security automation.
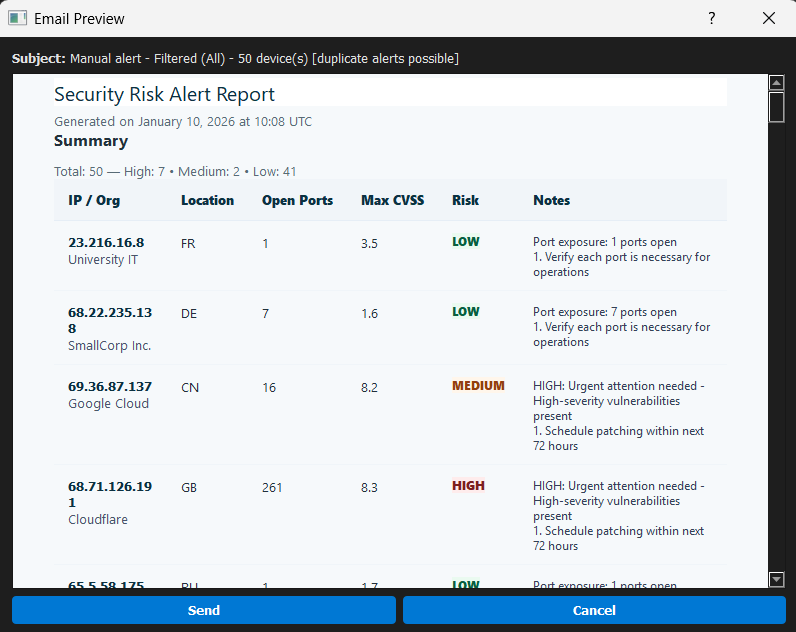 eclipsemanic/threatsentry-ai
ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…
 hackinglz/panrapidcheck
Extract useful information from PANOS support file for CVE-2024-3400