

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
40 results
staekka preview

staekka

GitHubj-0-t/staekka

Stækka Metasploit - Extenting Metasploit

anti-botexploit-frameworksforensics+7
549 years ago
CVE-2007-2447-Exploitation-SIEM-Detection-Lab preview

CVE-2007-2447-Exploitation-SIEM-Detection-Lab

GitHubharshiys/cve-2007-2447-exploitation-siem-detection-lab

Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
educationexploitationexploit-frameworks+7
2 months ago
ssh-enum preview

ssh-enum

GitHubalisha-chaudhary/ssh-enum

This project explores whether modern OpenSSH reveals valid usernames through subtle response or timing differences. CVE-2016-6210 user enumeration…
educationinformation-gatheringlog-analysis+4
4 months ago
DeepBlueCLI preview

DeepBlueCLI

GitHubsans-blue-team/deepbluecli

PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…

digital-forensicsincident-responseintrusion-detection+2
2.4k3 years ago
VcenterKiller preview

VcenterKiller

GitHubschira4396/vcenterkiller

一款针对Vcenter的综合利用工具,包含目前最主流的CVE-2021-21972、CVE-2021-21985以及CVE-2021-22005、One Access的CVE-2022-22954、CVE-2022-22972/31656以及log4j,提供一键上传webshell,命令执行或者上传…
command-and-controlexploitationlog-analysis+6
1.5k2 years ago
freedomfighting preview

freedomfighting

GitHubjusticerage/freedomfighting

A collection of scripts which may come in handy during your freedom fighting activities.
crawlerencryption-decryption-toolsforensics+8
4183 years ago
Kvasir preview

Kvasir

GitHubkvasirsecurity/kvasir

Kvasir: Penetration Test Data Management
data-recoveryinformation-gatheringlog-analysis+3
4279 years ago
sleep_python_bridge preview

sleep_python_bridge

GitHubcobalt-strike/sleep_python_bridge

This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…
command-and-controlioc-managementlog-analysis+3
1881 year ago
brawl-public-game-001 preview

brawl-public-game-001

GitHubmitre/brawl-public-game-001

Data from a BRAWL Automated Adversary Emulation Exercise
adversarial-attackcloud-securitydigital-forensics+7
2158 years ago
Agentic-SOC-Simulation preview

Agentic-SOC-Simulation

GitHubsafelineman/agentic-soc-simulation

AI 驱动的 SOC 仿真平台
ai-securityeducationforensics+8
16610 months ago
Purple-Team-Automation preview

Purple-Team-Automation

GitHubjoshuagodwin7929/purple-team-automation

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

adversarial-attackcommand-and-controlincident-response+6
591 month ago
siem preview

siem

GitHubekitji/siem

Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
curated-resourcesdefensive-toolseducation+7
5913 days ago
Log4Pot preview

Log4Pot

GitHubthomaspatzke/log4pot

A honeypot for the Log4Shell vulnerability (CVE-2021-44228).
intrusion-detectionlog-analysispayload-generation+2
941 year ago
latma preview

latma

GitHubsilverfort-open-source/latma

Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…

anomaly-detectioncloud-securityincident-response+5
803 years ago
macos-collector preview

macos-collector

GitHublethal-forensics/macos-collector

macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR

digital-forensicsforensicsincident-response+2
491 month ago
SCOPE preview

SCOPE

GitHubtayontech/scope

AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
ai-securitycloud-infrastructure-securitycloud-security+8
544 months ago
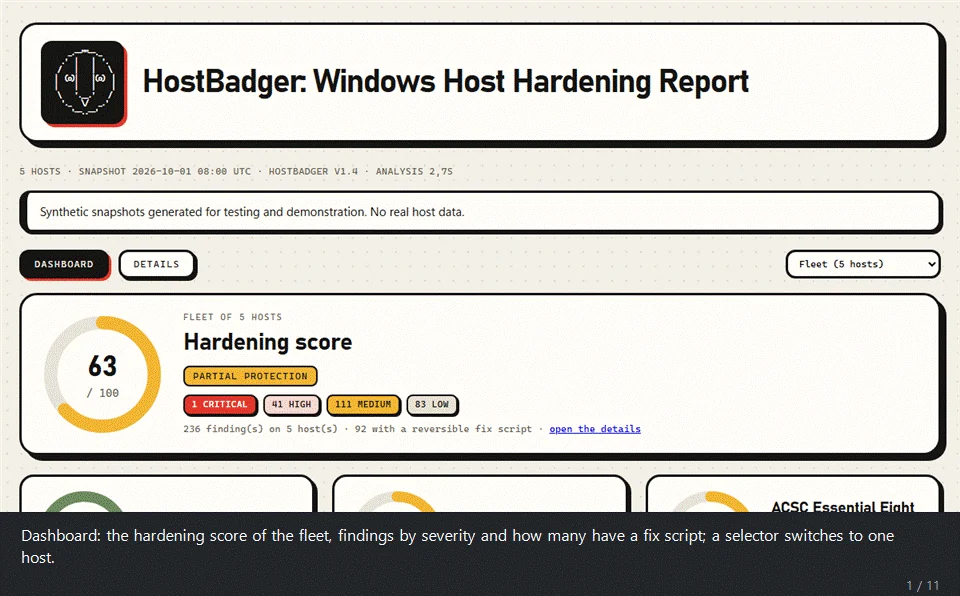
HostBadger preview

HostBadger

GitHubg4bri-3l3/hostbadger

Windows host hardening auditor and remediation tool in PowerShell: CIS, DISA STIG, Essential Eight checks, reversible fixes, optional AI analysis
configuration-auditingdefensive-toolsincident-response+6
215 days ago
Ledger preview

Ledger

GitHubshellkraft/ledger

An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…

command-and-controlincident-responselog-analysis+5
275 months ago
Previous123Next