
ssh-enum
 alisha-chaudhary/ssh-enum
This project explores whether modern OpenSSH reveals valid usernames through subtle response or timing differences. CVE-2016-6210 user enumeration…
educationinformation-gatheringlog-analysis+4
alisha-chaudhary/ssh-enumThis project explores whether modern OpenSSH reveals valid usernames through subtle response or timing differences. CVE-2016-6210 user enumeration…
 pedrofbrm/apache-web-log-analysis-lab
Blue Team lab focused on analyzing Apache web access logs to detect directory brute forcing and web scanning activity.
 fenkohq/dnsmonster
Passive DNS Capture and Monitoring Toolkit
 randomuserid/tylium
Primary data pipelines for intrusion detection, security analytics and threat hunting
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…

 kunai-project/kunai
eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
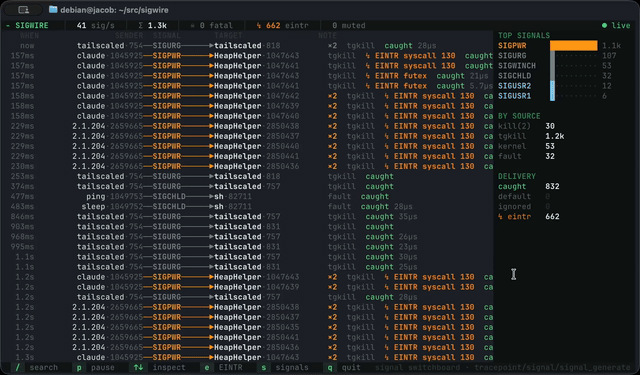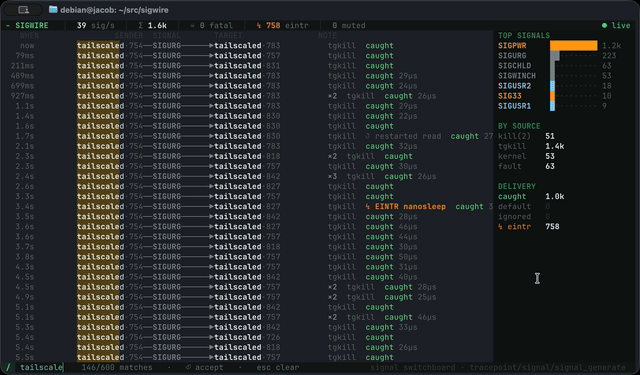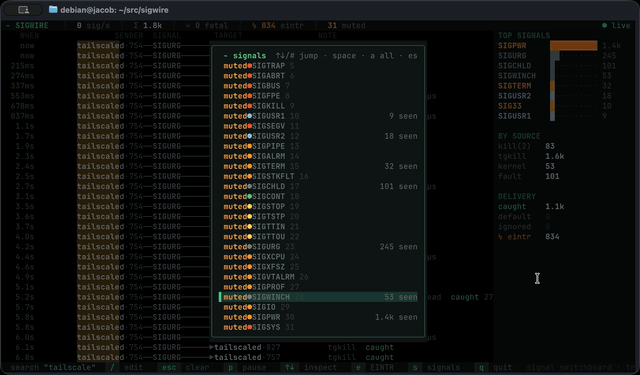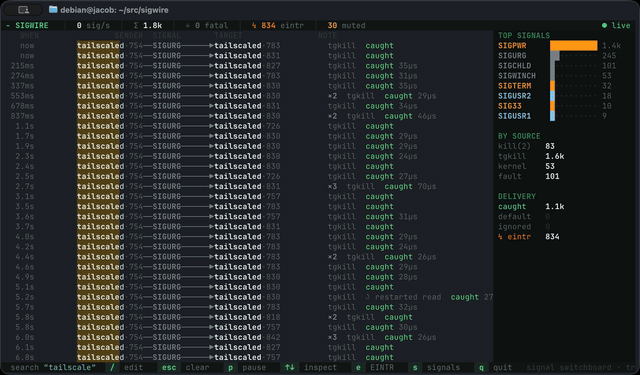 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
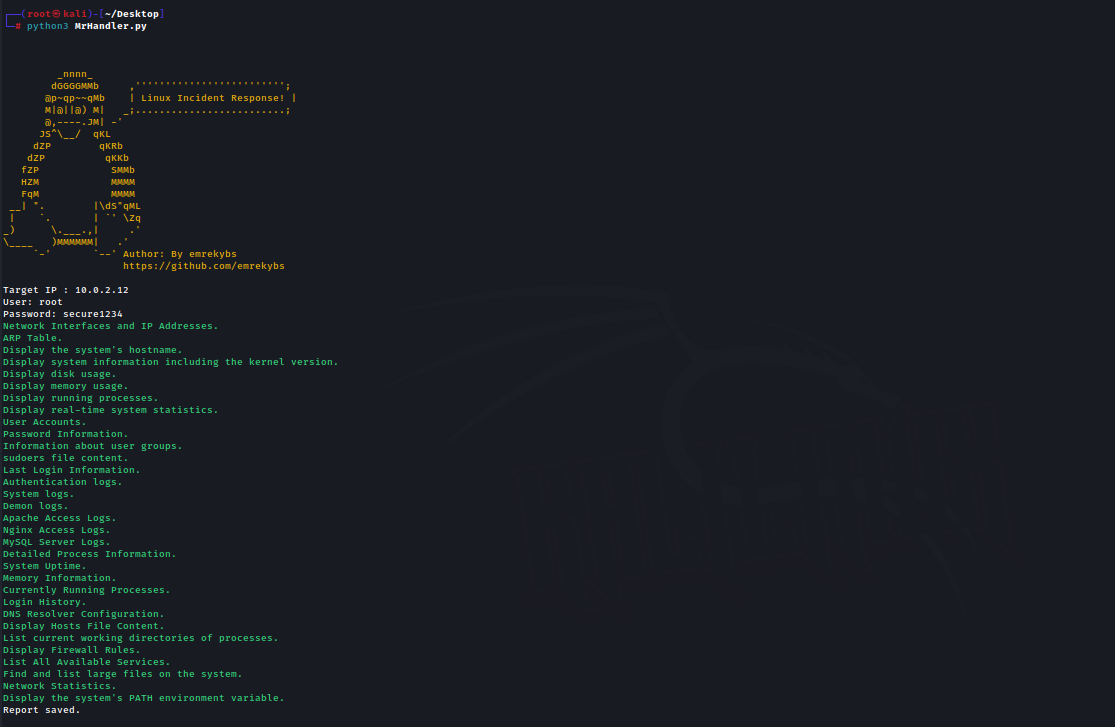 emrekybs/mrhandler
SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 renich/pared
Lightweight, secure control plane & real-time web dashboard in Crystal for Linux firewalld and NetworkManager host security.
 abdom.seada/security-checks
linux security checks
 0warn/defender
This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…
 kolya5544/bearftp
Honeypot FTP server written in .NET Core (C#) for both Linux and Windows.
 ghostop14/sparrow-wifi
Next-Gen GUI-based WiFi and Bluetooth Analyzer for Linux
 otrf/ossem
Community-driven project for documenting, standardizing, and modeling security event logs to improve detection analytics and data normalization…