
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
36 results
MasterParser preview

MasterParser

GitHubsecurityjoes/masterparser

MasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs
digital-forensicseducationforensics+3
7628 months ago
APT-Hunter preview

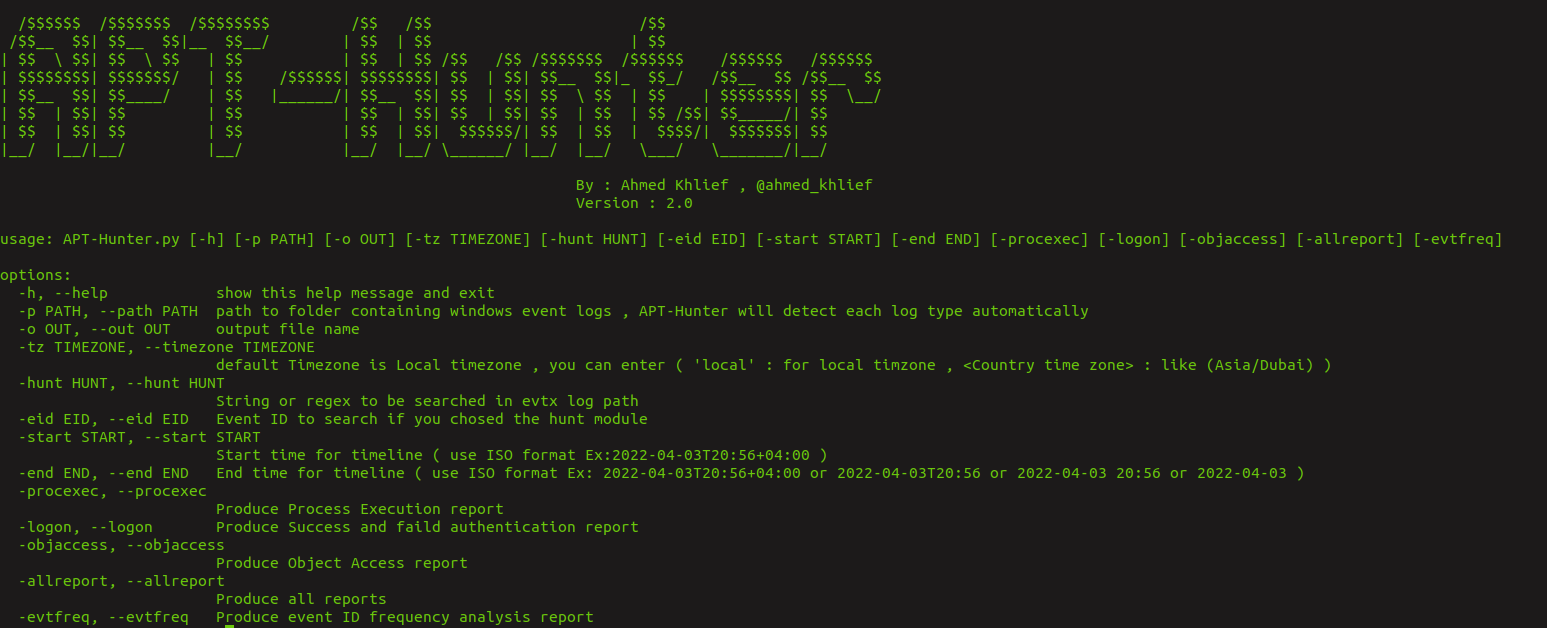
APT-Hunter

GitHubahmedkhlief/apt-hunter

APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…
forensicsincident-responselog-analysis+1
1.4k21 days ago
Zircolite preview

Zircolite

GitHubwagga40/zircolite

A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
forensicsincident-responselog-analysis+1
85920h 58m ago
ALFA preview

ALFA

GitHubinvictus-ir/alfa

Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…
cloud-securitydigital-forensicsforensics+3
1861 month ago
Fennec preview

Fennec

GitHubabdulrhmanalfaifi/fennec

Artifact collection tool for *nix systems
digital-forensicsforensicsincident-response+3
2222 years ago
ThreatHound preview

ThreatHound

GitHubmazx0p/threathound

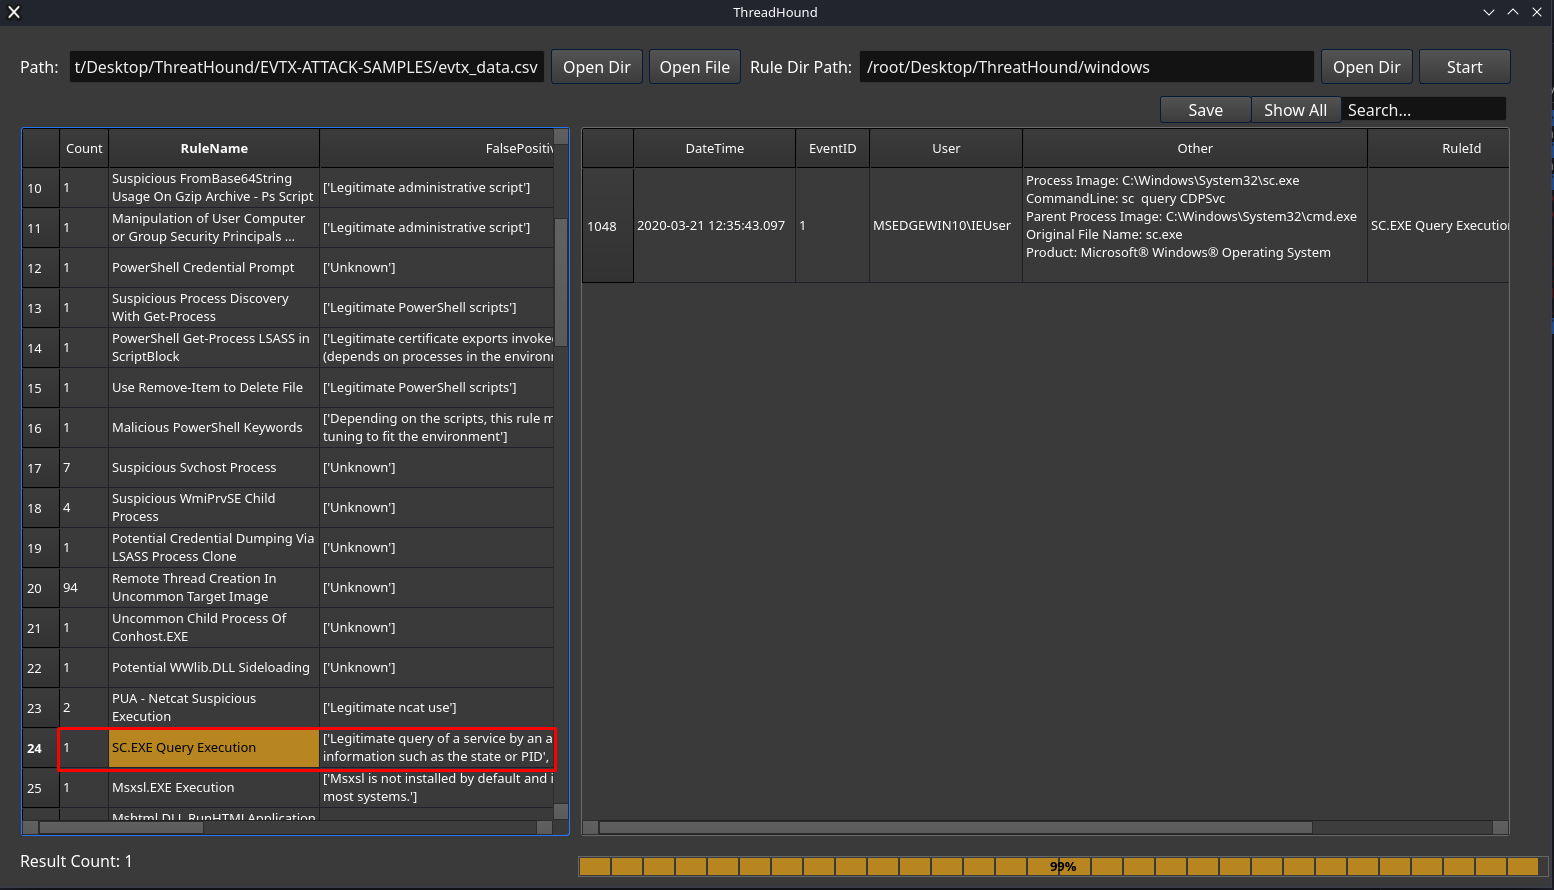
Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
digital-forensicsincident-responselog-analysis+1
1592 years ago
detectree preview

detectree

GitHubwithsecurelabs/detectree

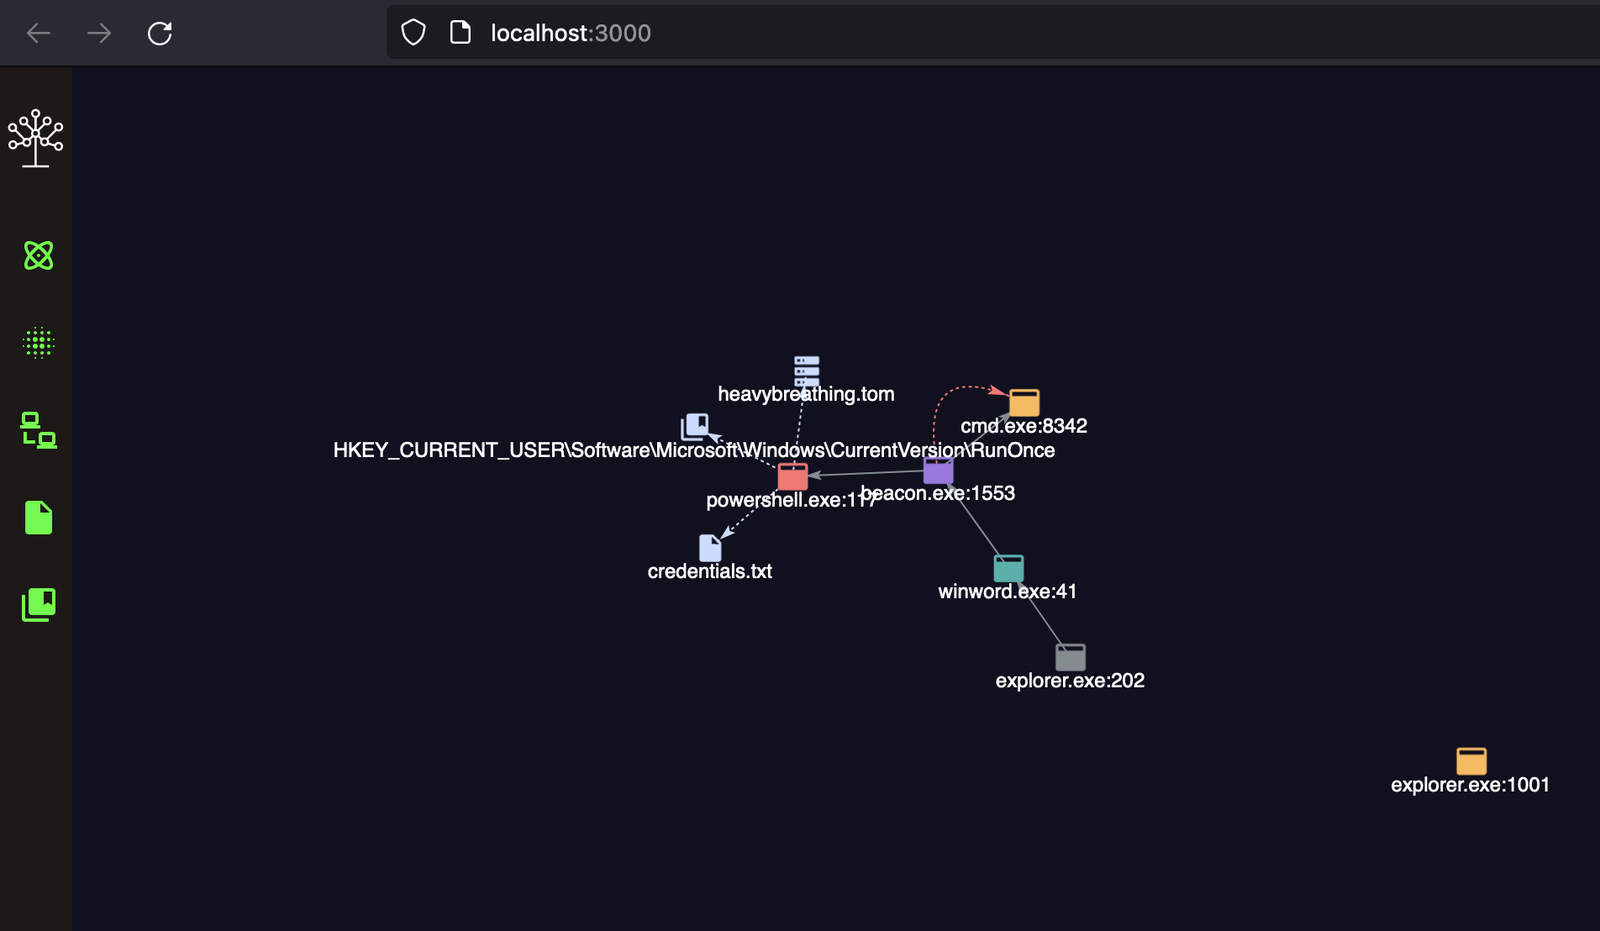
Interactive data visualization tool for blue teams to analyze detection data, understand relationships, reduce alert fatigue, and improve incident…
defensive-toolsincident-responselog-analysis+1
1263 years ago
ESFang preview

ESFang

GitHubwithsecurelabs/esfang

ESF modular ingestion tool for development and research.
digital-forensicsforensicsincident-response+1
384 years ago
RemotePSpy preview

RemotePSpy

GitHubwithsecurelabs/remotepspy

Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…

defensive-toolsdigital-forensicsincident-response+3
196 years ago
CVE-2021-44228-kusto preview

CVE-2021-44228-kusto

GitHubwheezysec/cve-2021-44228-kusto

Kusto query-based detection and analysis tool for CVE-2021-44228 (Log4Shell) vulnerability, enabling rapid log hunting and exploitation…
exploitationincident-responselog-analysis+2
4 years ago
LDAP-Monitoring-Watchdog preview
Archived

LDAP-Monitoring-Watchdog

GitHubmegamansec/ldap-monitoring-watchdog

LDAP Watchdog: A real-time linux-compatible LDAP monitoring tool for detecting directory changes, providing visibility into additions, modifications,…

incident-responselog-analysisthreat-intelligence
1966 months ago
timesketch preview

timesketch

GitHubgoogle/timesketch

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
data-recoverydigital-forensicsdisk-forensics+7
3.4k1 day ago
mongobleed-detector preview

mongobleed-detector

GitHubneo23x0/mongobleed-detector

Detection Script for MongoBleed Exploitation
database-securitydigital-forensicsforensics+5
829 months ago
MacOSThreatTrack preview

MacOSThreatTrack

GitHubab2pentest/macosthreattrack

Bash tool used for proactive detection of malicious activity on macOS systems.
digital-forensicsincident-responseinformation-gathering+1
401 year ago
OSXAuditor preview

OSXAuditor

GitHubjipegit/osxauditor

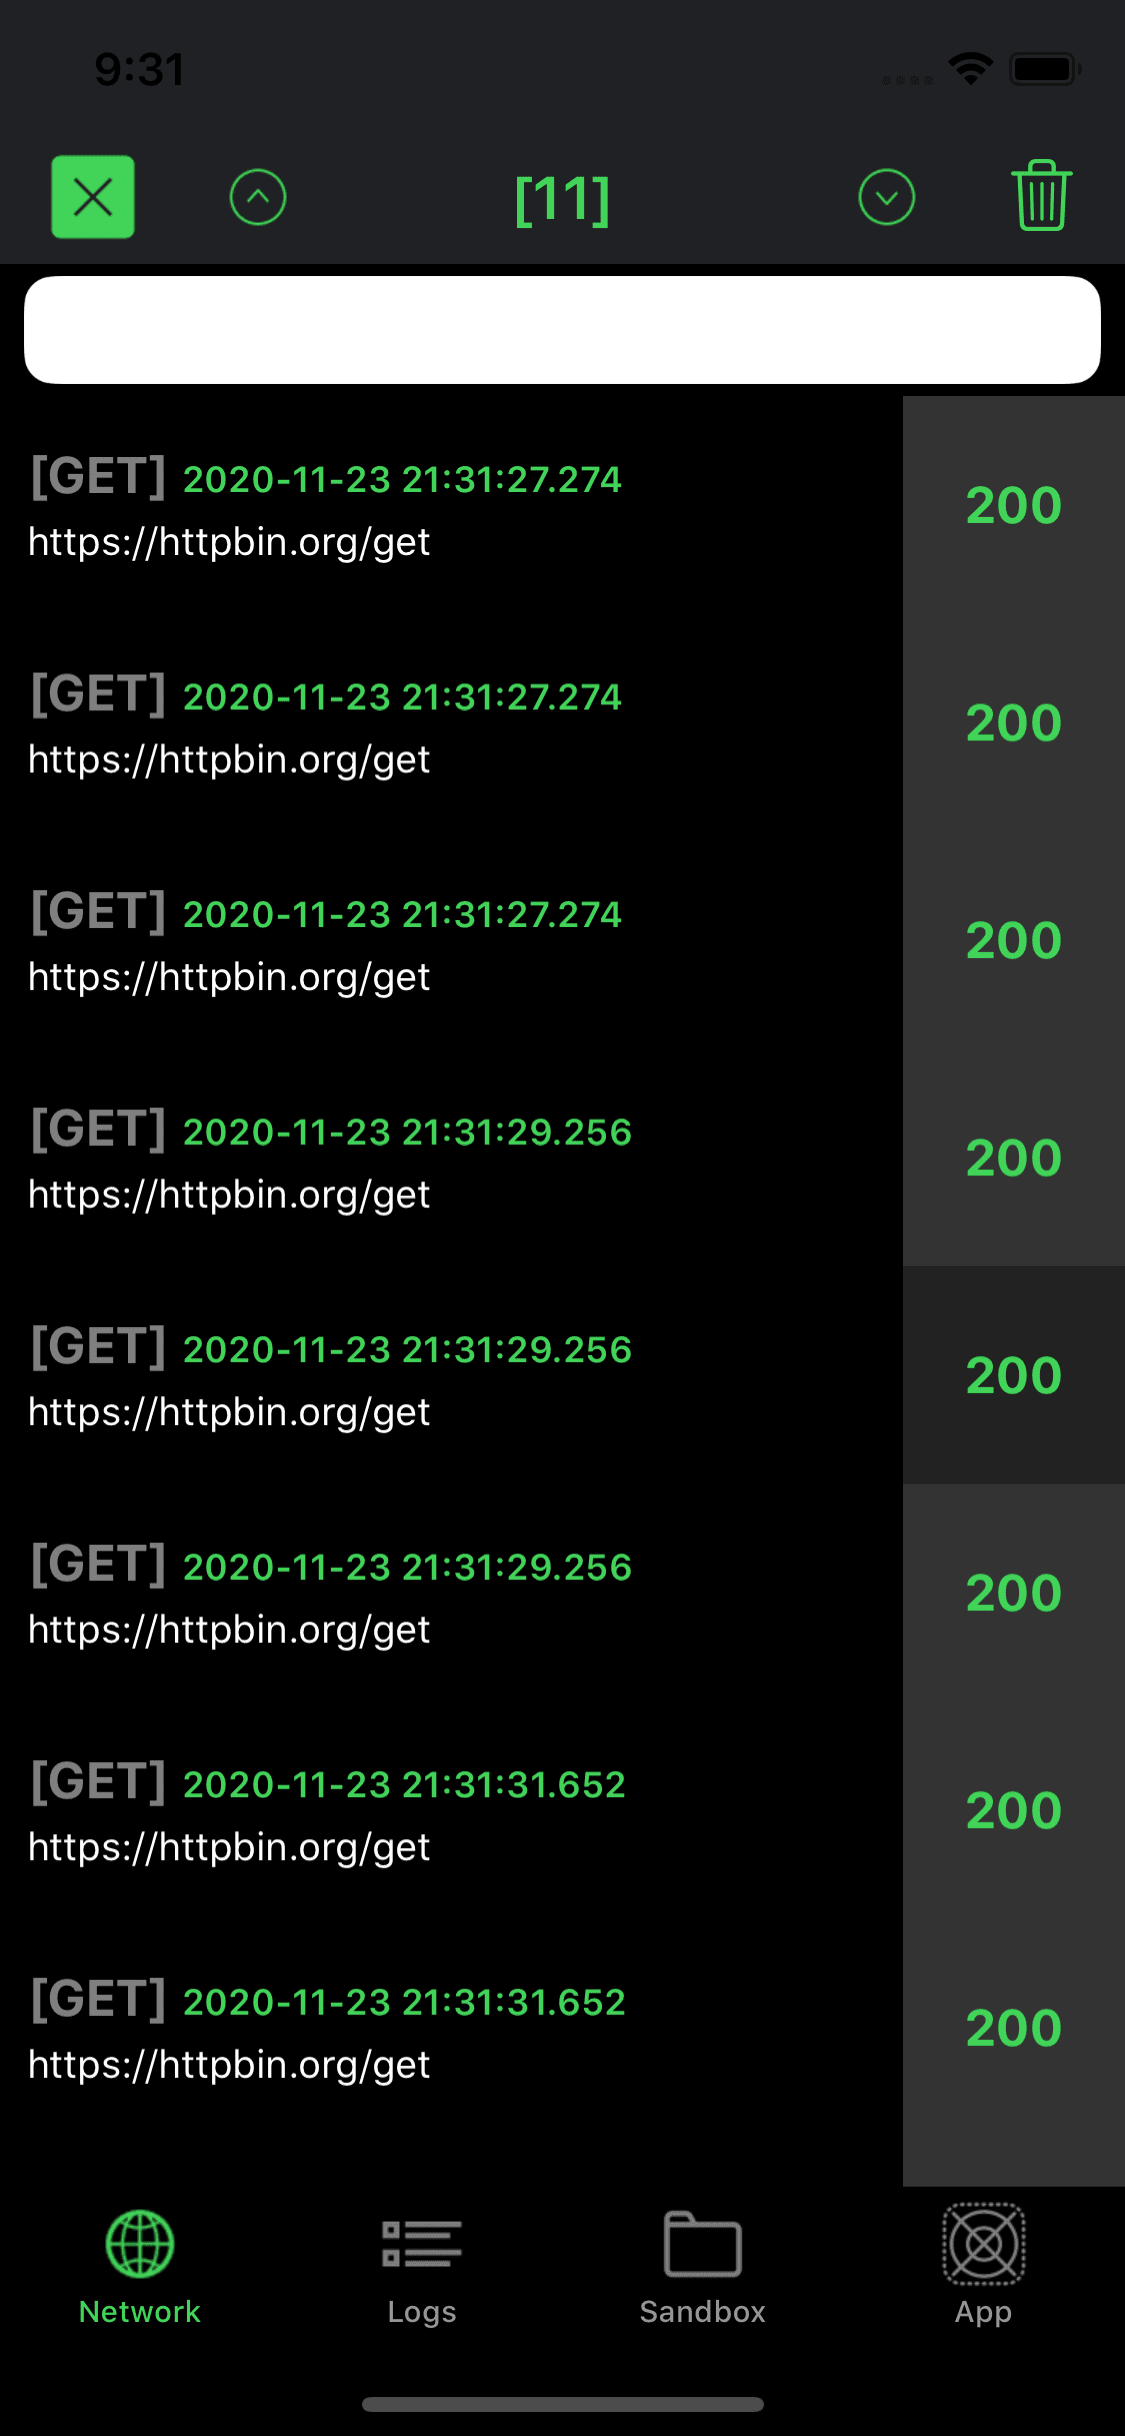
OS X Auditor is a free Mac OS X computer forensics tool
digital-forensicsdisk-forensicsforensics+4
3.1k6 years ago
CocoaDebug preview

CocoaDebug

GitHubcocoadebug/cocoadebug

iOS Debugging Tool 🚀
debuggersdynamic-analysis-sandboxingios-security+2
4.1k3 years ago
sigwire preview

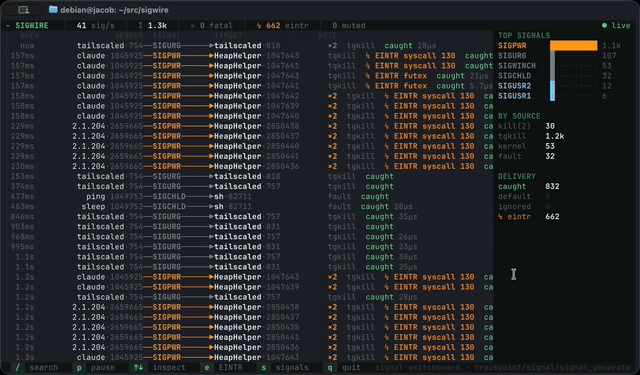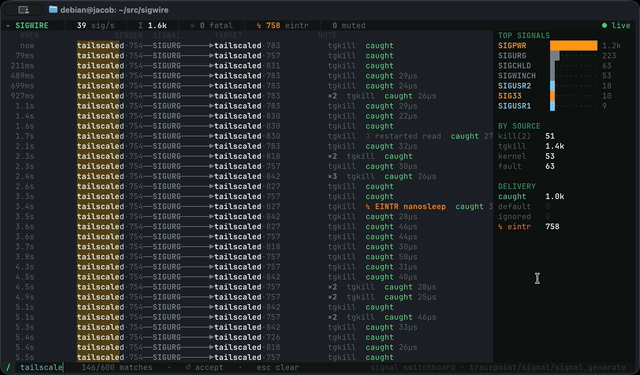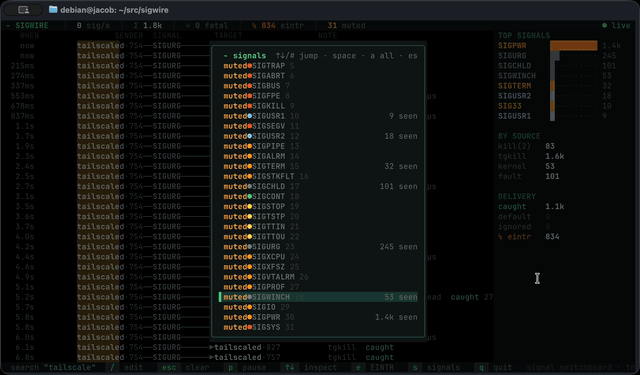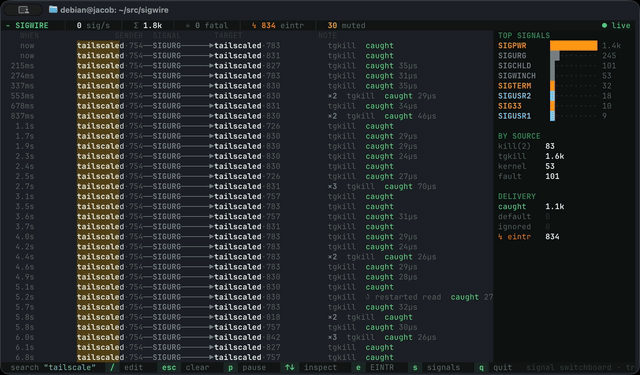
sigwire

GitHubyeet-src/sigwire

Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…

debuggersdynamic-analysis-sandboxingforensics+2
1612 months ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

database-securitydigital-forensicsdisk-forensics+8
856 months ago
Previous12Next