
tpotce
 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
defensive-toolseducationinformation-gathering+7
telekom-security/tpotce🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 securityjoes/masterparser
MasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs
 g0thamrabb1t/cve-2026-43284-dirtyfrag-detection
Lab validation report and detection artifacts for CVE-2026-43284 (DirtyFrag) Linux LPE. Provides auditd telemetry, event correlation rules, and…
 atlas-ghostshell/cve-2025-27558_patching
Patching CVE-2025-27558 vulnerability that had affected my linux image.
 g0thamrabb1t/cve-2026-46331-pedit-cow-detection
Defensive validation of CVE-2026-46331 / pedit COW with auditd, AppArmor, mitigation comparison and detection logic.
 pedrofbrm/apache-web-log-analysis-lab
Blue Team lab focused on analyzing Apache web access logs to detect directory brute forcing and web scanning activity.
 daryllundy/cve-2025-32463
Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
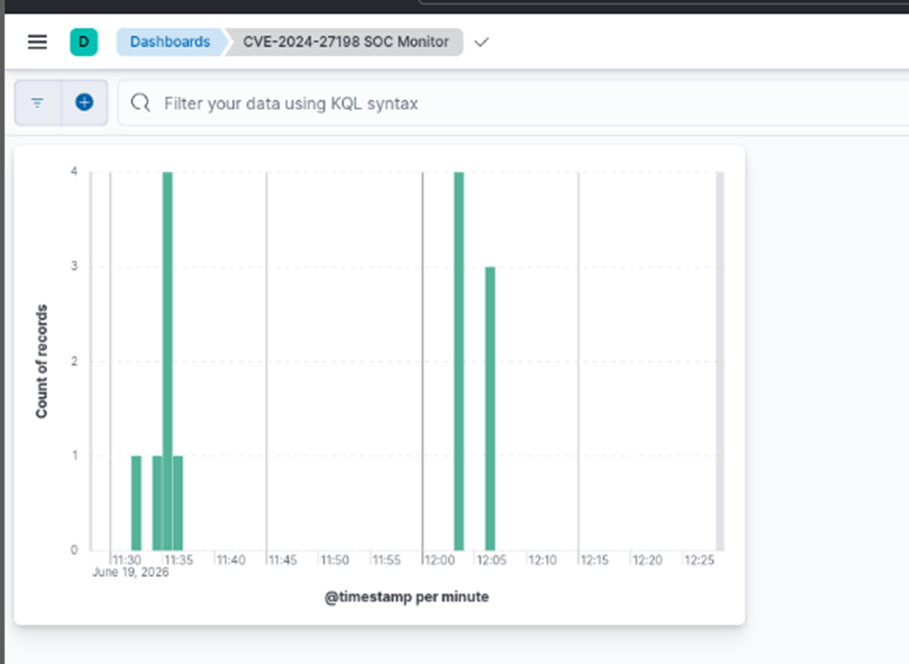 ptd200110/cve-2024-27198-soc-lab
SOC detection and incident response lab simulating CVE-2024-27198 authentication bypass in JetBrains TeamCity. Includes ELK SIEM, Suricata IDS, Sigma…
 mithileshan/soc-investigation-lab
End-to-end SOC investigation: CVE-2011-2523 kill chain, multi-source log correlation, incident report — MITRE ATT&CK T1190
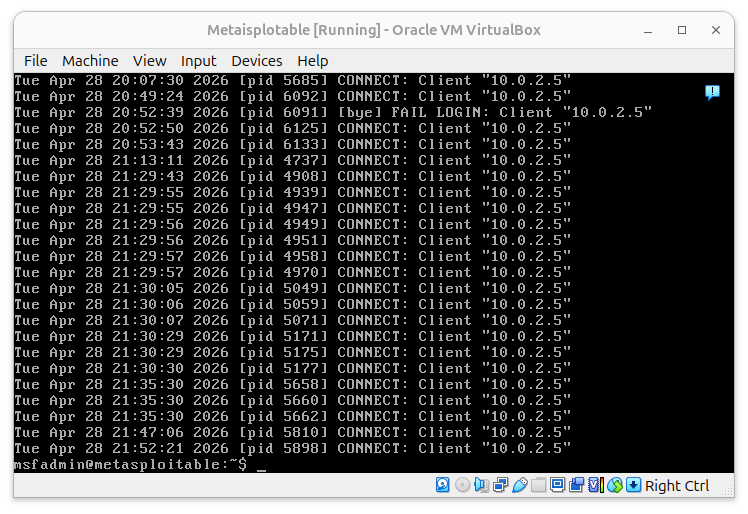 ivoalbacete/kali-metasploitable
Escaneo de vulnerabilidades, análisis de tráfico con Wireshark y explotación controlada del CVE-2011-2523 (vsftpd 2.3.4) en entorno de red segura.
 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
 alisha-chaudhary/ssh-enum
This project explores whether modern OpenSSH reveals valid usernames through subtle response or timing differences. CVE-2016-6210 user enumeration…

 itzmeshervin/siem-dashboard
A lightweight, real-time Security Information and Event Management (SIEM) dashboard built using Streamlit. It collects system logs, detects USB and…
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
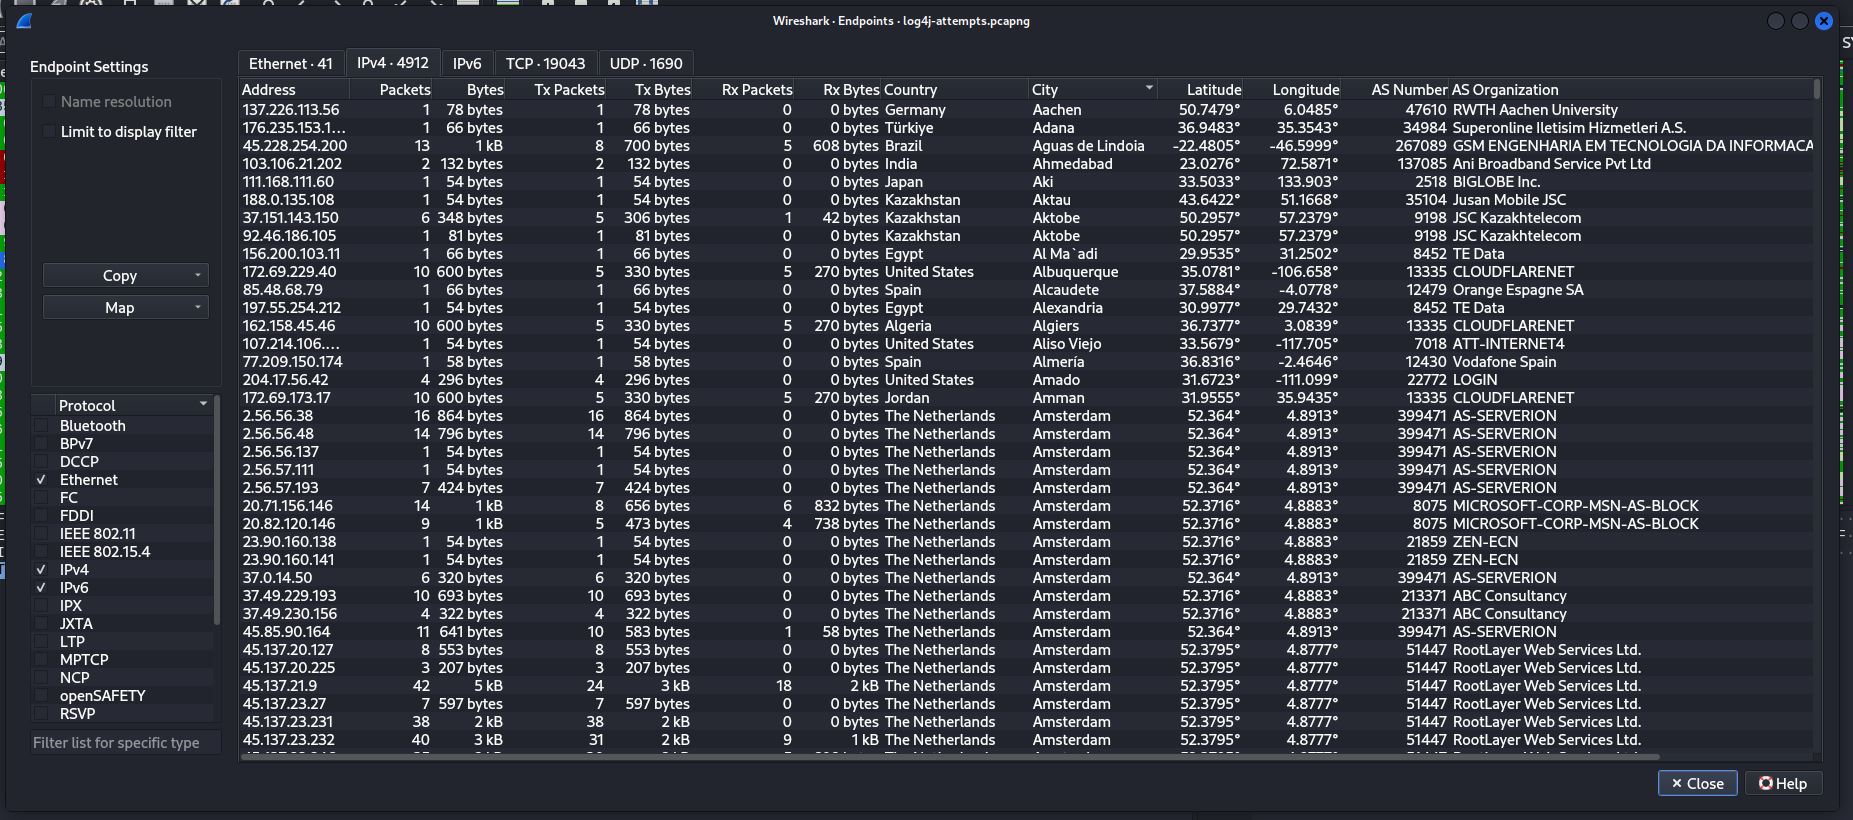 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools