
envocabulary
 sreckoskocilic/envocabulary
Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
configuration-auditingdigital-forensicsforensics+3
3
sreckoskocilic/envocabularyTrace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
 airbus-cert/etl-parser
Event Trace Log file parser in pure Python
 thecyberfairy/cve-lfi-lab
A hands on lab investigating CVE-2025-39507 from a Tier 1 SOC analyst perspective. Includes log review in Microsoft Sentinel, IP analysis, real world…
 zh54321/snafflerparser
Parses Snaffler output file and generate beautified outputs.
 withsecurelabs/macostriagecollectionscript
Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…
 cherrling/cve-2025-56499
Proof-of-concept exploit for CVE-2025-56499, demonstrating arbitrary file read via missing path validation in mihomo's rule-provider configuration,…
 hackinglz/panrapidcheck
Extract useful information from PANOS support file for CVE-2024-3400
 garethmsheldon/cve-2025-60787-detection-motioneye-rce-via-config-injection
Detection rules and YARA/KQL signatures for CVE-2025-60787, an unauthenticated RCE in motionEye via config injection, with process execution and file…
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 sentinelblue/cve-2022-29072
** DISPUTED ** 7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the…
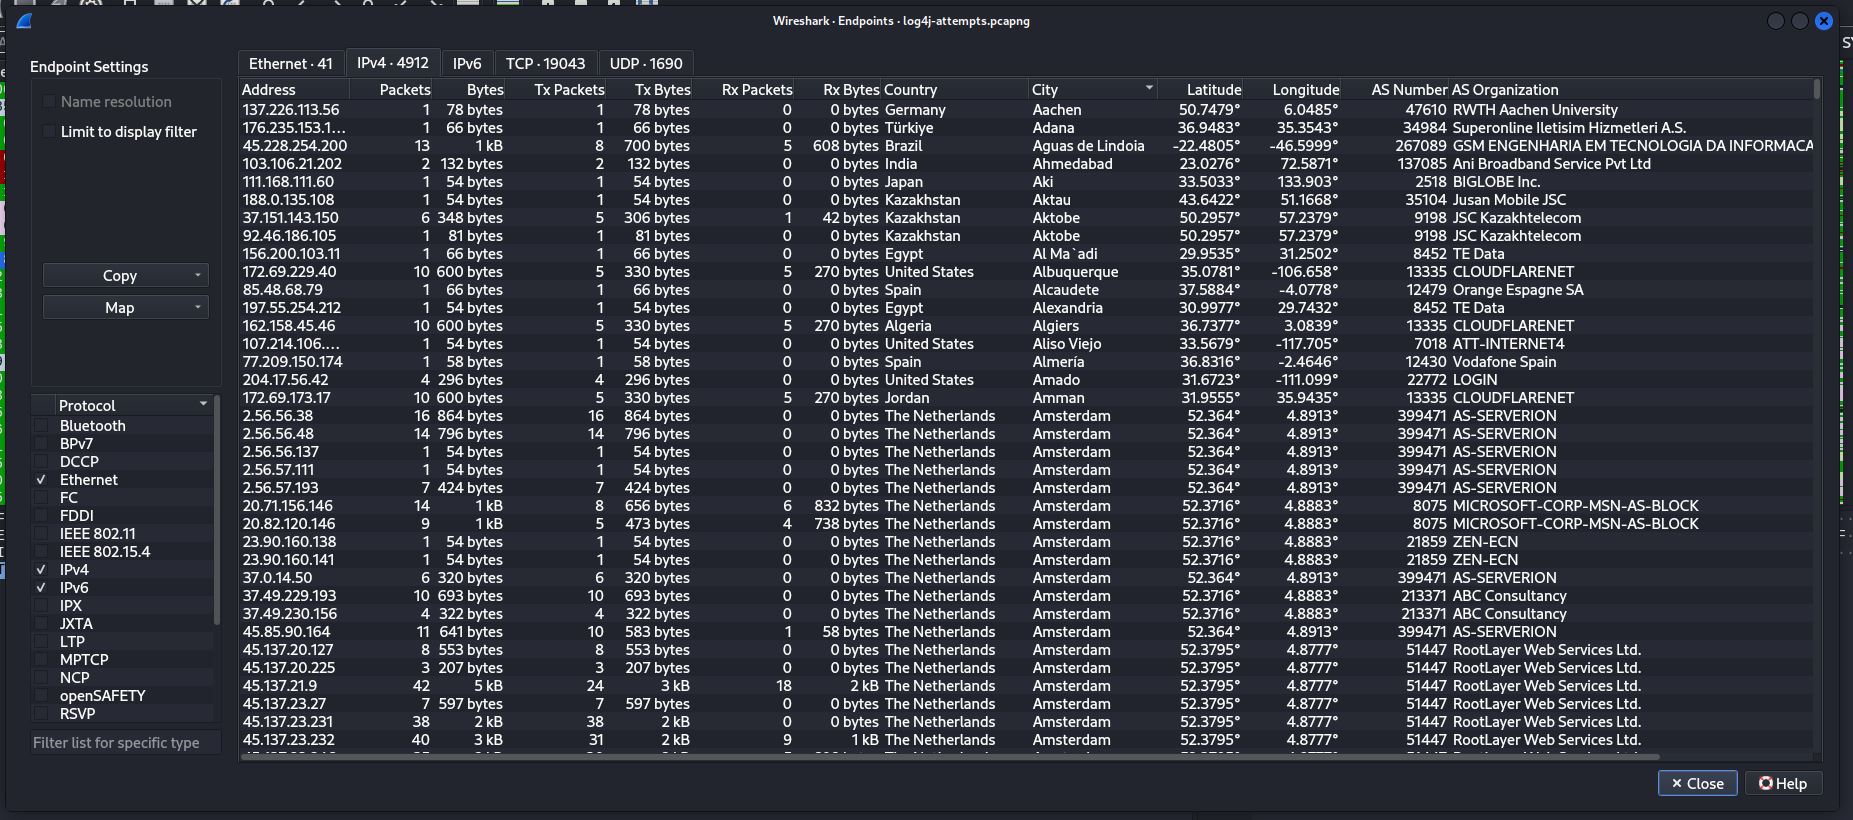 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 target/strelka-ui
Strelka Web UI for File Submission and Analysis
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 jschicht/logfileparser
Parser for $LogFile on NTFS
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 ossec/ossec-hids
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis, file integrity checking, policy monitoring, rootkit…
 nextronsystems/sysmon-config
Sysmon configuration file template with default high-quality event tracing
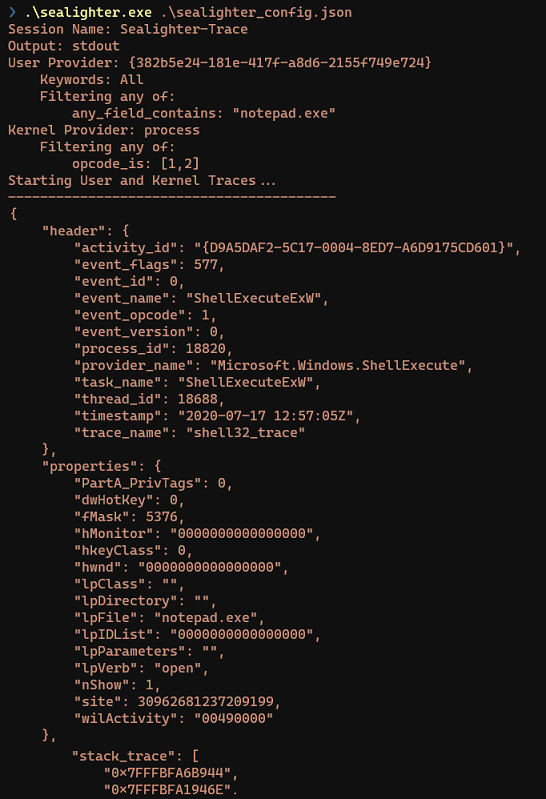 pathtofile/sealighter
ETW and WPP tracing tool for security research. Subscribes to multiple providers, auto-parses events to JSON, and supports advanced filtering,…