
RsWindowsThingies
Rust-based Windows forensic toolkit for real-time MFT monitoring, event log streaming, and channel enumeration, enabling live system analysis and…

Rust-based Windows forensic toolkit for real-time MFT monitoring, event log streaming, and channel enumeration, enabling live system analysis and…

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.

Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally

Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…

An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…

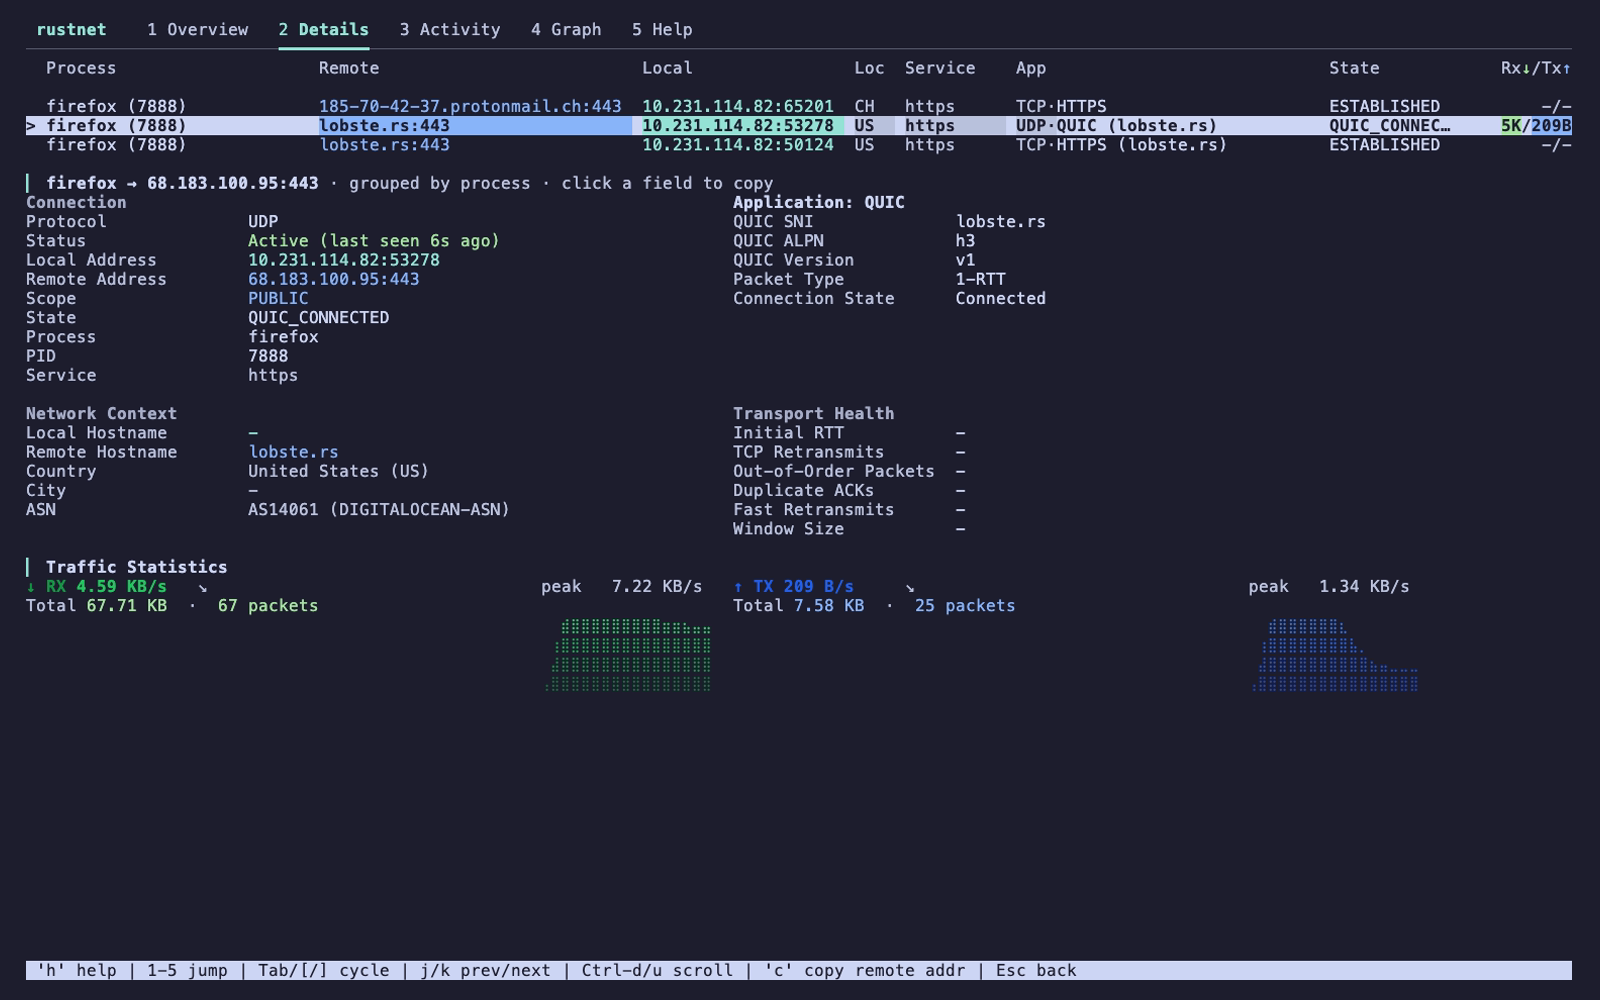
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

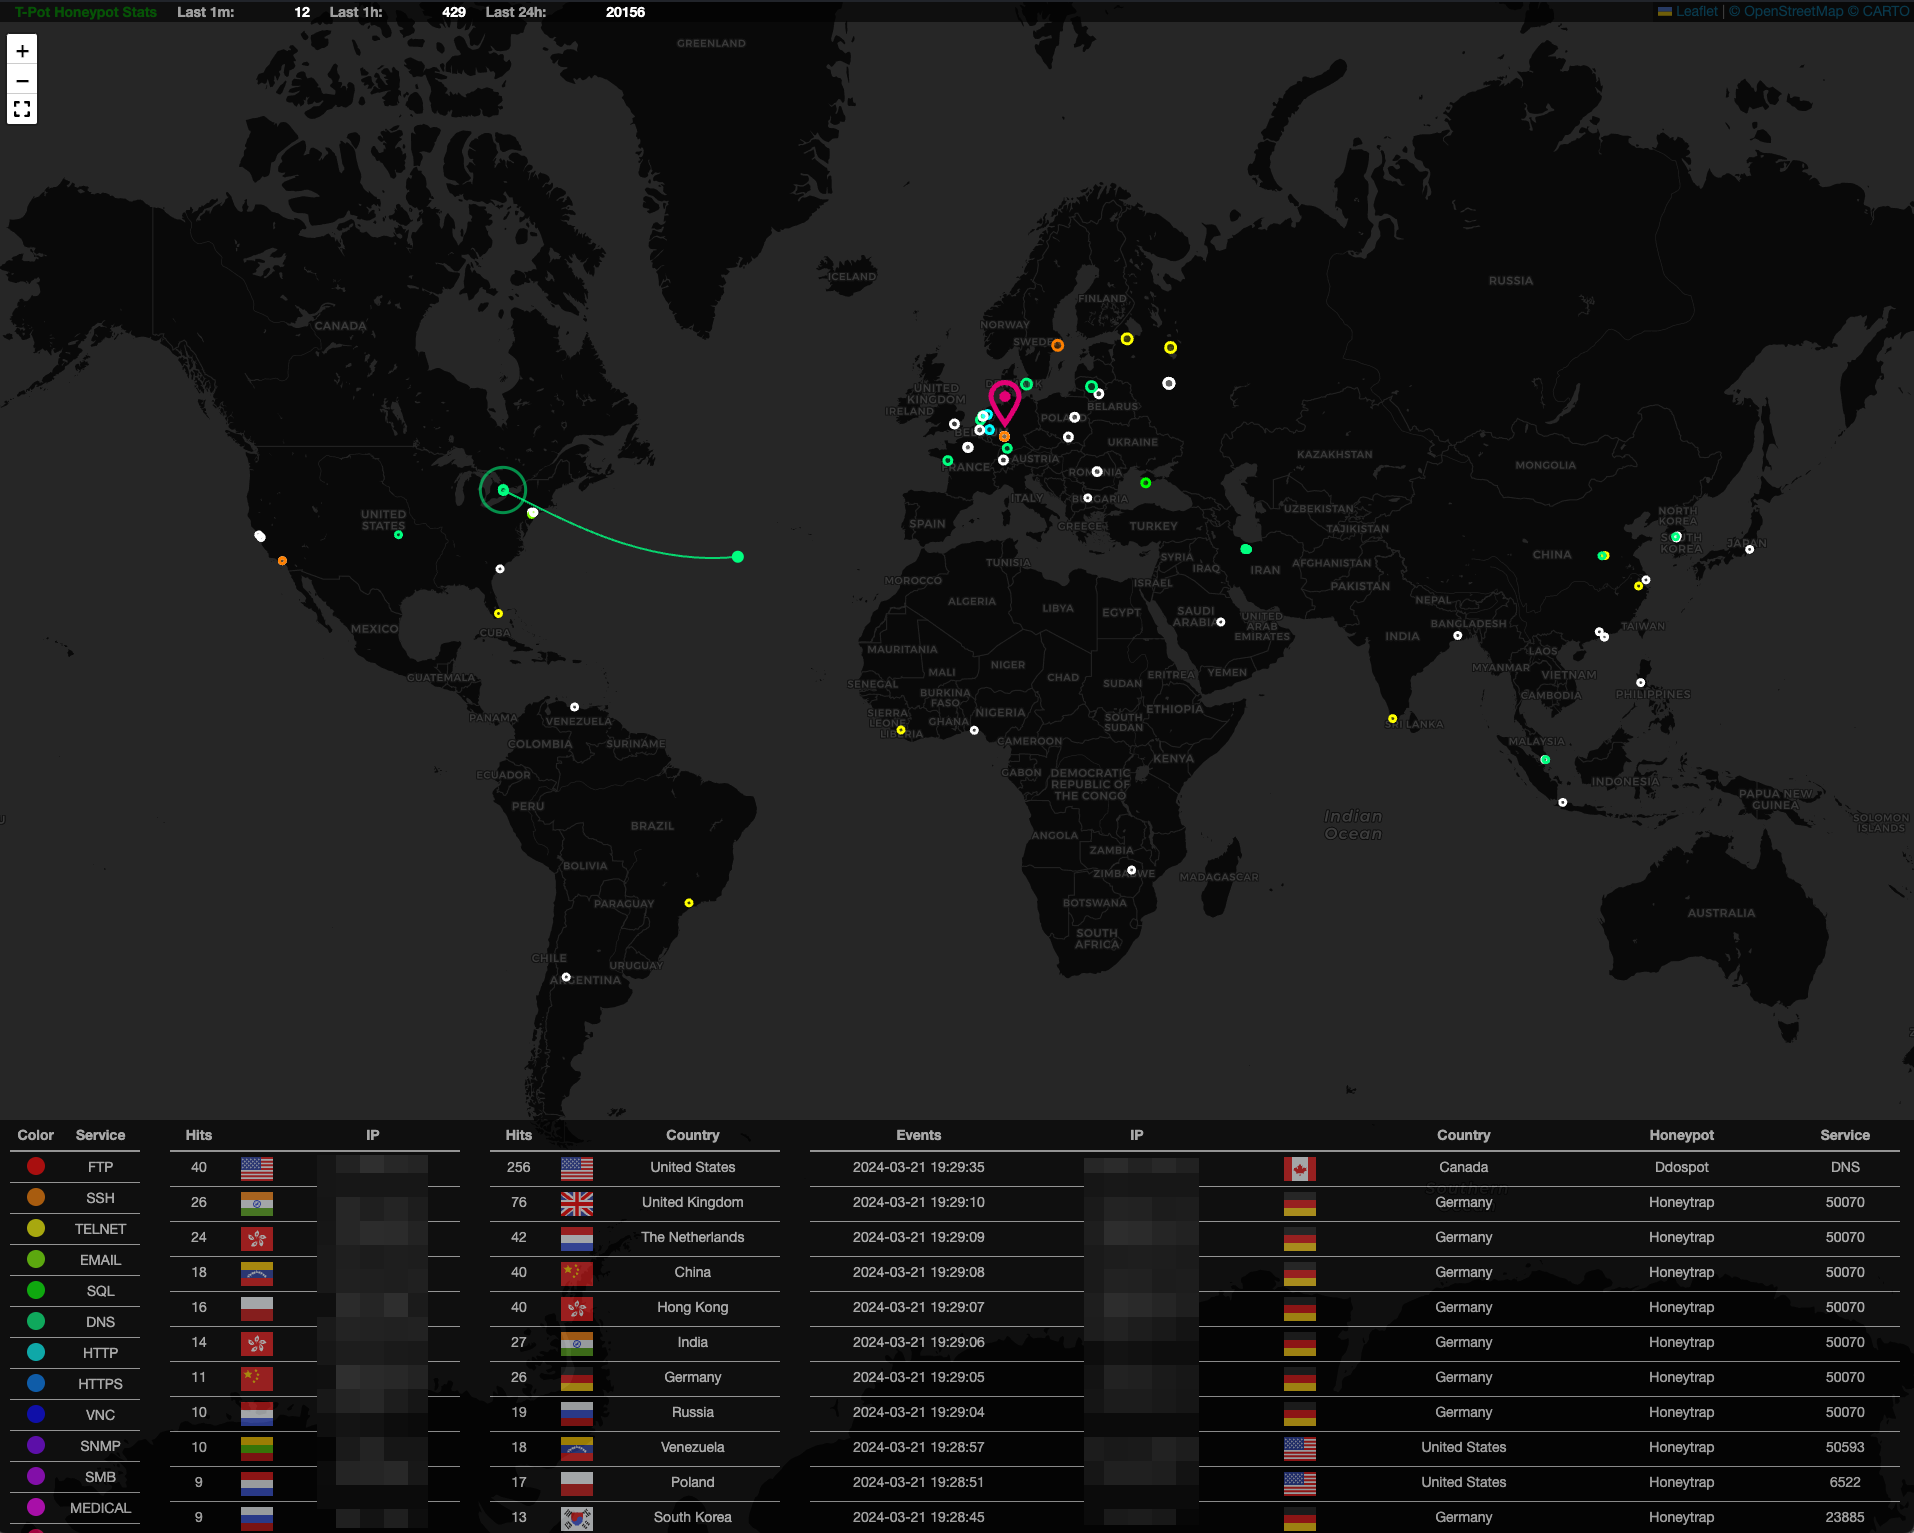
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝

Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.

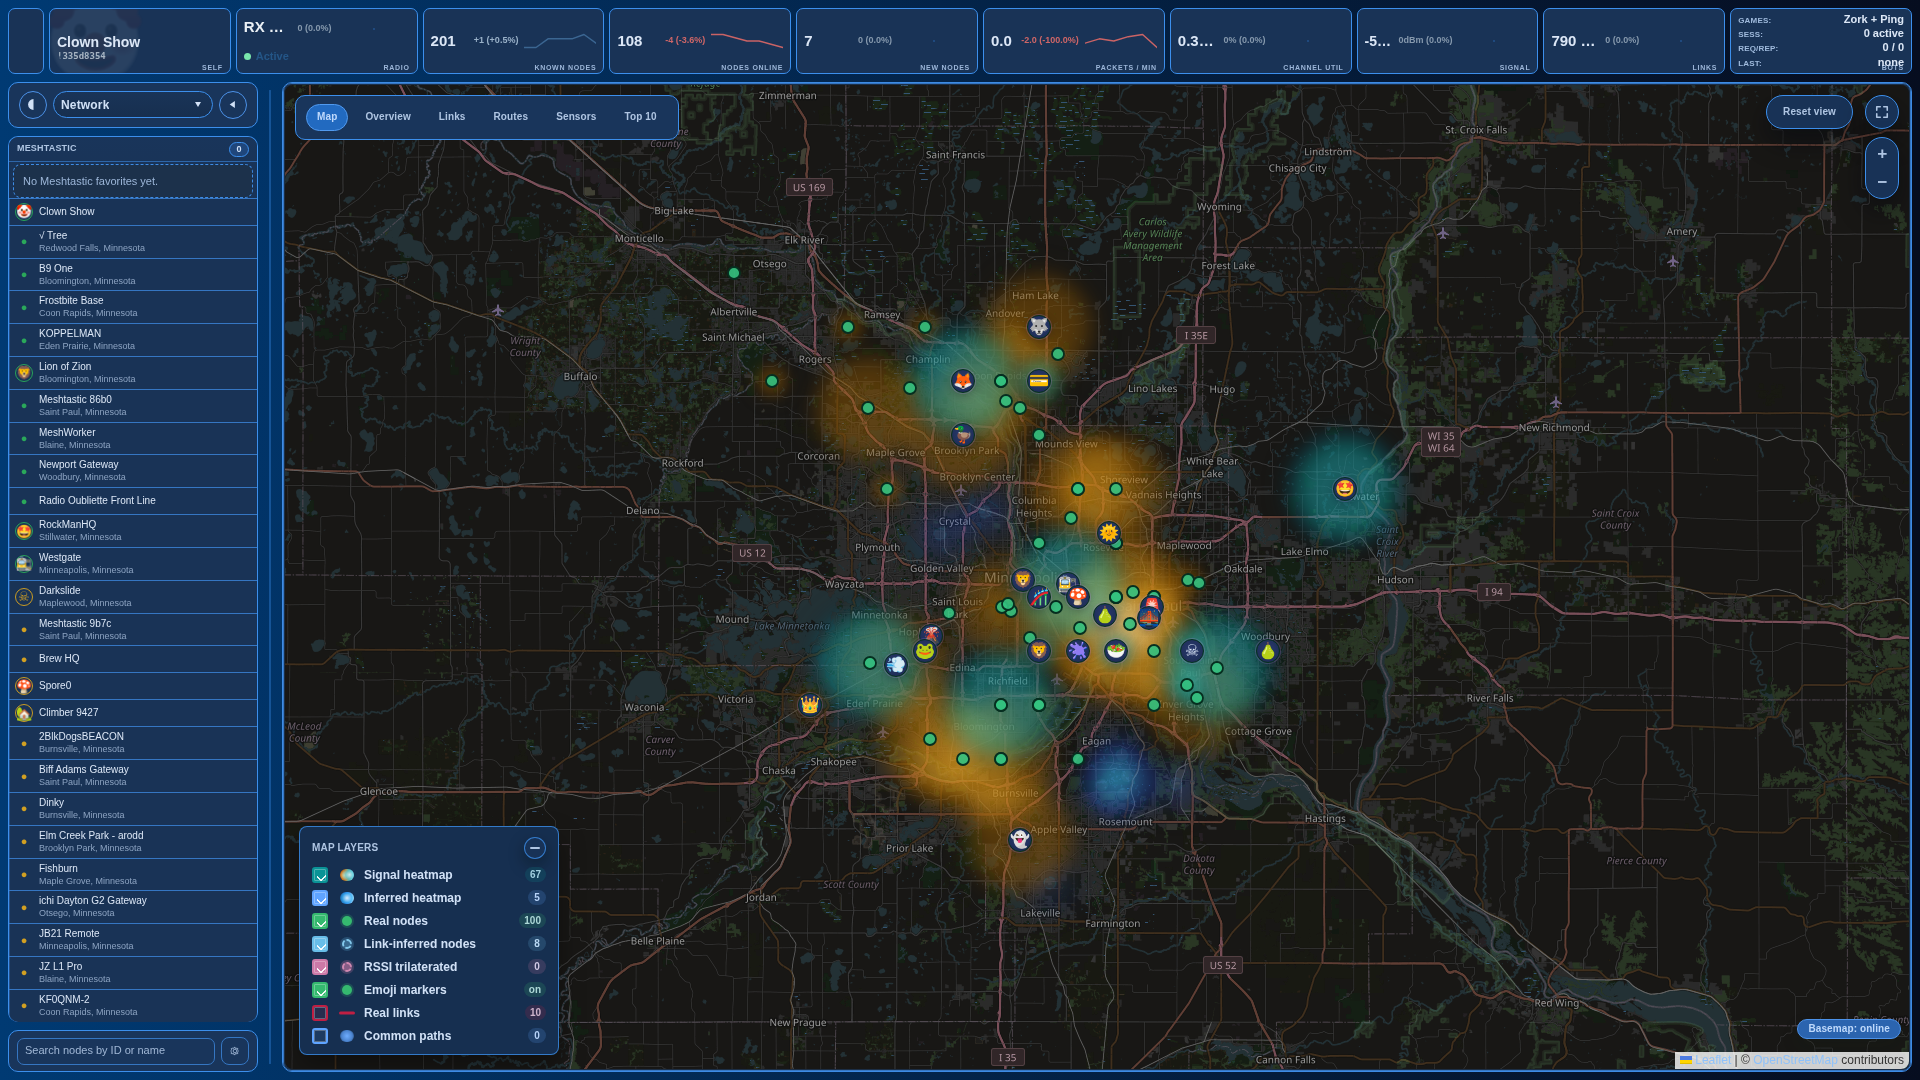
Single-page web dashboard for Meshtastic mesh networks with live network mapping, packet analysis, chat, sensor telemetry, and topology…

Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.

Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.

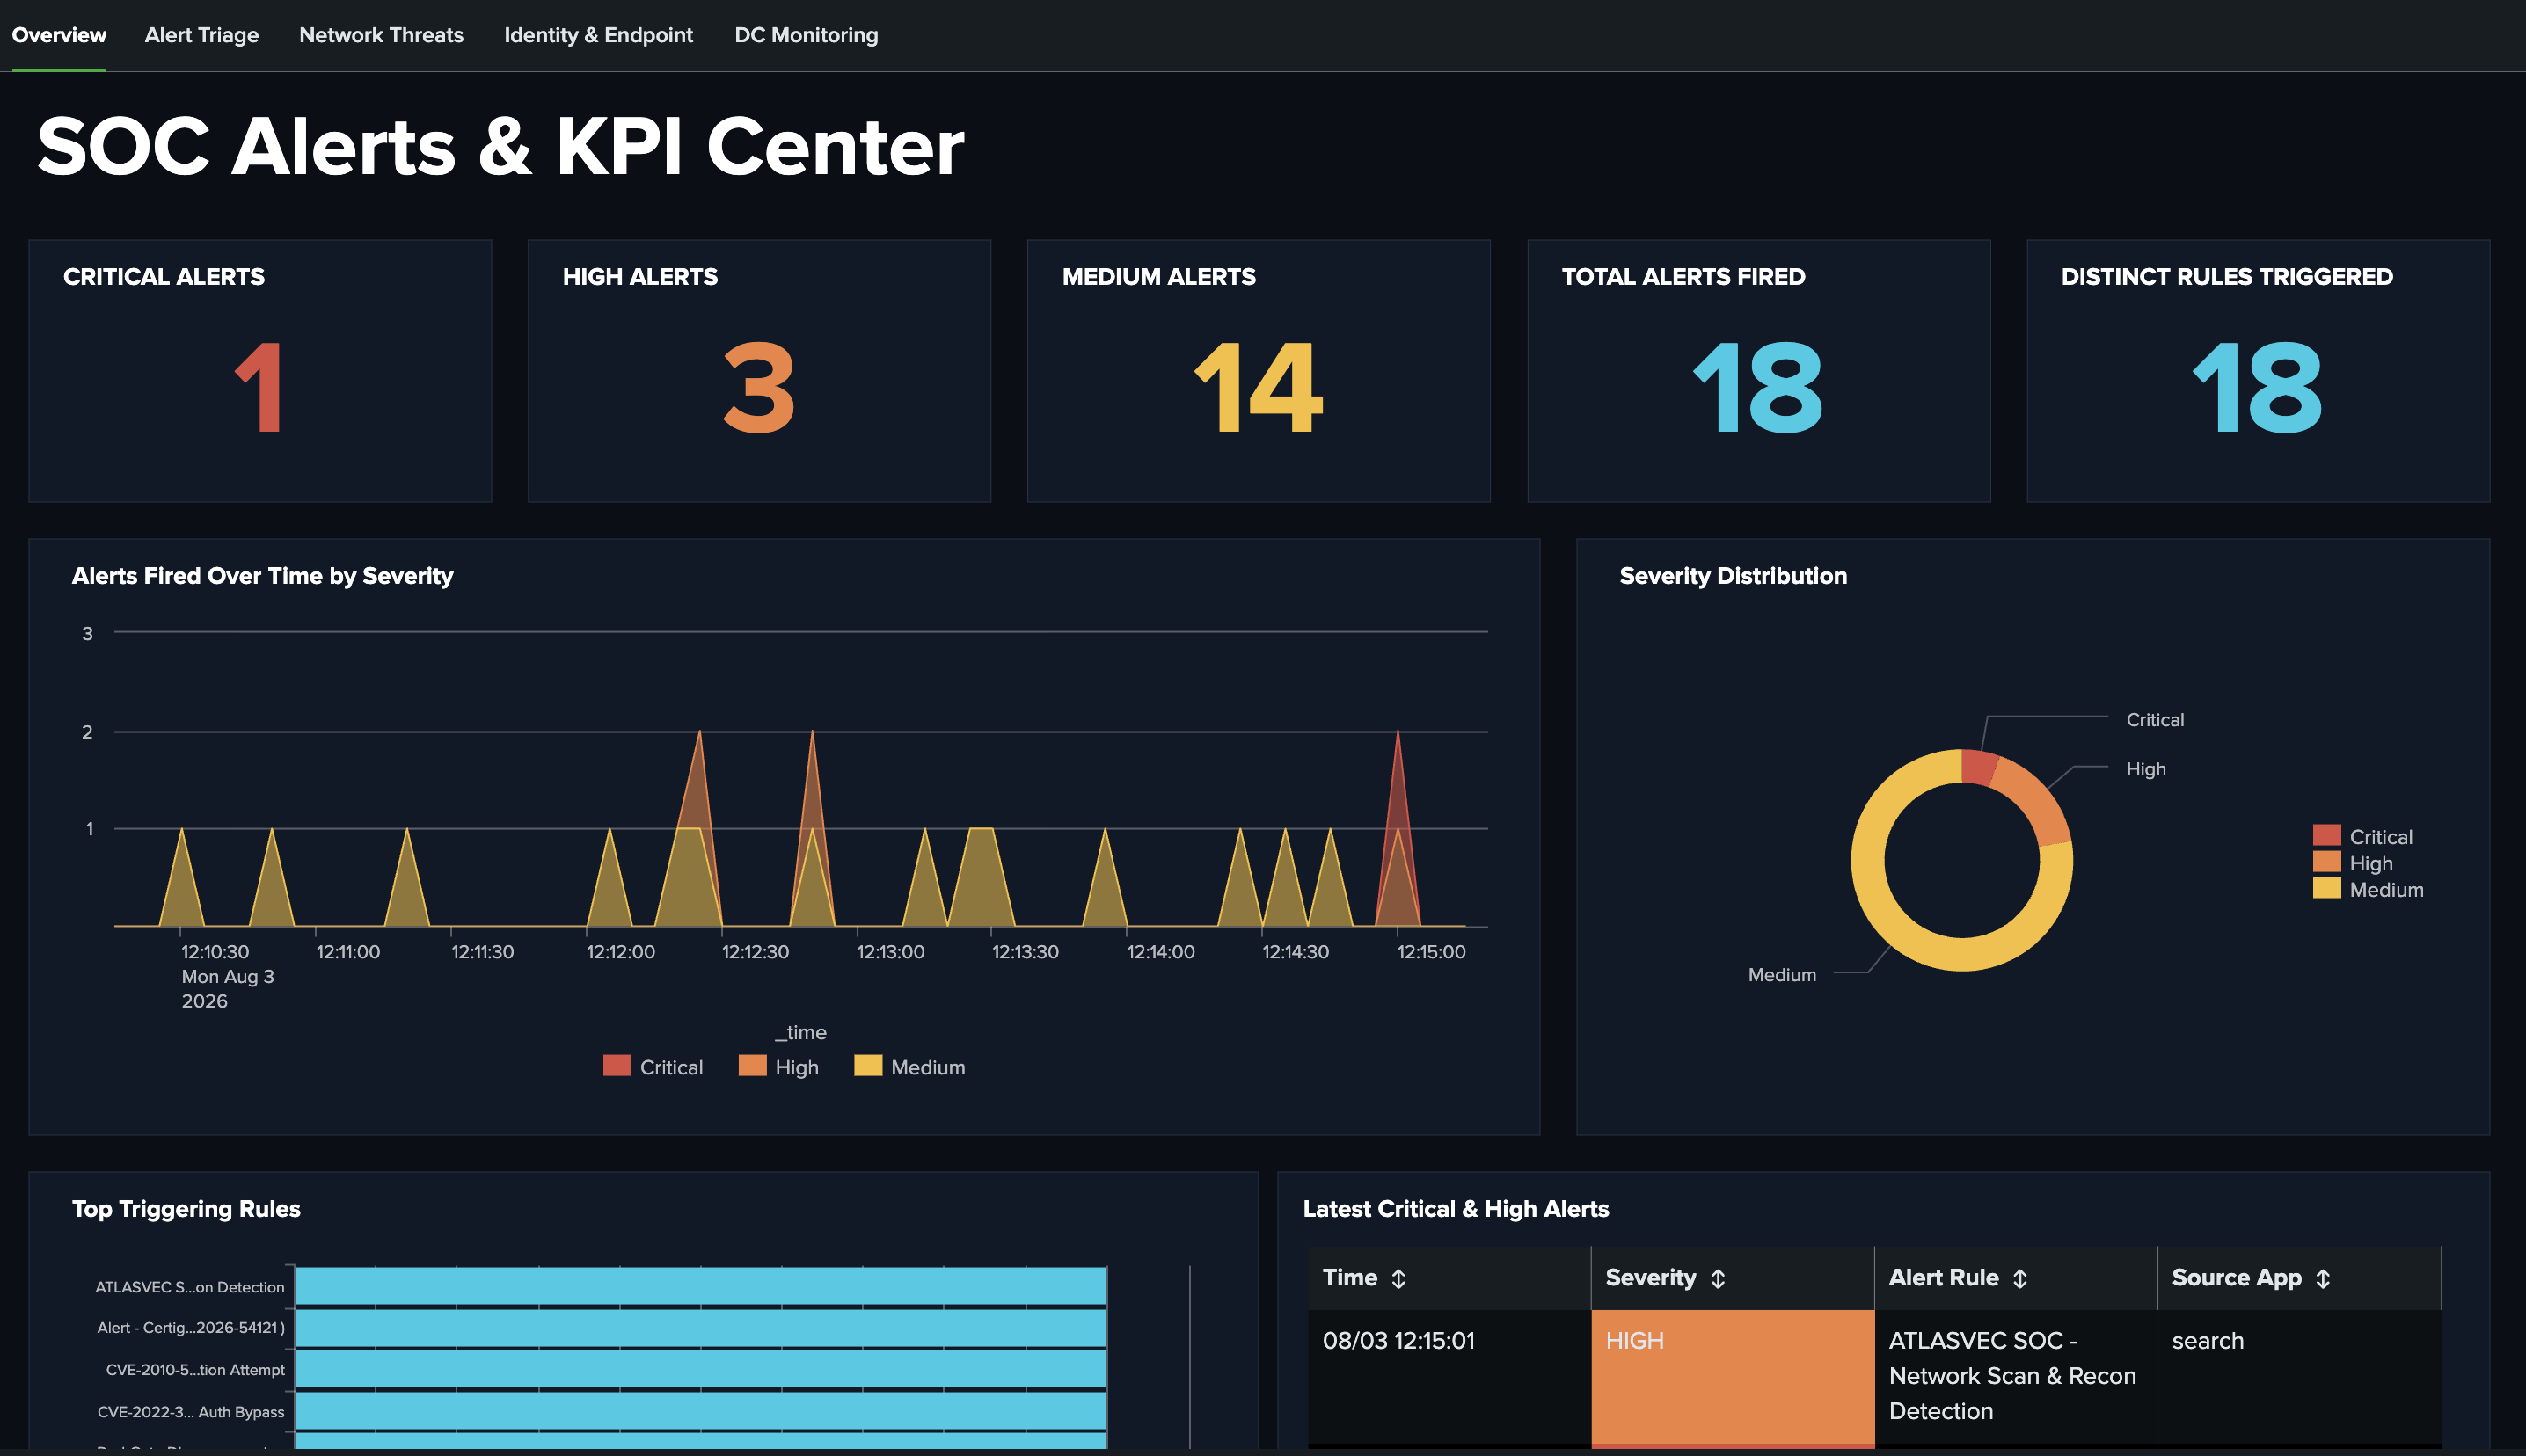
Splunk detection writeup for CVE-2026-54121 (CertiGhost): AD CS certificate chase abuse leading to full domain compromise. Lab-validated detection,…

Performed a live cybersecurity assessment on a university Linux server. During analysis, active attack activity was identified, including brute-force…

Easy-to-use live forensics toolbox for Linux endpoints