

scripts
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
digital-forensicsforensicsincident-response+5
86
clausing/scriptsCollection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
 nccgroup/mortimer
A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.
 googlecloudplatform/professional-services
Collection of Google Cloud solution examples and operational utilities for audit log monitoring, DLP de-identification, encryption key management,…
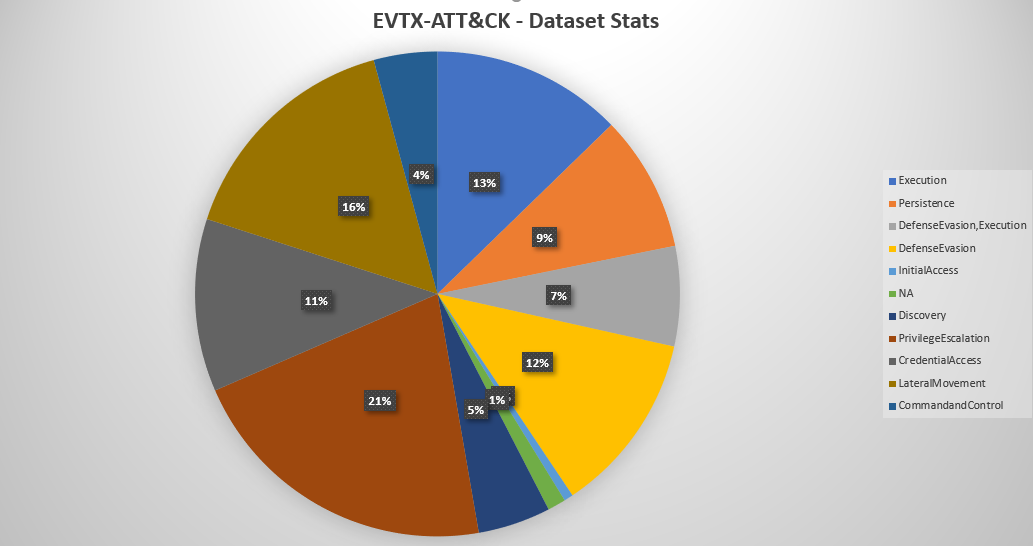 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
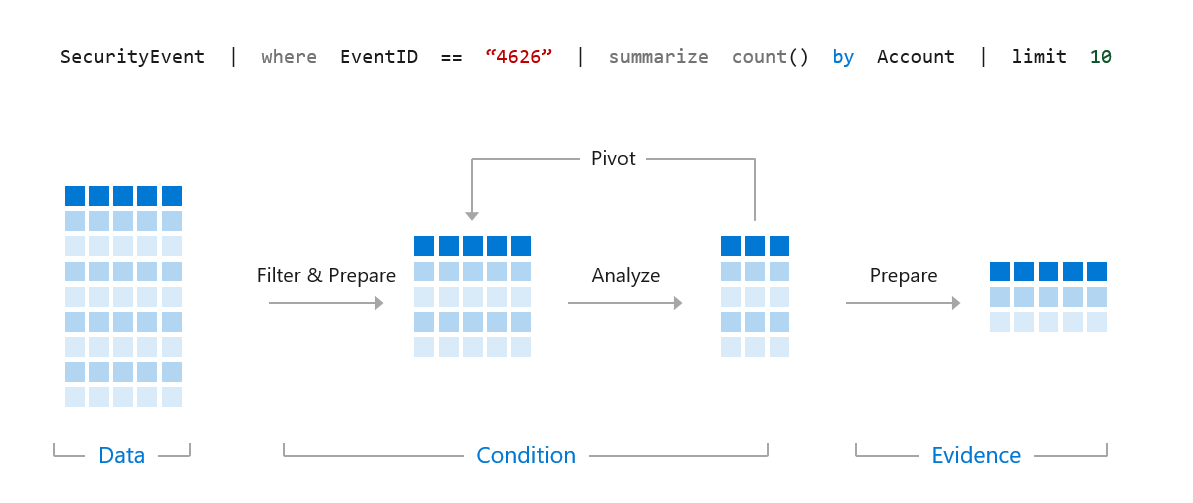 reprise99/sentinel-queries
Collection of KQL queries
 justicerage/freedomfighting
A collection of scripts which may come in handy during your freedom fighting activities.
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
 pe3zx/crowdstrike-falcon-queries
A collection of Splunk's Search Processing Language (SPL) for Threat Hunting with CrowdStrike Falcon
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
 randomuserid/adama
Searches For Threat Hunting and Security Analytics
 gitlab-security-oss/tldr
Sigma-based detection rules, log queries, atomic tests, and response procedures for monitoring and threat hunting in GitLab environments.
 embee-research/sigma
A repository to release detection rules to the public
 17patmaks/my-sigma-rule-collection
Sigma Rule for CVE-2025-49666
 asmitdesai/ubuntils
Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 withsecurelabs/linuxcatscale
Incident Response collection and processing scripts with automated reporting scripts