Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
334 results
mimikatz-detector-condrv preview

mimikatz-detector-condrv

GitHubnccgroup/mimikatz-detector-condrv

The Console Monitor Driver is a KMDF kernel-mode filter driver that captures certain Fast I/O operations (input and output) that is sent to or from…

anomaly-detectiondefensive-toolsincident-response+3
42
4 years ago
OSTE-Web-Log-Analyzer preview

OSTE-Web-Log-Analyzer

GitHubostesayed/oste-web-log-analyzer

OSTE WLA automate the process of analyzing web server logs with the Python Web Log Analyzer.

anomaly-detectionintrusion-detectionlog-analysis+2
442 years ago
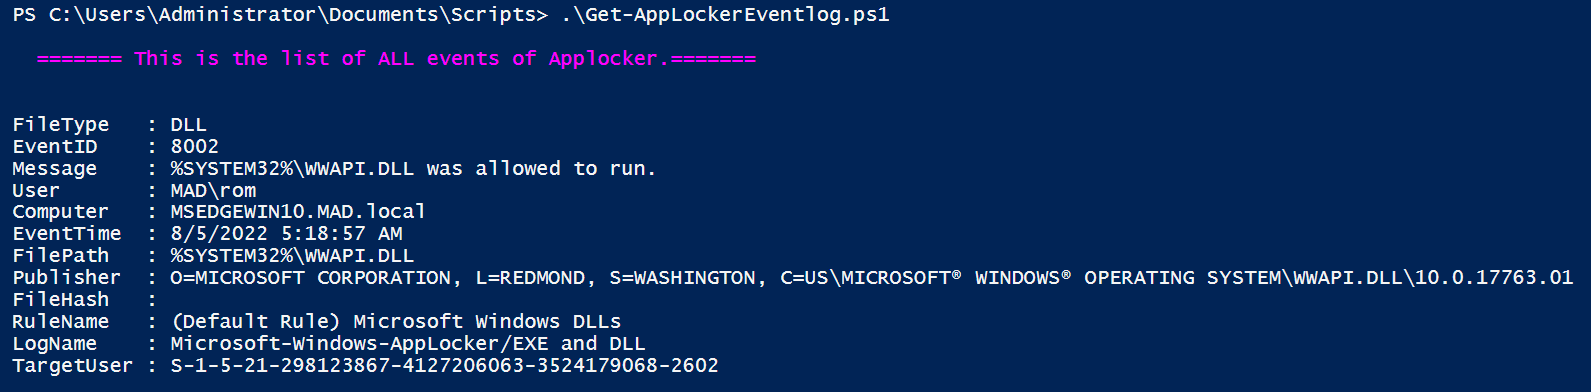
Get-AppLockerEventlog preview

Get-AppLockerEventlog

GitHubromaissaadjailia/get-applockereventlog

This is a repo for fetching Applocker event log by parsing the win-event log

forensicsincident-responselog-analysis+1
294 years ago
IntelligentProcessLifecycle preview

IntelligentProcessLifecycle

GitHubd3sre/intelligentprocesslifecycle

The Intelligent Process Lifecycle of Active Cyber Defenders

configuration-auditingcurated-resourceseducation+6
343 years ago
ltm preview

ltm

GitHubagent-hellboy/ltm

ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…

debuggersdigital-forensicsdisk-forensics+7
233 months ago
keycloak-cve-2026-18963-hunt preview

keycloak-cve-2026-18963-hunt

GitHubkyos-public/keycloak-cve-2026-18963-hunt

Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database

authenticationdatabase-securitydigital-forensics+3
165 days ago
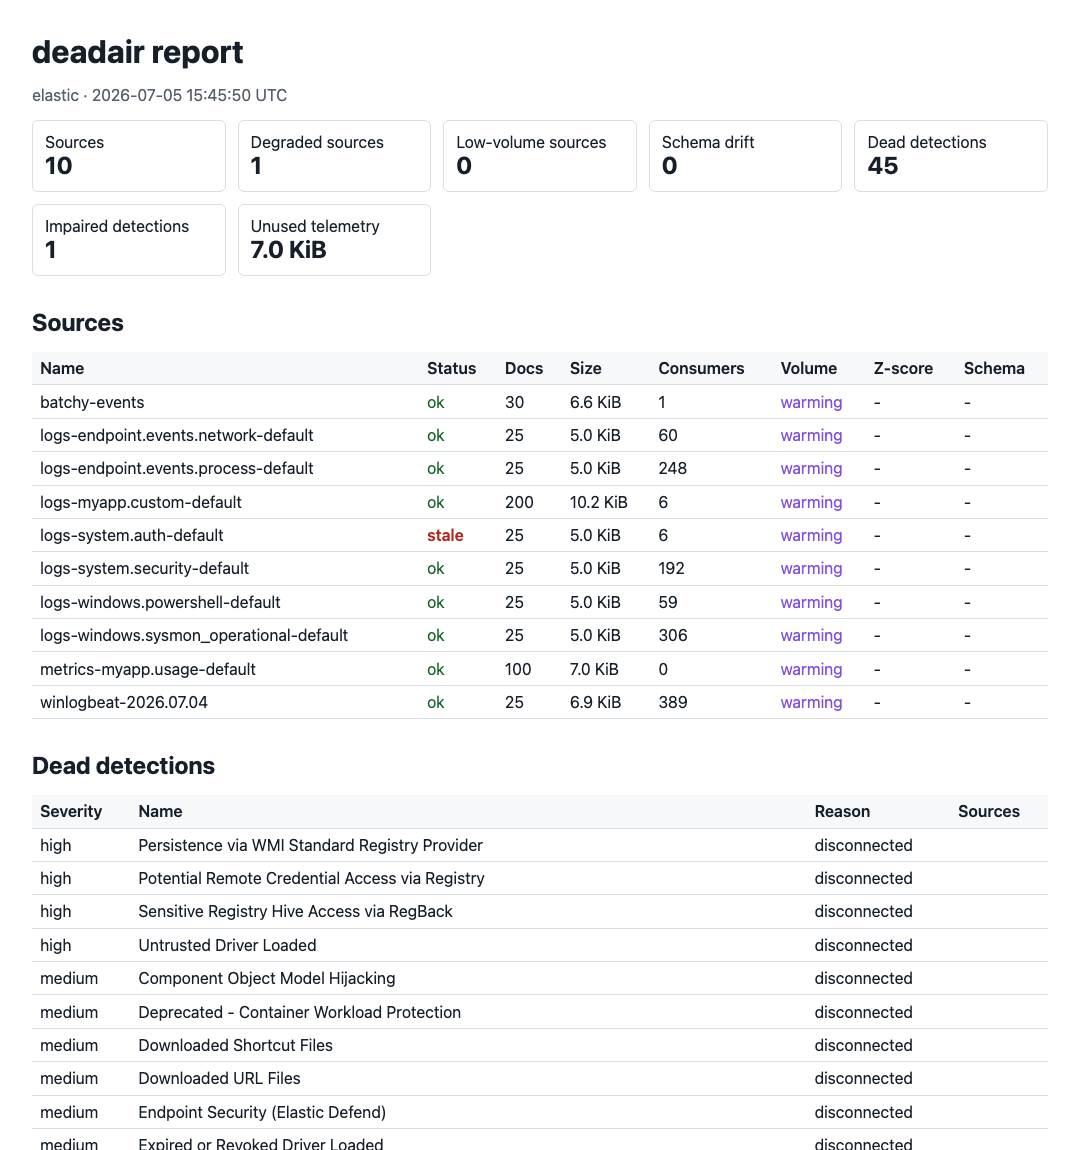
deadair preview

deadair

GitHubbig-comfy/deadair

Finds the detection rules in your SIEM that are running blind

configuration-auditinglog-analysisvulnerability-analysis
61 month ago
mimikatz-detector-busylight preview

mimikatz-detector-busylight

GitHubnccgroup/mimikatz-detector-busylight

USB HID driver emulation with PID/VID (0x3bca/0x27bb) of Plenom A/S Busylight Alpha, that is supported by Mimikatz. When mimikatz is executed, a…

defensive-toolsincident-responseintrusion-detection+3
214 years ago
DFIRHub preview

DFIRHub

GitHublascc/dfirhub

Search Windows forensic artifacts, see where each one lives on disk, and copy the KAPE command to collect it. Also builds collection scripts and…

curated-resourcesdigital-forensicsforensics+4
101 day ago
secfesc preview

secfesc

GitHubake13-art/secfesc

Lightweight security state inspector for Linux — bridging the gap between pretty fetch tools and heavy-duty audit frameworks.

authenticationconfiguration-auditingdefensive-tools+3
204 months ago
ZeroLogon-Exploitation-Check preview

ZeroLogon-Exploitation-Check

GitHubyossisassi/zerologon-exploitation-check

quick'n'dirty automated checks for potential exploitation of CVE-2020-1472 (aka ZeroLogon), using leading artifects in determining an actual…

exploitationincident-responseinformation-gathering+3
75 years ago
CVE-2025-61882-Oracle-E-Business-Suite-Pre-Auth-RCE-Exploit preview

CVE-2025-61882-Oracle-E-Business-Suite-Pre-Auth-RCE-Exploit

GitHubadityabhatt3010/cve-2025-61882-oracle-e-business-suite-pre-auth-rce-exploit

A critical pre-authentication Remote Code Execution (RCE) flaw in Oracle E-Business Suite (versions 12.2.3 - 12.2.14) allows attackers to gain full…

exploitationforensicsincident-response+4
121 year ago
Sigma preview

Sigma

GitHubembee-research/sigma

A repository to release detection rules to the public

curated-resourcesdefensive-toolsincident-response+3
83 years ago
CVE-2022-29072 preview

CVE-2022-29072

GitHubsentinelblue/cve-2022-29072

** DISPUTED ** 7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the…

exploitationincident-responselog-analysis+3
84 years ago
Detection-Rules preview

Detection-Rules

GitHubmanishrawat21/detection-rules

This repository contains validated detection rules for adversary behaviors observed during APT29 simulation. Each rule was tested against the actual…

curated-resourceseducationintrusion-detection+4
42 months ago
SecLog preview

SecLog

GitHubseclog-open/seclog

Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…

anomaly-detectiondynamic-analysis-sandboxingeducation+6
211 days ago
DetectTrace preview

DetectTrace

GitHubg0dse11/detecttrace

Open-source detection engineering tool that traces security detections end to end and identifies the first failing stage.

defensive-toolsdevsecopsincident-response+5
228 days ago
quietos-sentinel preview

quietos-sentinel

GitHubjondean213-pixel/quietos-sentinel

Sentinel — DeanWay Labs' inbound governor. Guards what an AI agent hears: world content is data, never orders. The mirror of QuietOS.

ai-securitydefensive-toolsincident-response+2
210 days ago
Previous1…345…19Next