logdata-anomaly-miner

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

Purpleteam scripts simulation & Detection - trigger events for SOC detections

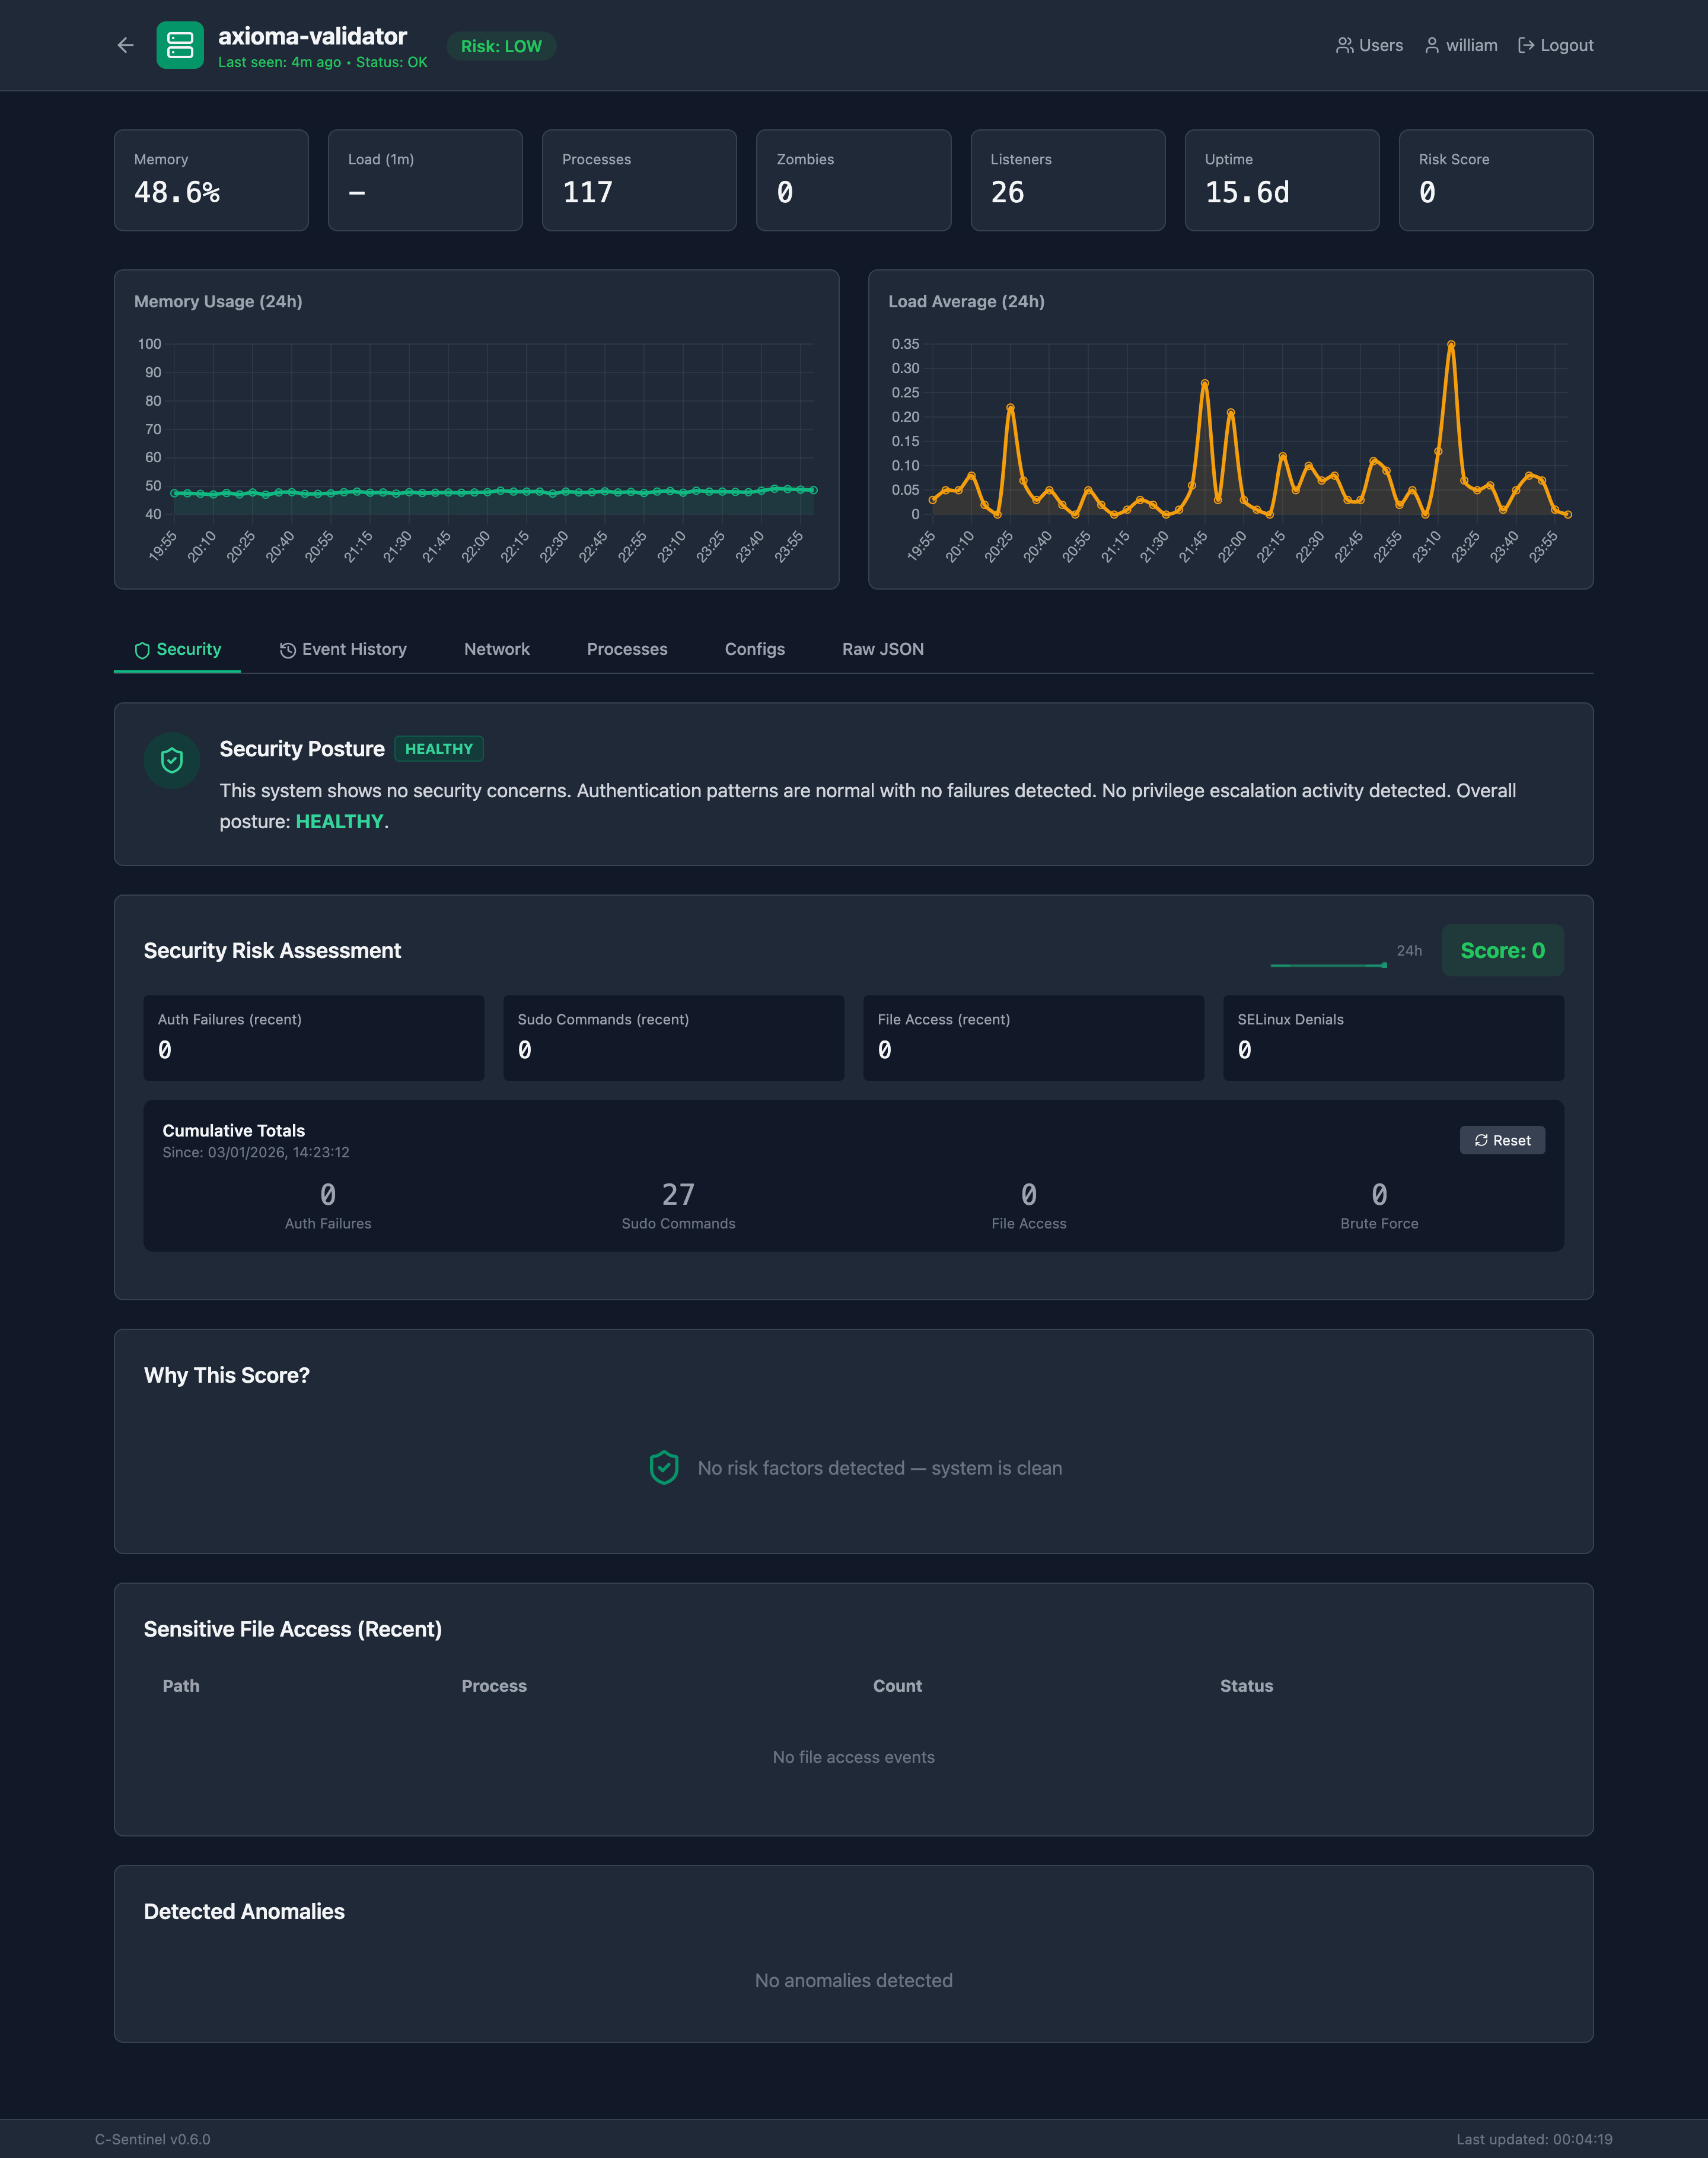
Semantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…

Analyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…

USB port access control tool for Debian with whitelist management, automatic background scanning daemon, and CLI interface to block or allow USB…

Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…

SQL powered operating system instrumentation, monitoring, and analytics.

The easiest, and most secure way to access and protect all of your infrastructure.

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

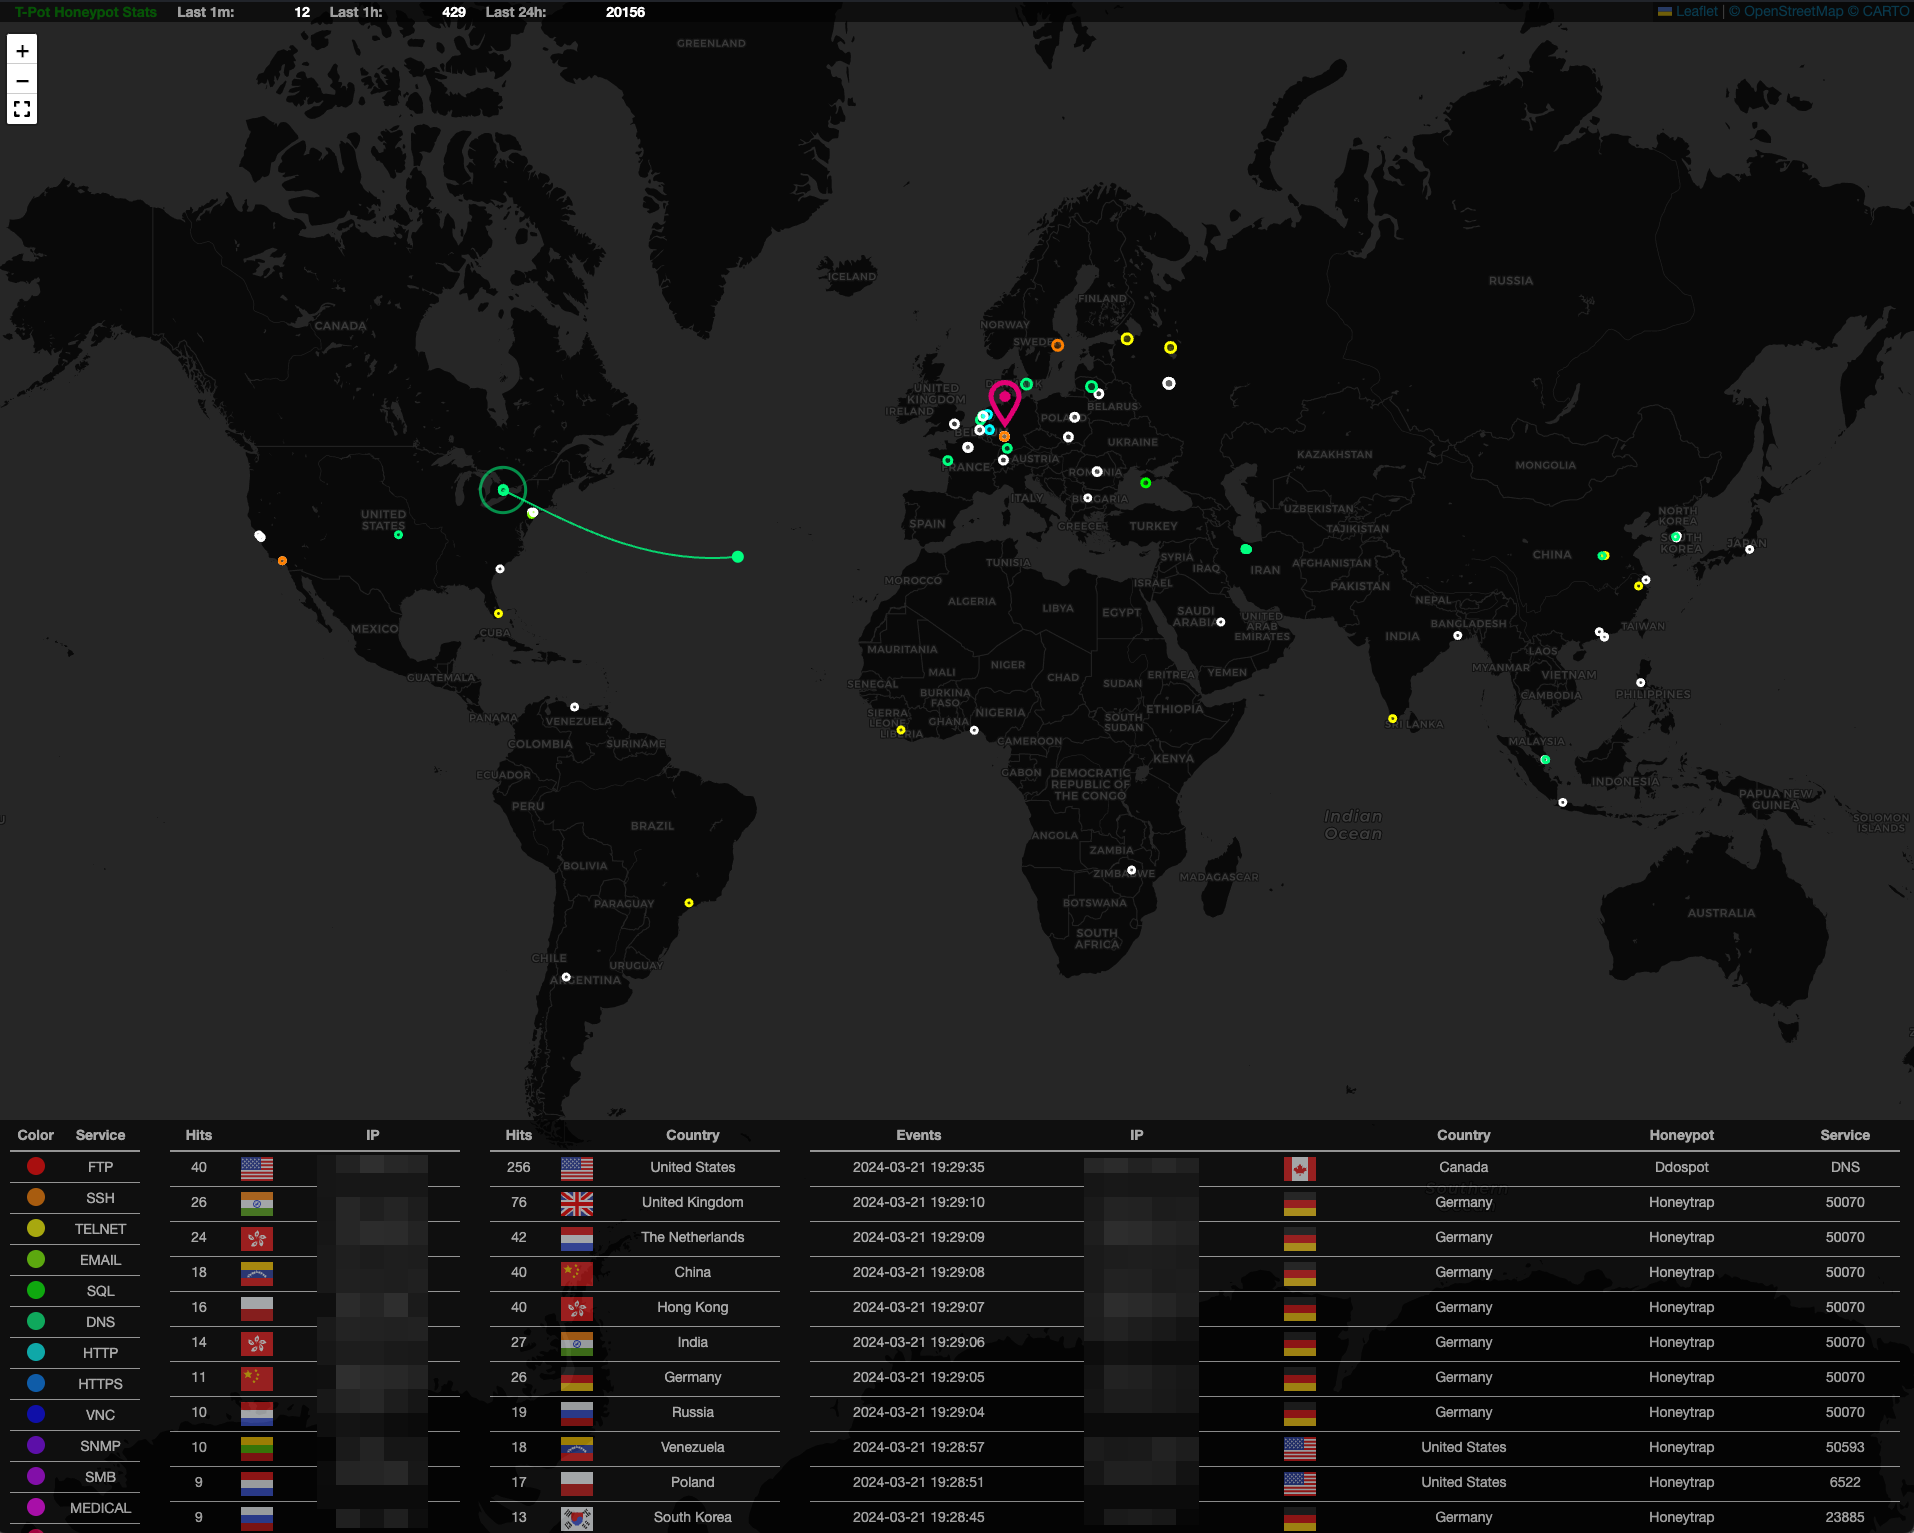
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝

Web-based Traffic and Cybersecurity Network Traffic Monitoring

Automate the creation of a lab environment complete with security tooling and logging best practices

Curated list of threat detection and hunting resources: detection rules, SIEM and log analysis tools, endpoint/network monitoring, datasets,…

Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support


A repository of sysmon configuration modules

Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…