

AIOstack
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
ai-securitycloud-securitycontainer-security+8
62
aurva-io/aiostackAI runtime inventory: discover shadow AI, trace LLM calls
 corelight/ecs-mapping
Mapping Corelight or Zeek data to Elastic Common Schema fields
 kjean13/adft
Active Directory Forensic Toolkit : Detect & reconstruct AD attacks from Windows event logs (EVTX)
 corelight/zeek-community-id
Zeek support for Community ID flow hashing.
 goatmilkkk/tinyprocessor
A post-processing script for TinyTracer
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
 d3sre/intelligentprocesslifecycle
The Intelligent Process Lifecycle of Active Cyber Defenders
 corelight/log-add-http-post-bodies
Add POST body excerpt to Bro's HTTP log
 nccgroup/windowsmempagedelta
A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
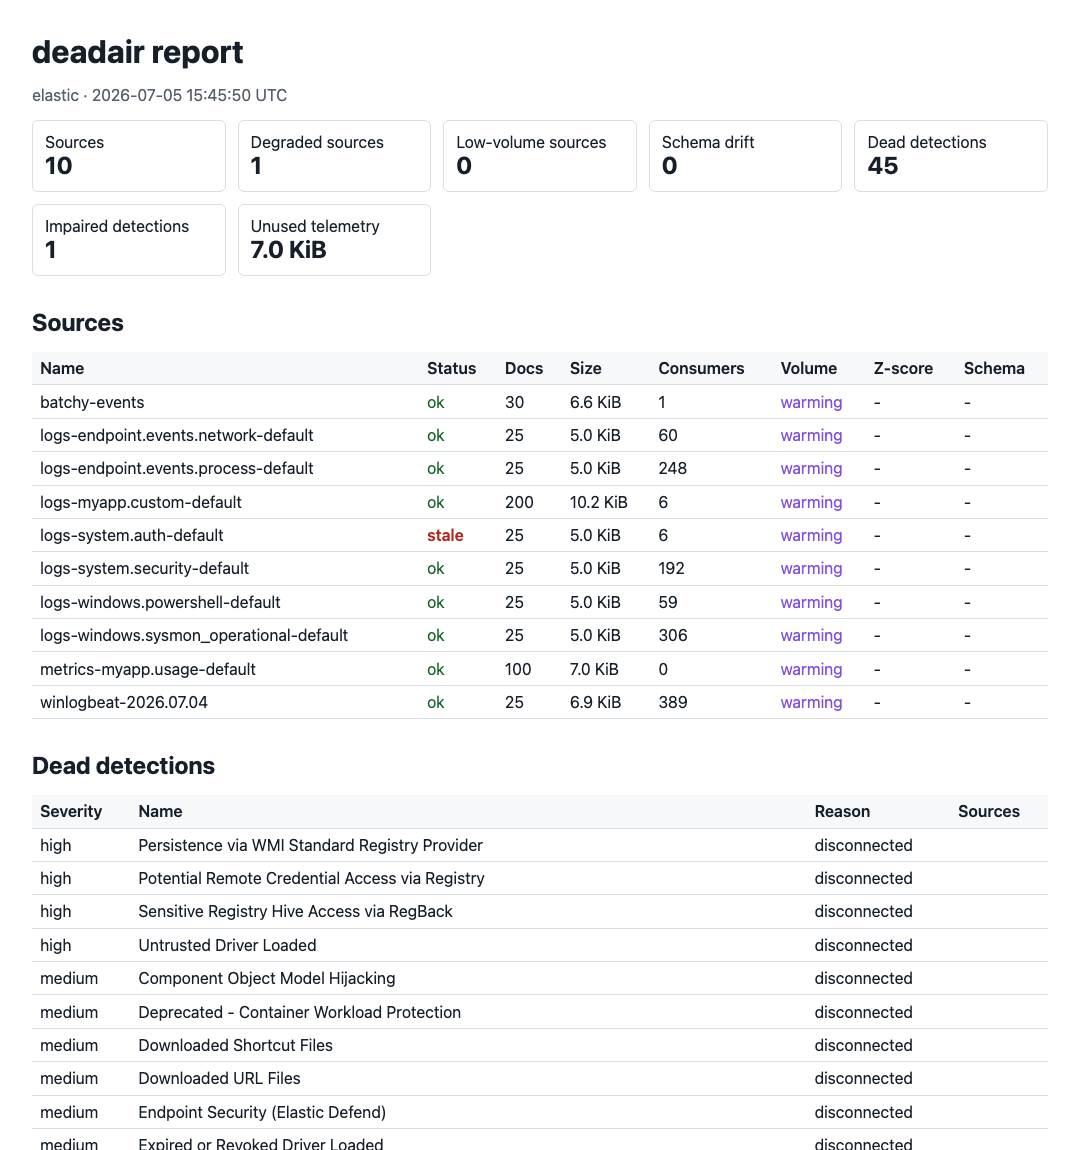 big-comfy/deadair
Finds the detection rules in your SIEM that are running blind
 knqyf263/ndff
A flow-based network monitor with Deep Packet Inspection
 0xmfbk/ebpf-container-escape-framework
Audit only eBPF EDR for Linux 5.15+ LTS: 14 kernel hooks, 15 actions (13 MITRE techniques), process lineage, SIEM export, K8s/Docker ready.
 darwinsec/defcon-kql-kung-fu-22
DEF CON Cloud Village workshop slides teaching KQL for cloud security log analysis, with practical exercises in a shared Azure Log Analytics…
 corelight/top-dns
Top DNS Measurement for Bro
 azeemering/cve-2021-44228-dfir-notes
CVE-2021-44228 DFIR Notes
 anasabugaddara-ux/defender-bluehammer-audit
Defensive Metasploit post module for CVE-2026-33825 (BlueHammer): Defender version/posture detection + compromise-hunt. Detection only.
 j-dahl7/mcp-attack-detection-sentinel
Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…
 cakescats/airborn-ios-cve-2025-24252
iOS Airborne vulnerabilities log artifact extractor from LogArchive CVE-2025-24252