
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
100 results
envocabulary preview

envocabulary

GitHubsreckoskocilic/envocabulary

Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
configuration-auditingdigital-forensicsforensics+3
3
9 days ago
cve-2025-24054-lab preview

cve-2025-24054-lab

GitHubt0tooro/cve-2025-24054-lab

Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
authenticationconfiguration-auditingeducation+7
2 months ago
CVE-2026-46331-pedit-COW-detection preview

CVE-2026-46331-pedit-COW-detection

GitHubg0thamrabb1t/cve-2026-46331-pedit-cow-detection

Defensive validation of CVE-2026-46331 / pedit COW with auditd, AppArmor, mitigation comparison and detection logic.
educationincident-responseintrusion-detection+3
2 months ago
MacOSThreatTrack preview

MacOSThreatTrack

GitHubab2pentest/macosthreattrack

Bash tool used for proactive detection of malicious activity on macOS systems.
digital-forensicsincident-responseinformation-gathering+1
3911 months ago
KQL-threat-hunting-queries preview

KQL-threat-hunting-queries

GitHubcyb3rmik3/kql-threat-hunting-queries

A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).

ctfcurated-resourceseducation+4
7973 months ago
key-transparency-auditor preview

key-transparency-auditor

GitHubsignalapp/key-transparency-auditor

Continuously fetches and cryptographically verifies key transparency log updates, maintains a condensed prefix and log tree view, and returns signed…
cryptographydefensive-toolslog-analysis
91 month ago
PacketPirate preview

PacketPirate

GitHubd0rb/packetpirate

A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
api-security-testingeducationinformation-gathering+6
9 months ago
ThreatHunting-Keywords preview

ThreatHunting-Keywords

GitHubmthcht/threathunting-keywords

Awesome list of keywords and artifacts for Threat Hunting sessions
curated-resourcesdefensive-toolsdigital-forensics+3
6731 year ago
ketshash preview

ketshash

GitHubcyberark/ketshash

A little tool for detecting suspicious privileged NTLM connections, in particular Pass-The-Hash attack, based on event viewer logs.

authenticationdefensive-toolsincident-response+3
1681 year ago
CVE-2022-29072 preview

CVE-2022-29072

GitHubsentinelblue/cve-2022-29072

** DISPUTED ** 7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the…
exploitationincident-responselog-analysis+3
84 years ago
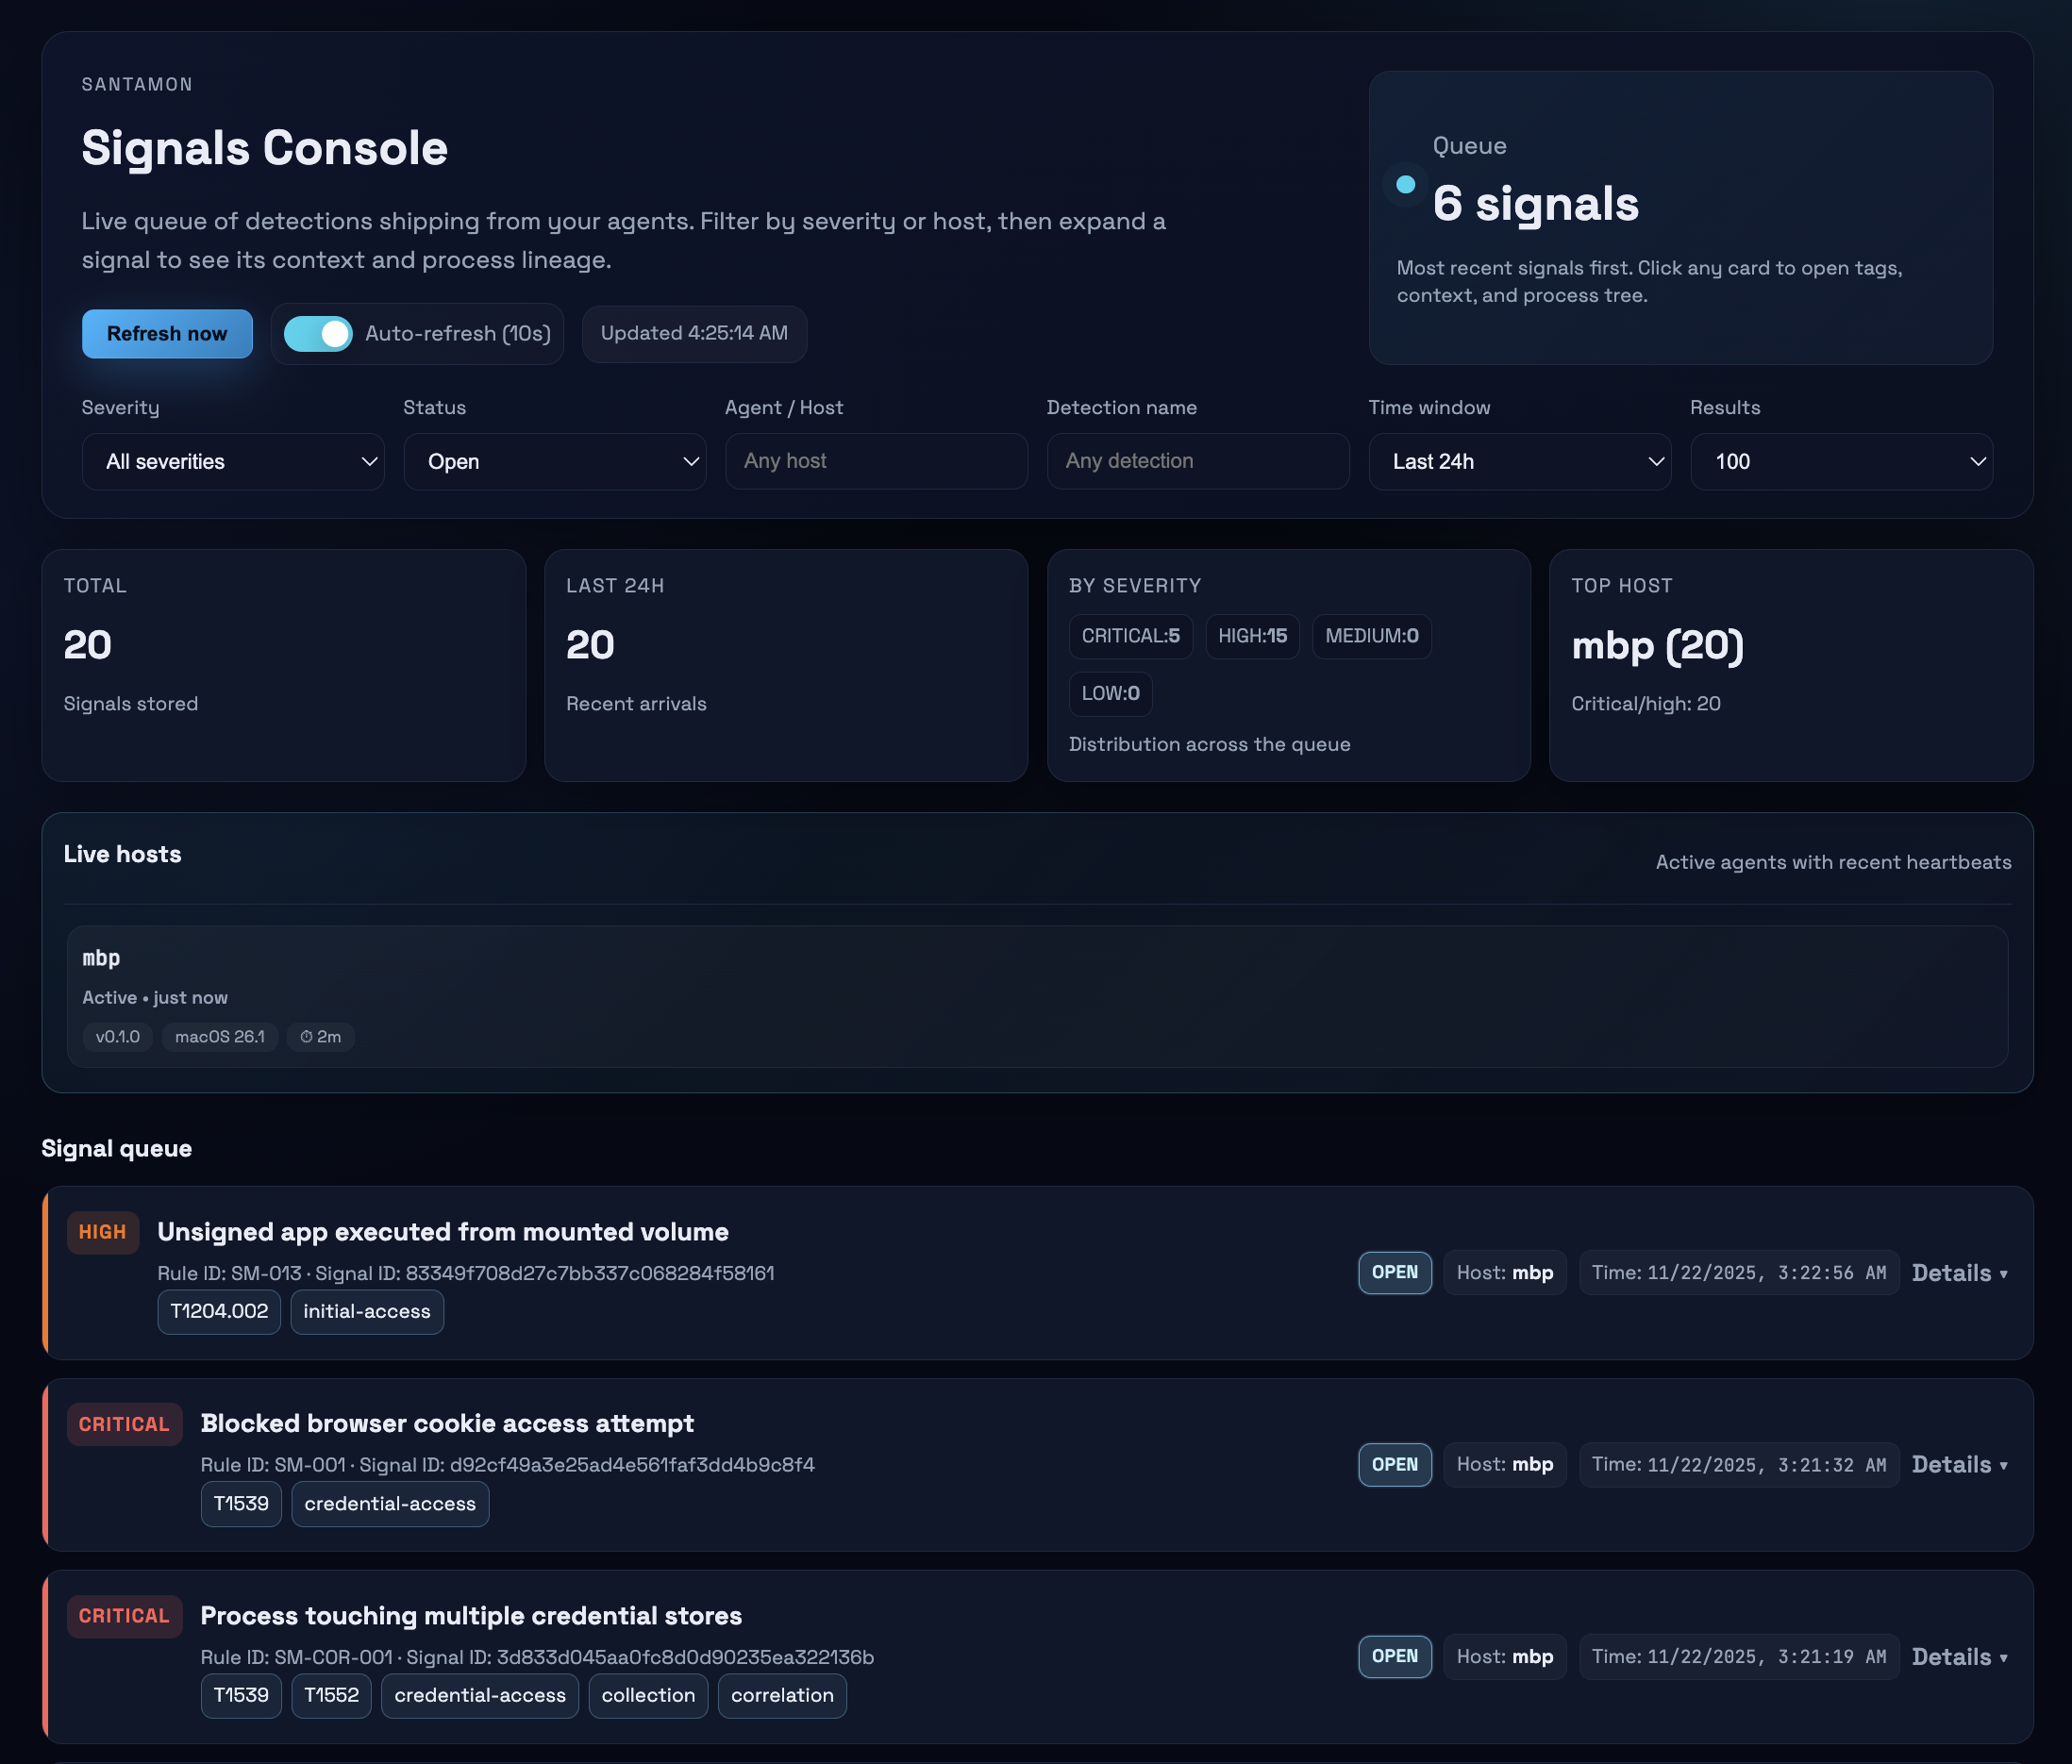
santamon preview

santamon

GitHub0x4d31/santamon

Lightweight macOS detection agent built on Santa’s Endpoint Security telemetry.

defensive-toolsincident-responseintrusion-detection+2
1159 months ago
proxynotshell-IOC-Checker preview

proxynotshell-IOC-Checker

GitHubrjsudlow/proxynotshell-ioc-checker

Script to check for IOC's created by ProxyNotShell (CVE-2022-41040 & CVE-2022-41082)
forensicsincident-responseioc-management+3
53 years ago
CVE-2019-19781-Forensic preview

CVE-2019-19781-Forensic

GitHubonsec-fr/cve-2019-19781-forensic

Automated forensic script hunting for cve-2019-19781
digital-forensicsforensicsincident-response+3
36 years ago
CVE-2007-2447-Exploitation-SIEM-Detection-Lab preview

CVE-2007-2447-Exploitation-SIEM-Detection-Lab

GitHubharshiys/cve-2007-2447-exploitation-siem-detection-lab

Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
educationexploitationexploit-frameworks+7
1 month ago
BaconSampler preview

BaconSampler

GitHublogisek/baconsampler

Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
dns-analysisforensicsinformation-gathering+6
208 months ago
exist preview
Archived

exist

GitHubnict-csl/exist

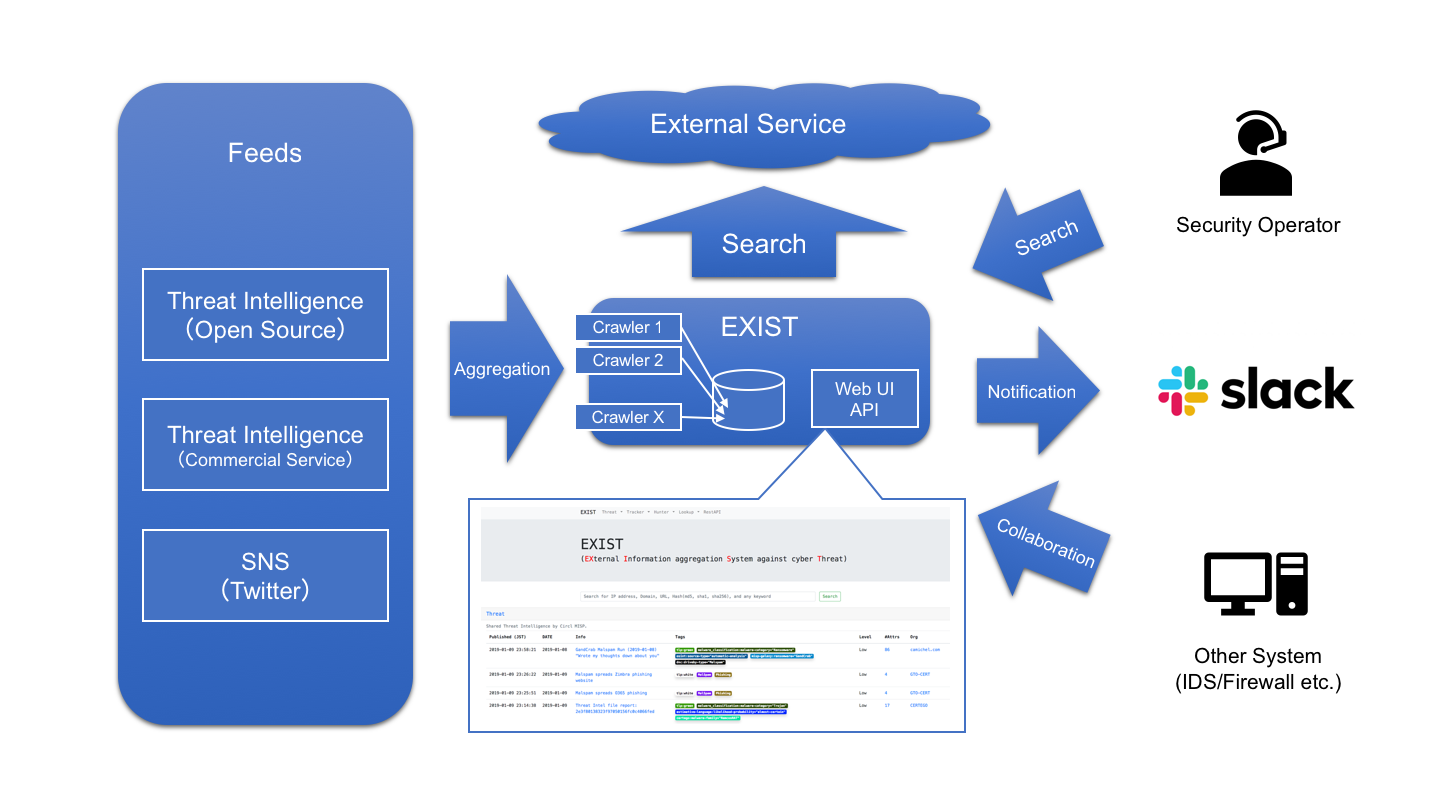
EXIST is a web application for aggregating and analyzing cyber threat intelligence.

educationincident-responseinformation-gathering+6
1526 months ago
sysmon-config preview

sysmon-config

GitHubion-storm/sysmon-config

Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…

anomaly-detectiondefensive-toolsdigital-forensics+5
8292 years ago
matano preview

matano

GitHubmatanolabs/matano

Open source security data lake for threat hunting, detection & response, and cybersecurity analytics at petabyte scale on AWS

cloud-securityincident-responselog-analysis+1
1.7k1 year ago
Previous123456Next