
Archived
WhoDat
 mitrecnd/whodat
Pivotable Reverse WhoIs / PDNS Fusion with Registrant Tracking & Alerting plus API for automated queries (JSON/CSV/TXT)
api-securitydata-exfiltrationdns-analysis+5
 nccgroup/mimikatz-detector-busylight
USB HID driver emulation with PID/VID (0x3bca/0x27bb) of Plenom A/S Busylight Alpha, that is supported by Mimikatz. When mimikatz is executed, a…
 alexpena5635/cve-2021-44228_scanner-main-modified-
Scans jar, war, and ear files for the presence of JndiLookup.class to detect applications vulnerable to CVE-2021-44228 (Log4Shell).
 0x0v1/audix
Audix is a PowerShell tool to quickly configure the Windows Event Audit Policies for security monitoring
 fireeye/cve-2021-44228
OpenIOC rules to facilitate hunting for indicators of compromise
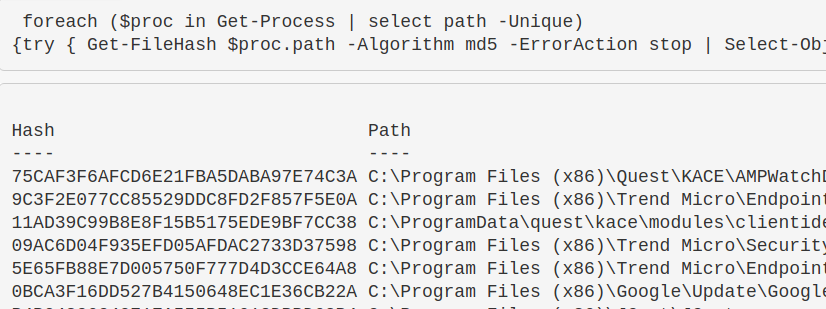 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 scarredmonk/sysmonsimulator
Sysmon event simulation utility which can be used to simulate the attacks to generate the Sysmon Event logs for testing the EDR detections and…
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
 neo23x0/auditd
Best Practice Auditd Configuration
 withsecurelabs/linuxcatscale
Incident Response collection and processing scripts with automated reporting scripts
 safelineman/agentic-soc-simulation
AI 驱动的 SOC 仿真平台
 embee-research/sigma
A repository to release detection rules to the public
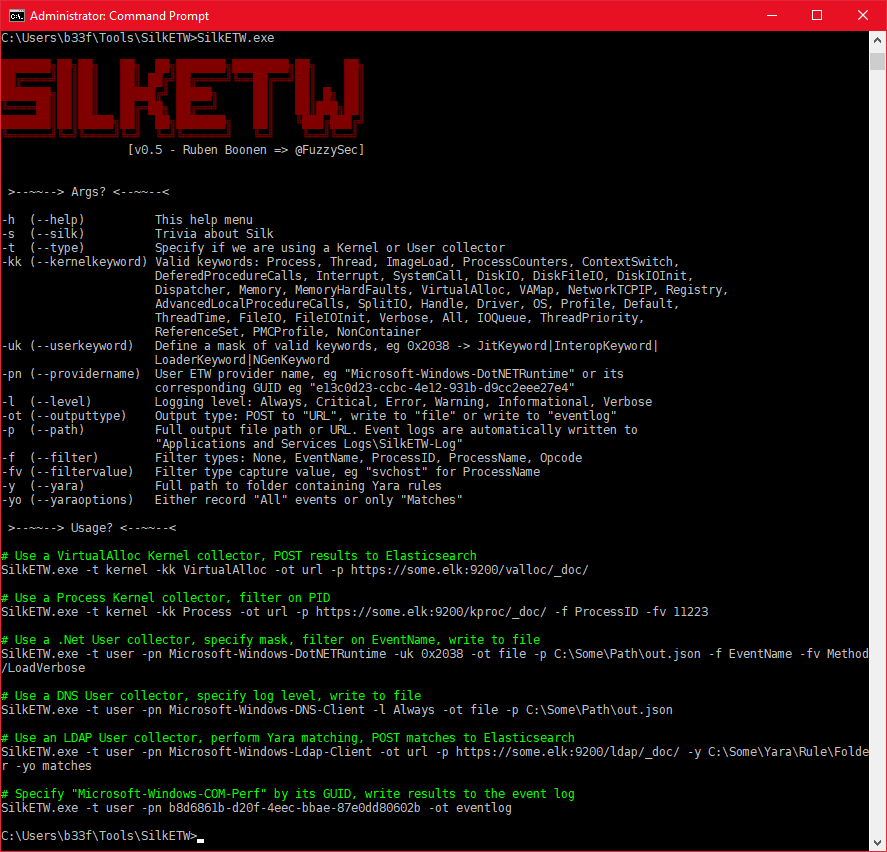 mandiant/silketw
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…
 hybridbrothers/hunting-queries-detection-rules
The purpose of this repository is to share KQL queries to help identify security misconfigurations, hunt for specific patterns, or detect malicious…
 tsale/edr-telemetry
This project aims to compare and evaluate the telemetry of various EDR products.
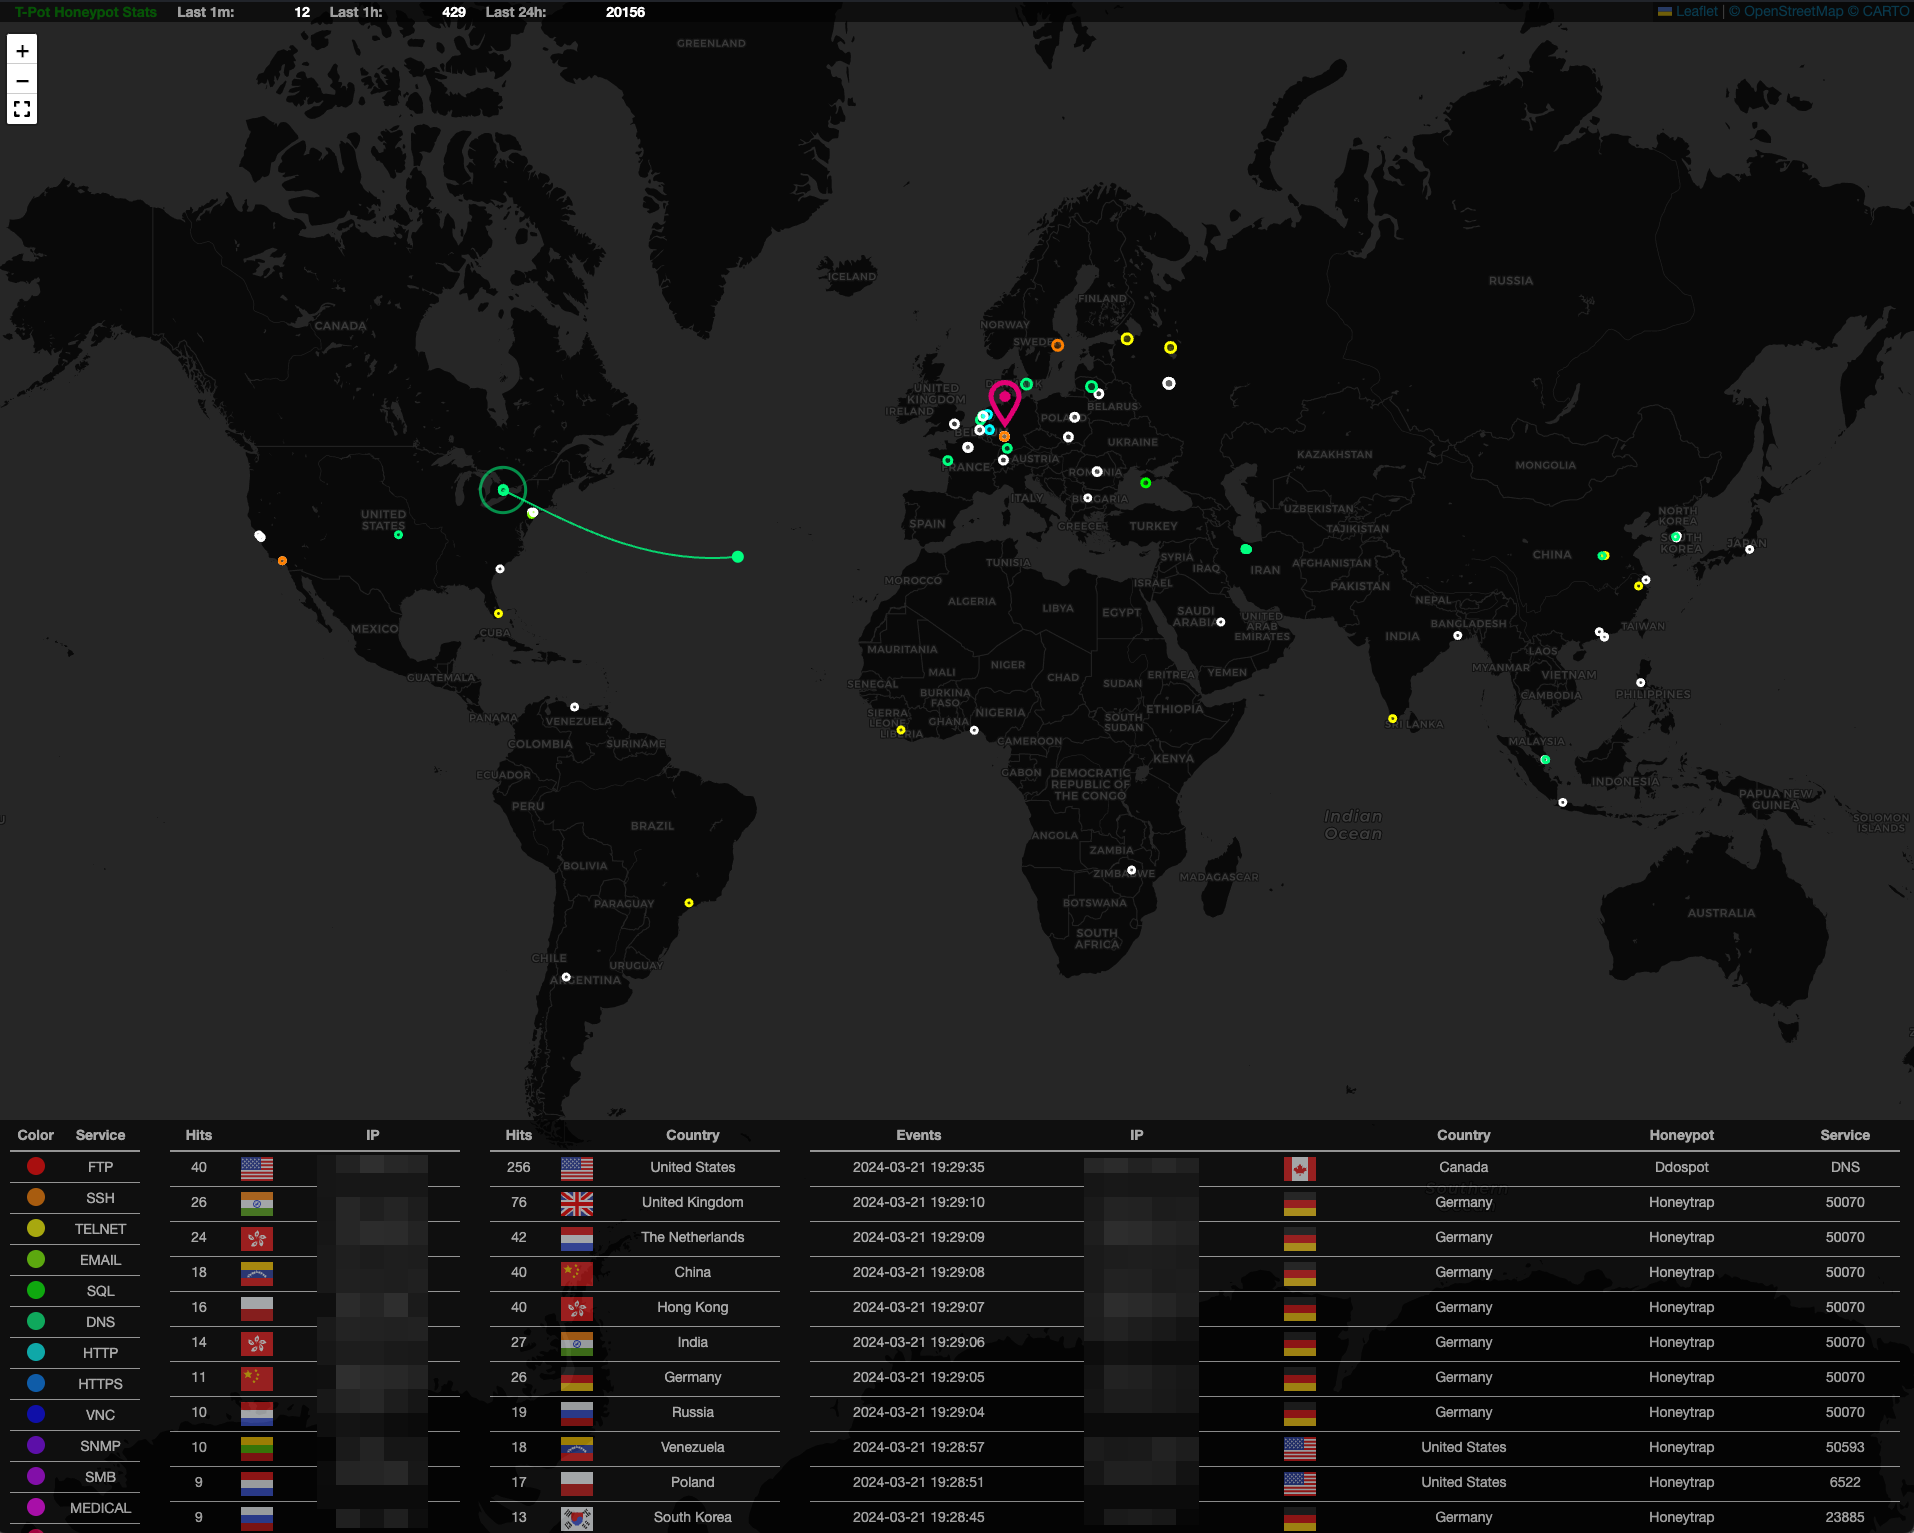 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 securityjoes/masterparser
MasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…