
ssh-enum
 alisha-chaudhary/ssh-enum
This project explores whether modern OpenSSH reveals valid usernames through subtle response or timing differences. CVE-2016-6210 user enumeration…
educationinformation-gatheringlog-analysis+4
alisha-chaudhary/ssh-enumThis project explores whether modern OpenSSH reveals valid usernames through subtle response or timing differences. CVE-2016-6210 user enumeration…
 freeguy-6/dmz-security-monitoring-hardening
CY376 Blue Team project — pfSense DMZ, Suricata IDS/IPS, and automated host hardening against CVE-2014-6271
 rohitmalik7/cve-2024-38063-detection-mitigation-system
End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…
 karmanyat28/multi-stage-exploitation-and-detection-engineering-analysis-of-cve-2023-34362-in-moveit-transfer
This repository contains an academic and technical analysis of CVE-2023-34362, a critical SQL injection vulnerability affecting the MOVEit Transfer…
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 the-dfir-report/sigma-rules
Rules generated from our investigations.
 jonny-jhnson/telemetrysource
Reference mapping Windows telemetry events—Sysmon, Security Auditing, and Threat Intelligence ETW—to underlying API functions, helping defenders…
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 cyberark/skywrapper
SkyWrapper helps to discover suspicious creation forms and uses of temporary tokens in AWS
 safelineman/agentic-soc-simulation
AI 驱动的 SOC 仿真平台
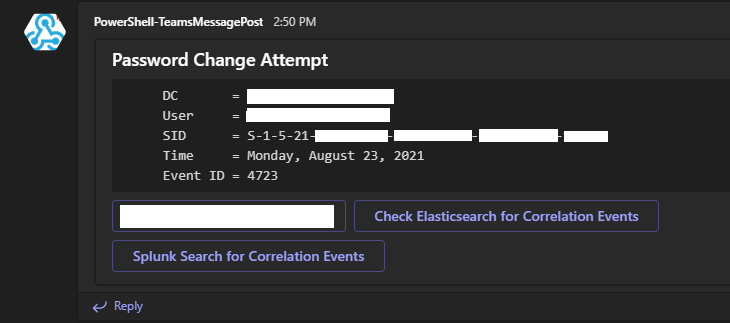 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
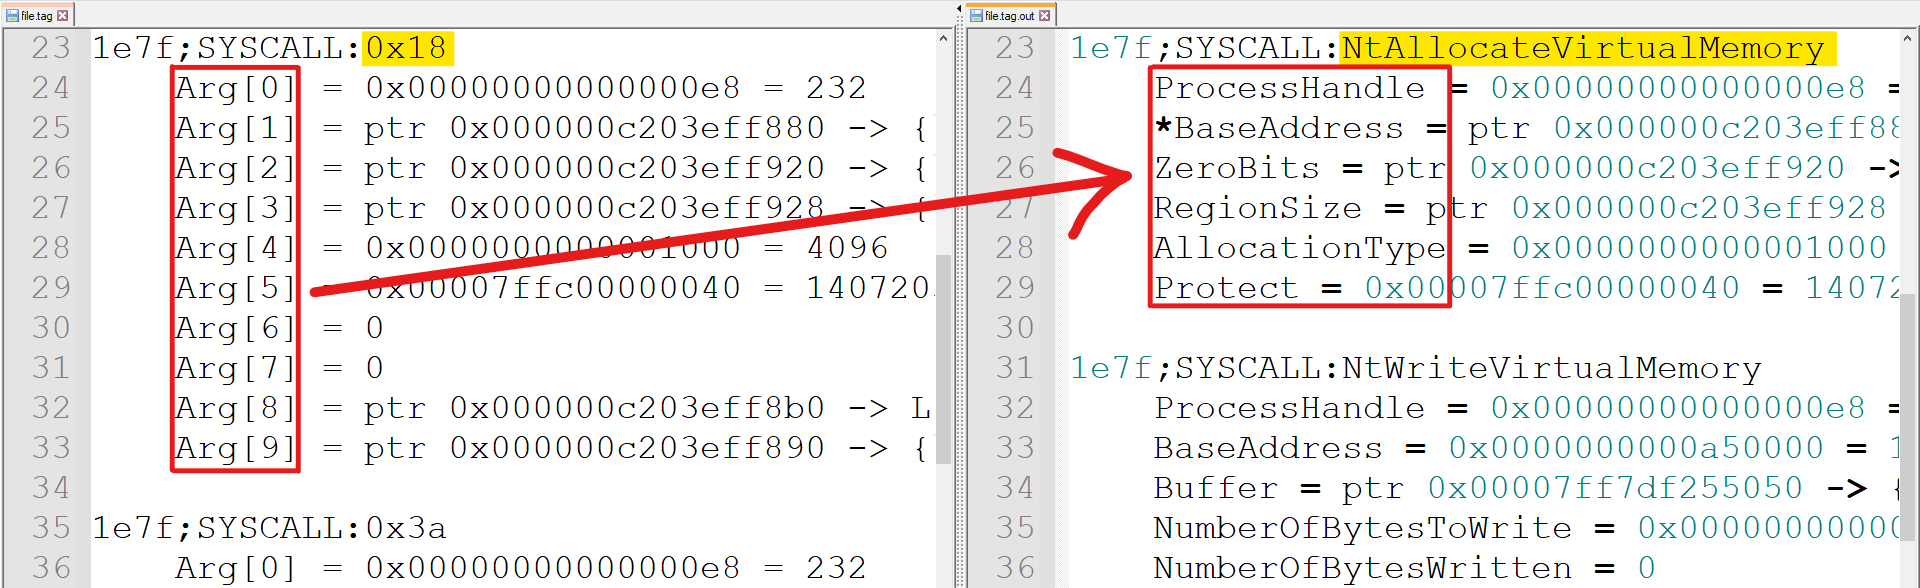 goatmilkkk/tinyprocessor
A post-processing script for TinyTracer
 ny1024/clawguard
Modular security toolkit for autonomous agents providing static analysis, configuration auditing, runtime monitoring, and supply chain verification…
 lucadibello/network-attack-detection
Advanced detection of port scanning, DoS and malware attacks using Machine Learning techniques
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.

 chrisandoryan/nethive-project
Restructured and Collaborated SIEM and CVSS Infrastructure. Presented at Blackhat Asia Arsenal 2020.
 lightless-labs/third-thoughts
Research toolkit for analyzing AI agent behavioral patterns through multi-disciplinary corpus analysis. Parses session logs, runs 23 analytical…