
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
99 results
Loki-RS preview

Loki-RS

GitHubneo23x0/loki-rs

🐍 High-performance, multi-threaded YARA & IOC scanner
digital-forensicsforensicsincident-response+7
3631 month ago
Winshark preview

Winshark

GitHubairbus-cert/winshark

A wireshark plugin to instrument ETW
forensicslog-analysisnetwork-security+1
5944 years ago
psad preview

psad

GitHubmrash/psad

psad: Intrusion Detection and Log Analysis with iptables
forensicsids-ips-evasionintrusion-detection+4
4387 years ago
SecurityClaw preview

SecurityClaw

GitHubsecurityclaw/securityclaw

A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
ai-securityanomaly-detectionforensics+8
2783 months ago
ALFA preview

ALFA

GitHubinvictus-ir/alfa

Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…
cloud-securitydigital-forensicsforensics+3
1872 months ago
etl-parser preview

etl-parser

GitHubairbus-cert/etl-parser

Event Trace Log file parser in pure Python
digital-forensicsforensicslog-analysis+1
1591 day ago
DFIR-O365RC preview

DFIR-O365RC

GitHubanssi-fr/dfir-o365rc

PowerShell module for Office 365 and Azure log collection
cloud-securitydigital-forensicsforensics+2
2841 year ago
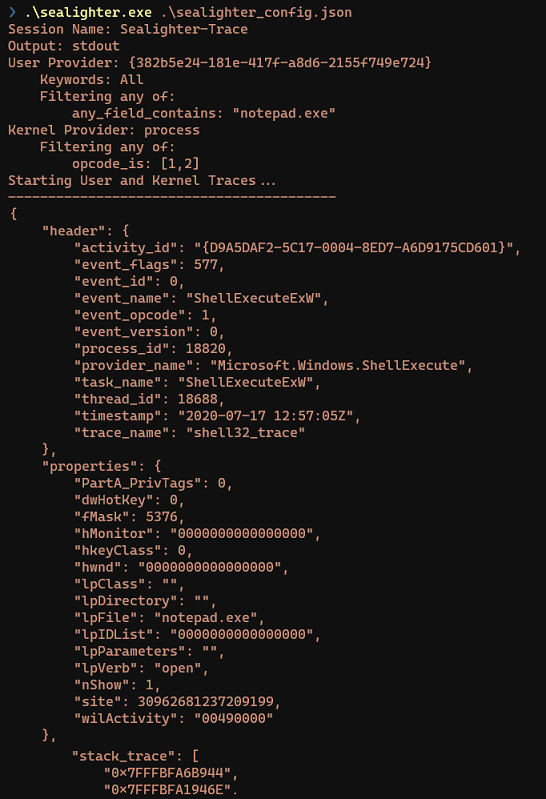
Sealighter preview

Sealighter

GitHubpathtofile/sealighter

ETW and WPP tracing tool for security research. Subscribes to multiple providers, auto-parses events to JSON, and supports advanced filtering,…
forensicslog-analysis
3973 years ago
LinuxCatScale preview

LinuxCatScale

GitHubwithsecurelabs/linuxcatscale

Incident Response collection and processing scripts with automated reporting scripts
digital-forensicsforensicsincident-response+2
3392 years ago
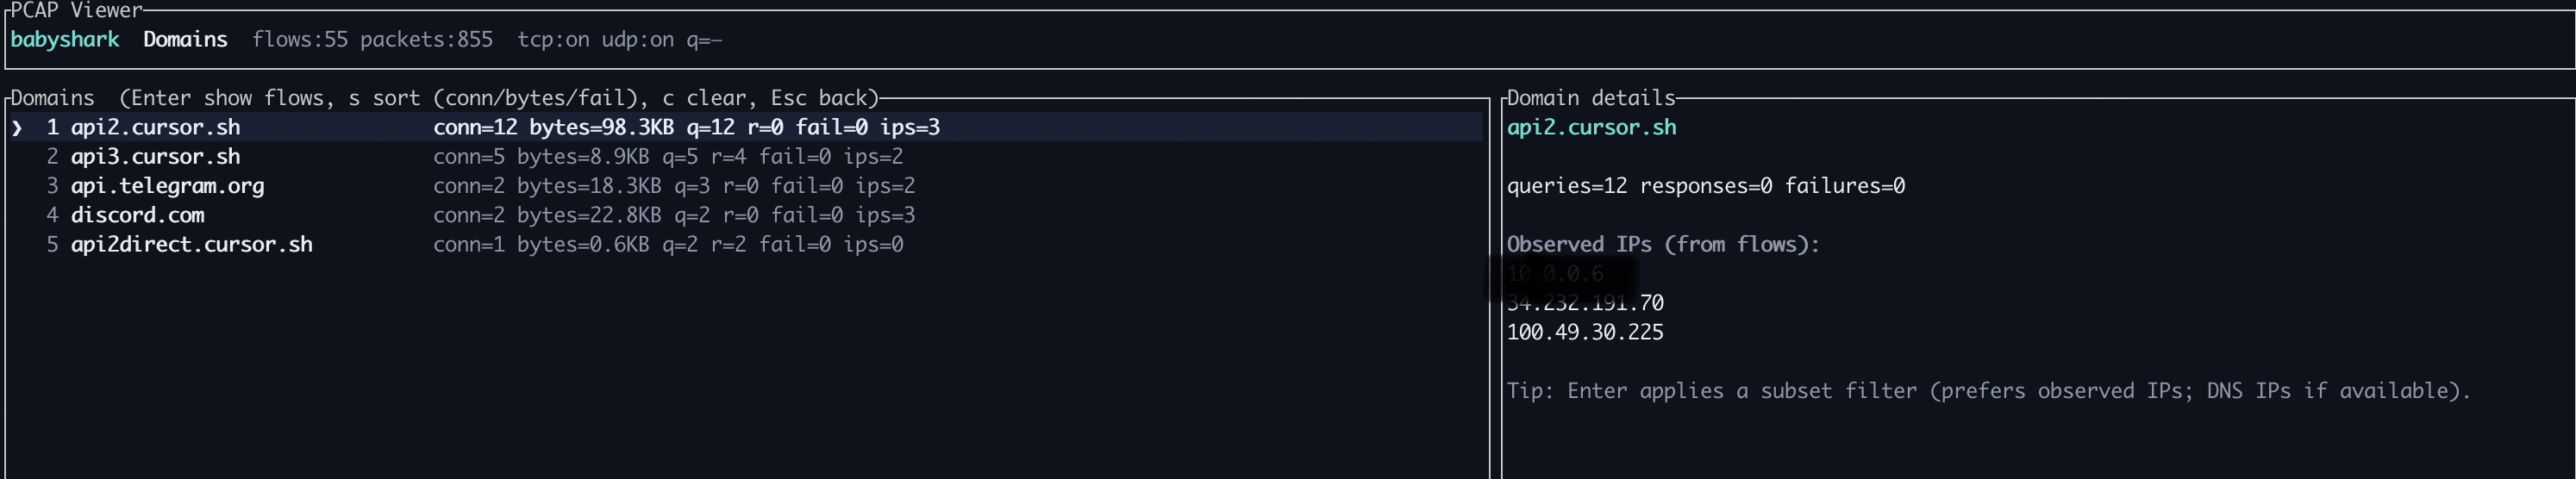
babyshark preview

babyshark

GitHubvignesh07/babyshark

Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
anomaly-detectiondns-analysisforensics+5
5678 months ago
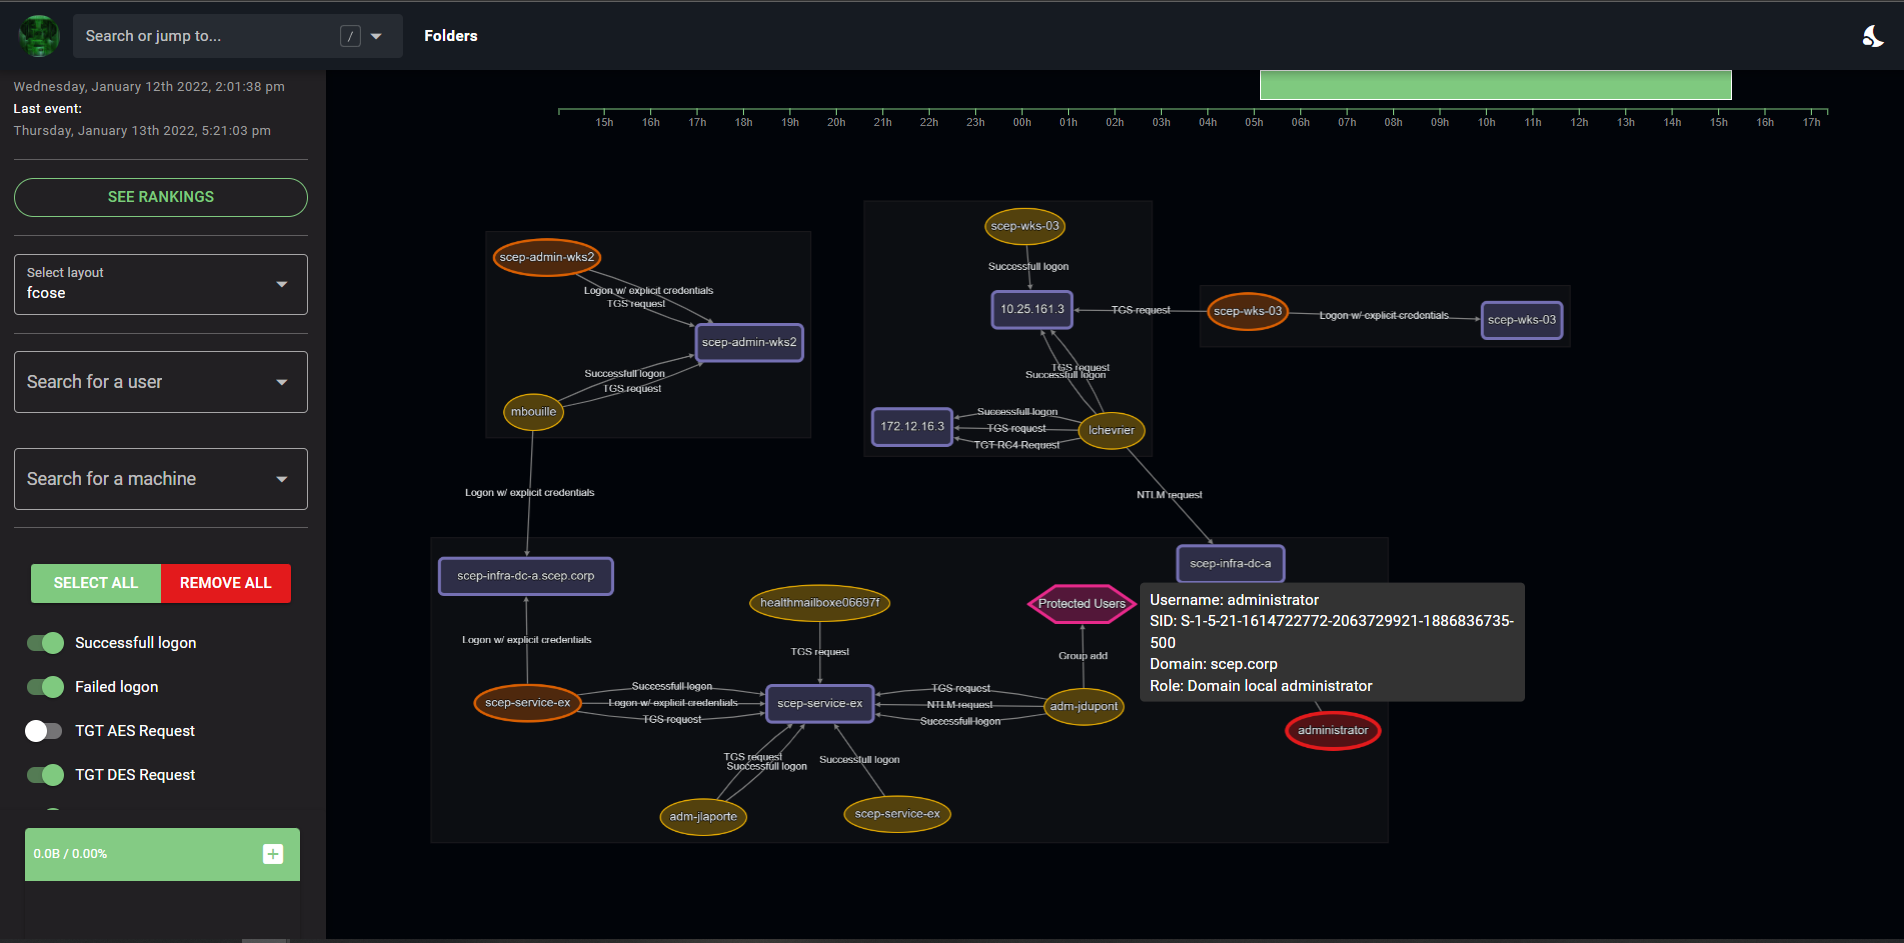
epagneul preview

epagneul

GitHubjurelou/epagneul

Graph Visualization for windows event logs

forensicslog-analysis
2541 year ago
MrHandler preview

MrHandler

GitHubemrekybs/mrhandler

SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…
digital-forensicsforensicsincident-response+1
867 months ago
Fennec preview

Fennec

GitHubabdulrhmanalfaifi/fennec

Artifact collection tool for *nix systems
digital-forensicsforensicsincident-response+3
2242 years ago
ADTrapper preview

ADTrapper

GitHubmhaggis/adtrapper

Hunt Smarter, Hunt Harder

anomaly-detectionauthenticationcloud-security+4
2017 months ago
packetsifterTool preview

packetsifterTool

GitHubpacketsifter/packetsiftertool

PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
defensive-toolsdigital-forensicsforensics+5
935 years ago
intelligence preview

intelligence

GitHubctrlaltint3l/intelligence

Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
forensicsinformation-gatheringioc-management+3
571 month ago
z9 preview

z9

GitHubsh1n0g1/z9

Detects PowerShell-based malware artifacts from event logs and performs static analysis on PowerShell scripts to identify malicious activity.

forensicslog-analysismalware-analysis+2
683 years ago
Kage-DFIR-toolkit preview

Kage-DFIR-toolkit

GitHubkarim852/kage-dfir-toolkit

Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…

defensive-toolsdigital-forensicsforensics+8
3919 days ago
Previous123456Next