
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
215 results
rita preview

rita

GitHubactivecm/rita

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
anomaly-detectioncommand-and-controldns-analysis+4
619
4 months ago
cve-2022-22954 preview

cve-2022-22954

GitHubcorelight/cve-2022-22954

Zeek package that detects CVE-2022-22954 exploit attempts, logs exploit URIs and attacker response data to aid in incident response and network…
exploitationincident-responseintrusion-detection+3
12 years ago
CyberDefense-Lab preview

CyberDefense-Lab

GitHubumidguluzada/cyberdefense-lab

A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
educationids-ips-evasionintrusion-detection+5
52 months ago
cve-2024-36401-security-simulator preview

cve-2024-36401-security-simulator

GitHubraniaemran/cve-2024-36401-security-simulator

Educational Python simulator modeling a fictional security incident inspired by CVE-2024-36401 to demonstrate vulnerability management, segmentation,…
defensive-toolseducationincident-response+5
1 month ago
scripts preview

scripts

GitHubclausing/scripts

Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…

digital-forensicsforensicsincident-response+5
866 days ago
Log4j_Attacker_IPList preview

Log4j_Attacker_IPList

GitHubc3-h2/log4j_attacker_iplist

Curated list of attacker IP addresses targeting the Log4j vulnerability (CVE-2021-44228) for threat intelligence, incident response, and network…
information-gatheringioc-managementlog-analysis+2
4 years ago
EagleEye preview

EagleEye

GitHubd4vinci/eagleeye

A host-based IDS and network monitoring system (My graduation project)
anomaly-detectiondefensive-toolseducation+5
285 years ago
kestrel preview

kestrel

GitHub1-bit-wonder/kestrel

Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.
anomaly-detectiondefensive-toolsintrusion-detection+2
3 months ago
pastokrapacefleciks preview

pastokrapacefleciks

GitHubnu11secur1ty/pastokrapacefleciks

Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
digital-forensicsforensicslog-analysis+2
2 months ago
neko-master preview

neko-master

GitHubforu17/neko-master

A modern and elegant dashboard for network traffic visualization and analysis.
information-gatheringlog-analysisnetwork-mapping+3
4.2k23 days ago
Snitch preview

Snitch

GitHubaixisstudio/snitch

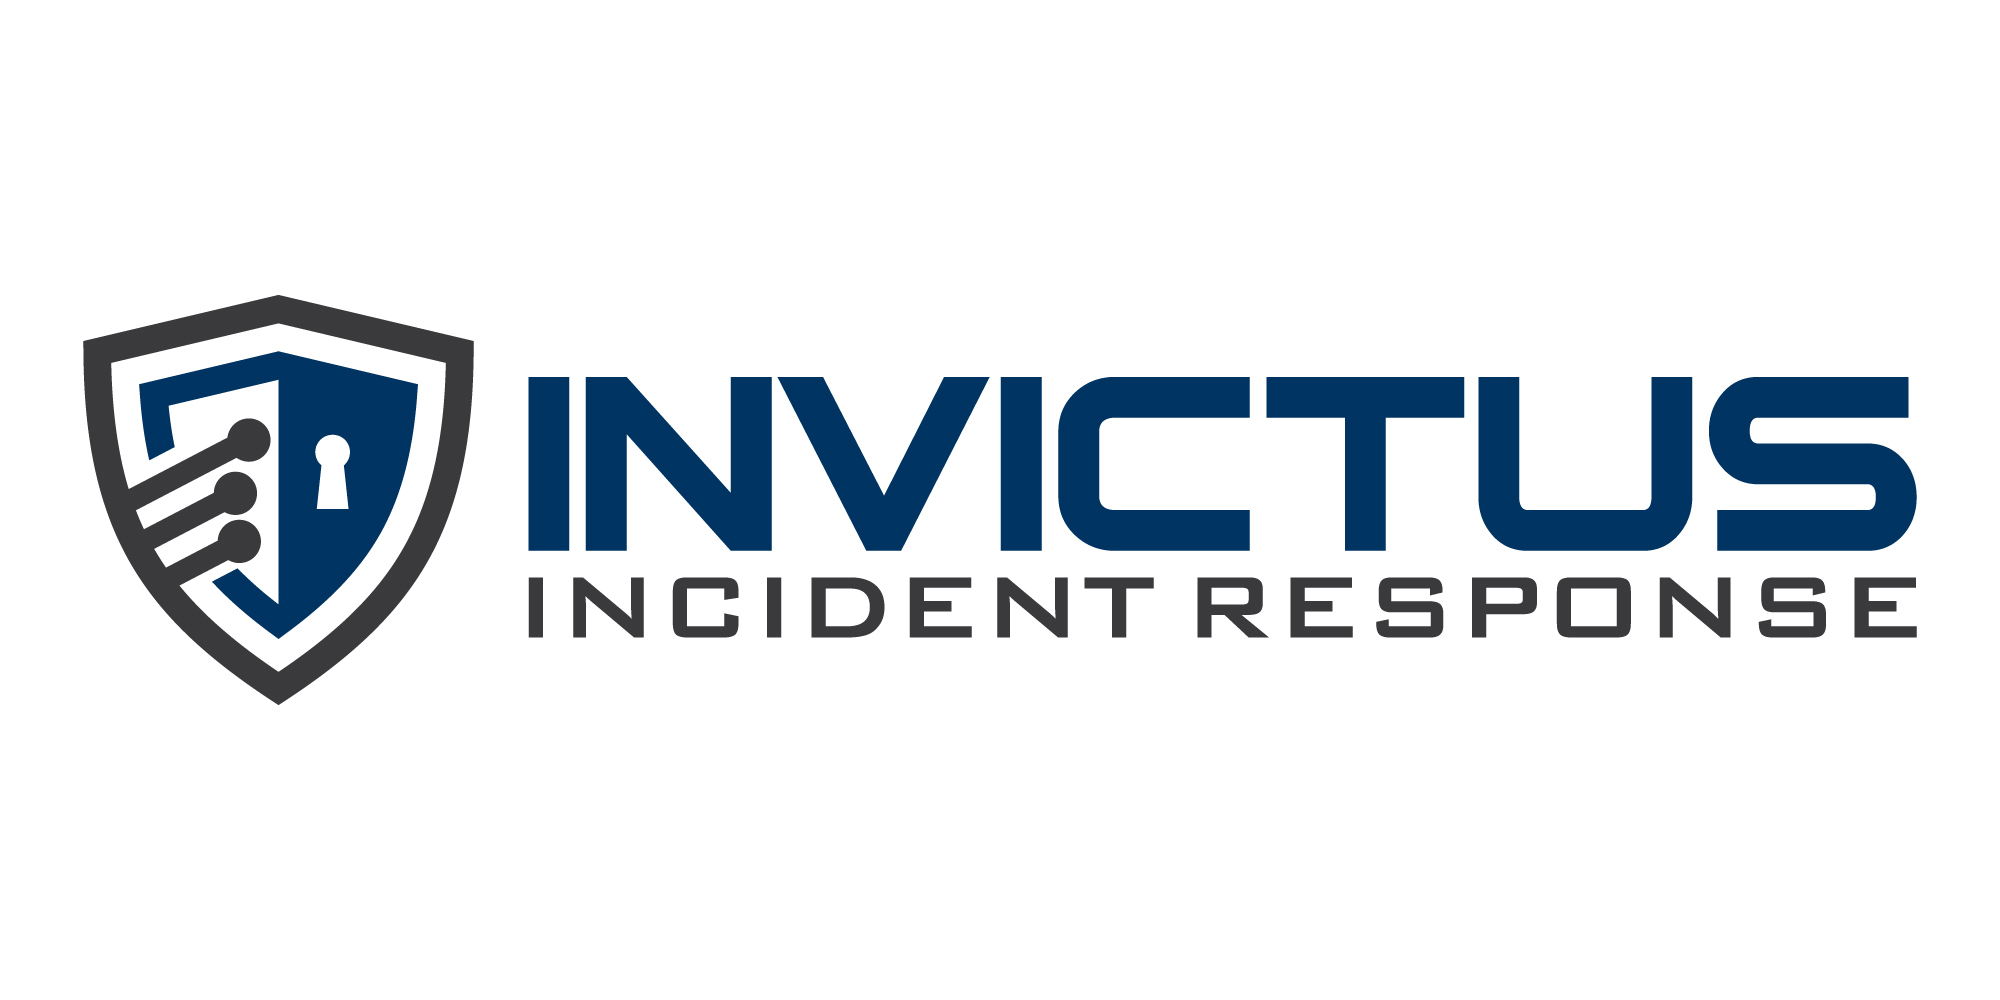
Real-time network monitor + outbound firewall — see & block every connection. Privacy-first, local-first, Rust fleet agent, SIEM exports, 8…
anomaly-detectiondefensive-toolsdns-analysis+6
6911 day ago
Microsoft-Extractor-Suite preview

Microsoft-Extractor-Suite

GitHubinvictus-ir/microsoft-extractor-suite

A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
cloud-securitydigital-forensicsincident-response+3
8374 months ago
Threat-Remediation-Scripts preview

Threat-Remediation-Scripts

GitHubxephora/threat-remediation-scripts

This repository contains a list of new remediation scripts.
defensive-toolsdigital-forensicsincident-response+5
19014 days ago
artillery preview

artillery

GitHubtrustedsec/artillery

Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
anomaly-detectiondefensive-toolshardware-iot-security+5
3386 years ago
meshyface preview

meshyface

GitHubjaronmcd/meshyface

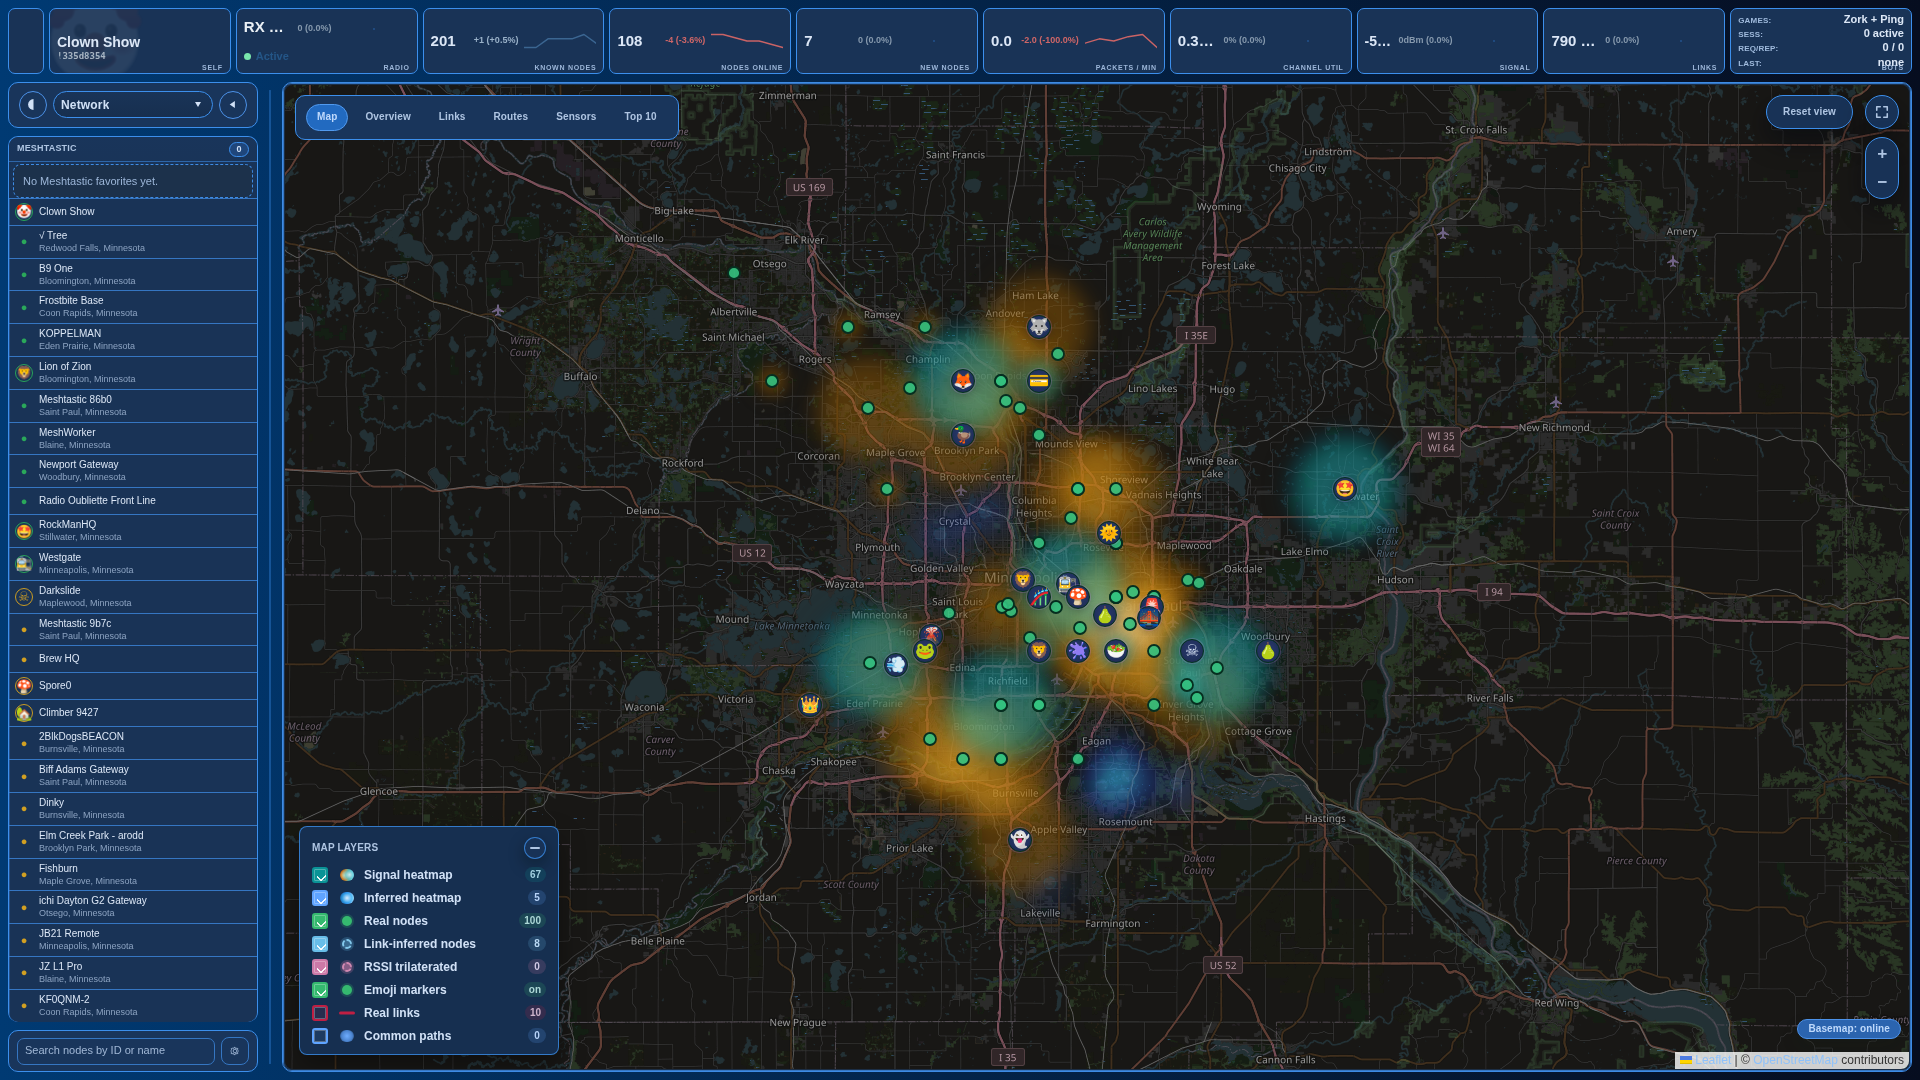
Single-page web dashboard for Meshtastic mesh networks with live network mapping, packet analysis, chat, sensor telemetry, and topology…
dns-analysisinformation-gatheringiot-security+4
1231 month ago
Sigma-Rules preview

Sigma-Rules

GitHubmbabinski/sigma-rules

A repository of my own Sigma detection rules.
defensive-toolsintrusion-detectionlog-analysis+1
16711 months ago
reportly preview

reportly

GitHubsap8899/reportly

AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
cloud-securityidentity-access-managementincident-response+2
963 years ago
netstat2neo4j preview

netstat2neo4j

GitHubtrinitor/netstat2neo4j

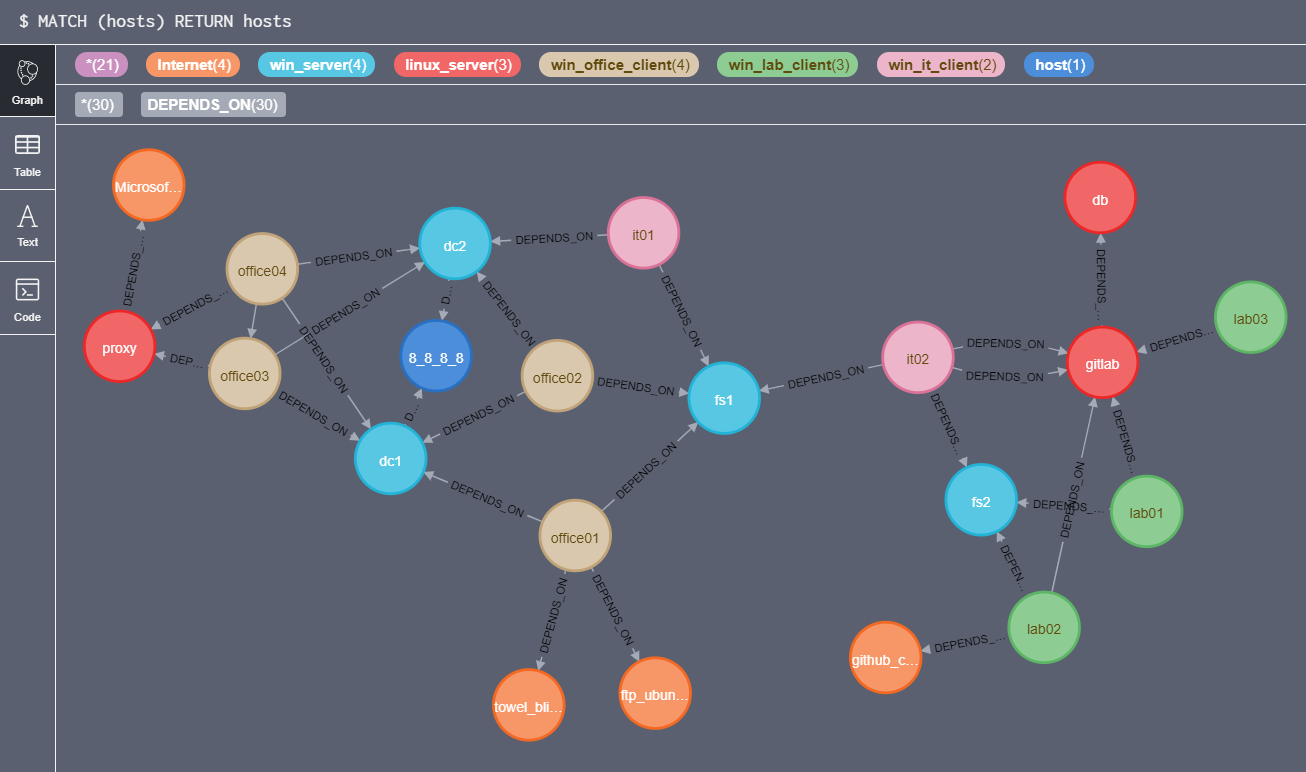
create cypher create statements for neo4j out of netstat files from multiple machines

information-gatheringlog-analysisnetwork-forensics
415 years ago
Previous123…12Next