Llama-Stack-0.4.0rc3-local-CVE-2026-25211

Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…

Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…

A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.

Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

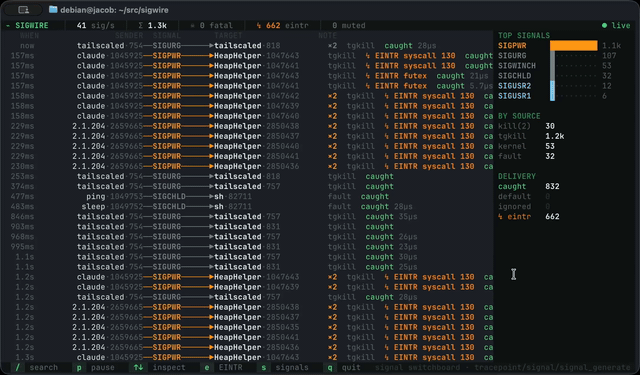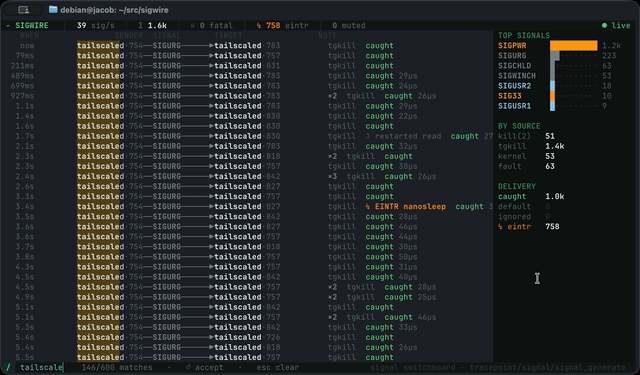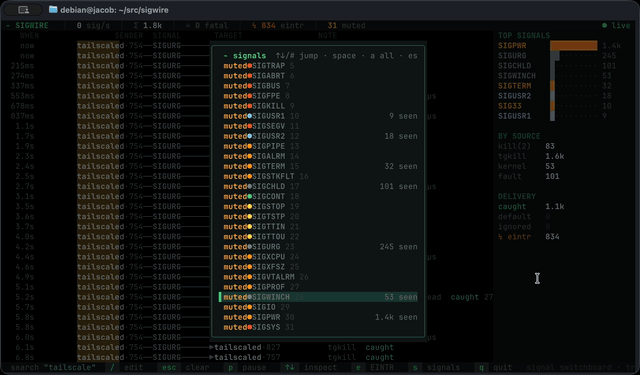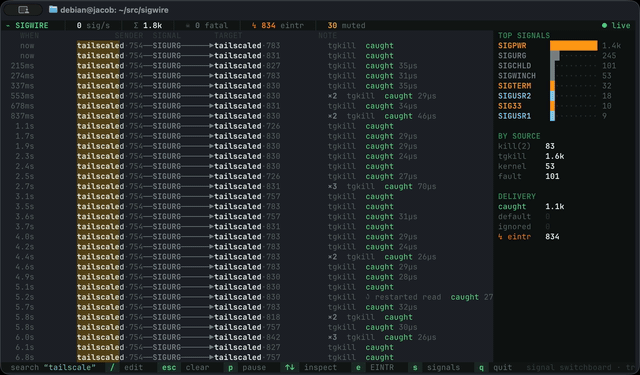
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…

Purpleteam scripts simulation & Detection - trigger events for SOC detections

GitHub mirror of the Linux Kernel's audit repository

Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.

Self-hosted multi-engine Sigma detection for event logs

Daemon to ban hosts that cause multiple authentication errors

A repository of sysmon configuration modules

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…

DECeption with Evaluative Integrated Validation Engine (DECEIVE): Let an LLM do all the hard honeypot work!

Hunt WiFi threats silently. Catch the hackers.