
QLOG
 threathunters-io/qlog
ETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…
defensive-toolsforensicsincident-response+1
44
threathunters-io/qlogETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 danielwep/cve-netscalerfilesystemcheck
This script checks the Citrix Netscaler if it has been compromised by CVE-2019-19781 attacks and collects all file system information
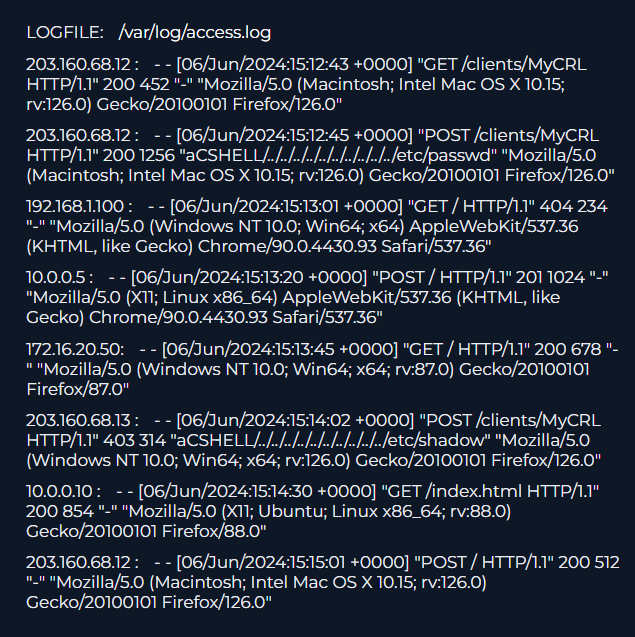 zedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
 karmanyat28/multi-stage-exploitation-and-detection-engineering-analysis-of-cve-2023-34362-in-moveit-transfer
This repository contains an academic and technical analysis of CVE-2023-34362, a critical SQL injection vulnerability affecting the MOVEit Transfer…
 randomrobbiebf/cve-2023-47529
Cloud Templates & Patterns collection <= 1.2.2 - Sensitive Information Exposure via Log File
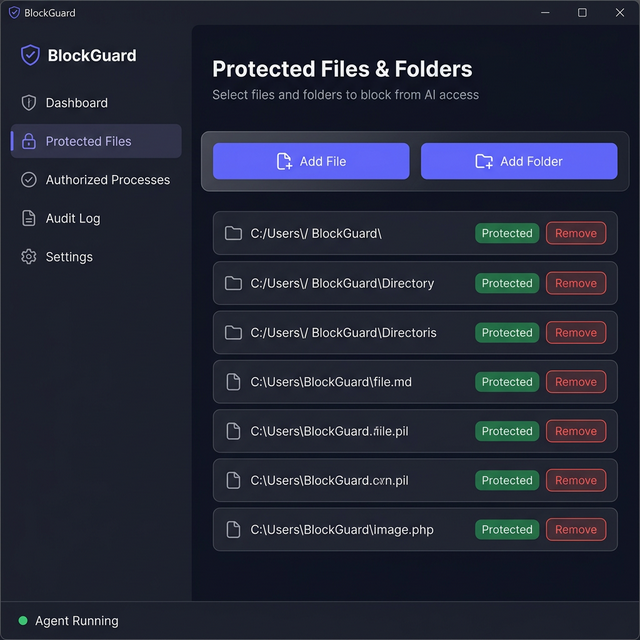 m2l33k/blockguard
BlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…
 cross-samuel1/soc-analyst-hub
Free, offline SOC Analyst Hub for Tier 1 — IR checklists, alert triage playbooks, threat hunting queries & analyst onboarding. Single HTML file, no…
 mrezqi/cve-2021-1675_carbonblack_huntingquery
CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.
 randomrobbiebf/cve-2023-47668
Restrict Content <= 3.2.7 - Information Exposure via legacy log file
 hubblestack/hubble
Hubble is a modular, open-source security compliance framework. The project provides on-demand profile-based auditing, real-time security event…
 fireeye/pywintrace
Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…
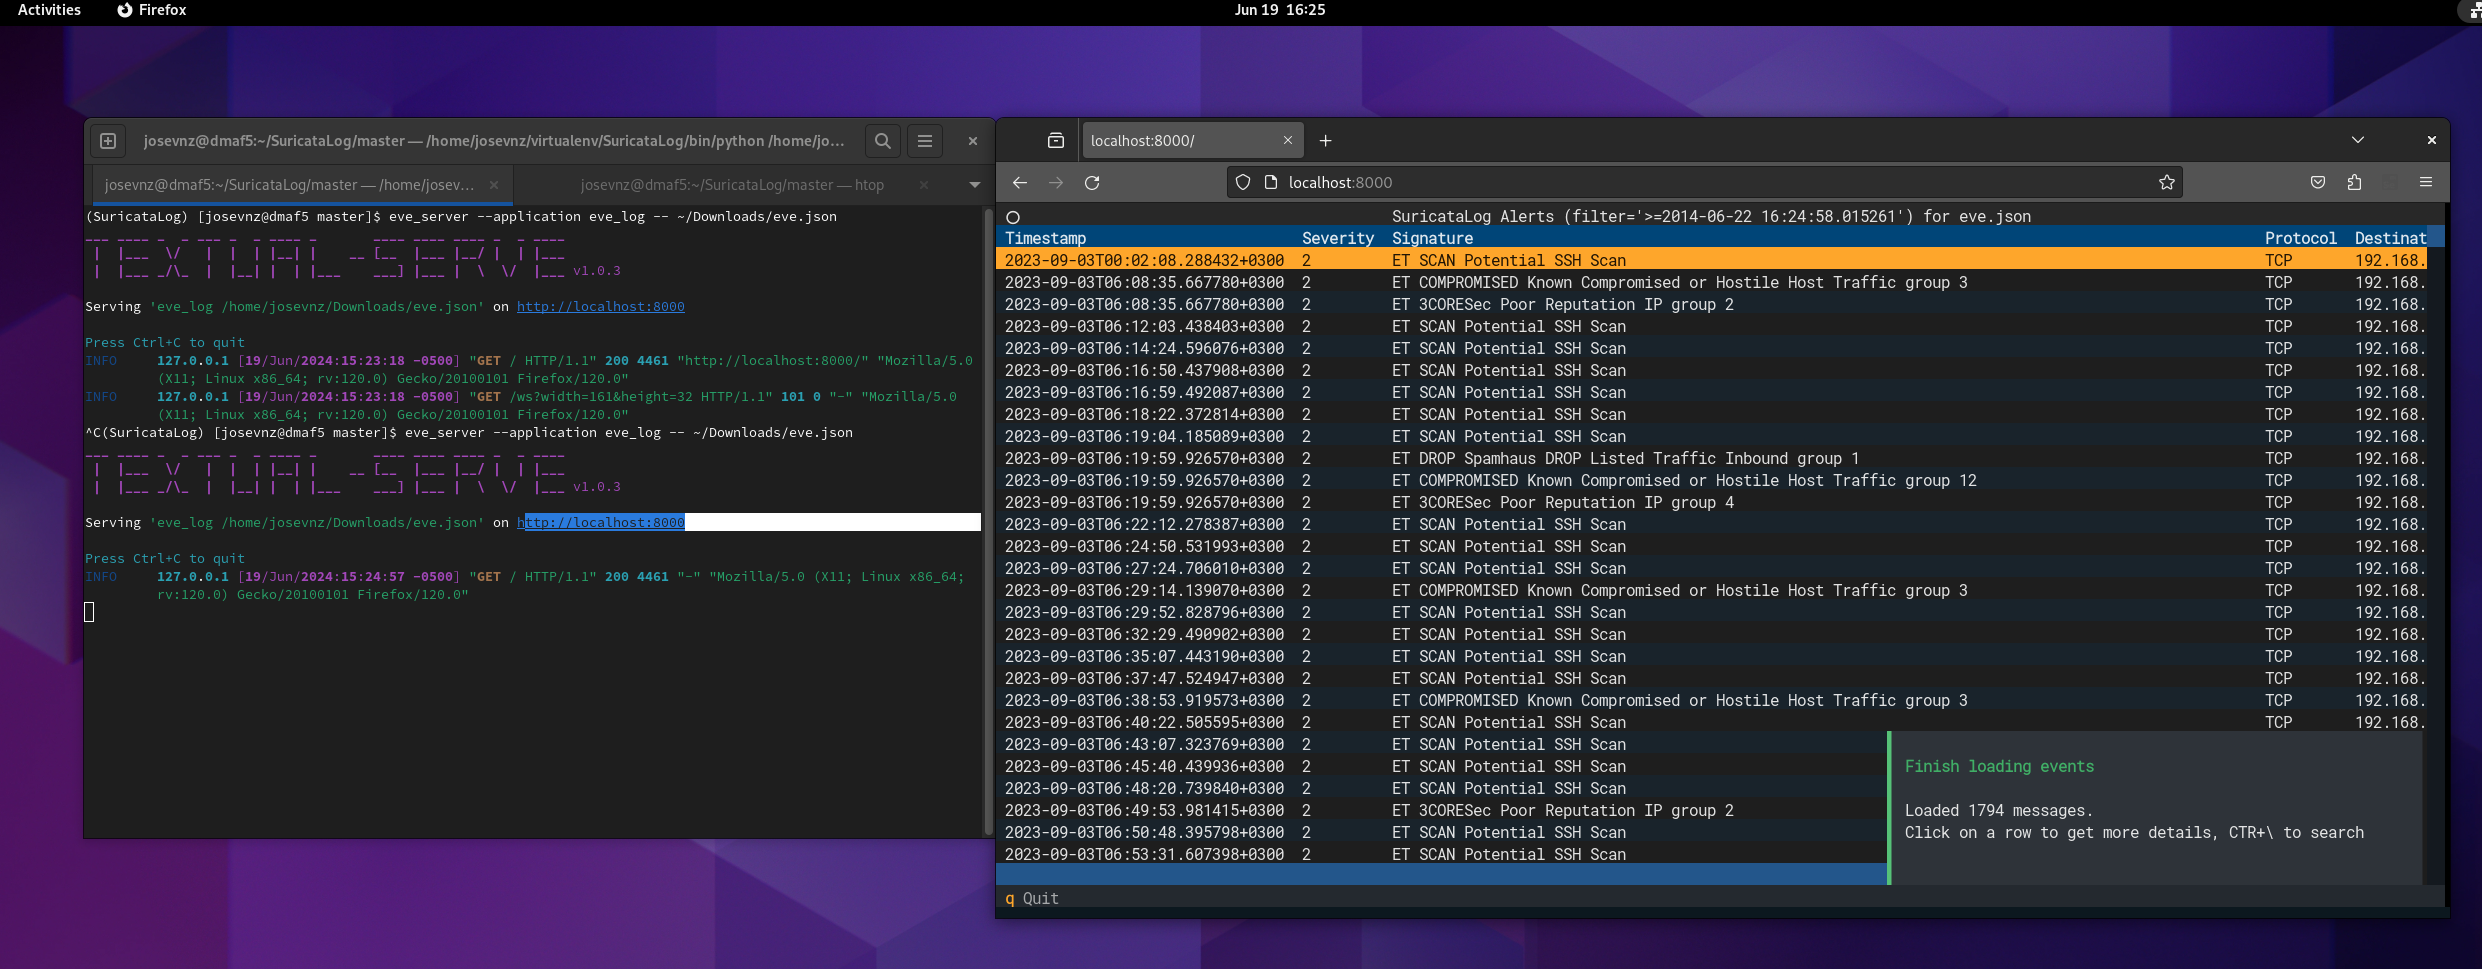 josevnz/suricatalog
Parse, filter, and visualize Suricata eve.json logs with CLI tools for alerts, flows, DNS, and payloads. Includes a tutorial for learning Suricata…
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
 k11h-de/bbot-ui
a terminal UI to browse bbot reports
 virologi-info/papercut-toolkit
#PaperCut CVE-2026-81578 + CVE-2026-82078 Defense Toolkit 2 3 A **defensive** toolkit to check and understand exposure to the chained
 corelight/extendintel
This package extends the Intel package to log more fields