

Archived
linux-explorer
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
digital-forensicsforensicsincident-response+7
404
intezer/linux-explorerEasy-to-use live forensics toolbox for Linux endpoints
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
 withsecurelabs/linuxcatscale
Incident Response collection and processing scripts with automated reporting scripts
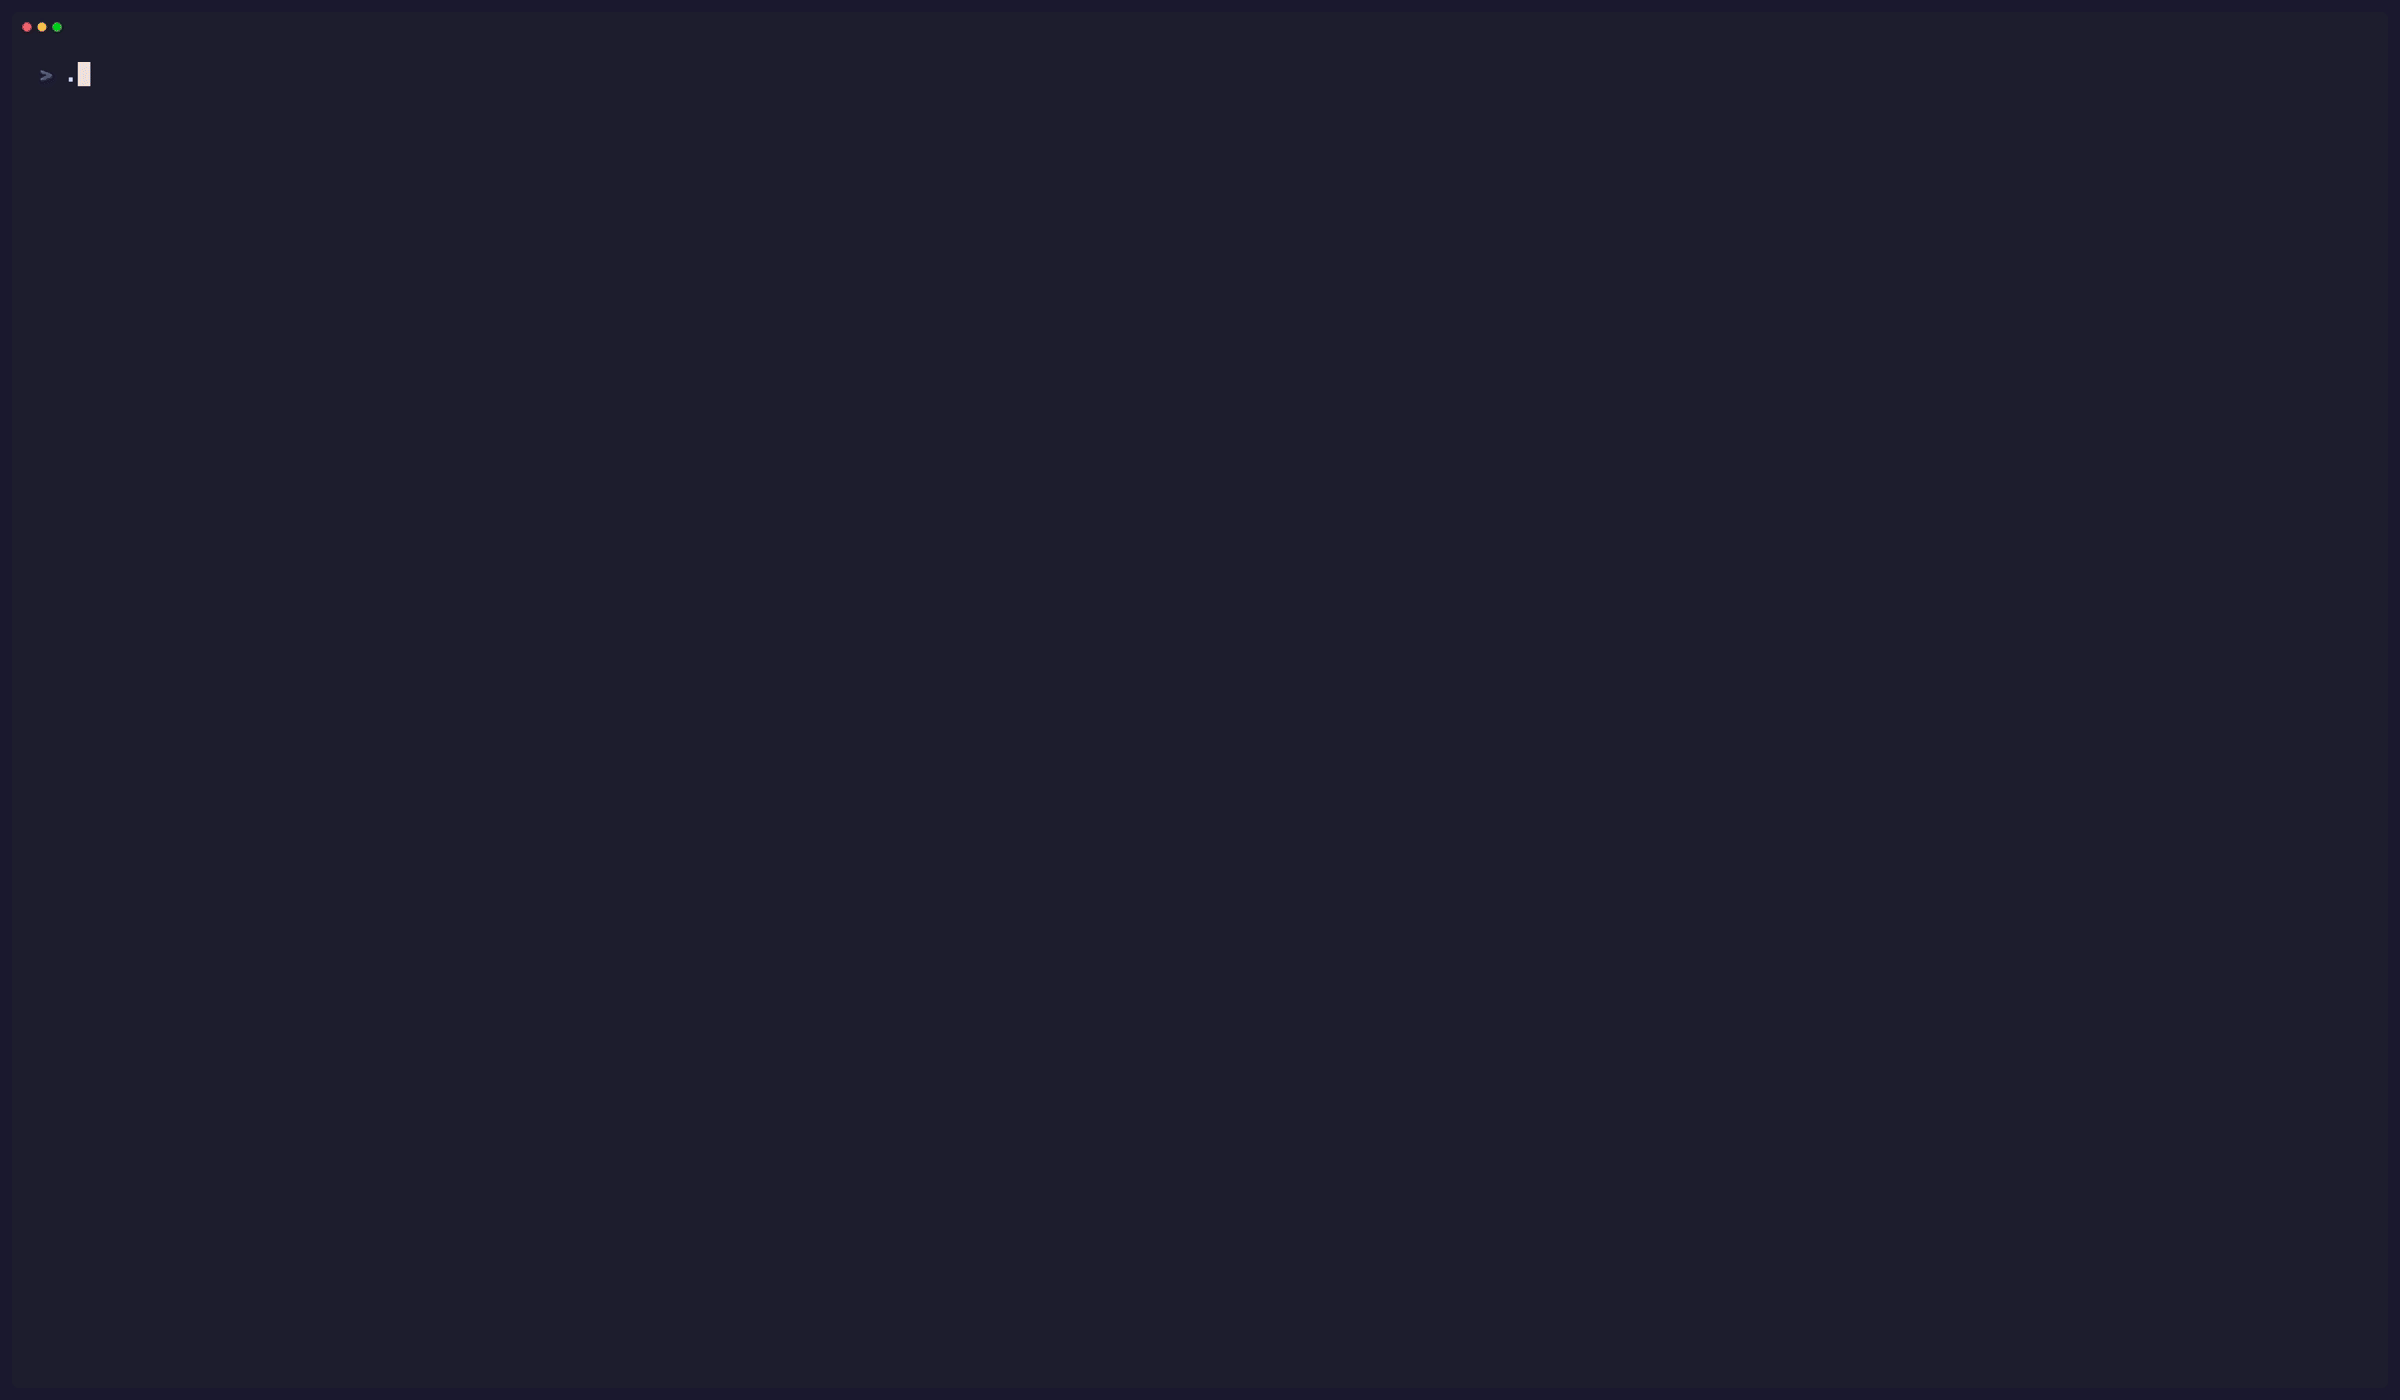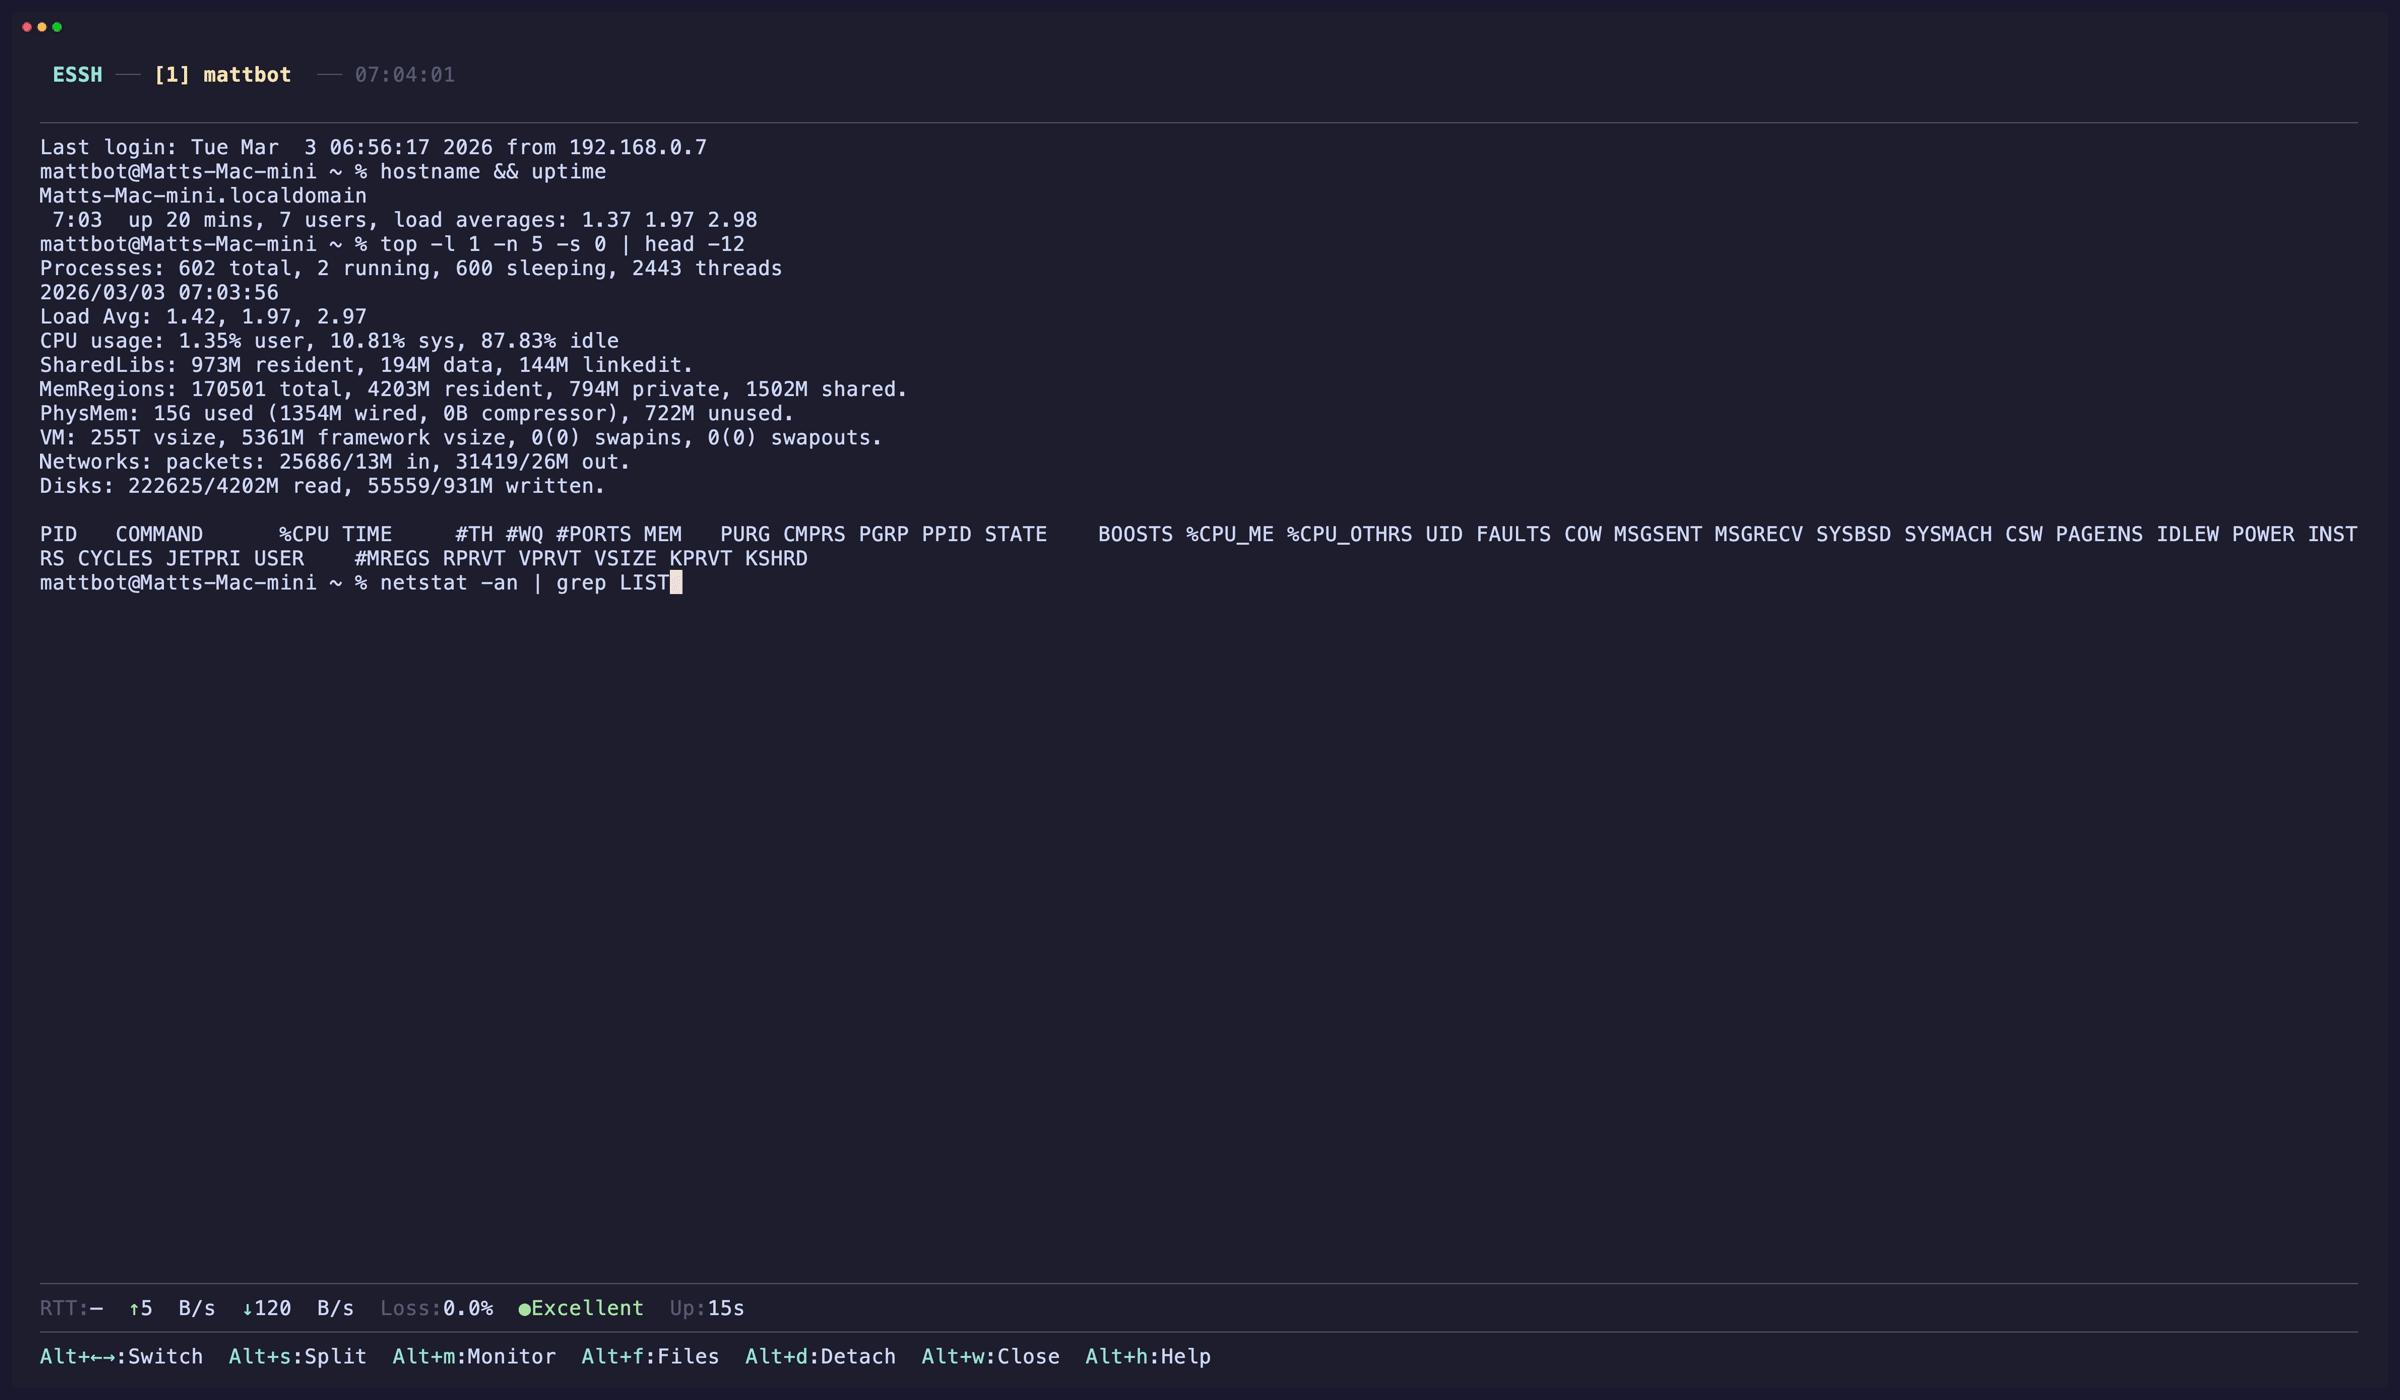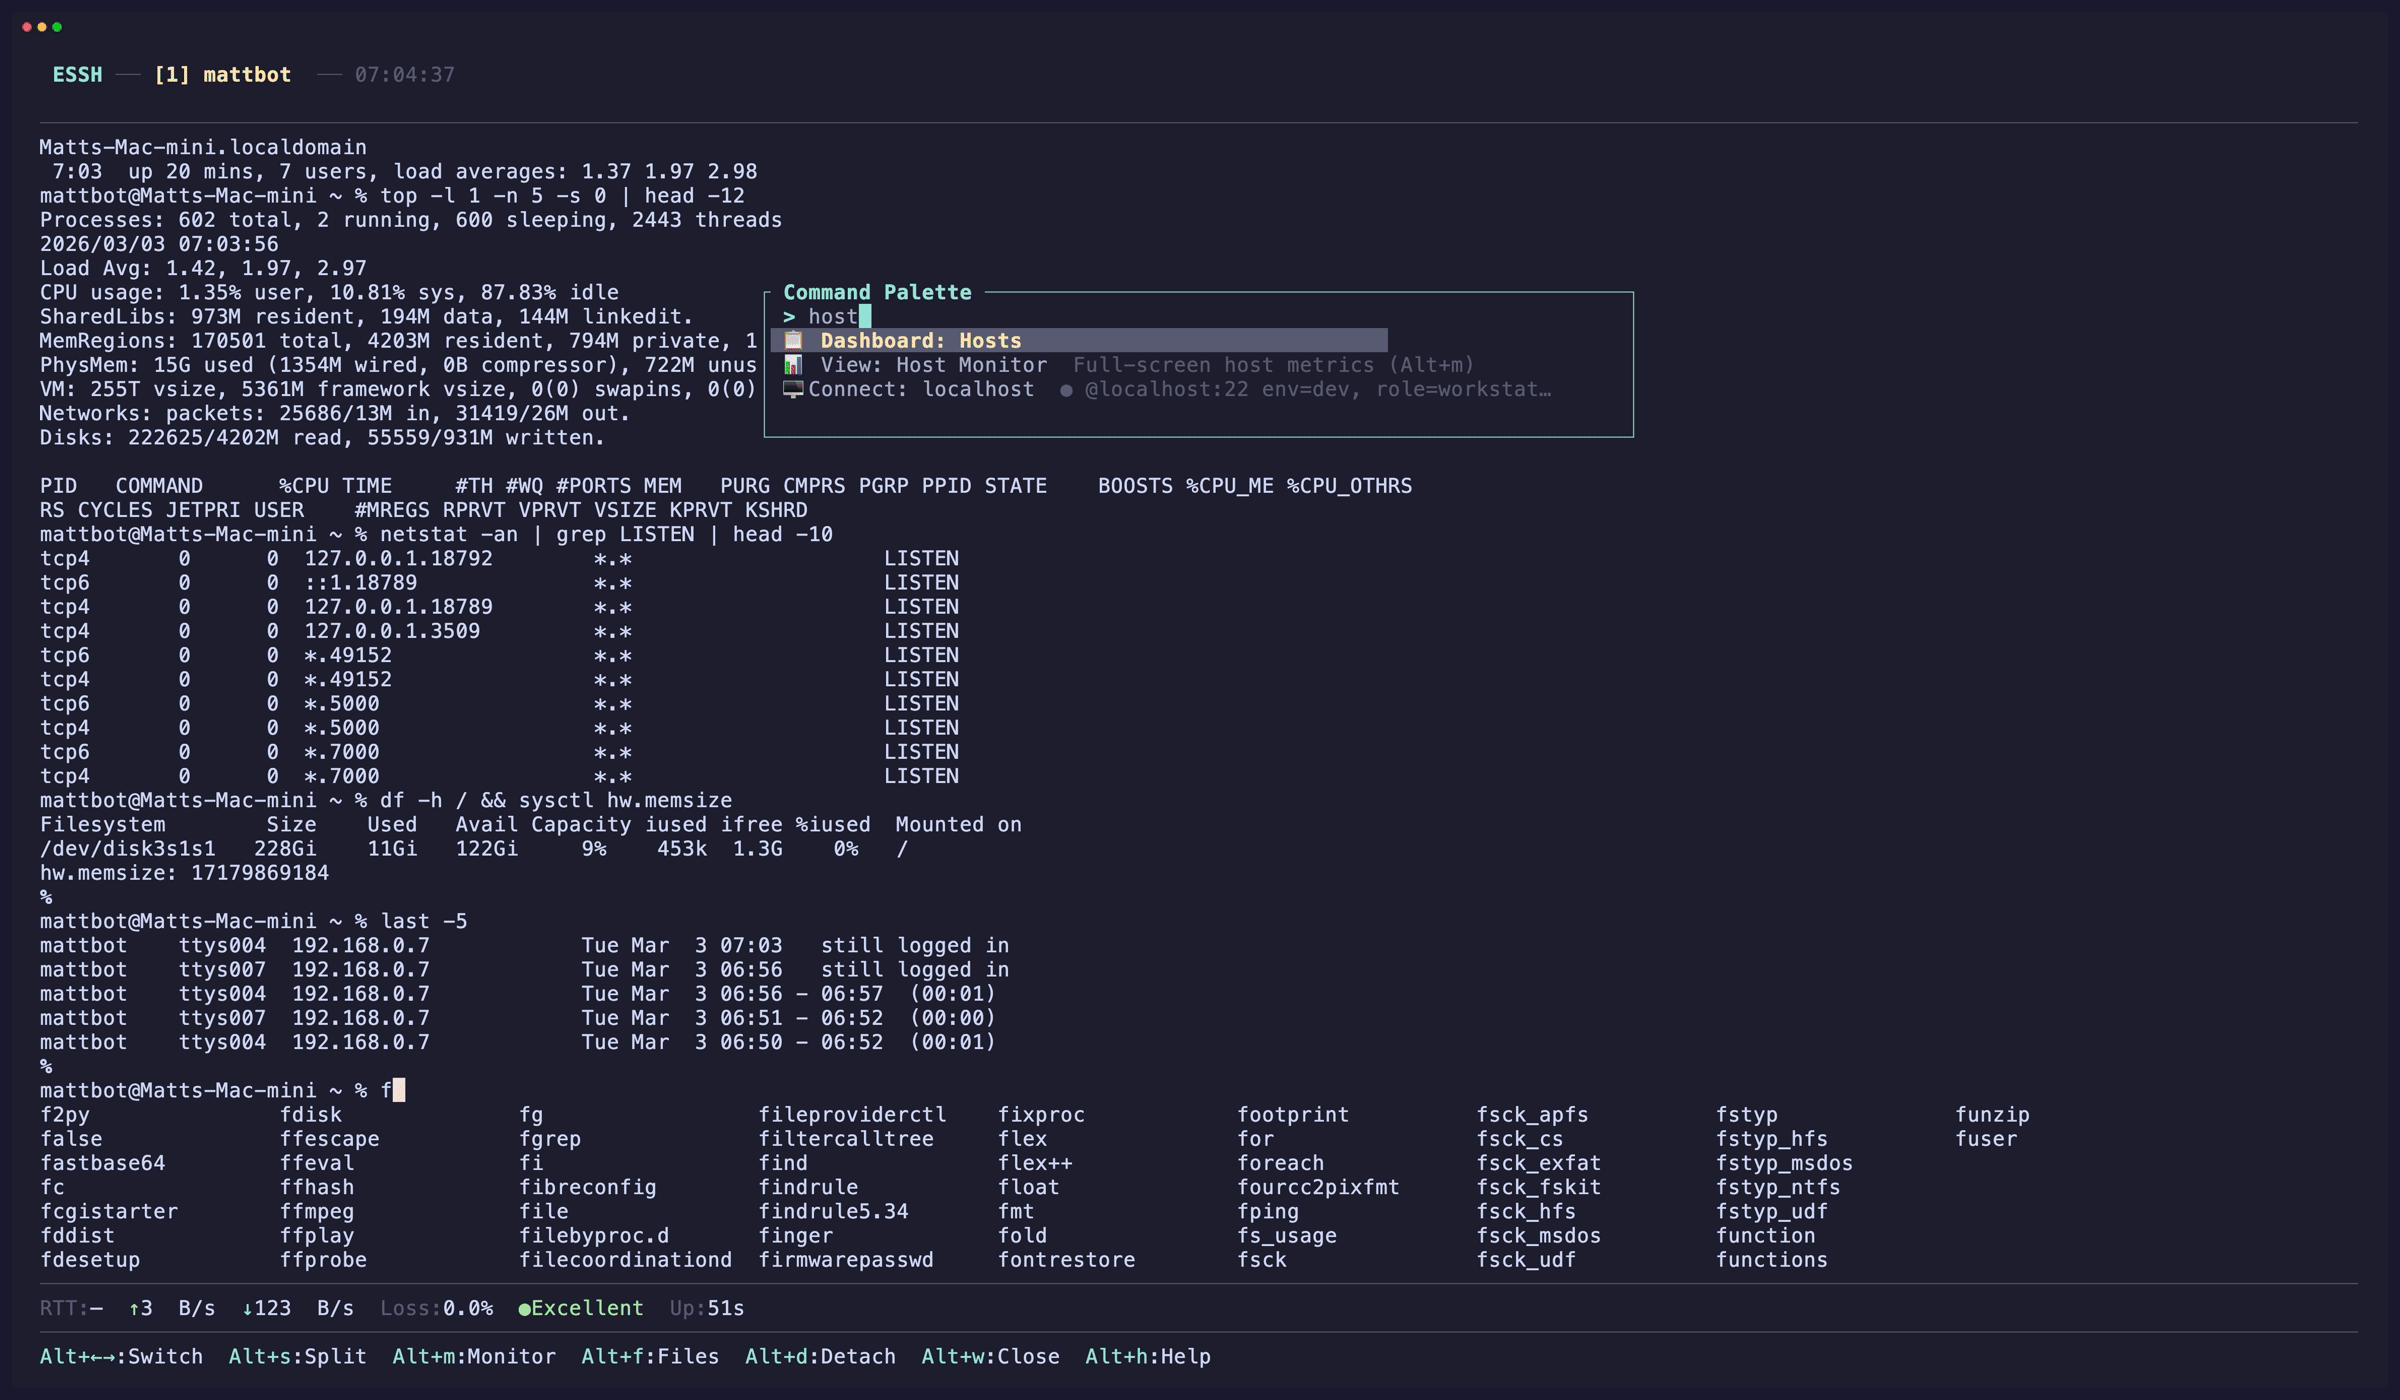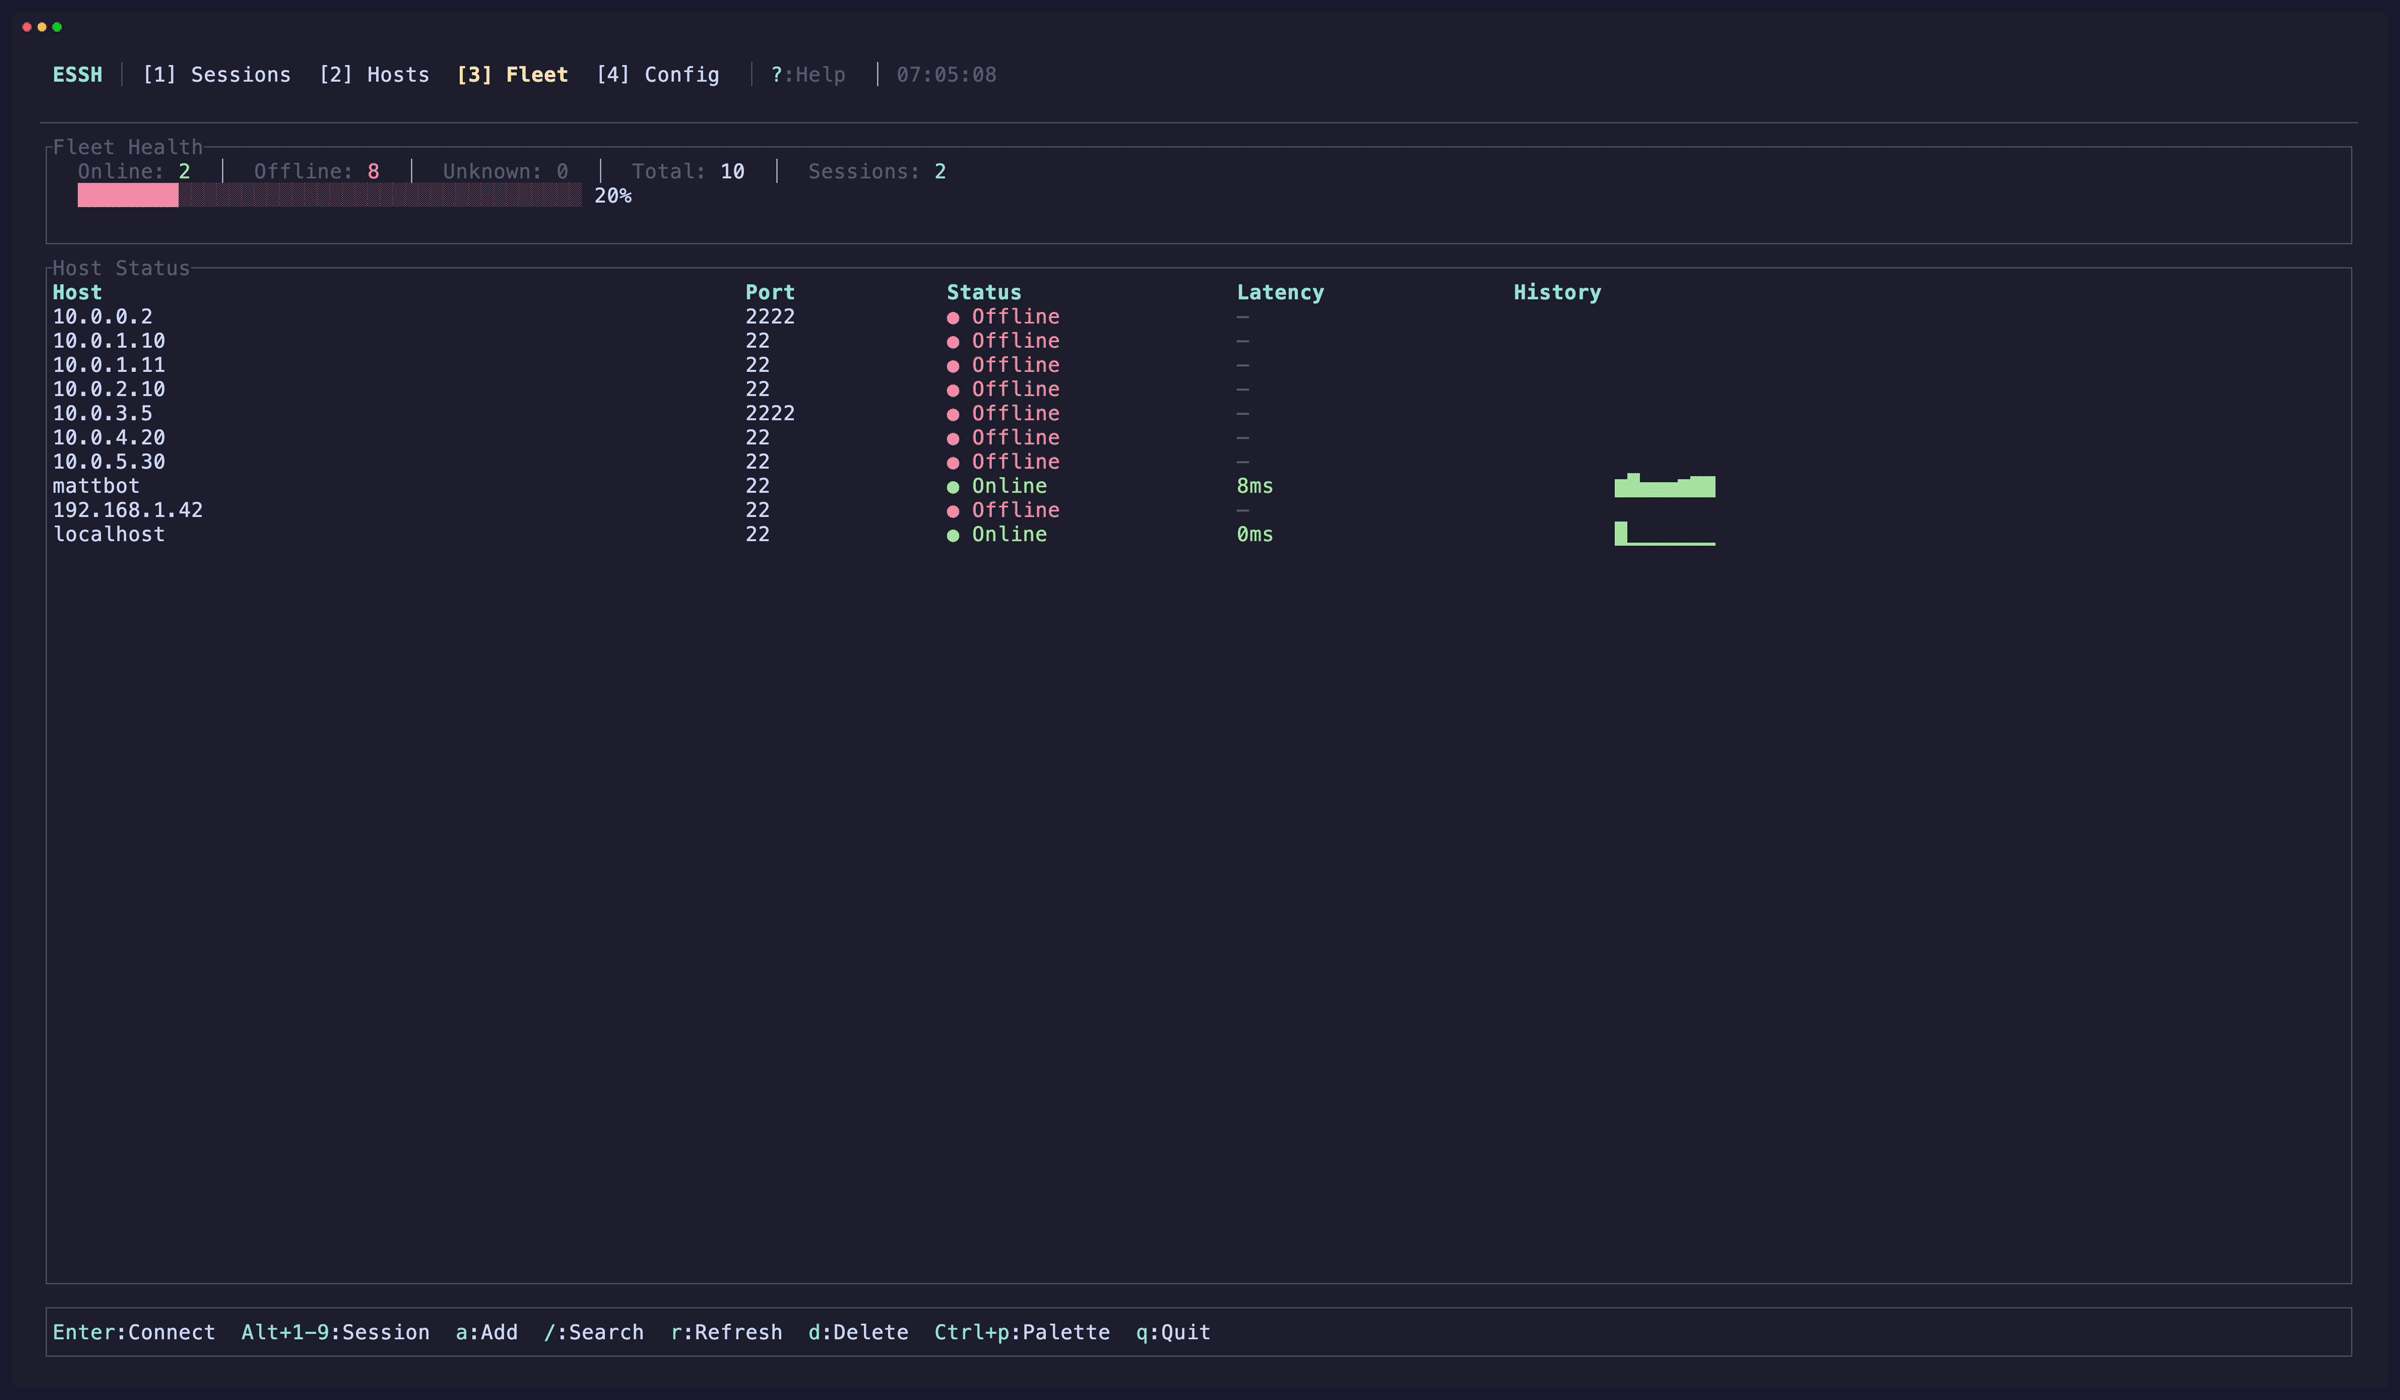 matthart1983/essh
Enhanced SSH client with TUI — manage connections, keys, and sessions
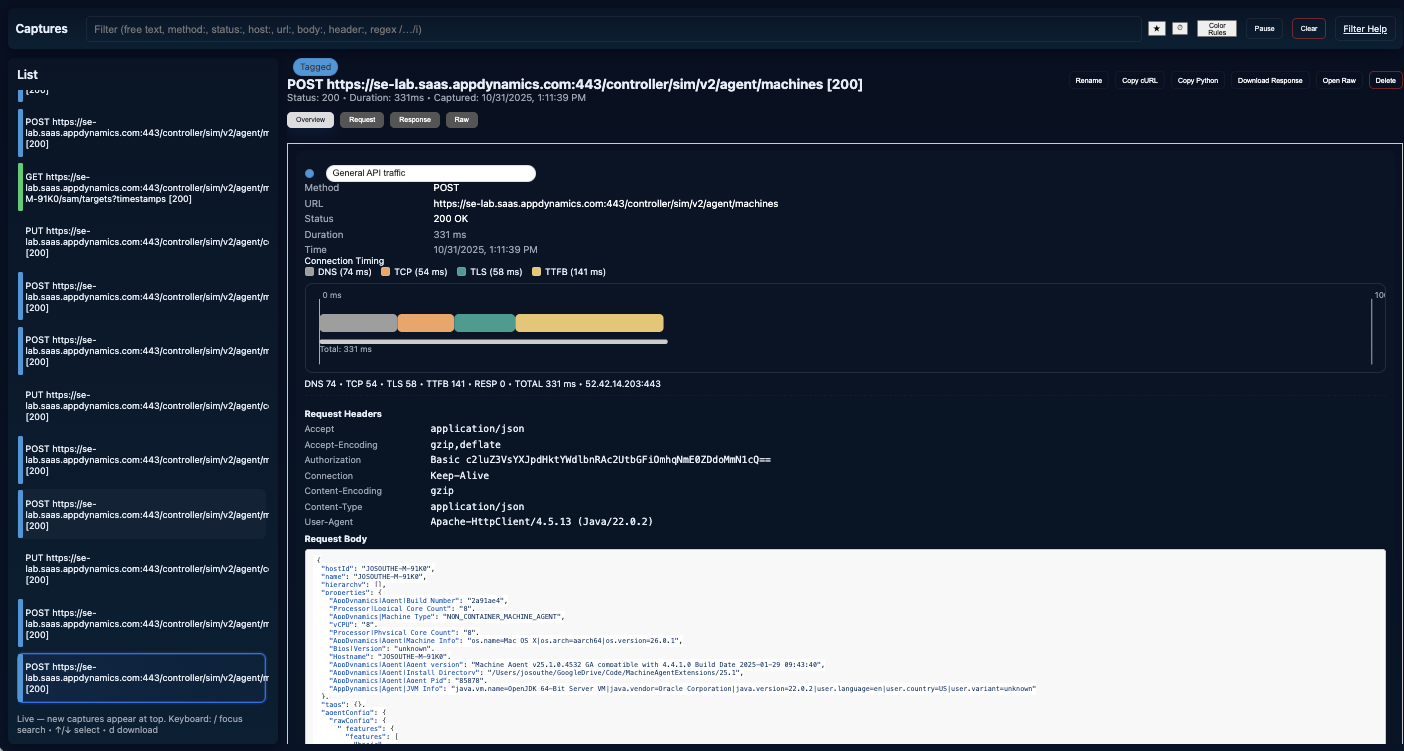 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
 k11h-de/bbot-ui
a terminal UI to browse bbot reports