
loki
 grafana/loki
Horizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
general-purpose-utilitiesincident-responselog-analysis+1
29.1k
grafana/lokiHorizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
 olafhartong/sysmon-modular
A repository of sysmon configuration modules
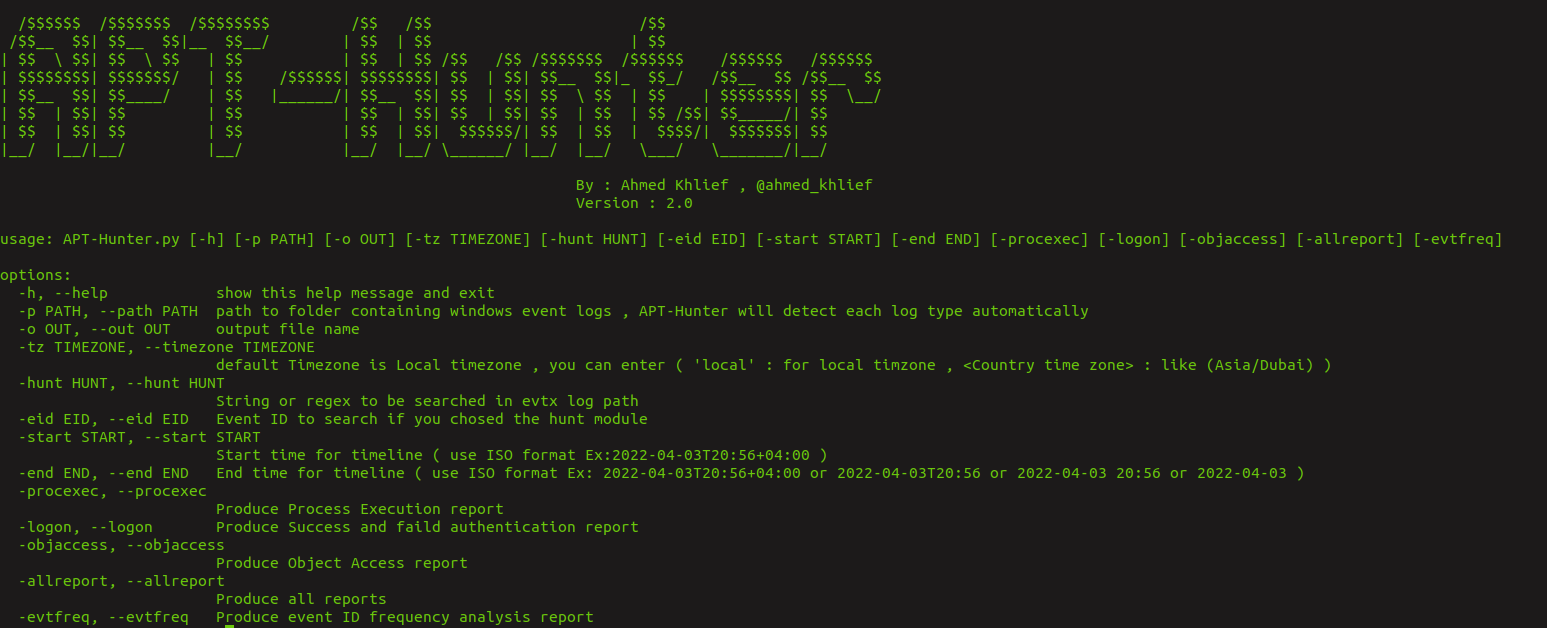 ahmedkhlief/apt-hunter
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…
 ion-storm/sysmon-config
Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 abdulrhmanalfaifi/fennec
Artifact collection tool for *nix systems
 hybridbrothers/hunting-queries-detection-rules
The purpose of this repository is to share KQL queries to help identify security misconfigurations, hunt for specific patterns, or detect malicious…
 sap8899/reportly
AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
 citrix/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
 fireeye/cve-2021-44228
OpenIOC rules to facilitate hunting for indicators of compromise
 ab2pentest/macosthreattrack
Bash tool used for proactive detection of malicious activity on macOS systems.
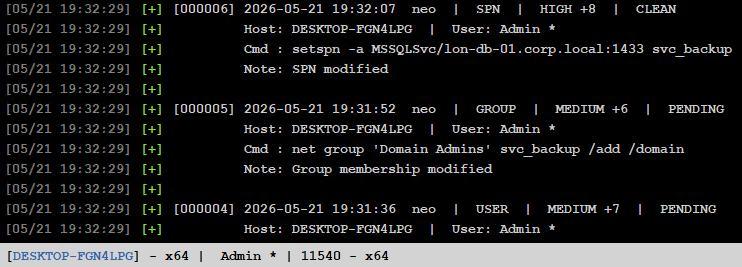 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
 f5devcentral/cve-2020-5902-ioc-bigip-checker
Local F5 BIG-IP script that scans for Indicators of Compromise (IoCs) related to CVE-2020-5902, checking logs, files, and system integrity to detect…
 nccgroup/mimikatz-detector-busylight
USB HID driver emulation with PID/VID (0x3bca/0x27bb) of Plenom A/S Busylight Alpha, that is supported by Mimikatz. When mimikatz is executed, a…
 santosomar/log4j-ioc-detector
A Simple Log4j Indicator of Compromise Linux Detector
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…