Multi-Stage-Exploitation-and-Detection-Engineering-Analysis-of-CVE-2023-34362-in-MOVEit-Transfer

This repository contains an academic and technical analysis of CVE-2023-34362, a critical SQL injection vulnerability affecting the MOVEit Transfer…

This repository contains an academic and technical analysis of CVE-2023-34362, a critical SQL injection vulnerability affecting the MOVEit Transfer…

Proof-of-concept exploit for CVE-2020-35488, a denial-of-service vulnerability in NXLOG Community Edition via crafted syslog payloads causing…

Scans GitHub workflows and logs for indicators of CVE-2025-30066, detecting malicious actions and exposed secrets using Checkmarx 2ms integration.

Automated threat hunting pipeline that ingests Azure logs, uses LLM reasoning to detect suspicious activity, assess risk, and generate remediation…

A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.

Advisory and detection notes for CVE-2026-25769, a critical Wazuh cluster-mode insecure deserialization flaw enabling worker-to-master root RCE, with…

Performed a live cybersecurity assessment on a university Linux server. During analysis, active attack activity was identified, including brute-force…

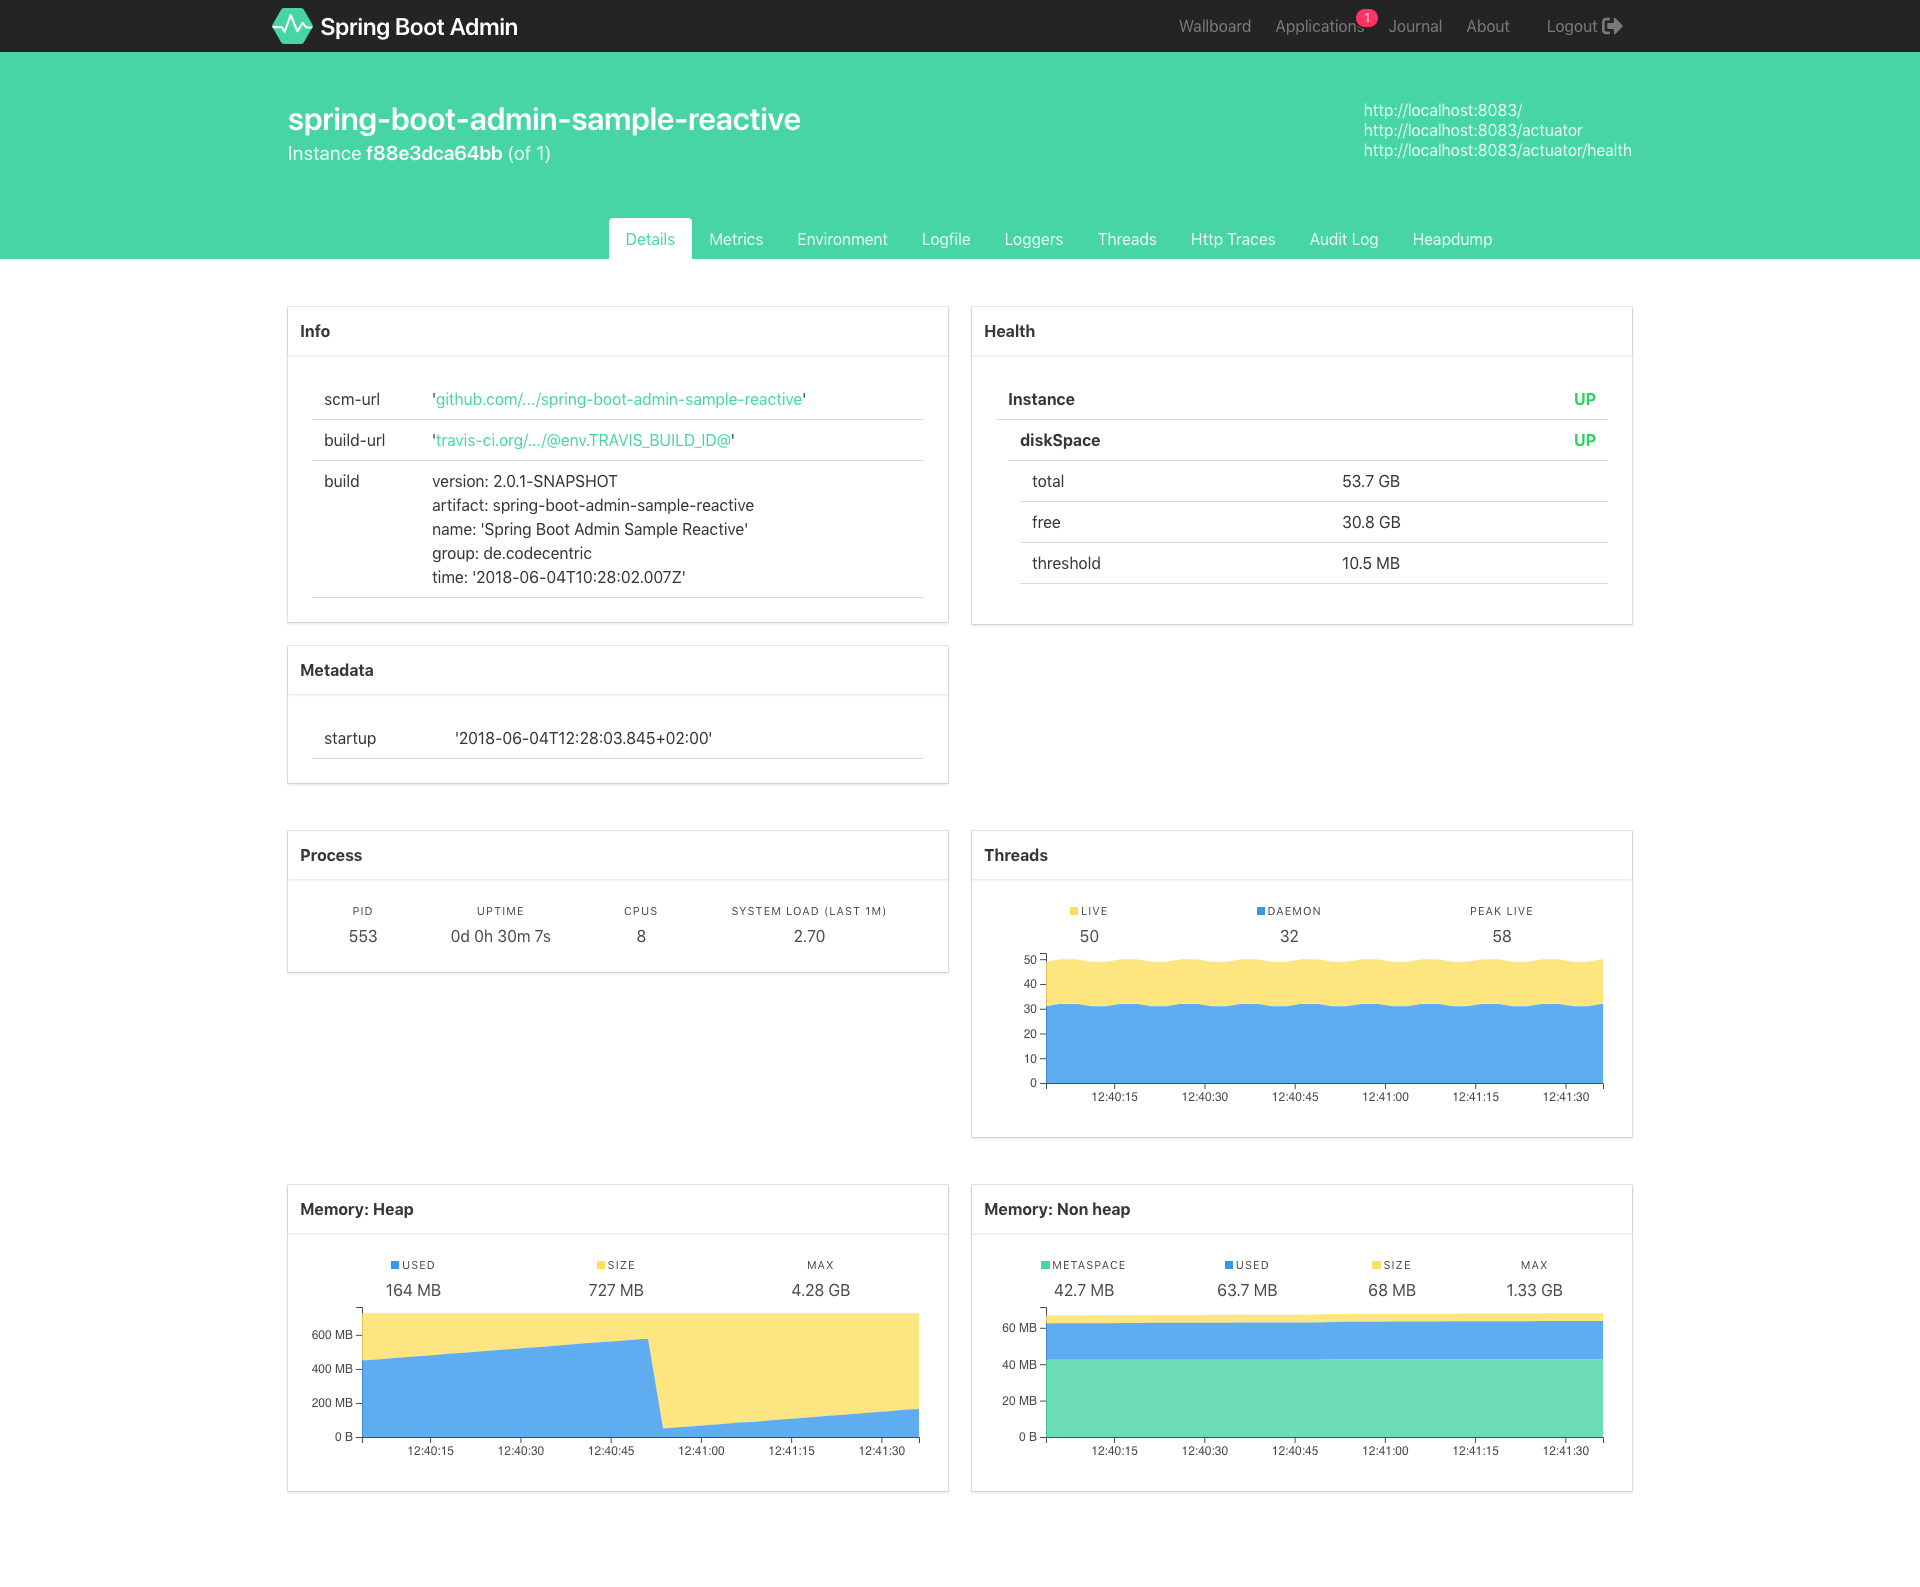
Admin interface for monitoring Spring Boot applications with health checks, metrics, log management, JMX interaction, and thread dump viewing.

A hands on lab investigating CVE-2025-39507 from a Tier 1 SOC analyst perspective. Includes log review in Microsoft Sentinel, IP analysis, real world…

Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…

PowerShell-based scanner to detect Log4j CVE-2021-44228 vulnerability by searching directories and log files for exploitation indicators.

CVE-2021-44228 Response Scripts

Check to see if your Palo Alto firewall has been compromised by running script againt support bundle.

This script is used to perform a fast check if your server is possibly affected by CVE-2021-44228 (the log4j vulnerability).

SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.

Easy-to-use live forensics toolbox for Linux endpoints

Indicator of Compromise Scanner for CVE-2019-19781

Pivotable Reverse WhoIs / PDNS Fusion with Registrant Tracking & Alerting plus API for automated queries (JSON/CSV/TXT)