

maltrail
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k
stamparm/maltrailReal-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
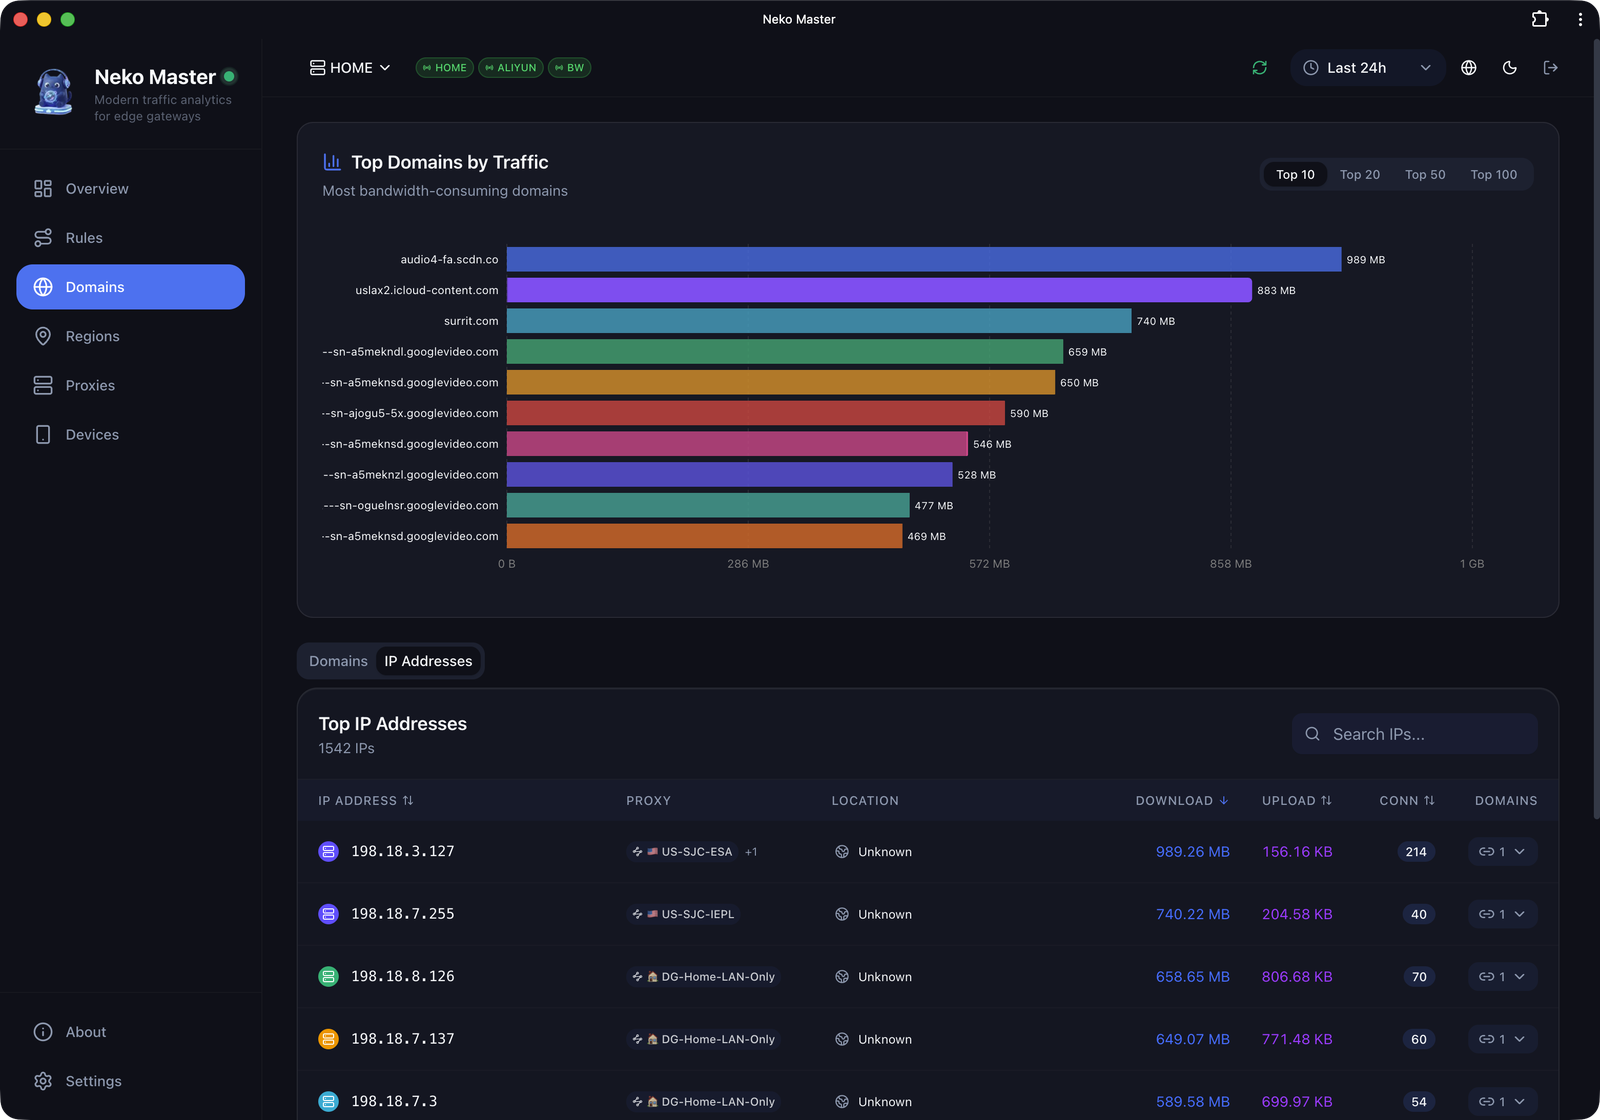 foru17/neko-master
A modern and elegant dashboard for network traffic visualization and analysis.
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
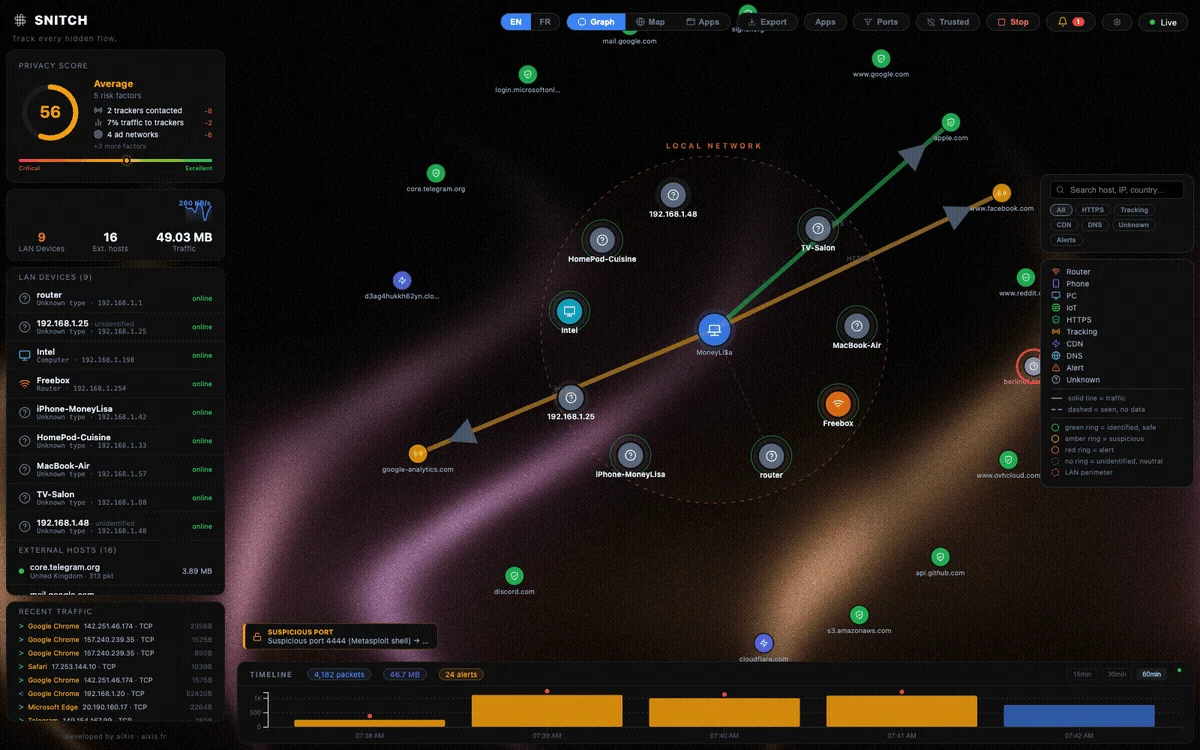 aixisstudio/snitch
Real-time network traffic visualizer — see every connection your computer makes. Privacy-first, 100% local. / Visualiseur de trafic réseau en temps…
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
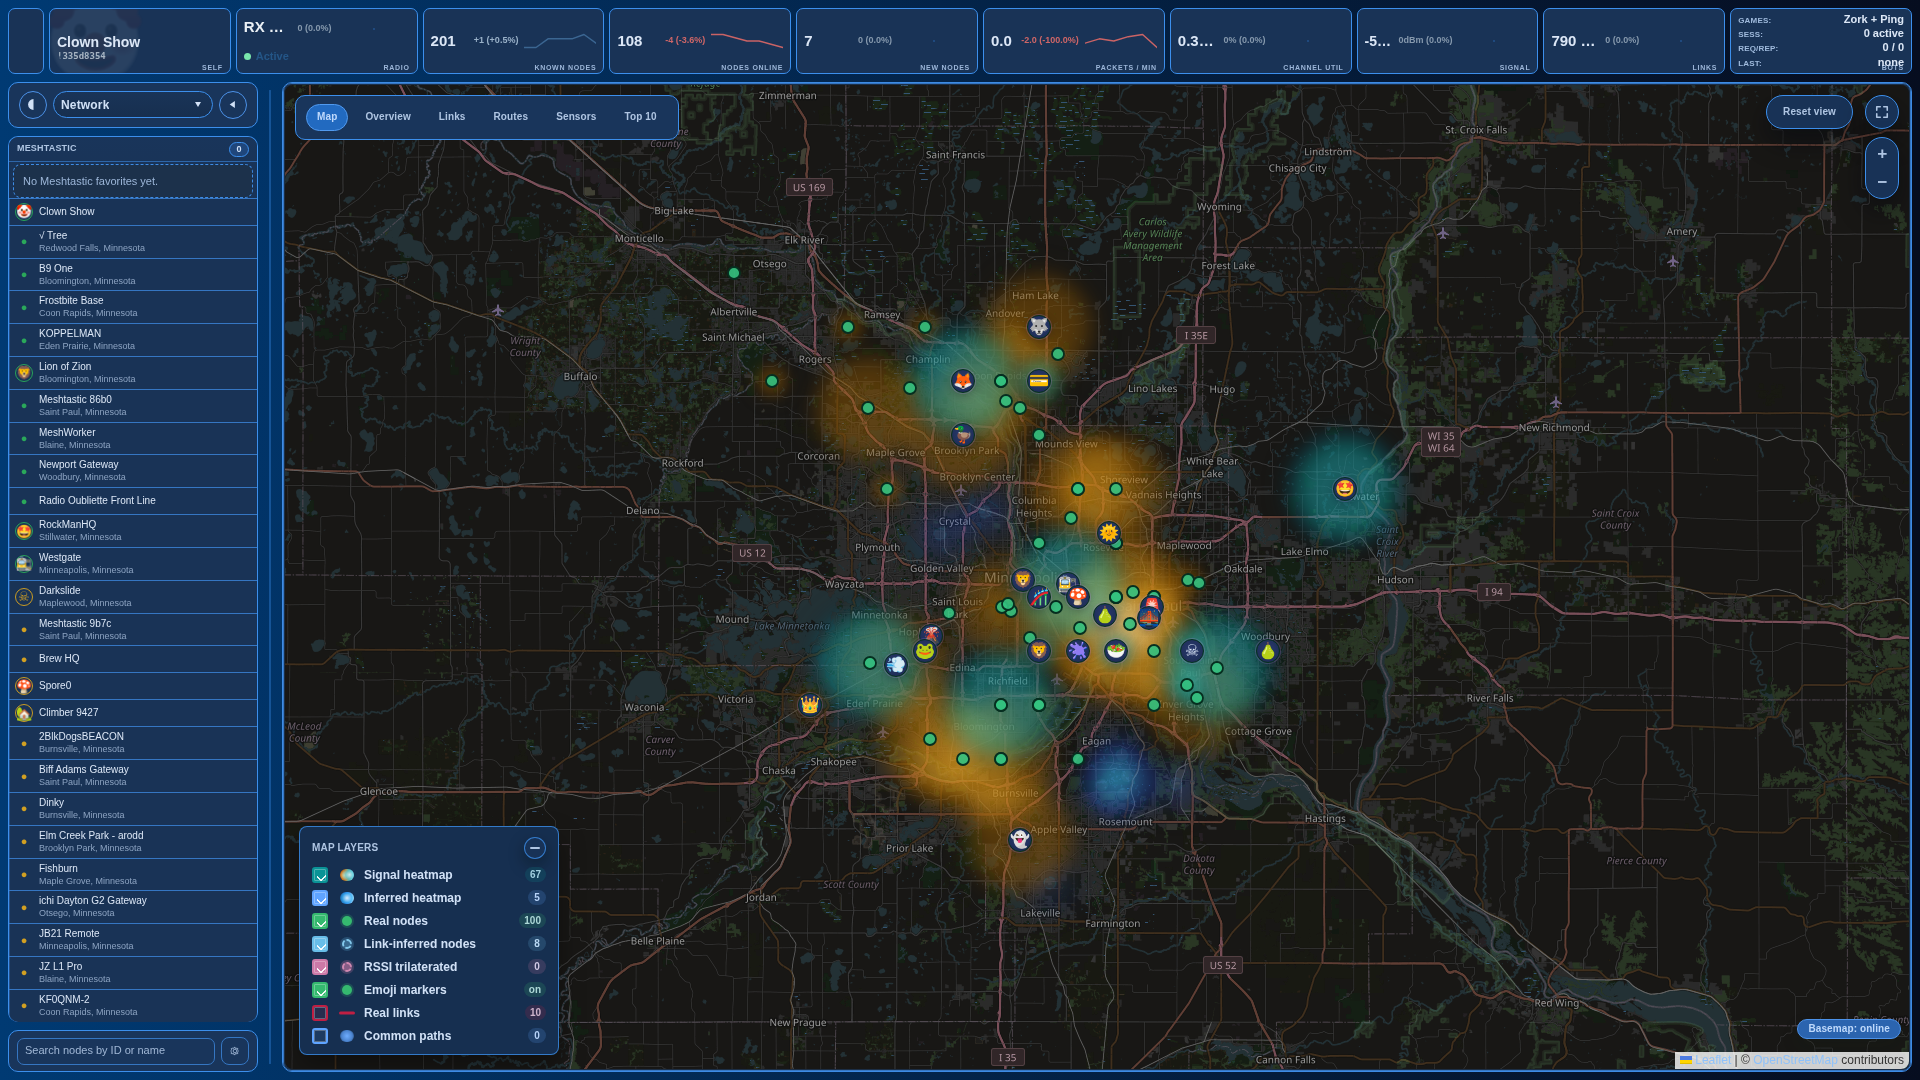 jaronmcd/meshyface
Single-page web dashboard for Meshtastic mesh networks with live network mapping, packet analysis, chat, sensor telemetry, and topology…
 fenkohq/dnsmonster
Passive DNS Capture and Monitoring Toolkit

 ctrlaltint3l/intelligence
Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
 corelight/zeek-endpoint-enrichment
Zeek log enrichment tool that adds host information and known entity references to enhance network security monitoring and incident response.
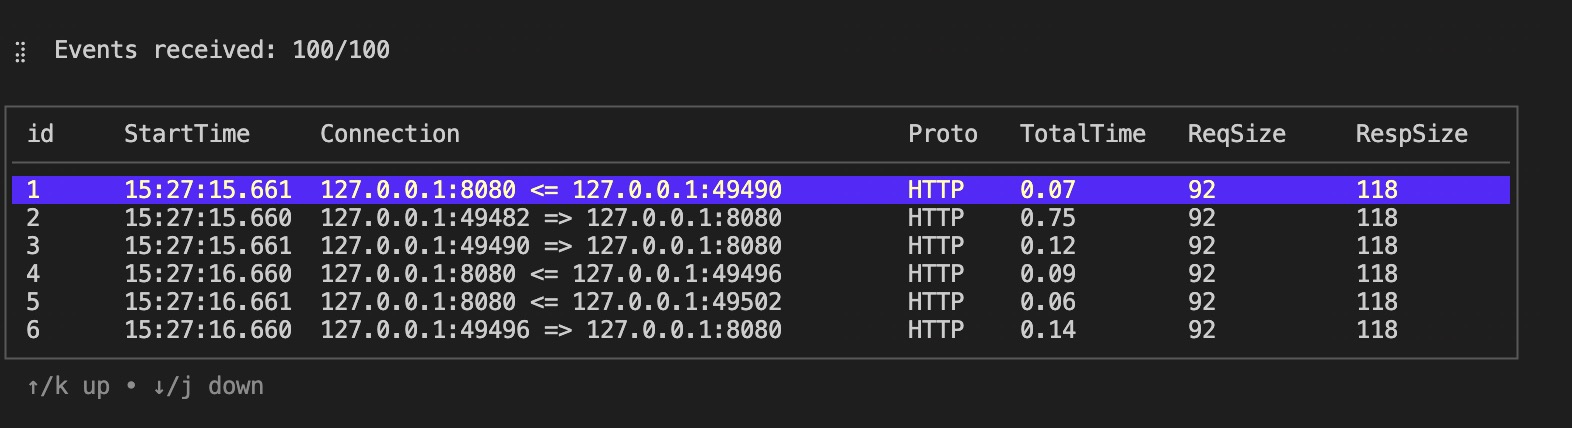 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
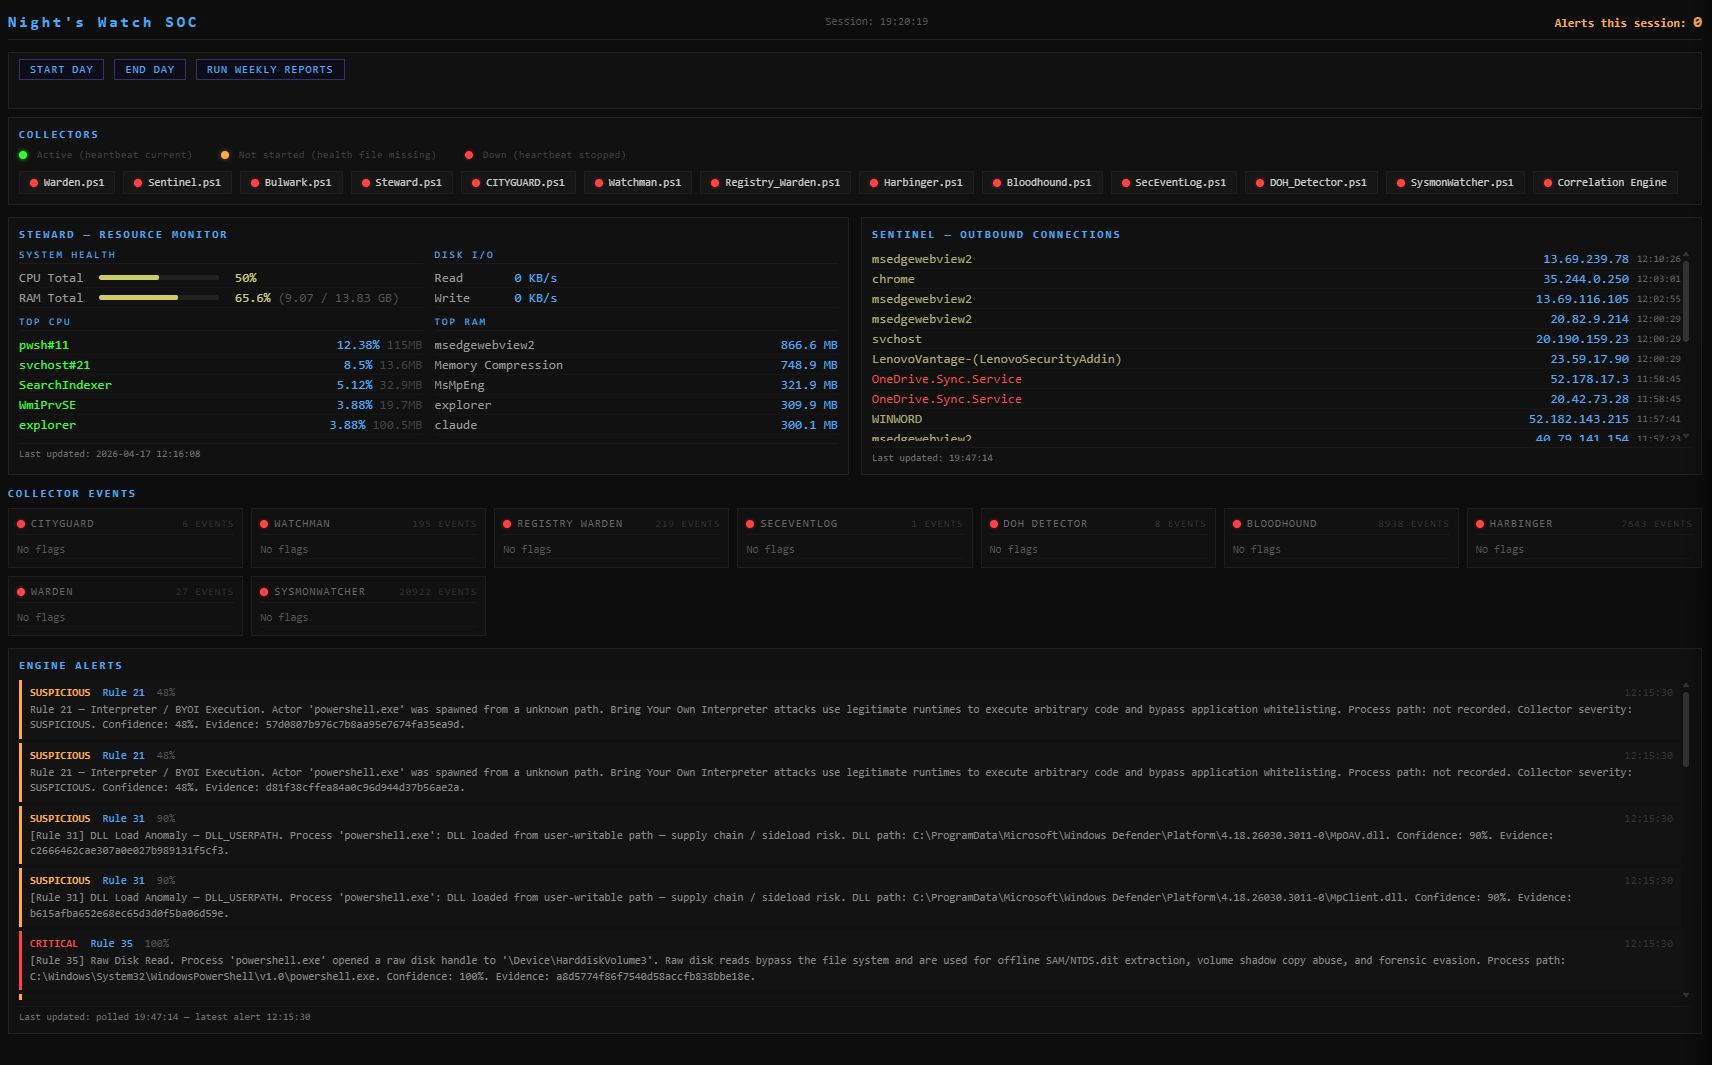 nate-ryan-7690/home_soc_suite
A personal Windows SOC suite built in PowerShell — monitors network connections, resource usage, scheduled tasks and power events with severity…
 mithileshan/soc-investigation-lab
End-to-end SOC investigation: CVE-2011-2523 kill chain, multi-source log correlation, incident report — MITRE ATT&CK T1190
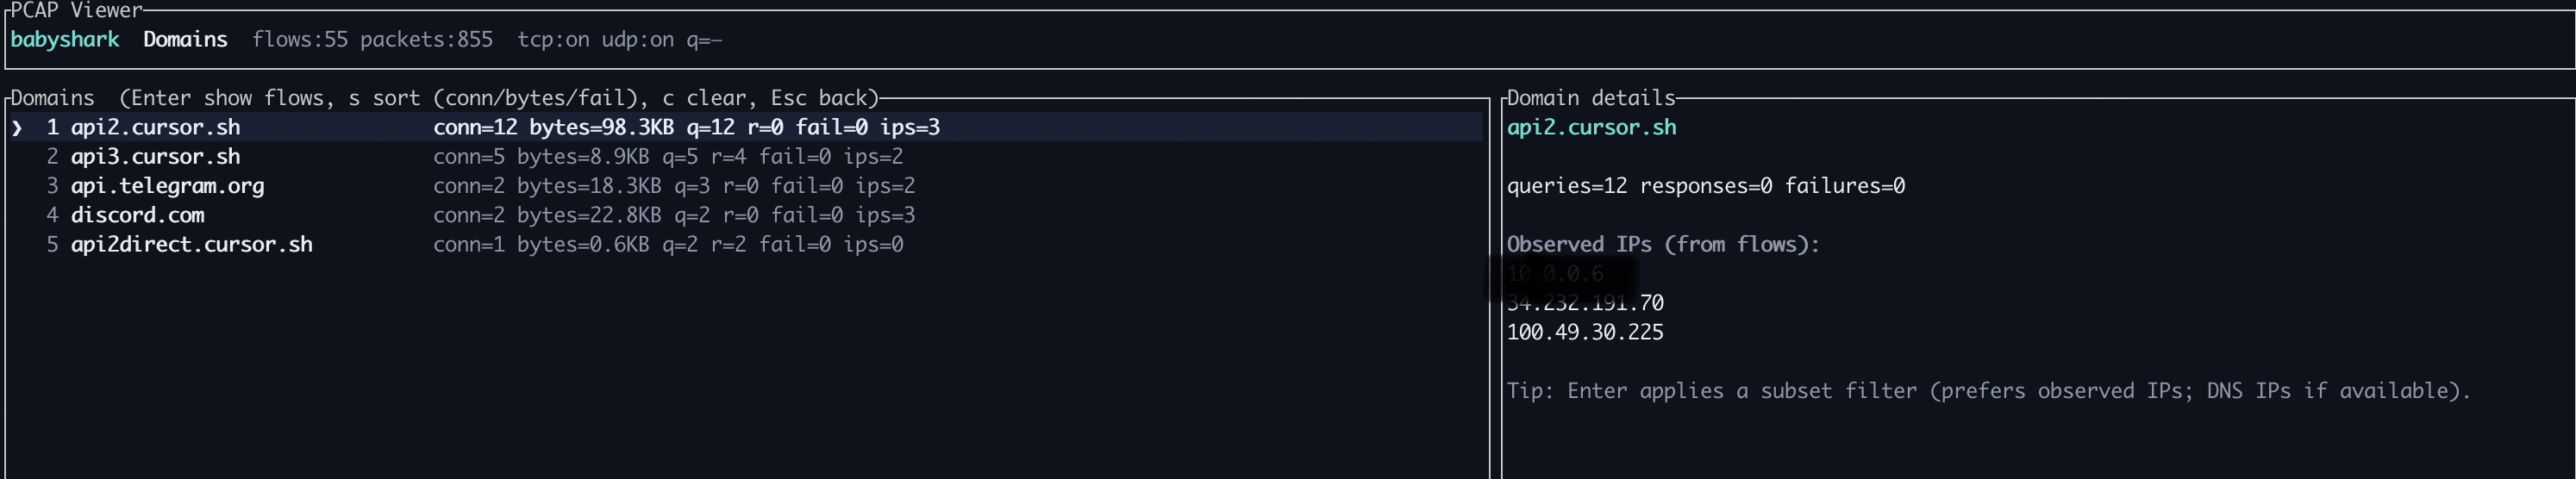 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
 k11h-de/bbot-ui
a terminal UI to browse bbot reports