
Agentic-Evidence
 owasp/agentic-evidence
OWASP reference project for agentic AI security evidence: correlates agent execution, identity, tool calls, and authorization decisions into…
ai-securityanomaly-detectioncurated-resources+6
2
owasp/agentic-evidenceOWASP reference project for agentic AI security evidence: correlates agent execution, identity, tool calls, and authorization decisions into…
 tsale/edr-telemetry
This project aims to compare and evaluate the telemetry of various EDR products.
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
 foru17/neko-master
A modern and elegant dashboard for network traffic visualization and analysis.
 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
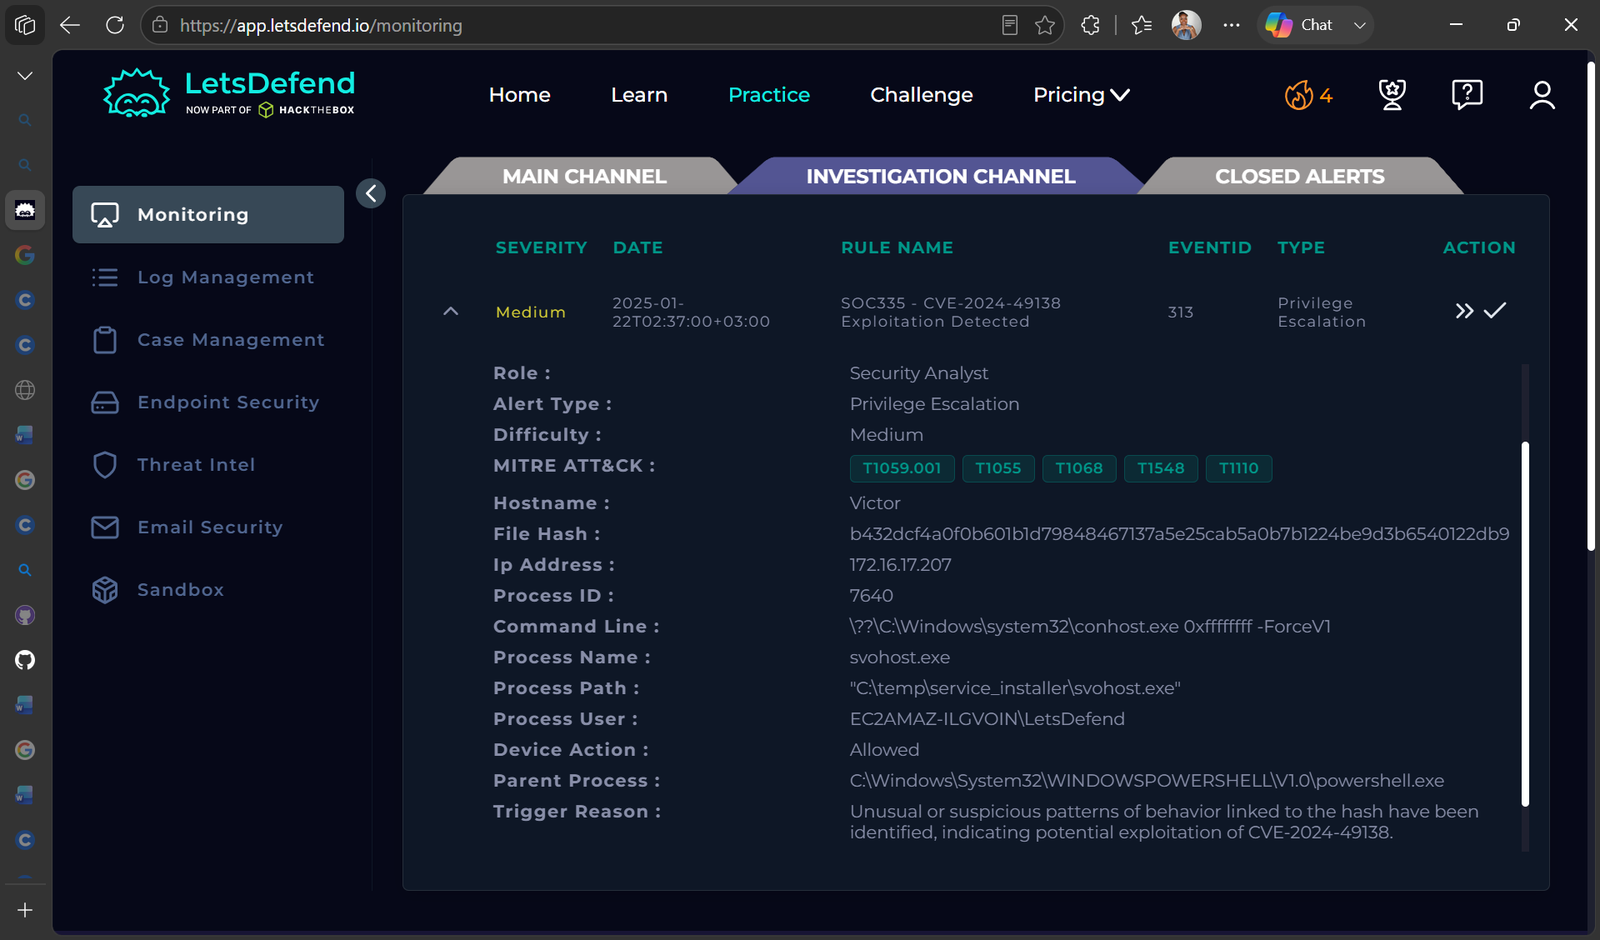 nadineelliottcyber/soc335-cve-2024-49138-investigation
SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 freeguy-6/dmz-security-monitoring-hardening
CY376 Blue Team project — pfSense DMZ, Suricata IDS/IPS, and automated host hardening against CVE-2014-6271
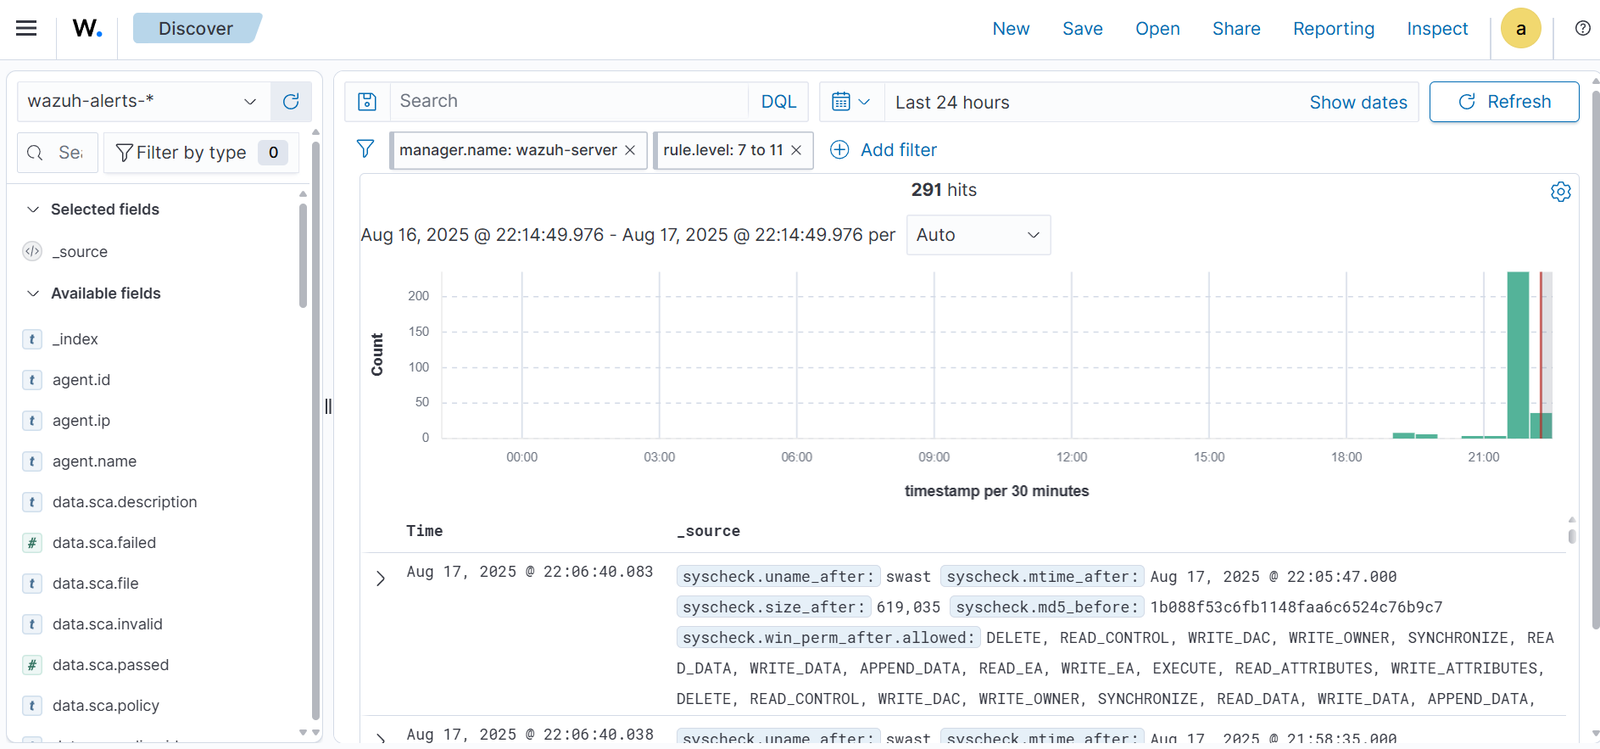 swastiksagar/wazuhlabproject
Hands-on Wazuh SIEM/XDR home lab covering OVA deployment, agent enrollment, file integrity monitoring, VirusTotal malware detection, and MITRE ATT&CK…
 shahdawadfallah-sys/cybersecurity-capstone-project
Cybersecurity Capstone Project completed during the NCSC Nashama CyberCamp 11, delivered in collaboration with IT Security C&T. The project…
 the-dfir-report/sigma-rules
Rules generated from our investigations.
 alisha-chaudhary/ssh-enum
This project explores whether modern OpenSSH reveals valid usernames through subtle response or timing differences. CVE-2016-6210 user enumeration…
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
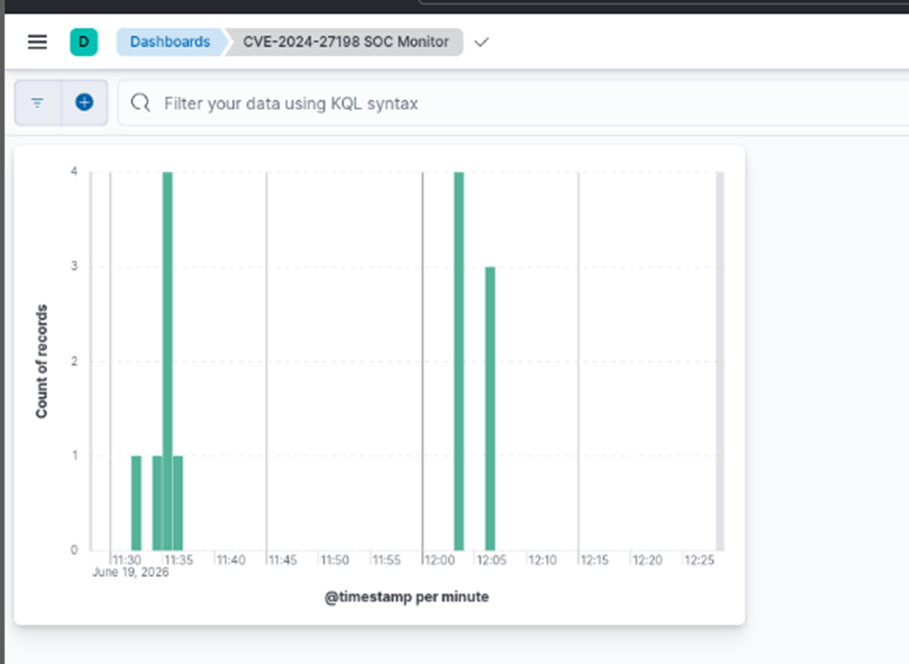 ptd200110/cve-2024-27198-soc-lab
SOC detection and incident response lab simulating CVE-2024-27198 authentication bypass in JetBrains TeamCity. Includes ELK SIEM, Suricata IDS, Sigma…