

ModSecurity
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
anti-botapi-securitydefensive-tools+7
9.8k
owasp-modsecurity/modsecurityModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 tenzir/tenzir
Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
 phpatch/weblogchecker
Free access-log compromise analyzer: webshell interactions, exploitation patterns and brute-force bursts in your Apache/nginx logs - severity,…
 gitlab-security-oss/tldr
Sigma-based detection rules, log queries, atomic tests, and response procedures for monitoring and threat hunting in GitLab environments.
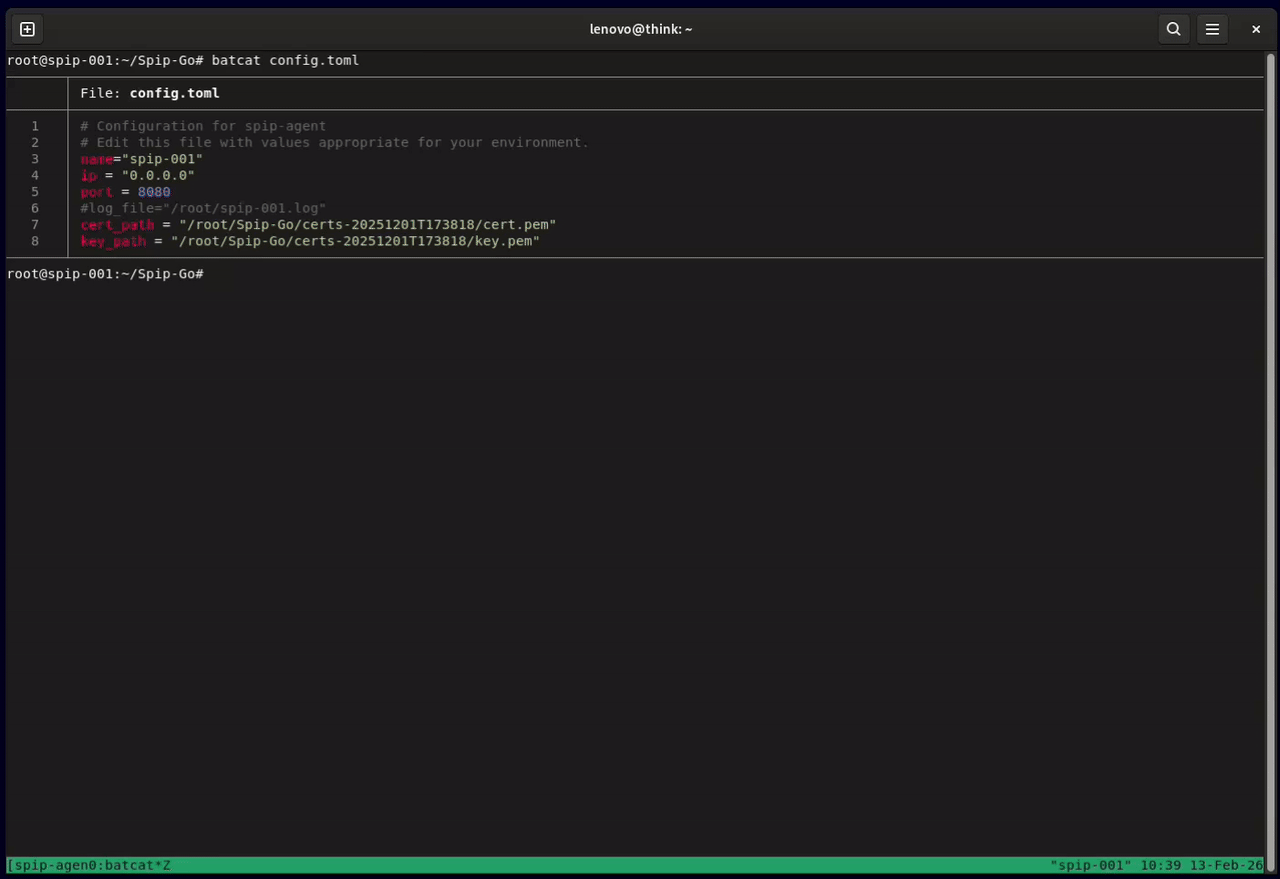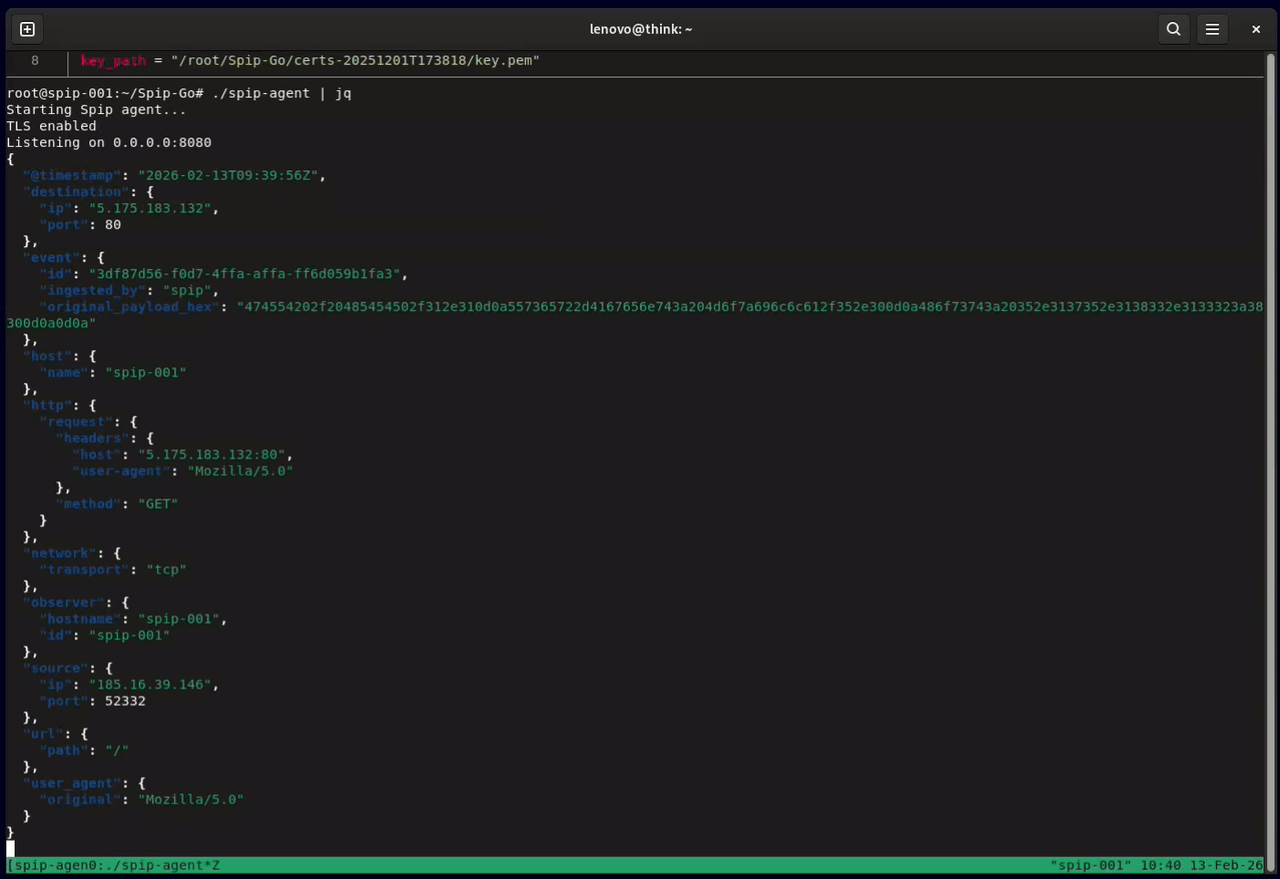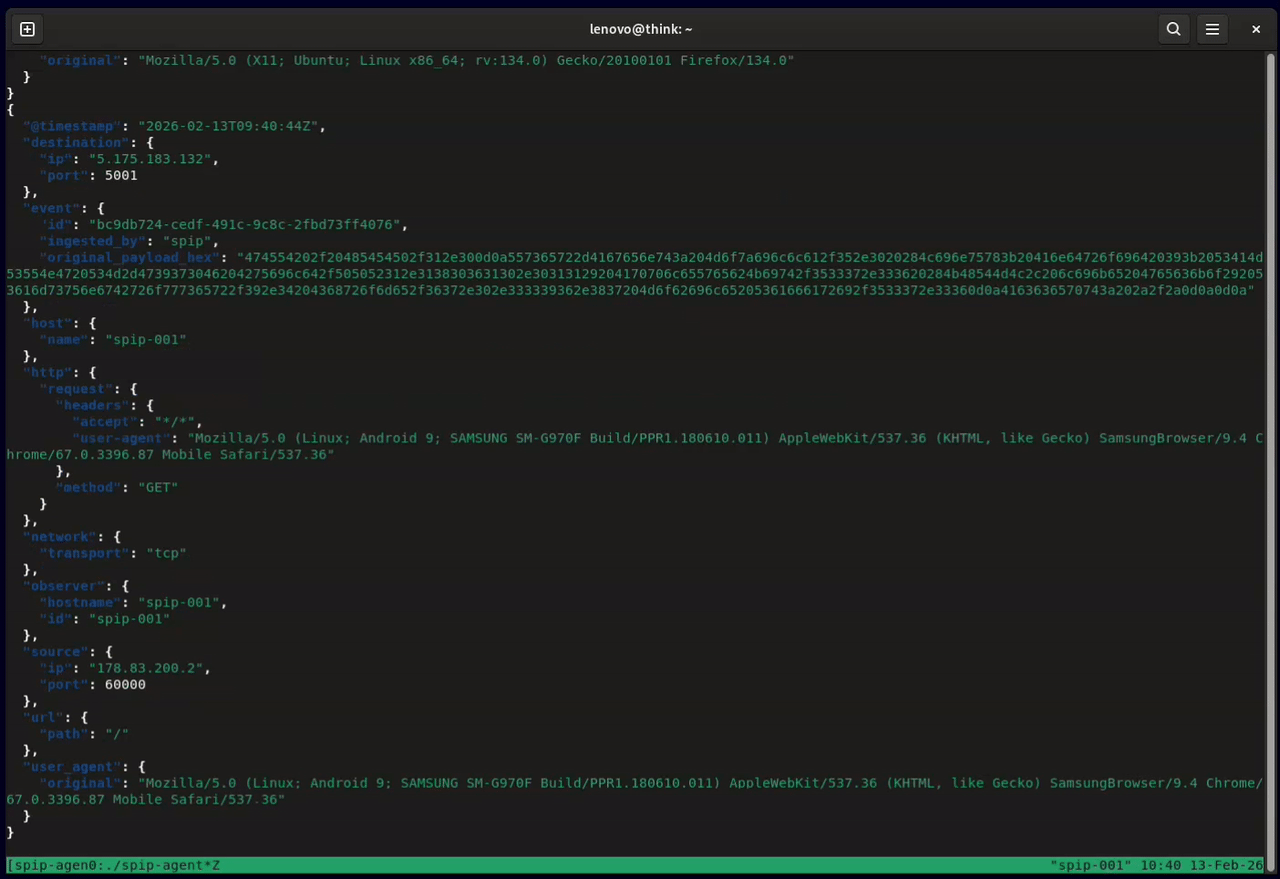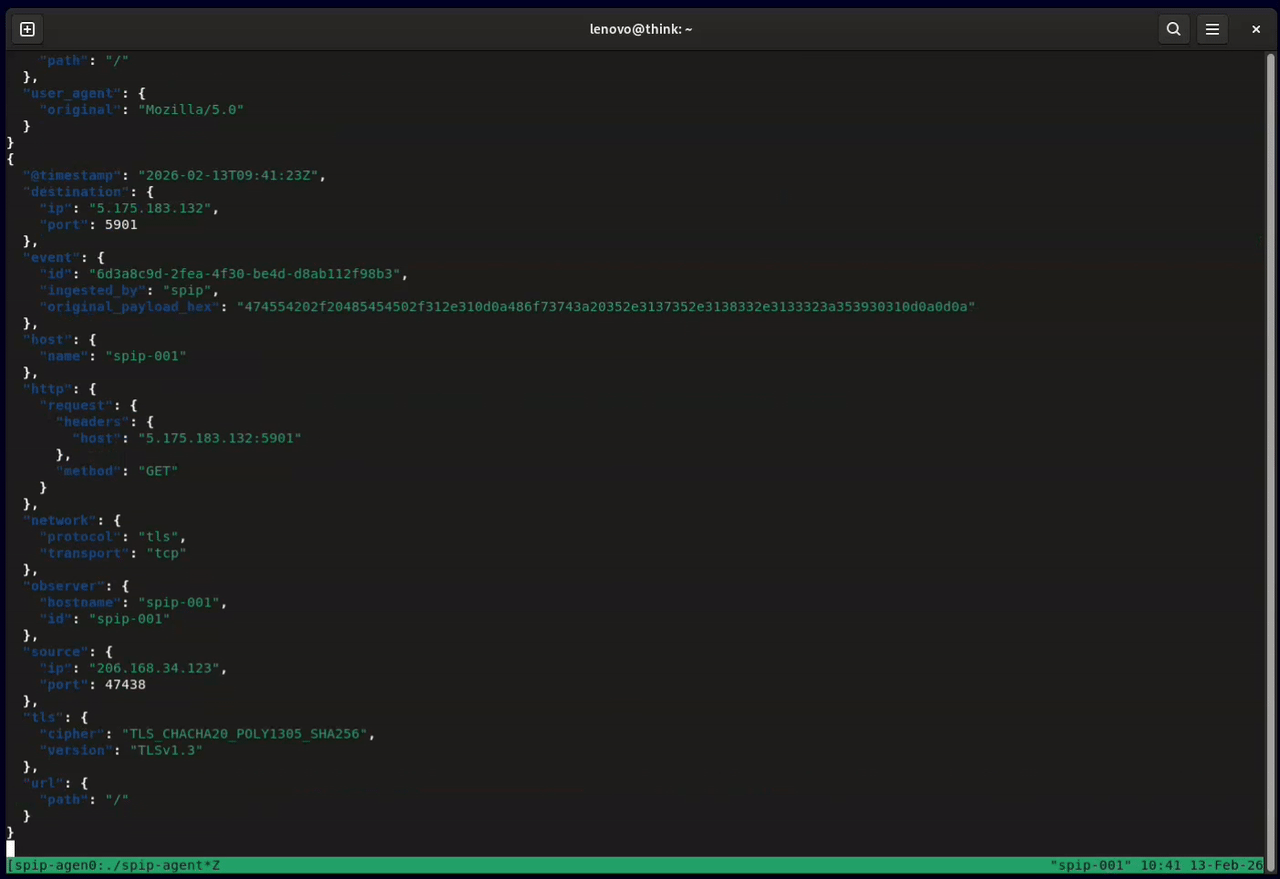 honeylabshq/spip-go
Spip network sensor written in Go
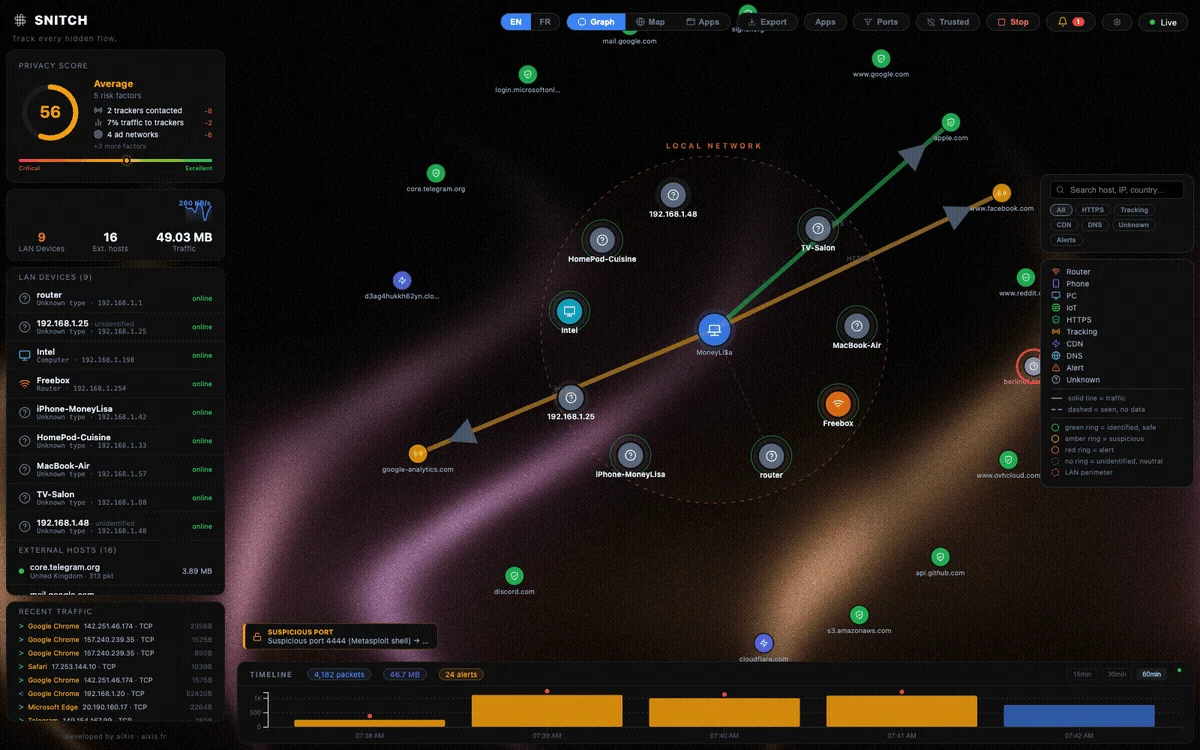 aixisstudio/snitch
Real-time network monitor + outbound firewall — see & block every connection. Privacy-first, local-first, Rust fleet agent, SIEM exports, 8…
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
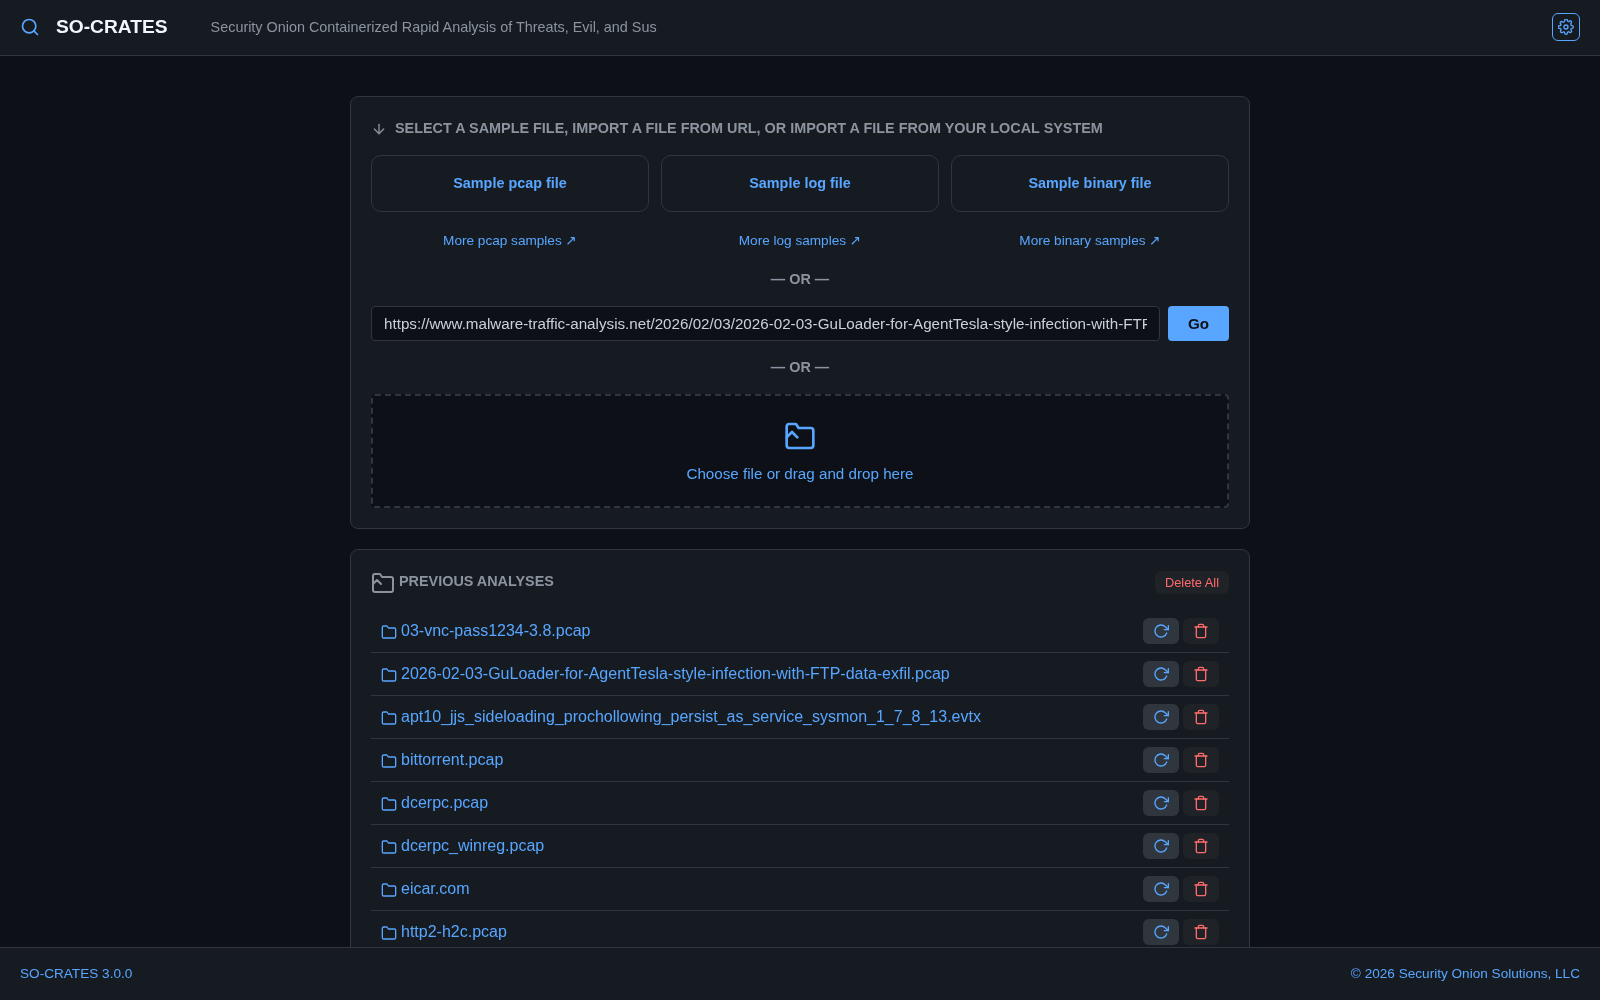 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
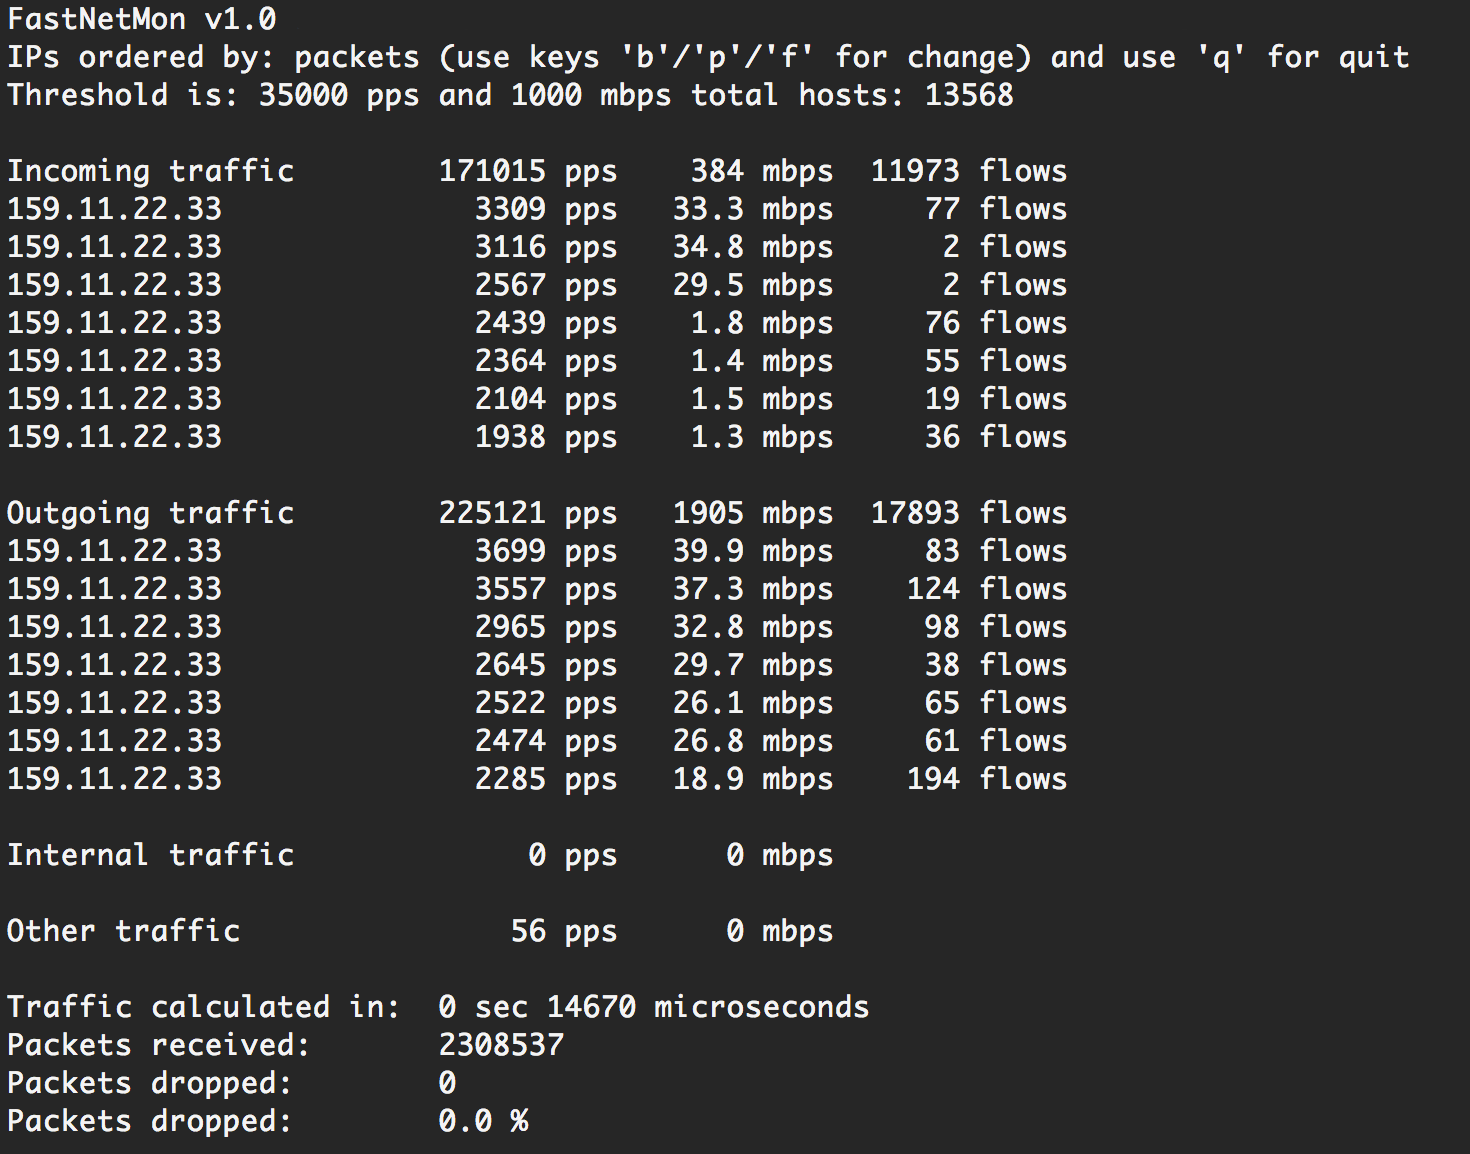 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
 adversarial-detection-engineering/adversarial-detection-engineering-framework
A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 fenkohq/dnsmonster
Passive DNS Capture and Monitoring Toolkit