
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
153 results
ALEAPP preview

ALEAPP

GitHubabrignoni/aleapp

Android Logs Events And Protobuf Parser
digital-forensicsincident-responselog-analysis+1
9353h 9m ago
detection-rules preview

detection-rules

GitHubelastic/detection-rules

Develop, validate, and publish SIEM detection rules for Elastic Security, with Python CLI tooling, KQL parsing, Kibana integration, and packaged…
anomaly-detectioncurated-resourcesdefensive-tools+3
2.7k8h 46m ago
iLEAPP preview

iLEAPP

GitHubabrignoni/ileapp

Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
digital-forensicsforensicsincident-response+3
1.3k9h 46m ago
OmniTriage preview

OmniTriage

GitHubprox0959/omnitriage

Zero-dependency, sub-second Windows live digital forensics & incident response (DFIR) triage engine for USB responders.

defensive-toolsdigital-forensicsforensics+8
114h 54m ago
maltrail preview

maltrail

GitHubstamparm/maltrail

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k16h 30m ago
evtx preview

evtx

GitHubomerbenamram/evtx

A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
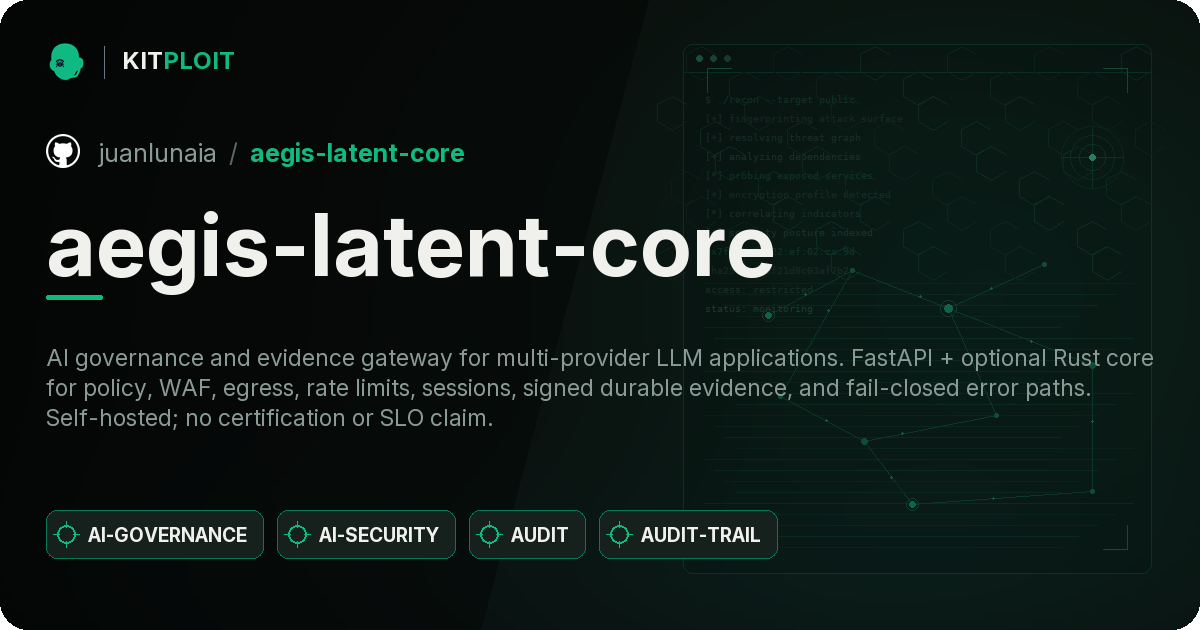
digital-forensicsforensicsincident-response+1
9661 day ago
aegis-latent-core preview

aegis-latent-core

GitHubjuanlunaia/aegis-latent-core

AI governance and evidence gateway for multi-provider LLM applications. FastAPI + optional Rust core for policy, WAF, egress, rate limits, sessions,…
ai-securityapi-securitycloud-security+3
181 day ago
ddos-reduction-system preview

ddos-reduction-system

GitHubdevinblack001/ddos-reduction-system

Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
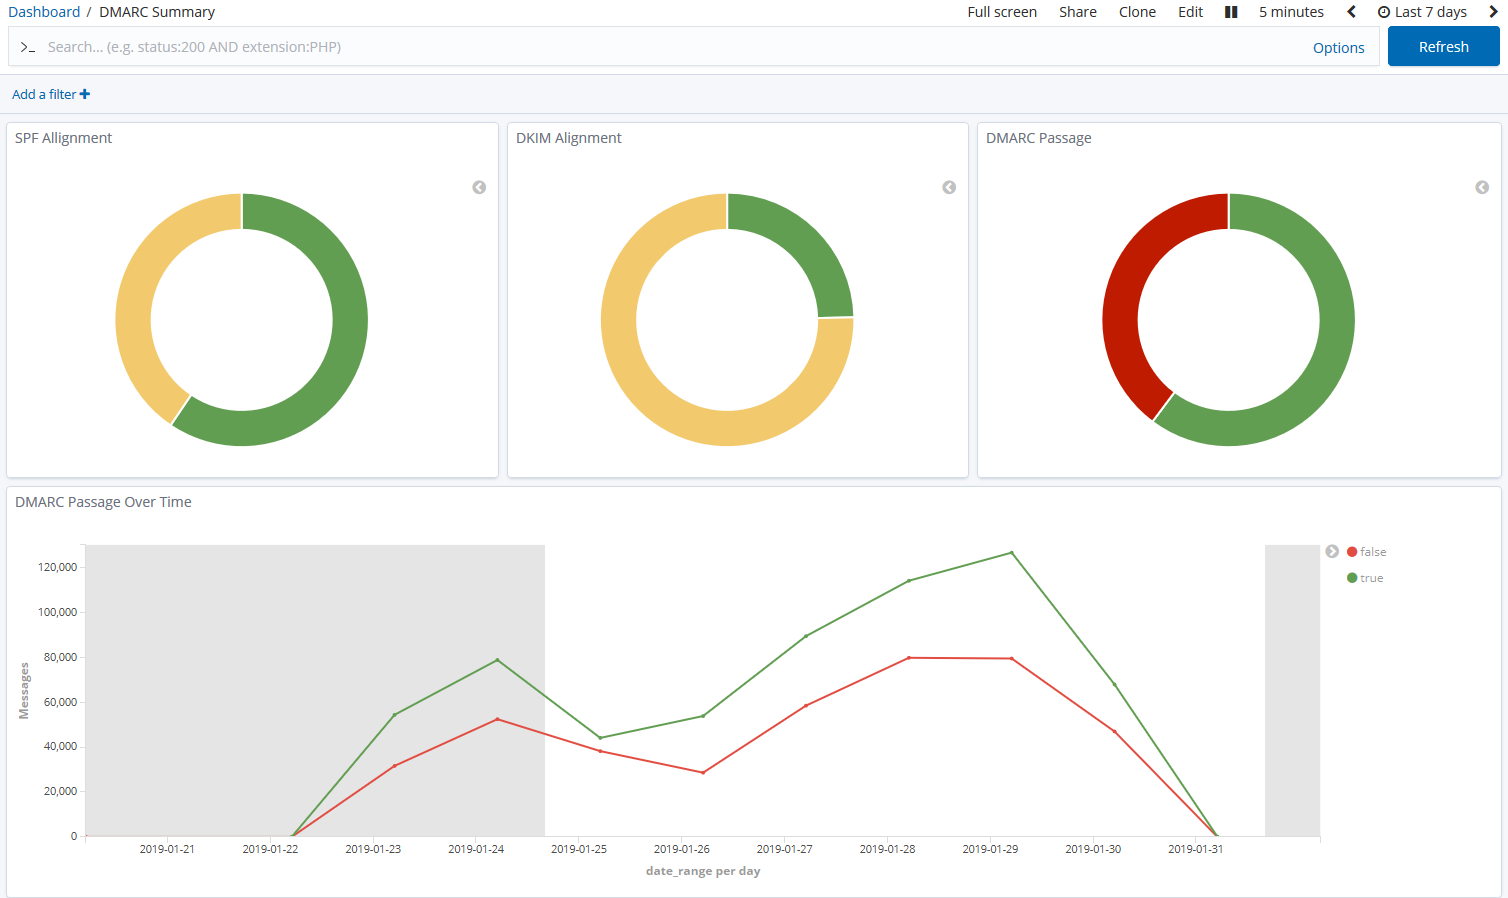
anomaly-detectiondefensive-toolsincident-response+6
21 day ago
parsedmarc preview

parsedmarc

GitHubdomainaware/parsedmarc

A Python package and CLI for parsing aggregate and forensic DMARC reports
authenticationdefensive-toolsdns-analysis+2
1.3k1 day ago
ubuntils preview

ubuntils

GitHubasmitdesai/ubuntils

Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…

configuration-auditingdefensive-toolsdigital-forensics+7
11 day ago
pySigma preview

pySigma

GitHubsigmahq/pysigma

Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
defensive-toolsintrusion-detectionlog-analysis+2
5972 days ago
ecs-templates preview

ecs-templates

GitHubcorelight/ecs-templates

Corelight or Zeek Elastic Common Schema Templates

log-analysisnetwork-securityutilities-frameworks
92 days ago
msticpy preview

msticpy

GitHubmicrosoft/msticpy

Microsoft Threat Intelligence Security Tools
anomaly-detectioncloud-securityeducation+6
2.0k3 days ago
defenseclaw preview

defenseclaw

GitHubcisco-ai-defense/defenseclaw

Security Governance for Agentic AI
ai-securitycloud-securitycode-analysis+7
8514 days ago
meshyface preview

meshyface

GitHubjaronmcd/meshyface

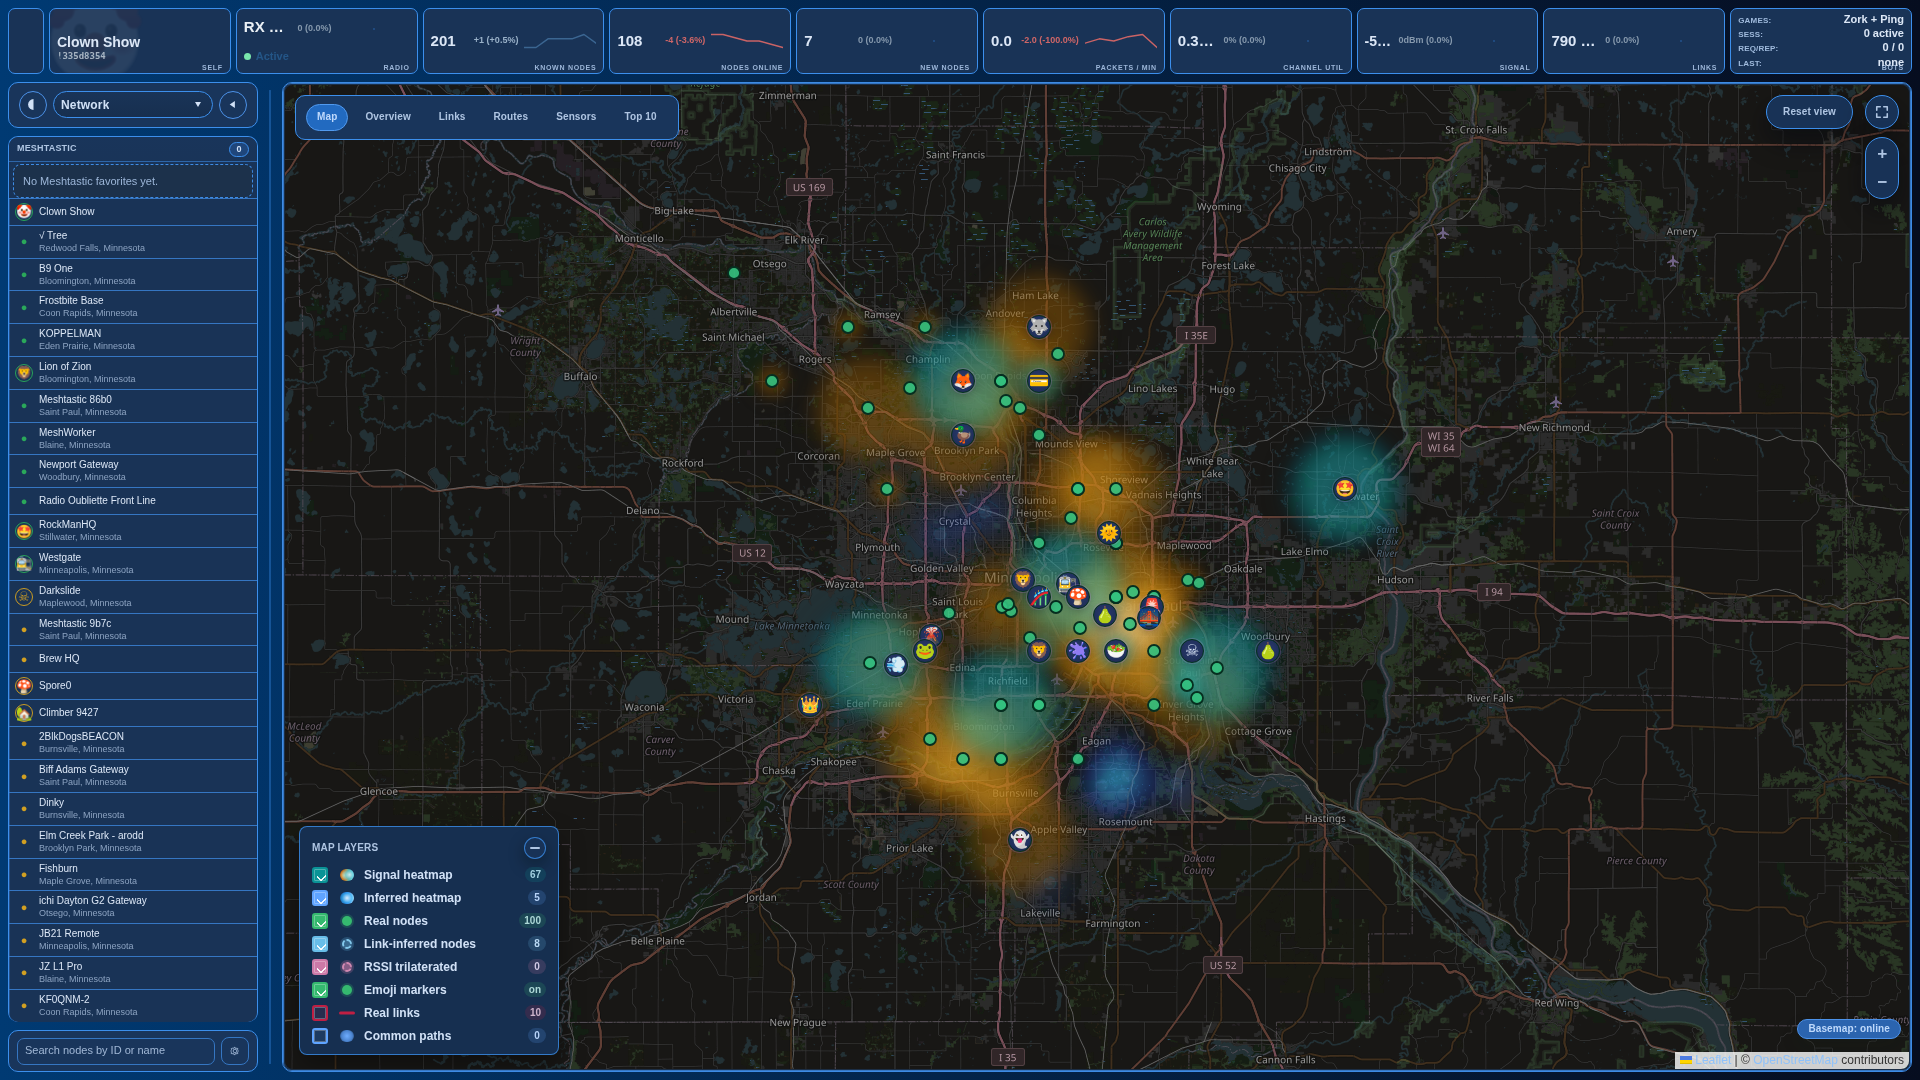
Single-page web dashboard for Meshtastic mesh networks with live network mapping, packet analysis, chat, sensor telemetry, and topology…

dns-analysisinformation-gatheringiot-security+4
1264 days ago
EntraTrace preview

EntraTrace

GitHubbert-janp/entratrace

Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
authenticationcloud-securitydefensive-tools+5
544 days ago
SSHintel preview

SSHintel

GitHubsonitbahl/sshintel

Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.

incident-responseintrusion-detectionlog-analysis+2
34 days ago
third-thoughts preview

third-thoughts

GitHublightless-labs/third-thoughts

Research toolkit for analyzing AI agent behavioral patterns through multi-disciplinary corpus analysis. Parses session logs, runs 23 analytical…

ai-securityanomaly-detectioncurated-resources+5
34 days ago
Previous12…9Next