
ndaal_public_auditd
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…

Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…

Read-only check of every WordPress core version on a server. Flags CVE-2026-87902 (fixed in 7.1.2 and backports), auto-updates turned off, and…

Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…

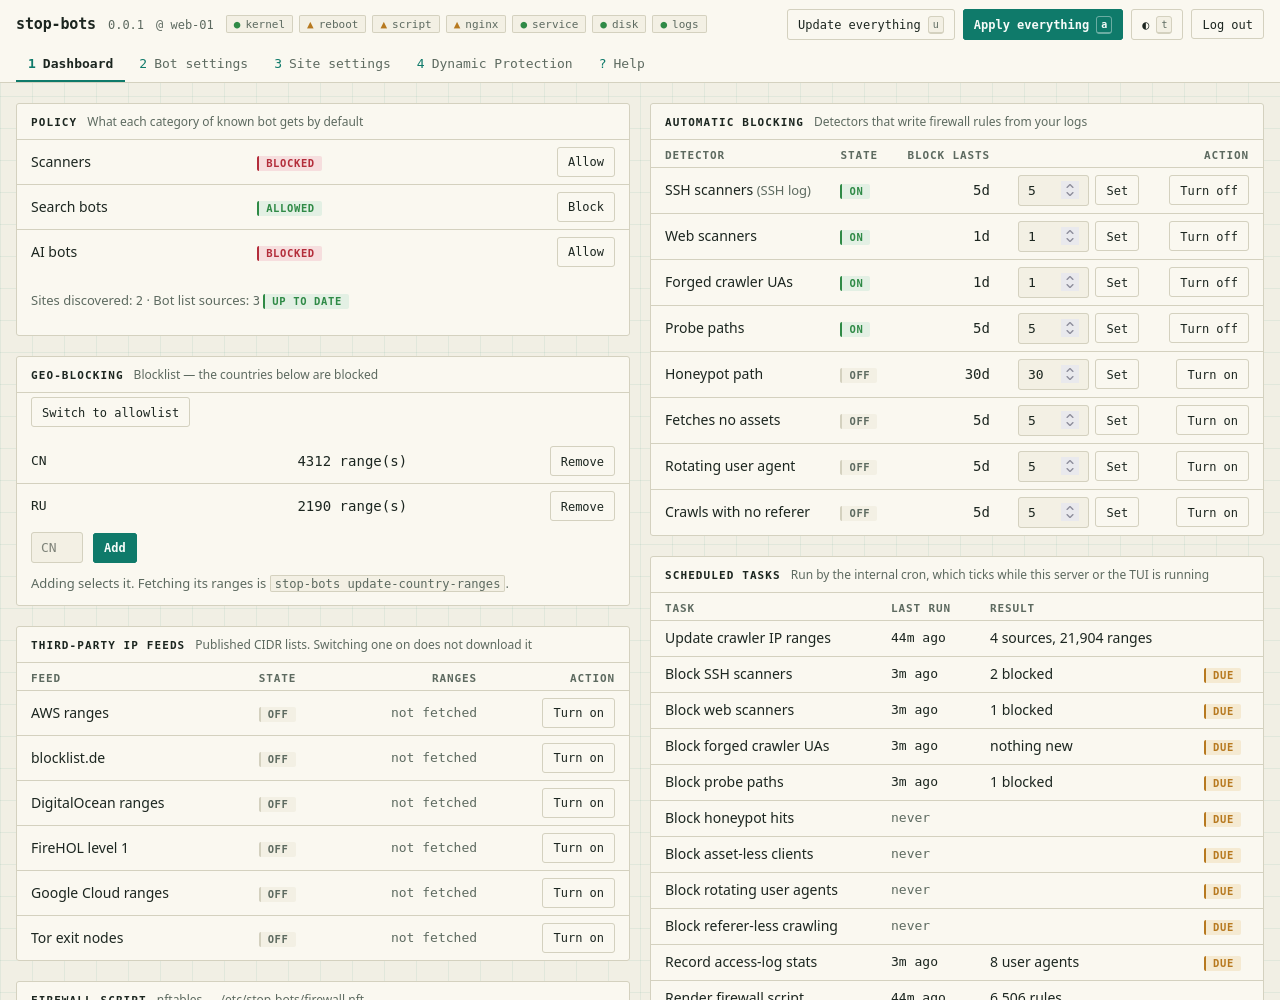
Automate stopping bad bots from accessing your server

Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…

#PaperCut CVE-2026-81578 + CVE-2026-82078 Defense Toolkit 2 3 A **defensive** toolkit to check and understand exposure to the chained

Monitors Windows Security logs for failed RDP attempts and automatically blocks abusive IPs via Windows Firewall, with configurable thresholds and…

Multi-OS vulnerability checker for CVE-2026-31431 (Linux kernel) and CVE-2026-41940 (cPanel)

Форензика после CVE-2026-41940 (cPanel/WHM) — bash-скрипт и чек-лист

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

The Intelligent Process Lifecycle of Active Cyber Defenders

A curated list of awesome Security Hardening techniques for Windows.

CY376 Blue Team project — pfSense DMZ, Suricata IDS/IPS, and automated host hardening against CVE-2014-6271

A really simple Nessus results library

Easy automated vulnerability scanning, reporting and analysis

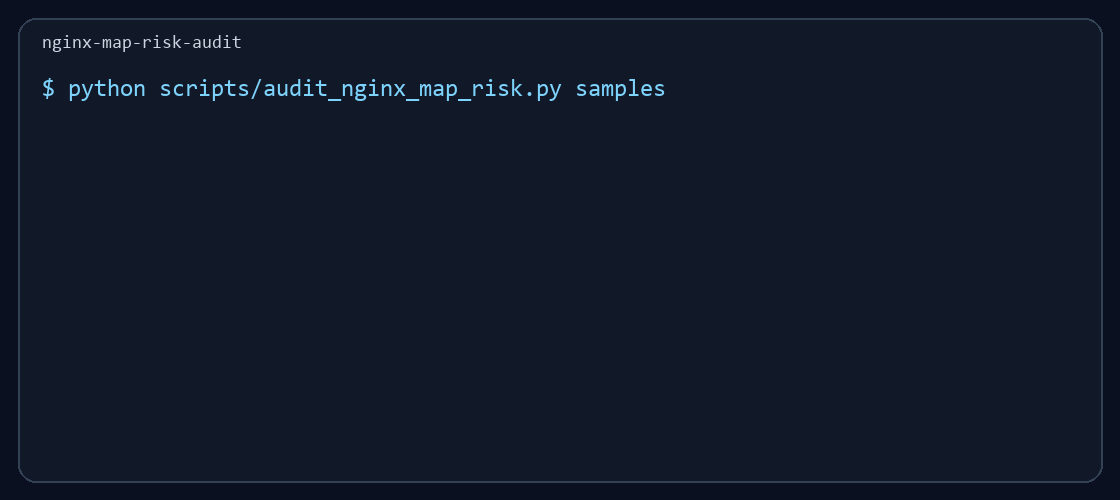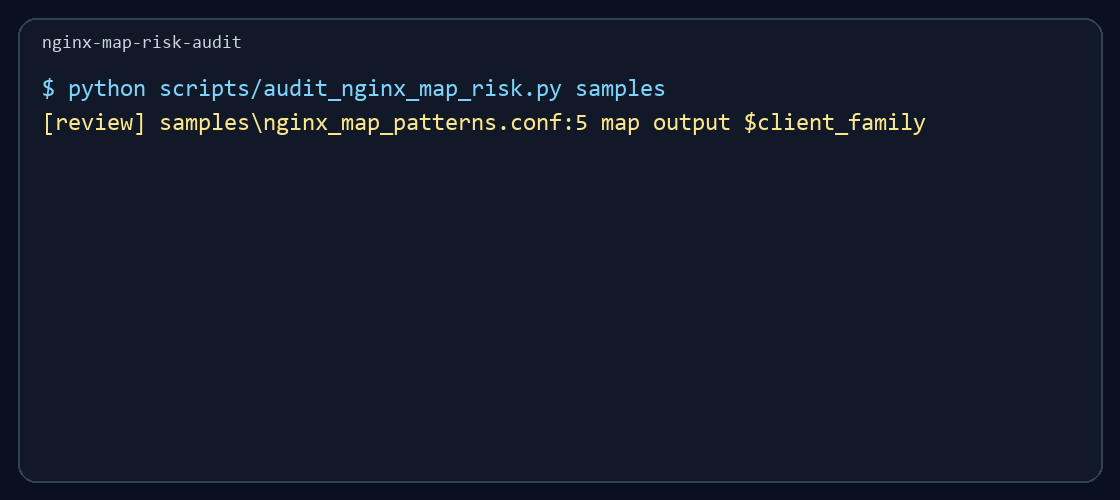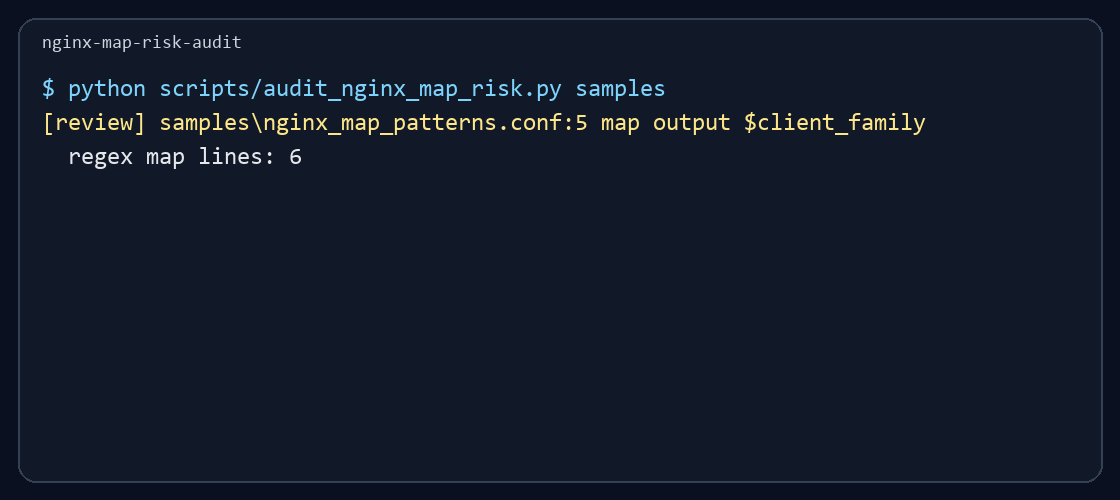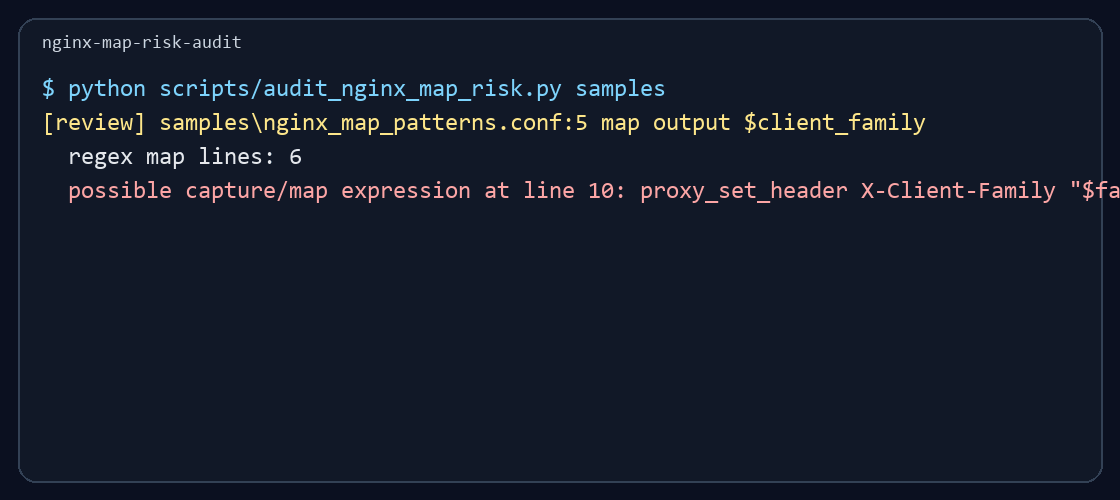
Defensive NGINX CVE-2026-42533 map regex risk audit with config scanner, Splunk/Defender notes, and lab evidence.

Audit Preference Pane and Log Reader for OS X

Prometheus Firewall Analyzer