

detecttrace
 g0dse11/detecttrace
Open-source detection engineering tool that traces security detections end to end and identifies the first failing stage.
defensive-toolsdevsecopsincident-response+5
1
g0dse11/detecttraceOpen-source detection engineering tool that traces security detections end to end and identifies the first failing stage.
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
 gmh5225/jataayu
LLM-backed AI agent security — inbound injection detection + outbound privacy protection
 tuskira/ai-agent-gateway
Open-source gateway that secures, governs, and observes AI agents' MCP tool calls and LLM traffic, with API-key authentication and an admin console…
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
 adarsh14734/aegis-releases
Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…
 falconforceteam/falcondash
Azure workbook dashboard that visualizes and explores detection performance metrics, helping security teams measure and proactively maintain their…
 icemoonhsv/tats
Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
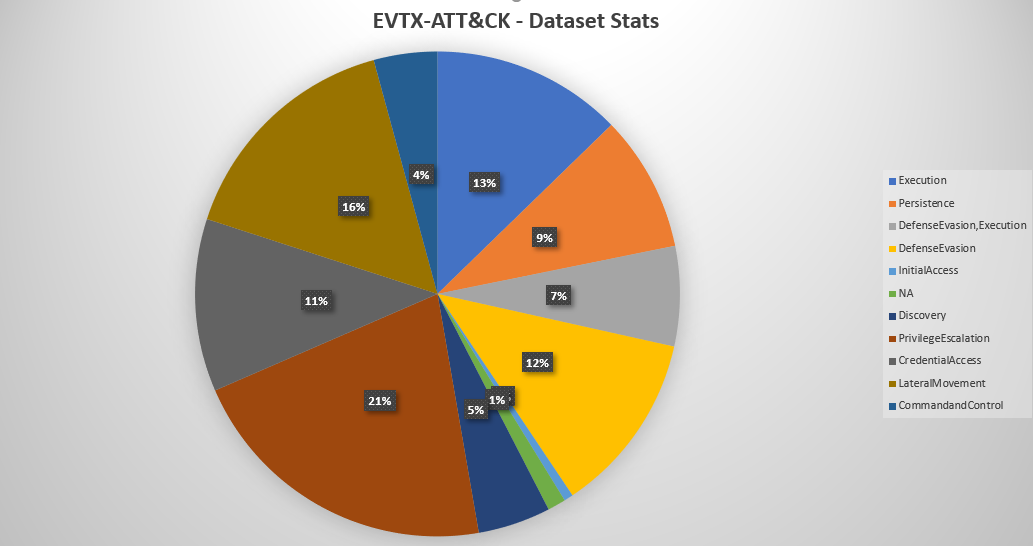 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
 eshlomo1/microsoft-sentinel-secops
SOC operations content for Microsoft Sentinel, including hunting queries, incident response playbooks, and security event analysis for Azure cloud…
 juanlunaia/aegis-latent-core
Self-hosted evidence gateway for AI systems: fail-closed policy, WAF, egress controls, signed durable MMR proofs, and offline verification across LLM…
 unfold-security/cve-2026-41940-detection
Detection signatures for CVE-2026-41940 and shemas for cPanel logs
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 letlaka/redsun-bluehammer-undefend-detection-pack
Microsoft Defender XDR KQL detections for RedSun, BlueHammer, UnDefend, and CVE-2026-33825-related Defender abuse behaviors.
 kreotic/sentrygrid
ML-driven threat detection and continuous monitoring platform built for federal zero trust architectures.
 kyos-public/keycloak-cve-2026-18963-hunt
Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database