

TATS
 icemoonhsv/tats
Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
authenticationidentity-access-managementlog-analysis+2
7
icemoonhsv/tatsAnalyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
 s0/rsyslog-librelp-cve-2018-1000140
Pinned version of rsyslov vulnerable to CVE-2018-1000140
 wattocyber/masq
Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
 nccgroup/burp-reflux
Burp proxy text log converter to CSV and SQLLite
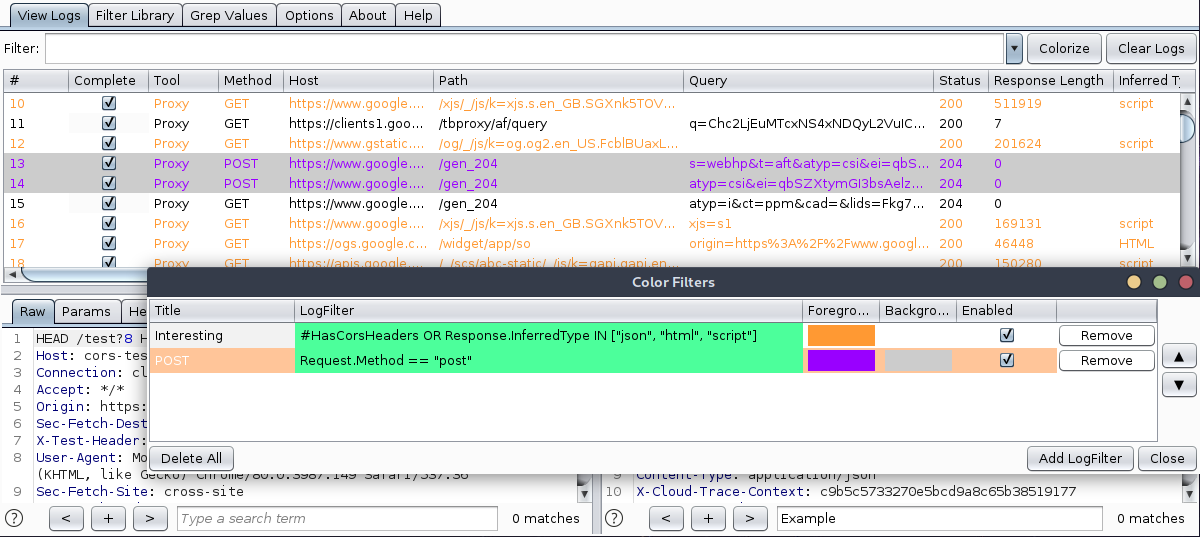 nccgroup/loggerplusplus
Advanced Burp Suite Logging Extension
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 viliuskraujutis/androidbroadcastsmonitor
A tool to subscribe to receive all standard Android broadcasts on your Android device.
 kvasirsecurity/kvasir
Kvasir: Penetration Test Data Management
 olafhartong/bamboozledr
A comprehensive ETW (Event Tracing for Windows) event generation tool designed for testing and research purposes.
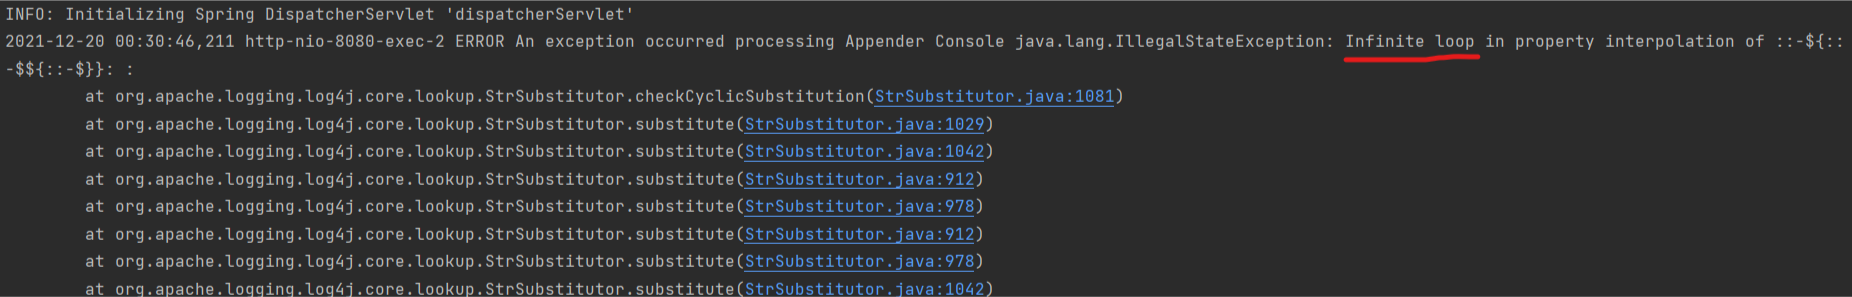 tejas-nagchandi/cve-2021-45105
Replicating CVE-2021-45105
 wdahlenburg/cve-2022-38725
Proof of Concept for CVE-2022-38725 against syslog-ng
 karmanyat28/multi-stage-exploitation-and-detection-engineering-analysis-of-cve-2023-34362-in-moveit-transfer
This repository contains an academic and technical analysis of CVE-2023-34362, a critical SQL injection vulnerability affecting the MOVEit Transfer…
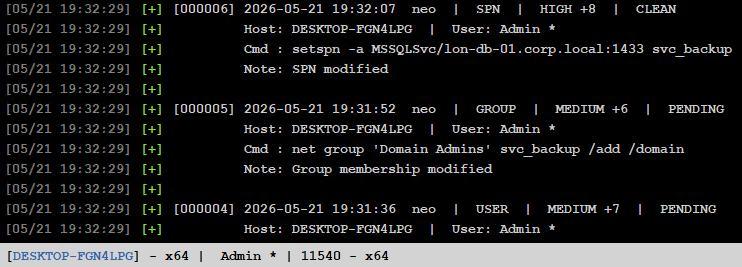 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
 guillaumepetit84/cve-2020-35488
Proof-of-concept exploit for CVE-2020-35488, a denial-of-service vulnerability in NXLOG Community Edition via crafted syslog payloads causing…
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
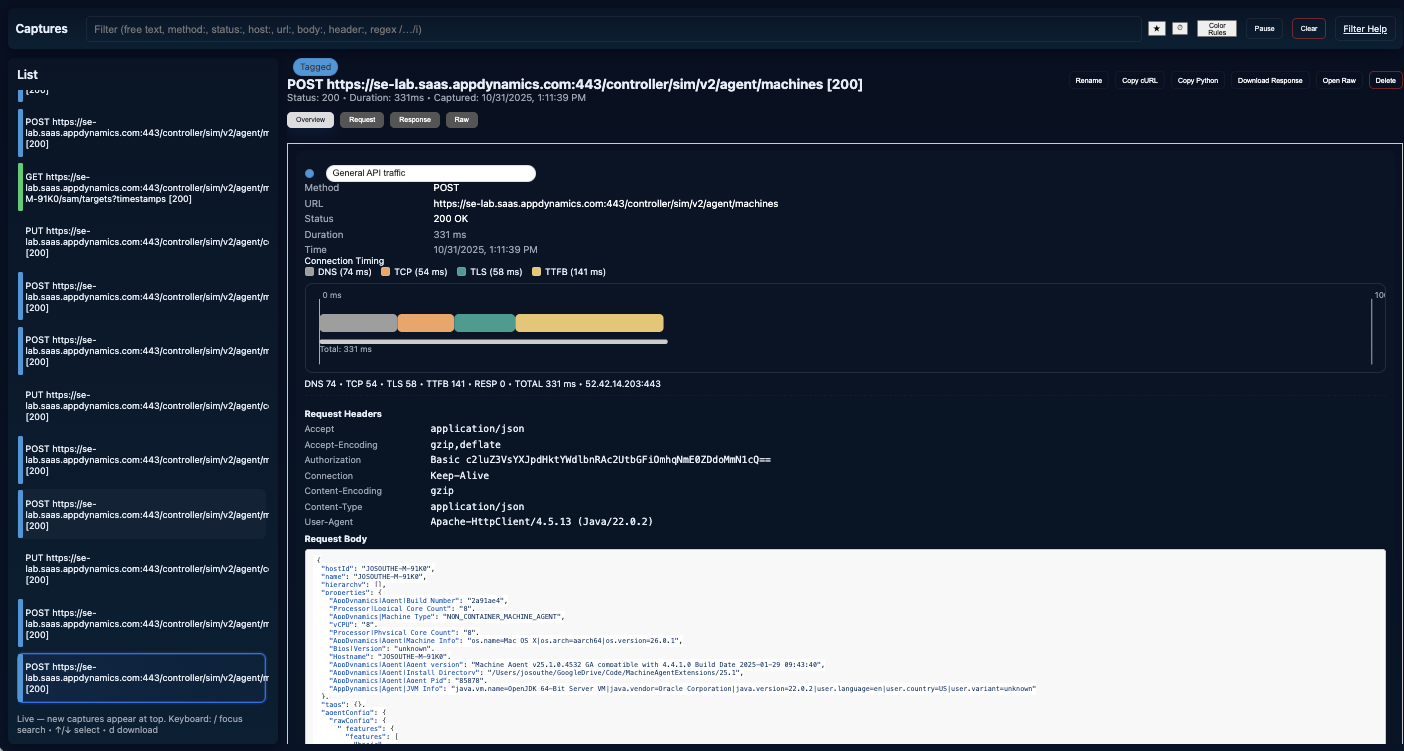 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
 bfurkanyildiz/android-rce-analizi
Android CVE-2024-0044, 43093, 23706 zafiyet analizi ve PoC lab ortamı
 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI