loki
 grafana/loki
Horizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
general-purpose-utilitiesincident-responselog-analysis+1
29.0k
grafana/lokiHorizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 v1d1an/s1em
This project is a SIEM with SIRP and Threat Intel, all in one.
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
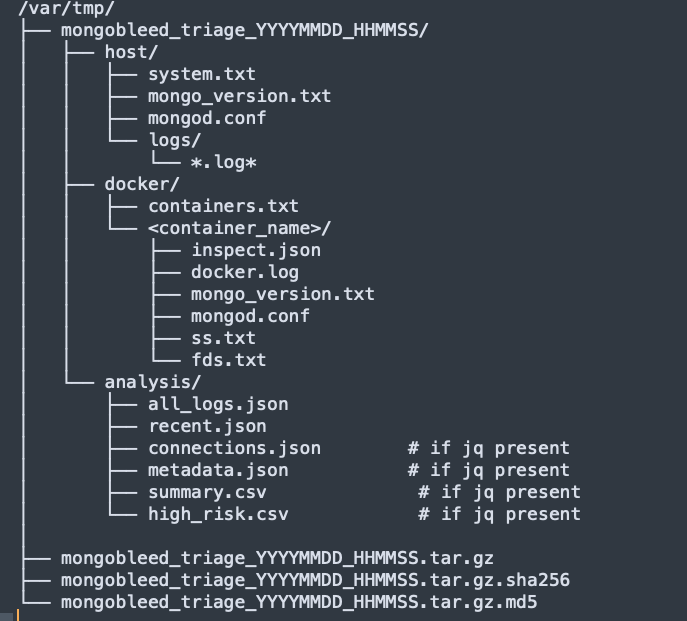 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
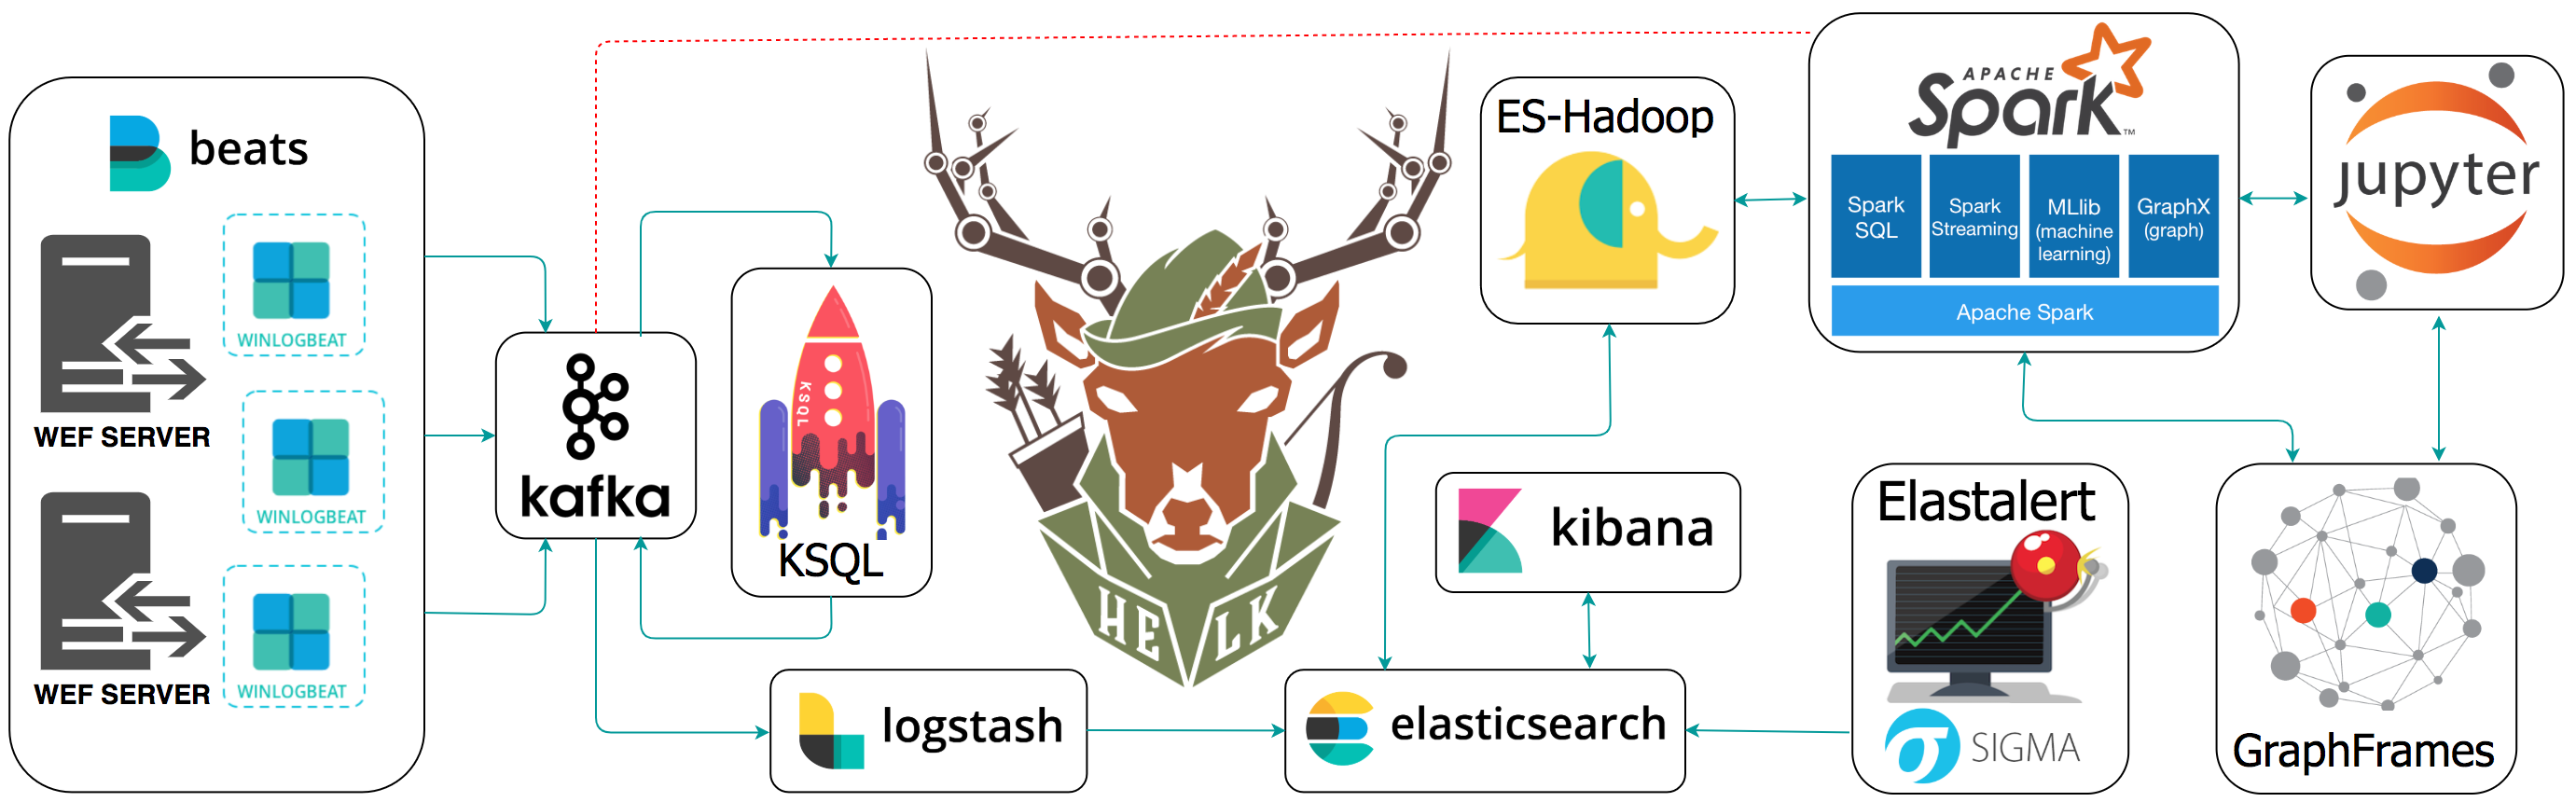
 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 ossie-git/log4shell_sentinel
A Smart Log4Shell/Log4j/CVE-2021-44228 Scanner
 kunai-project/kunai
eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 ait-aecid/logdata-anomaly-miner
This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…