
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
307 results
loki preview

loki

GitHubgrafana/loki

Horizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
general-purpose-utilitiesincident-responselog-analysis+1
28.9k
7h 16m ago
Dshell preview

Dshell

GitHubusarmyresearchlab/dshell

Dshell is a network forensic analysis framework.

digital-forensicsdns-analysisforensics+3
5.5k2 years ago
zeek preview

zeek

GitHubzeek/zeek

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

anomaly-detectionanti-botdefensive-tools+14
8.0k14h 32m ago
kubeshark preview

kubeshark

GitHubkubeshark/kubeshark

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…

ai-securitycloud-infrastructure-securitycloud-security+9
12.1k5 days ago
suricata preview

suricata

GitHuboisf/suricata

Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
anomaly-detectionanti-botdefensive-tools+9
6.6k1 month ago
deadair preview

deadair

GitHubbig-comfy/deadair

Finds the detection rules in your SIEM that are running blind
configuration-auditinglog-analysisvulnerability-analysis
229 days ago
ThreatHound preview

ThreatHound

GitHubmazx0p/threathound

Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
digital-forensicsincident-responselog-analysis+1
1602 years ago
pastokrapacefleciks preview

pastokrapacefleciks

GitHubnu11secur1ty/pastokrapacefleciks

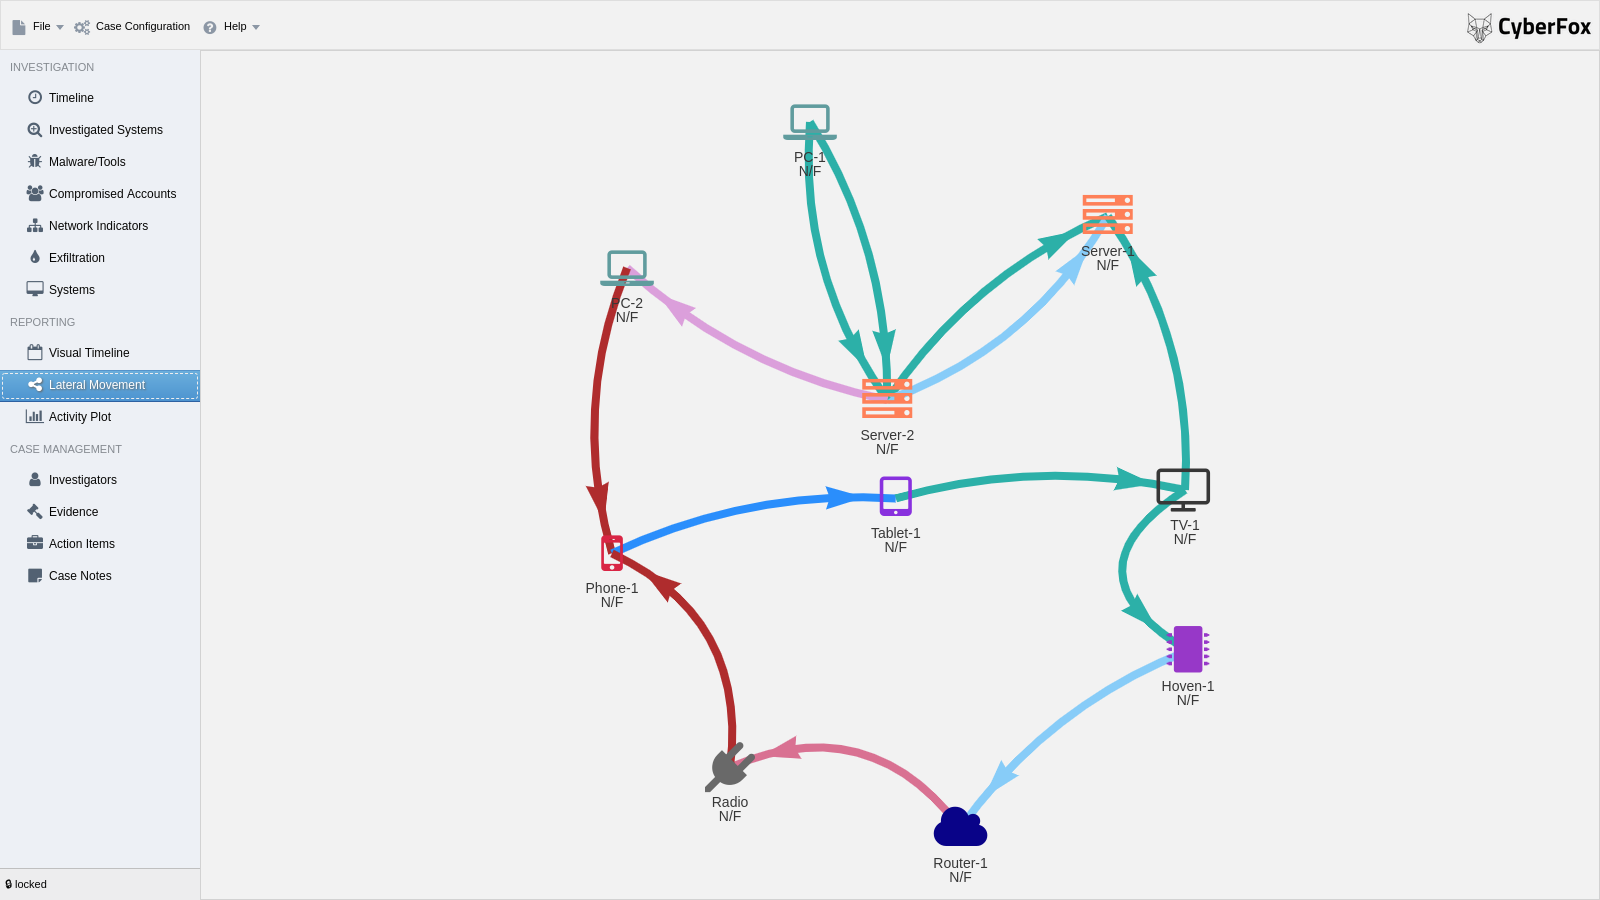
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
digital-forensicsforensicslog-analysis+2
22 days ago
Aurora-Incident-Response preview

Aurora-Incident-Response

GitHubcyb3rfox/aurora-incident-response

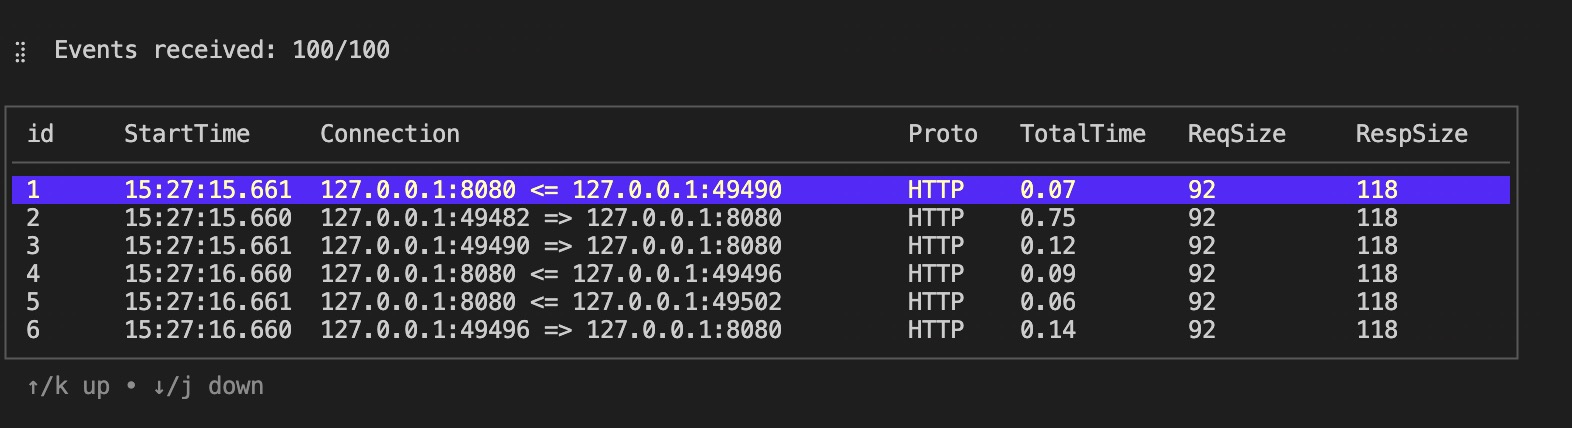
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
digital-forensicsforensicsincident-response+3
1.1k3 years ago
kyanos preview

kyanos

GitHubhengyoush/kyanos

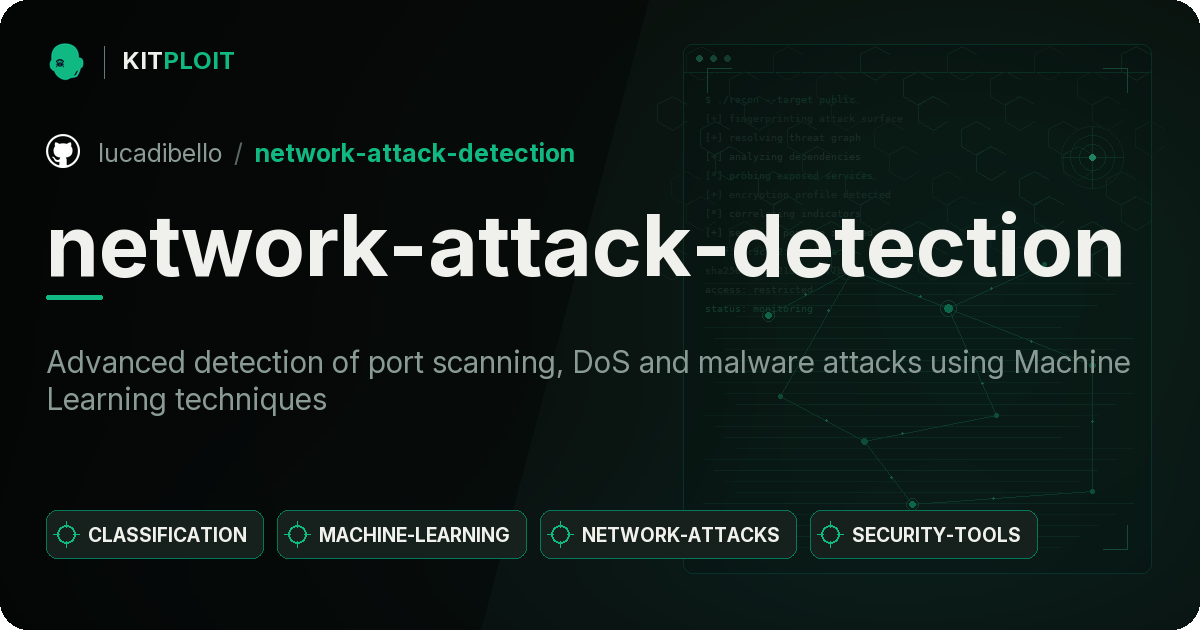
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
dns-analysisdynamic-analysis-sandboxinglog-analysis+3
5.1k3 months ago
network-attack-detection preview

network-attack-detection

GitHublucadibello/network-attack-detection

Advanced detection of port scanning, DoS and malware attacks using Machine Learning techniques
anomaly-detectioneducationinformation-gathering+5
133 years ago
SuricataLog preview

SuricataLog

GitHubjosevnz/suricatalog

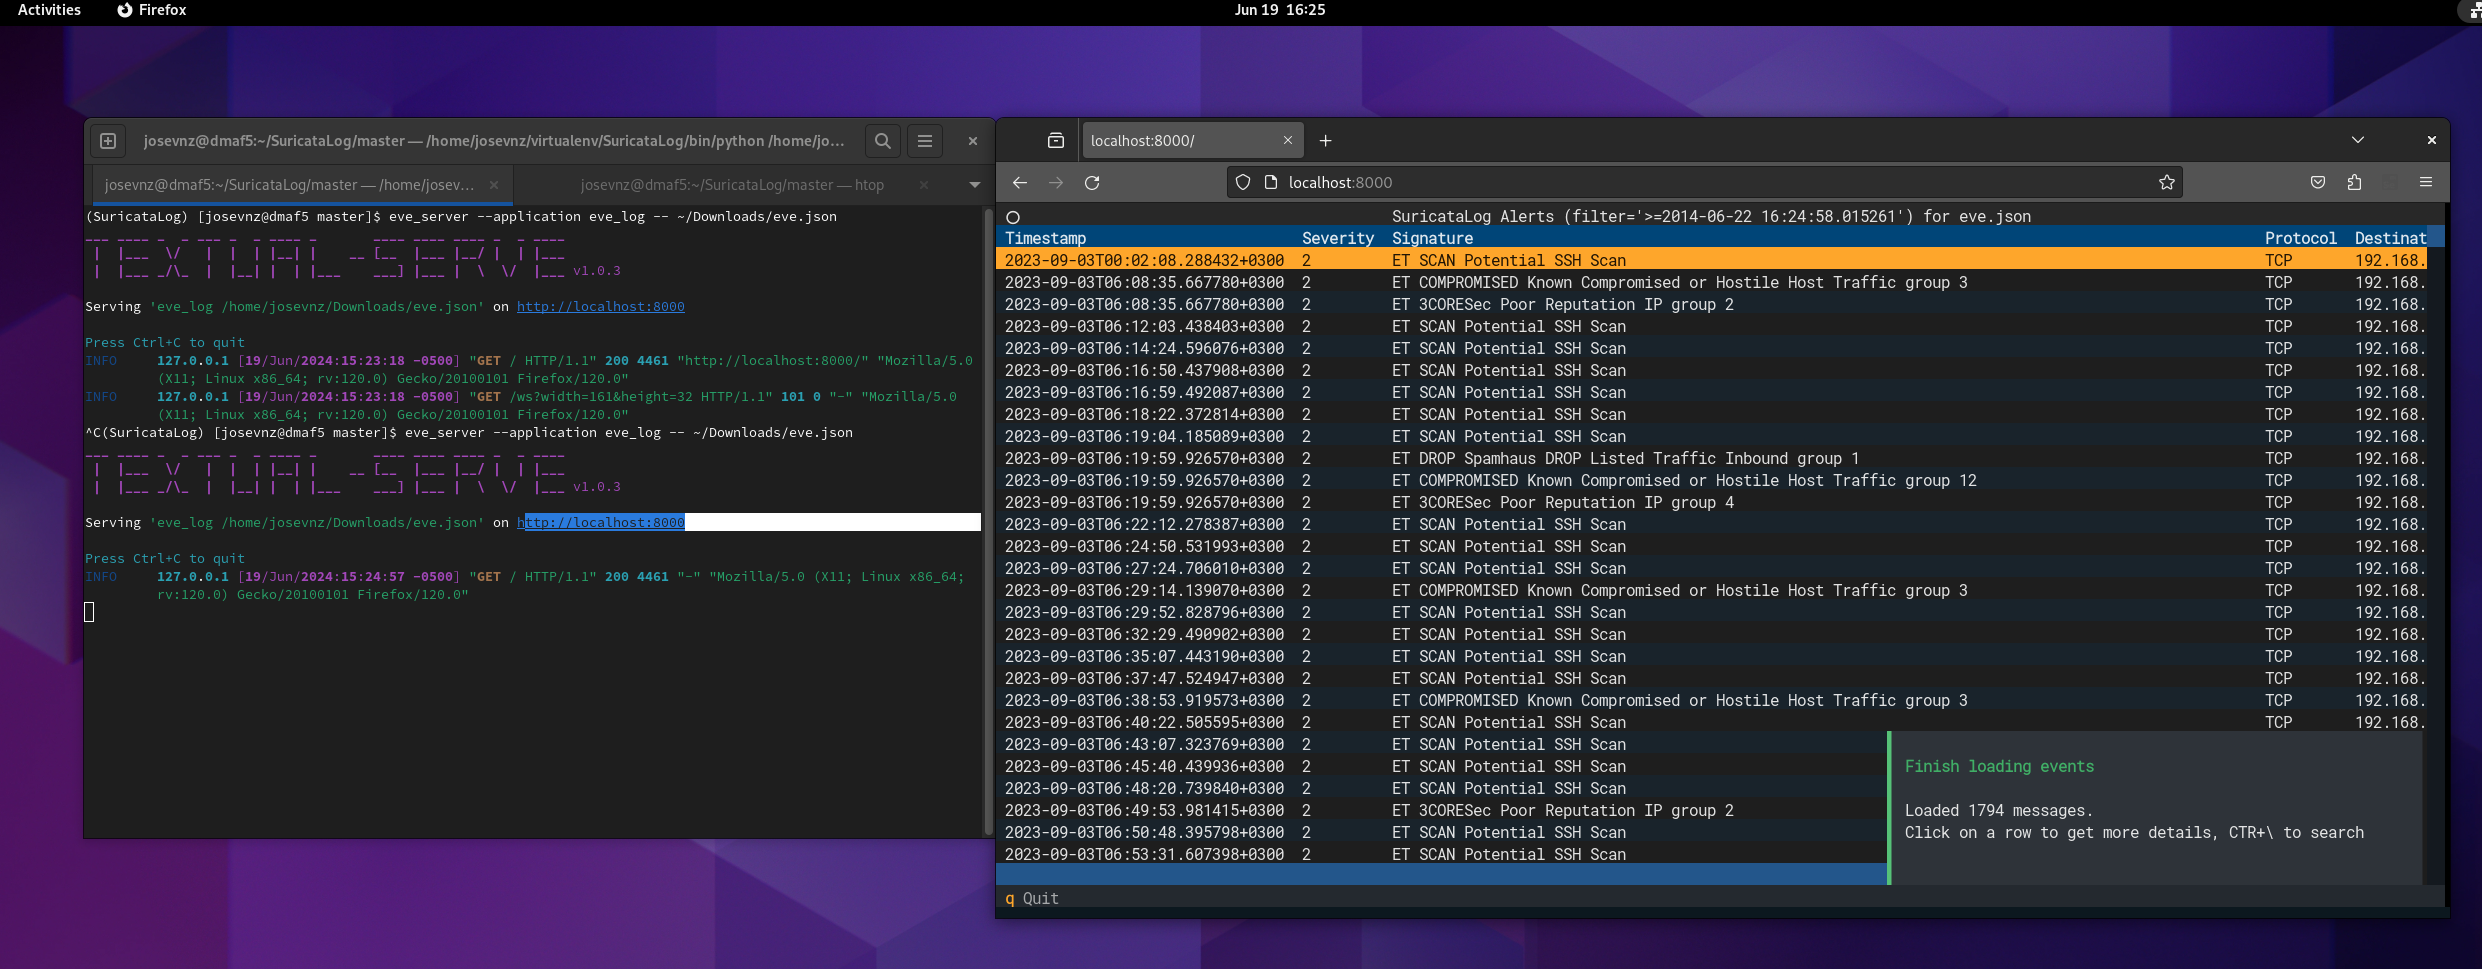
Parse, filter, and visualize Suricata eve.json logs with CLI tools for alerts, flows, DNS, and payloads. Includes a tutorial for learning Suricata…
educationintrusion-detectionlog-analysis+1
271 month ago
IfritProxy preview

IfritProxy

GitHub0tsystemspublicrepos/ifritproxy

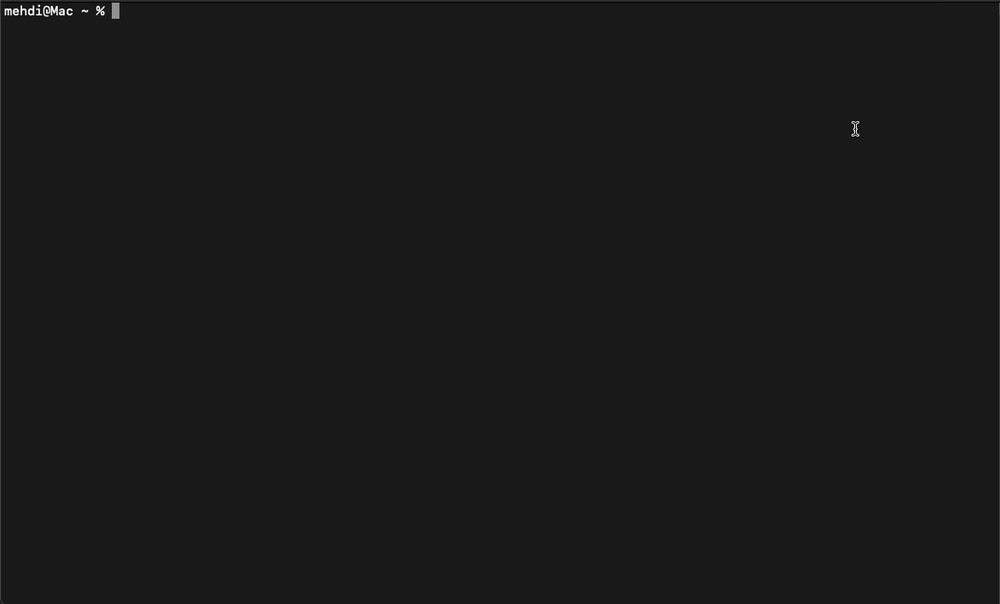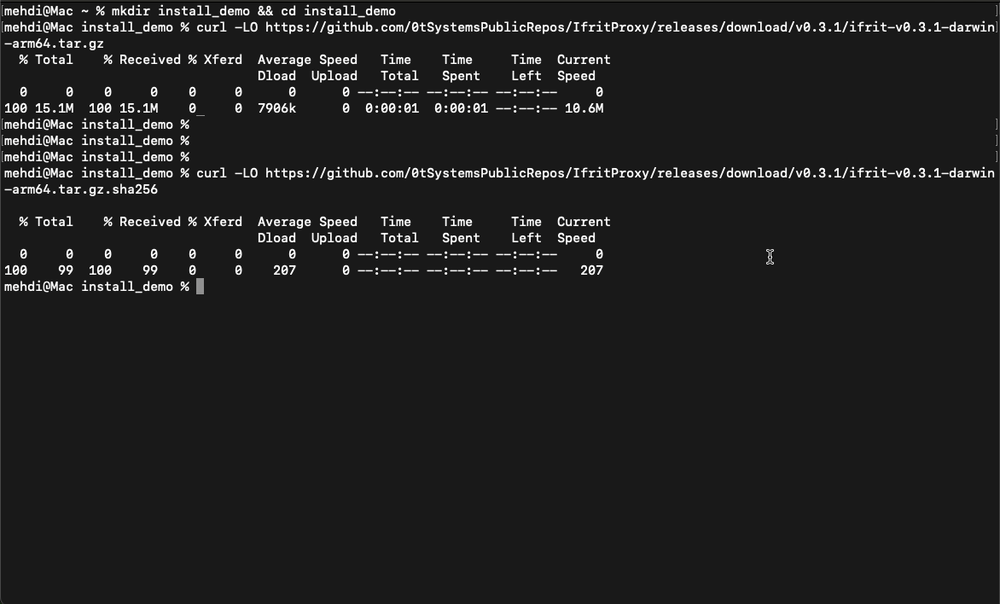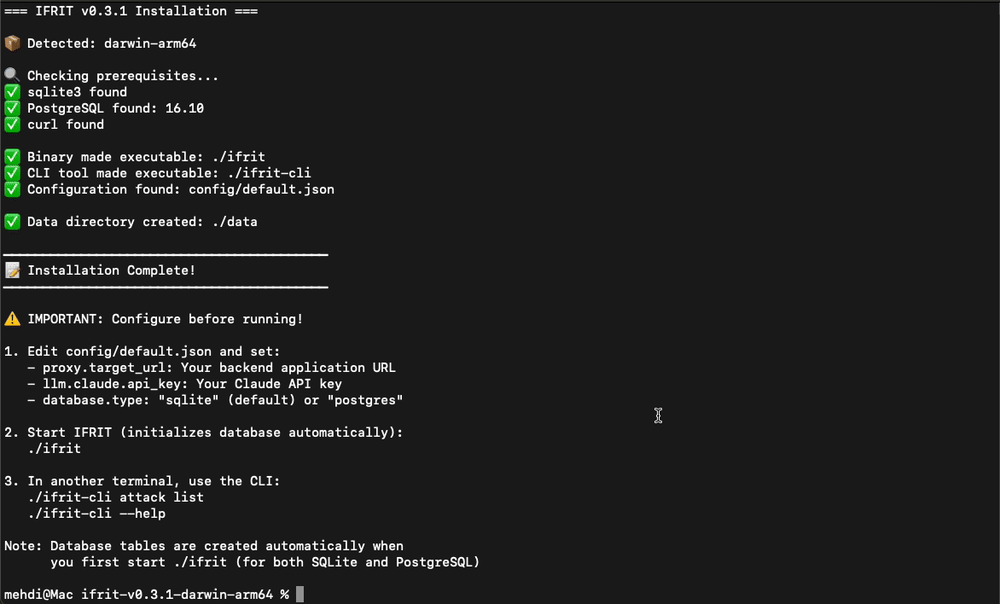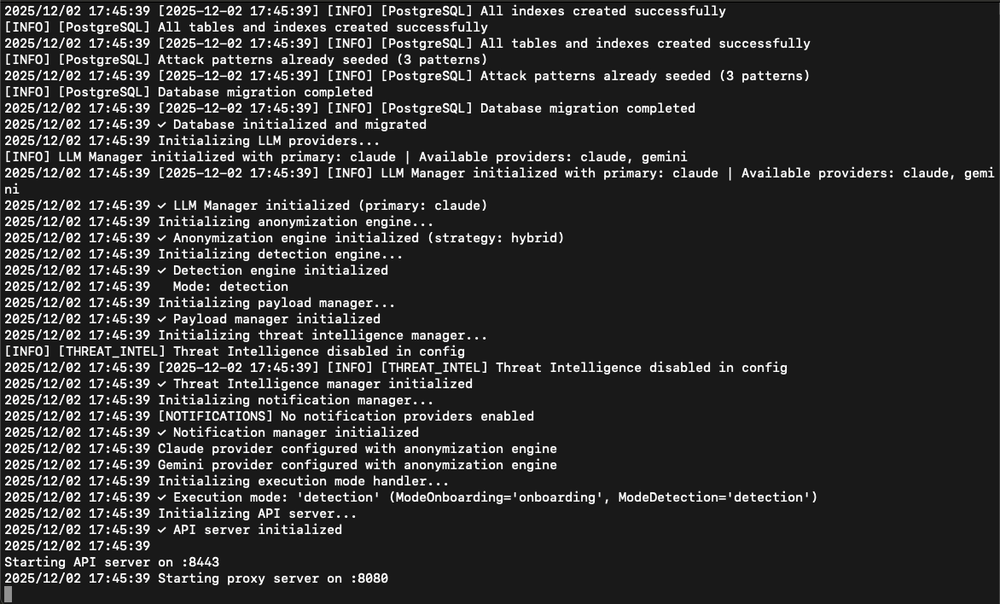
IFRIT is an AI-powered reverse proxy that intercepts incoming requests in real time, classifying each one as legitimate or malicious. Legitimate…
ai-securitydefensive-toolsids-ips-evasion+7
17 months ago
SOC274---Palo-Alto-Networks-PAN-OS-Command-Injection-Vulnerability-Exploitation-CVE-2024-3400- preview

SOC274---Palo-Alto-Networks-PAN-OS-Command-Injection-Vulnerability-Exploitation-CVE-2024-3400-

GitHubcyberbibs/soc274---palo-alto-networks-pan-os-command-injection-vulnerability-exploitation-cve-2024-3400-

Step-by-step SOC analyst walkthrough for investigating and remediating CVE-2024-3400 (PAN-OS command injection). Covers detection, log analysis,…

digital-forensicseducationincident-response+6
1 year ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
digital-forensicsdisk-forensicsforensics+6
8113 months ago
aegis-latent-core preview

aegis-latent-core

GitHubjuanlunaia/aegis-latent-core

AI governance and evidence gateway for multi-provider LLM applications. FastAPI + optional Rust core for policy, WAF, egress, rate limits, sessions,…
ai-securityapi-securitycloud-security+3
176 days ago
CyberDefense-Lab preview

CyberDefense-Lab

GitHubumidguluzada/cyberdefense-lab

A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
educationids-ips-evasionintrusion-detection+5
628 days ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

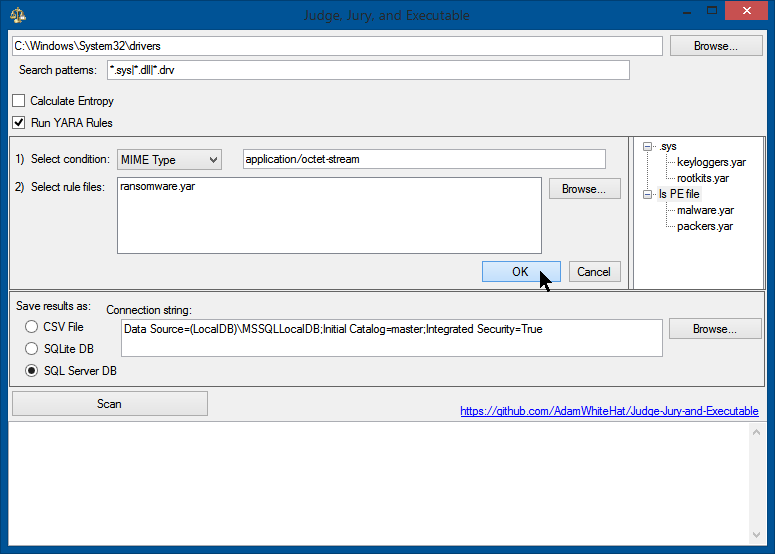
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

database-securitydigital-forensicsdisk-forensics+8
855 months ago
Previous12…18Next