Purple-Team-Automation

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…

Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…

Catch what's lurking in your Kafka clusters.

Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…

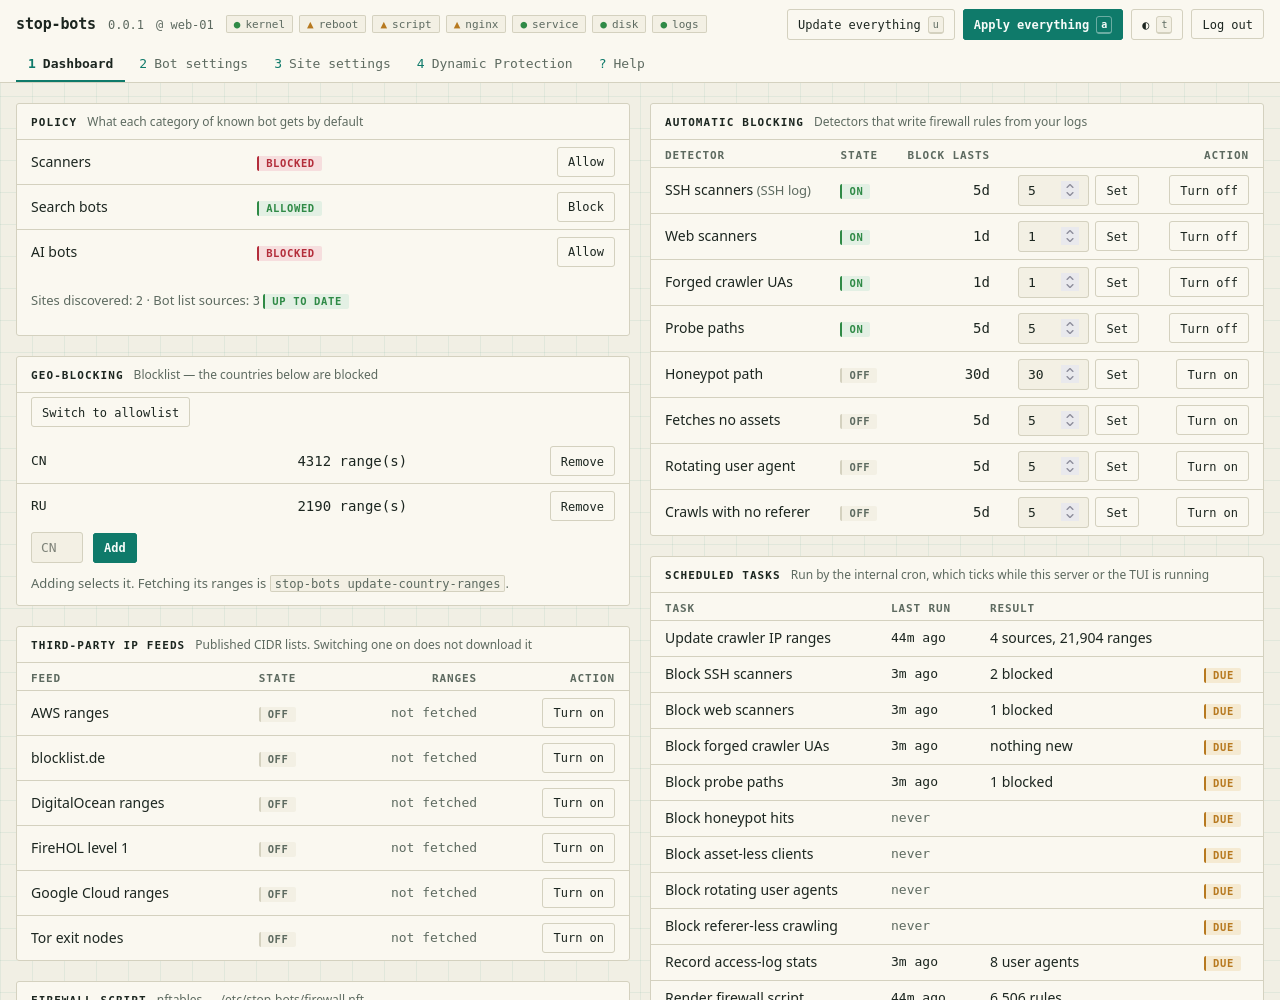
Automate stopping bad bots from accessing your server

🍯 T-Pot - The All In One Multi Honeypot Platform 🐝

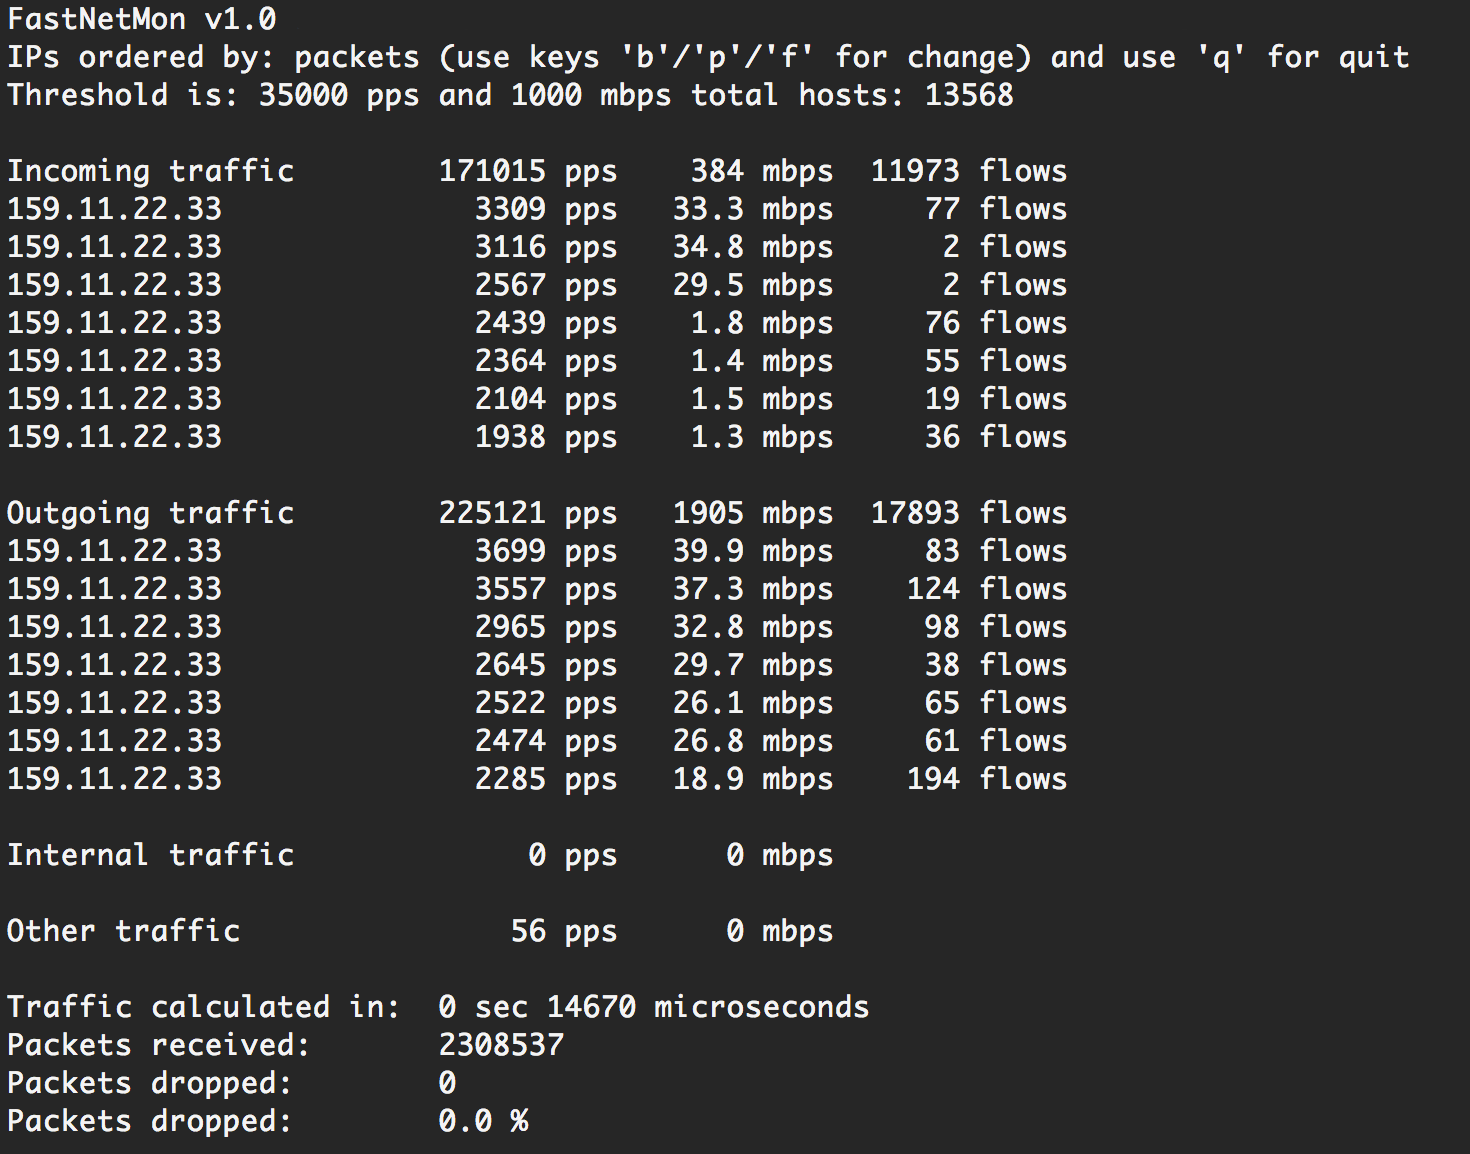
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support

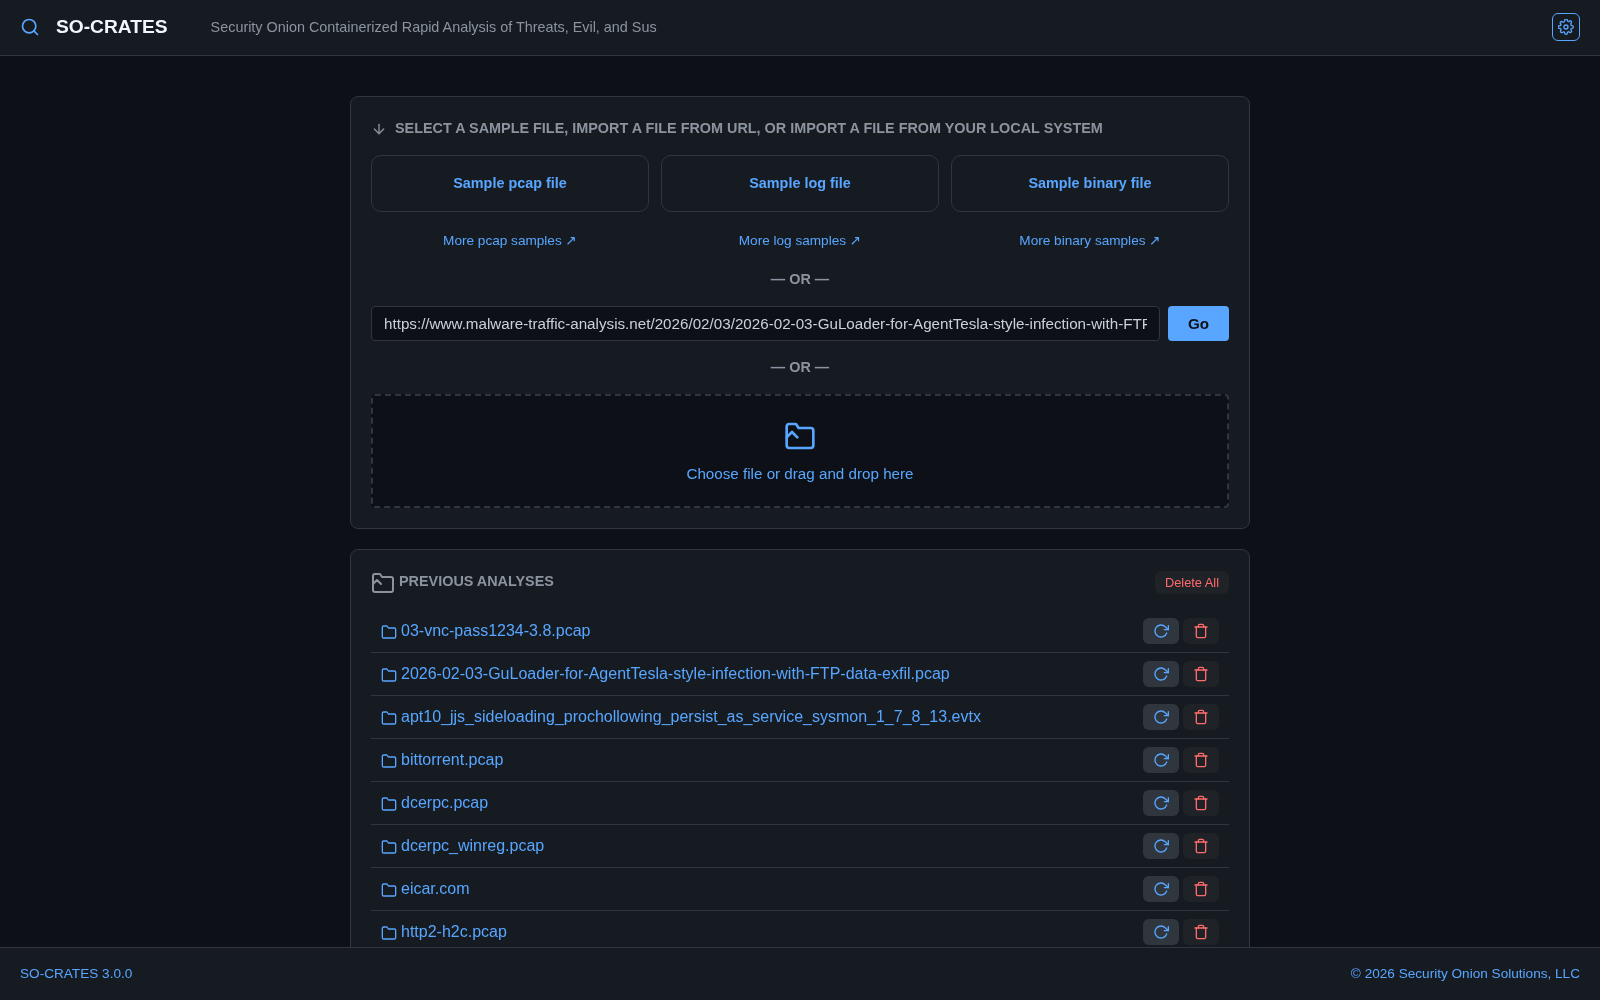
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

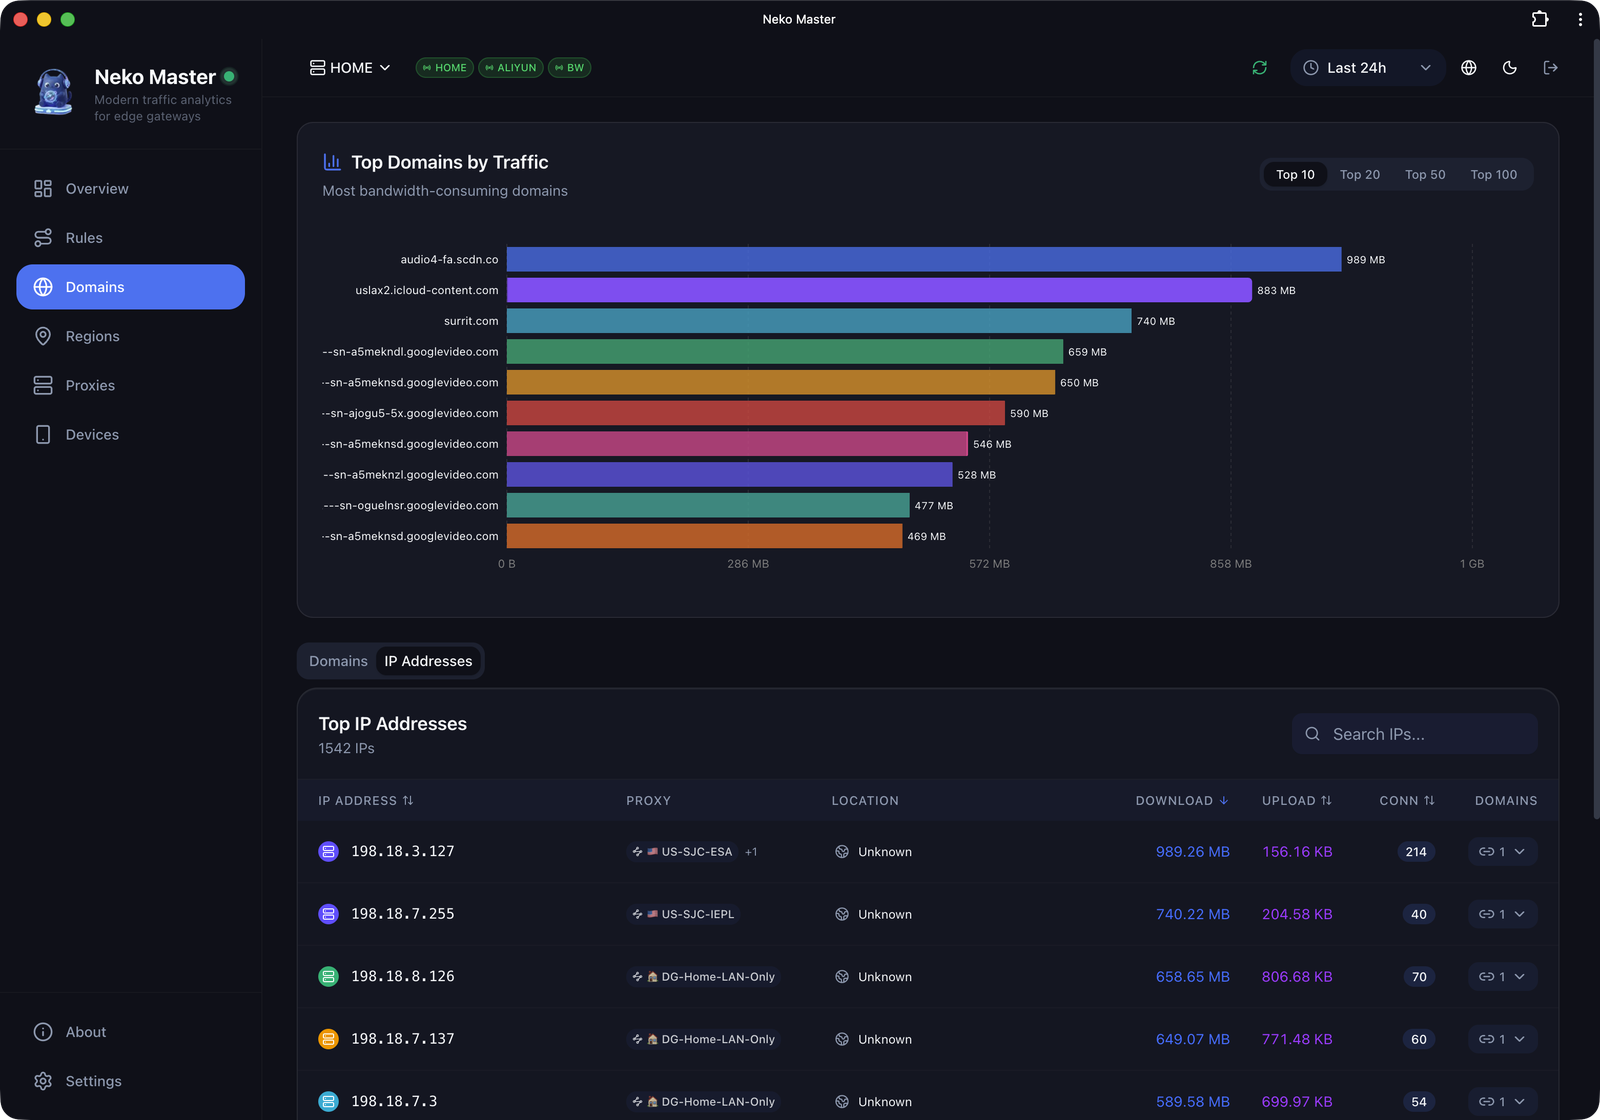
A modern and elegant dashboard for network traffic visualization and analysis.

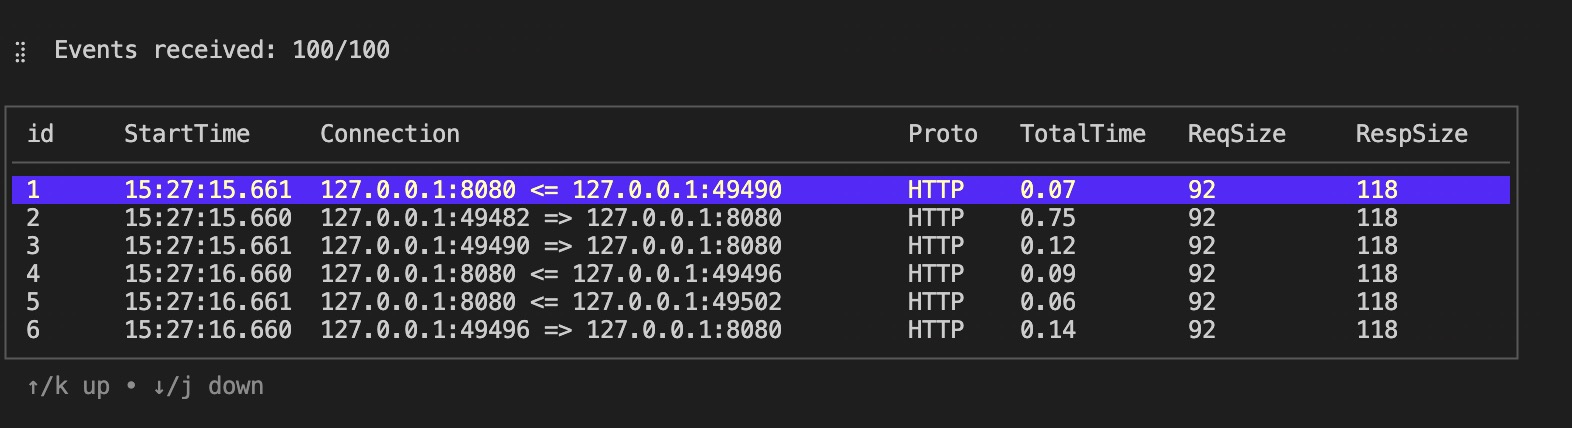
Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.

Advanced detection of port scanning, DoS and malware attacks using Machine Learning techniques

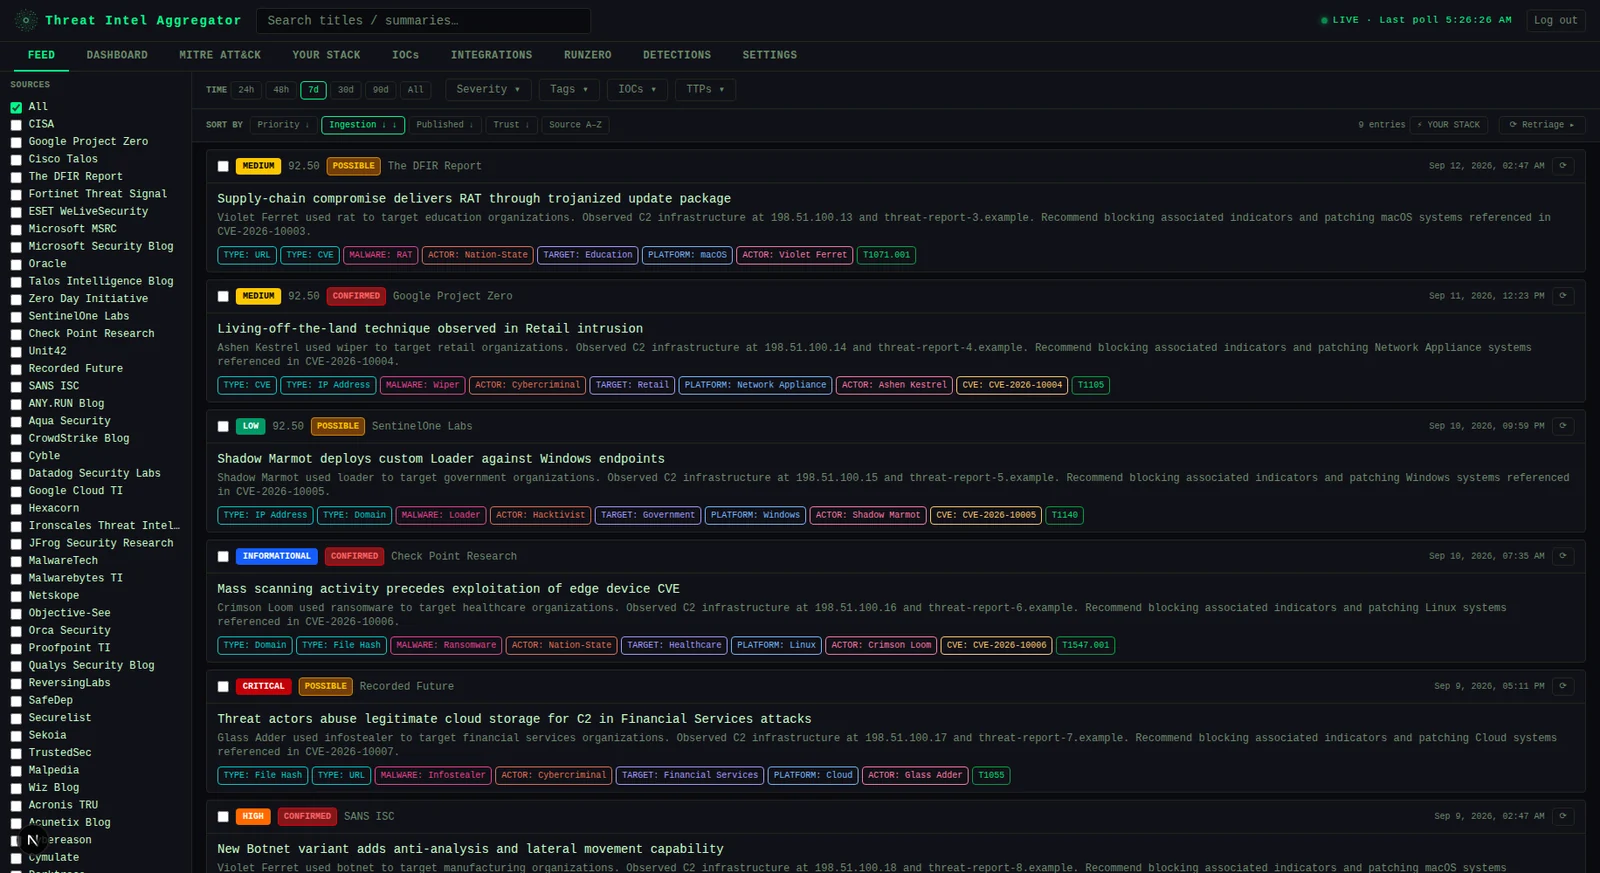
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…

Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…


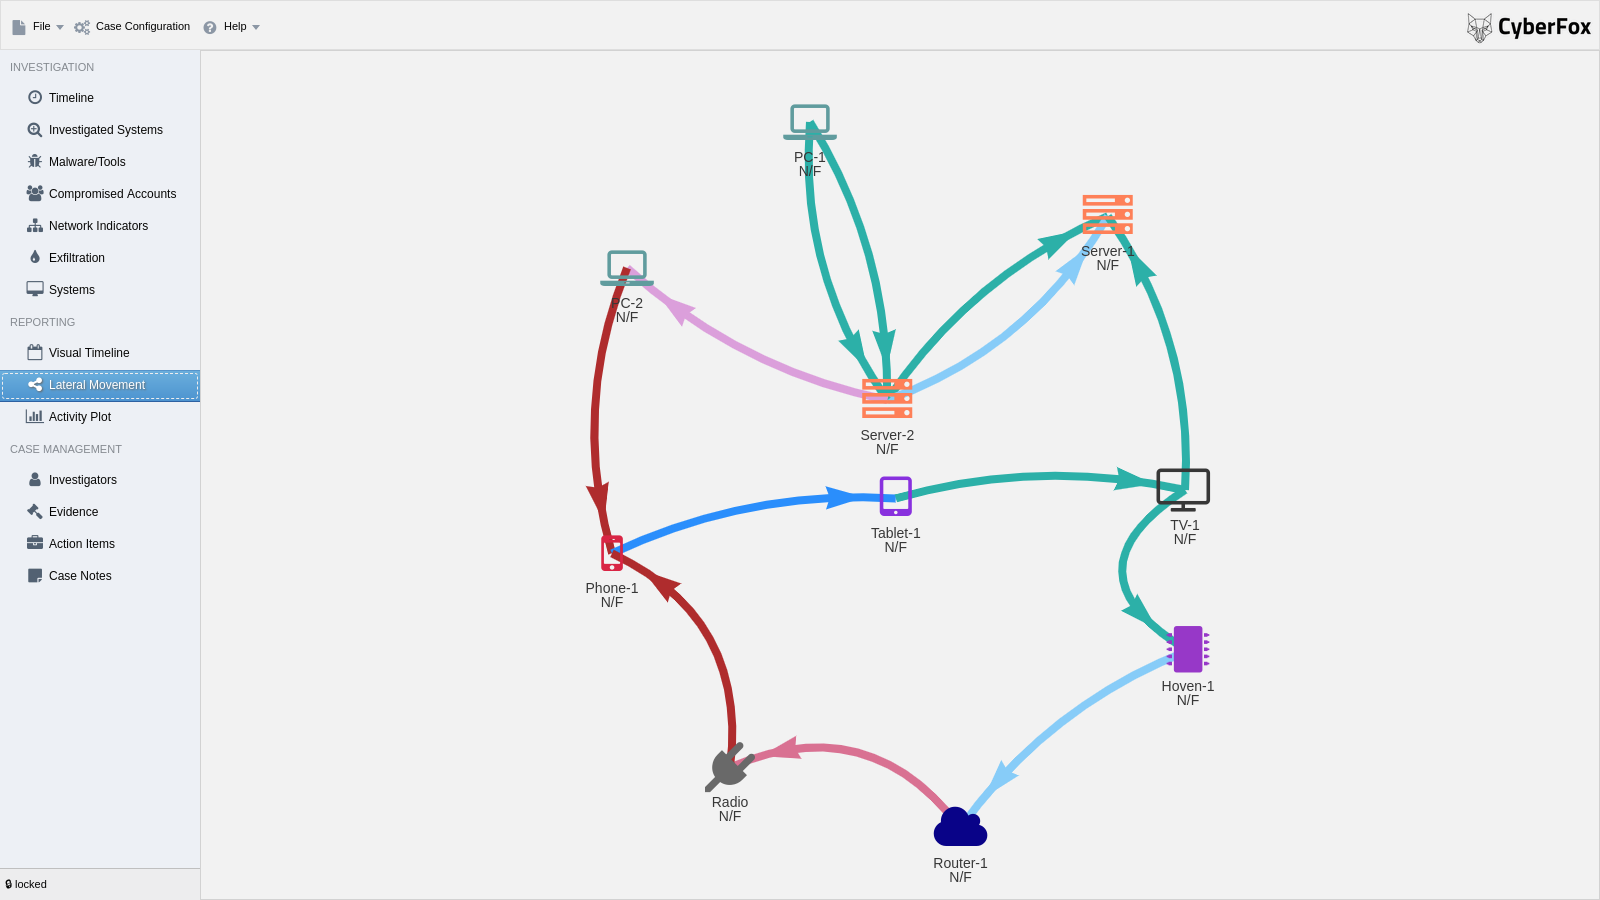
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders