

EntraTrace
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
authenticationcloud-securitydefensive-tools+5
bert-janp/entratraceDefensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 olafhartong/sysmon-modular
A repository of sysmon configuration modules
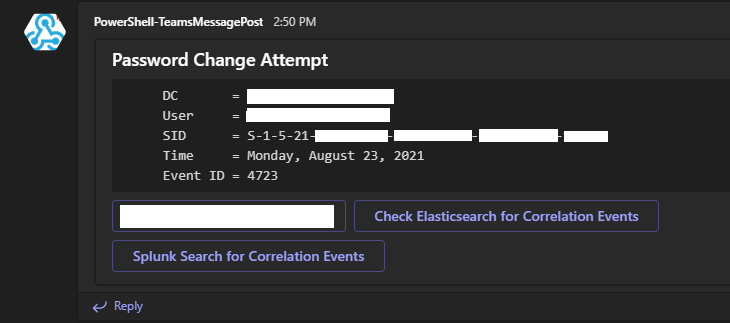 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
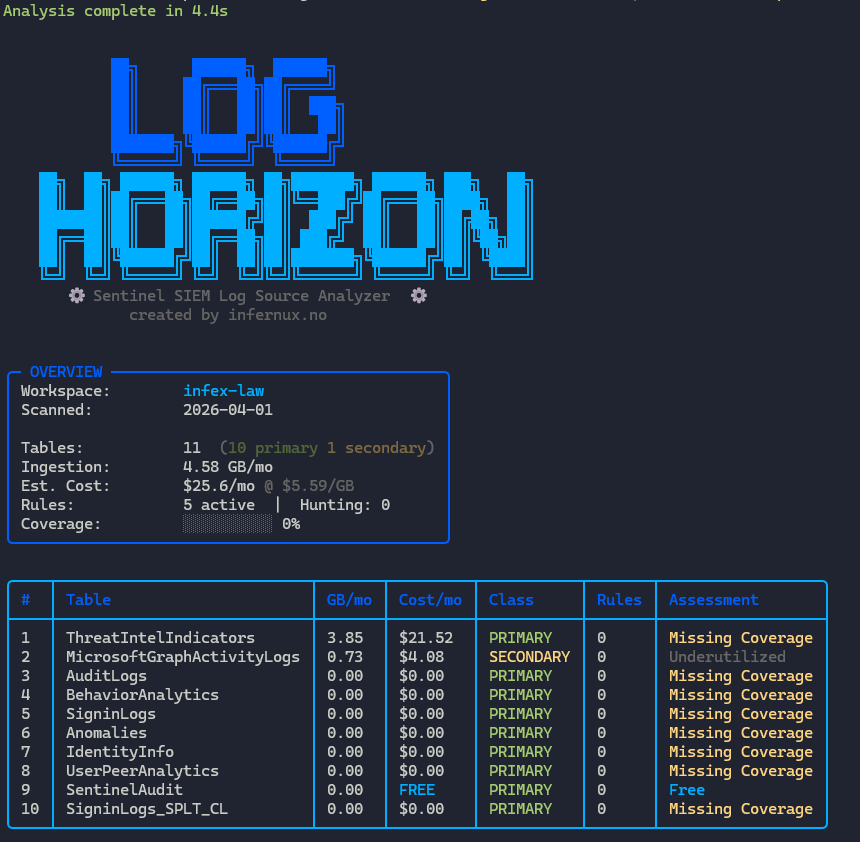 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 azure/azure-sentinel
Cloud-native SIEM for intelligent security analytics for your entire enterprise.
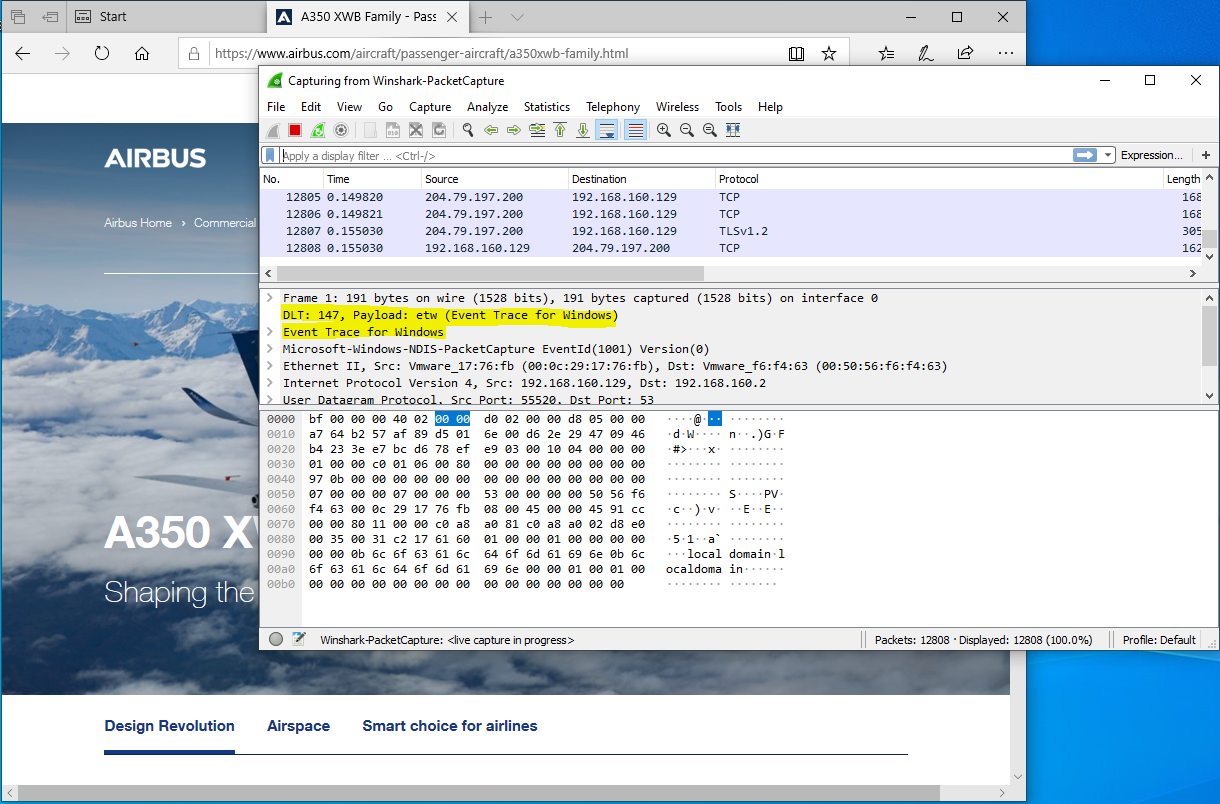 airbus-cert/winshark
A wireshark plugin to instrument ETW
 dobybaxter127/nimbus-vestige
A forensic reconstruction engine for cloud and identity incident response.
 chpratik/cve-2026-54121
Improper authorization in Active Directory Certificate Services (AD CS) allows an authorized attacker to elevate privileges over a network.
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
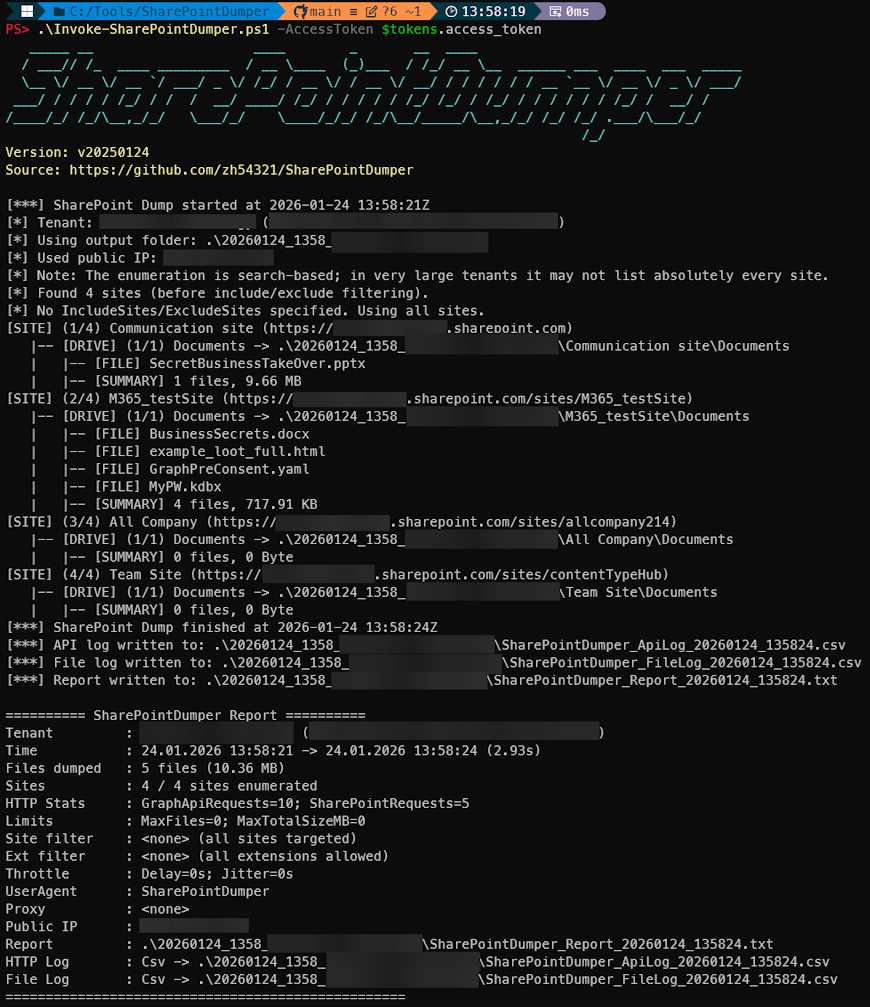 zh54321/sharepointdumper
PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…
 jangeisbauer/gundog
gundog - guided hunting in Microsoft Defender
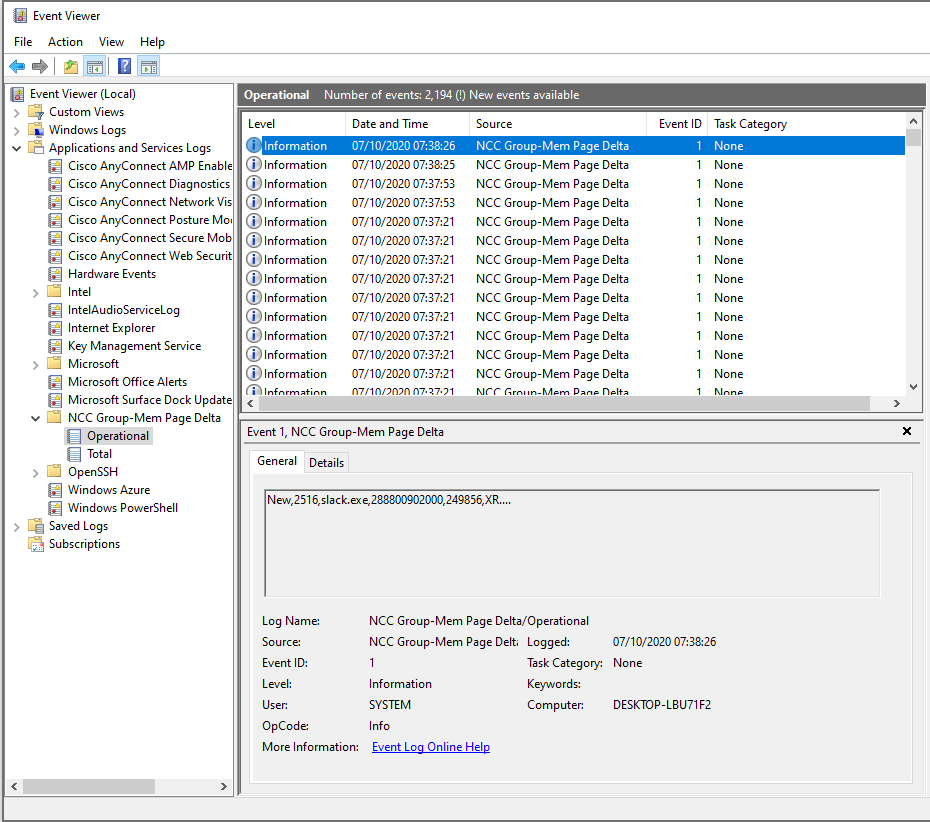 nccgroup/windowsmempagedelta
A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
 blacksnufkin/invoke-dumpmdeconfig
PowerShell script to dump Microsoft Defender Config, protection history and Exploit Guard Protection History (no admin privileges required )
 cyprianatsyor/letsdefend-cve-2022-41082-exploitation-attempt
Detailed incident report and educational analysis of CVE-2022-41082 (ProxyNotShell) exploitation attempt on Microsoft Exchange Server, including…
 maikelnight/zerologon
Check for events that indicate non compatible devices -> CVE-2020-1472