The Hitchhikers Guide to Online Anonymity

Comprehensive, open-source guide teaching online anonymity, OpSec, and identity protection techniques for activists, journalists, and…

Comprehensive, open-source guide teaching online anonymity, OpSec, and identity protection techniques for activists, journalists, and…

Centralized YAML-based knowledge base linking MITRE CWE, OWASP Top10, ASVS, and other security standards with versioned references. Includes MkDocs…

CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.

Structured online cybersecurity curriculum for educators, providing ready-to-use activities and resources to teach teens (13-18) about security…

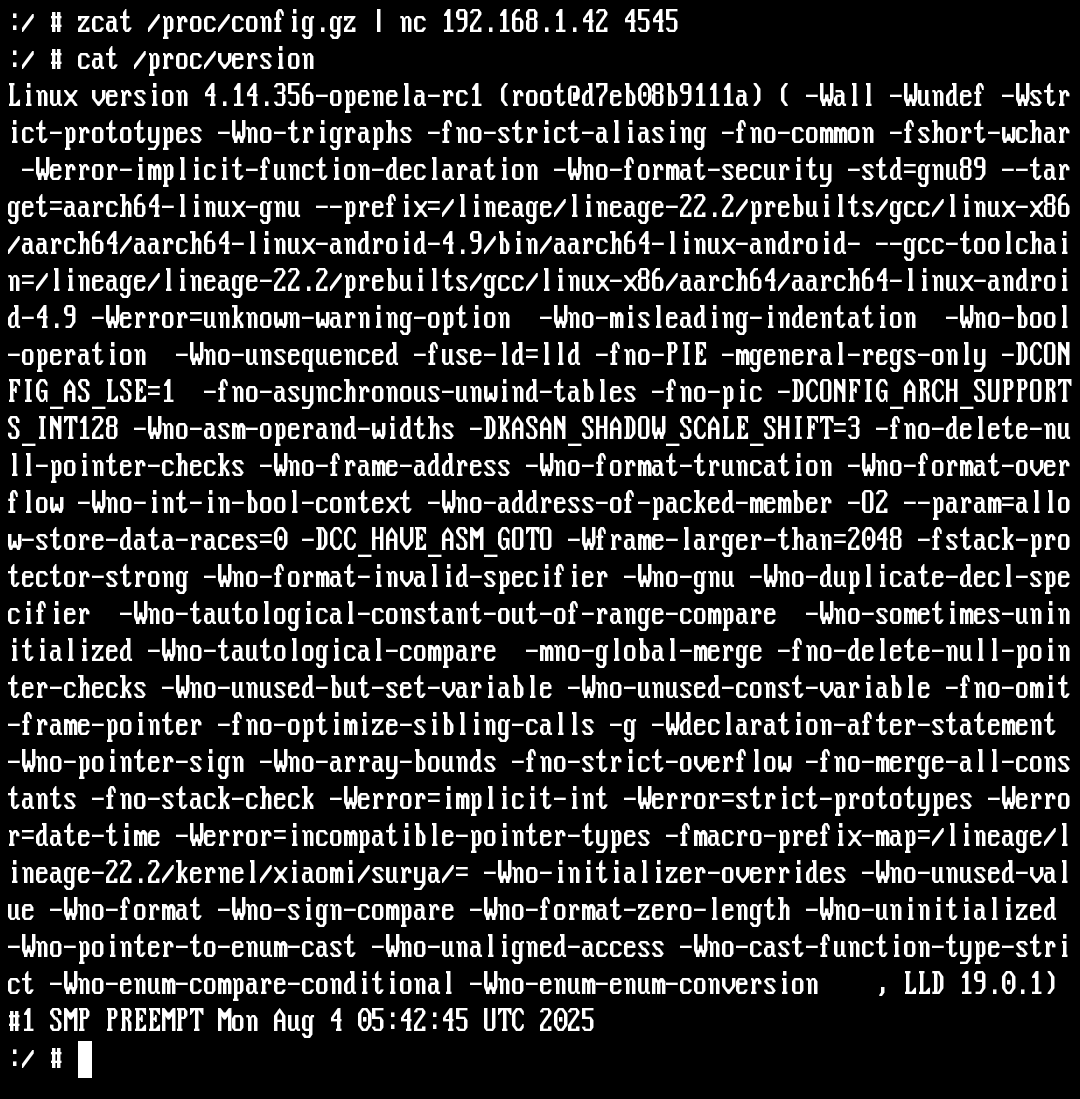
Step-by-step guide to building custom Kali NetHunter kernels for Android: source retrieval, toolchain selection, cross-compilation, and flashing.

Curated collection of Python scripts and tutorials for penetration testing, web security, and exploitation techniques, designed for security…

A Hacker's E-learning App for Tamil People

A free, open-source cybersecurity app for non techy people.

Curated bug-bounty methodology library with runbooks, recon/fuzz playbooks, checklists, and CLI helpers for target scoping, cert enumeration, and…

Slides for Developing Secure Software in 2024 at CanSecWest

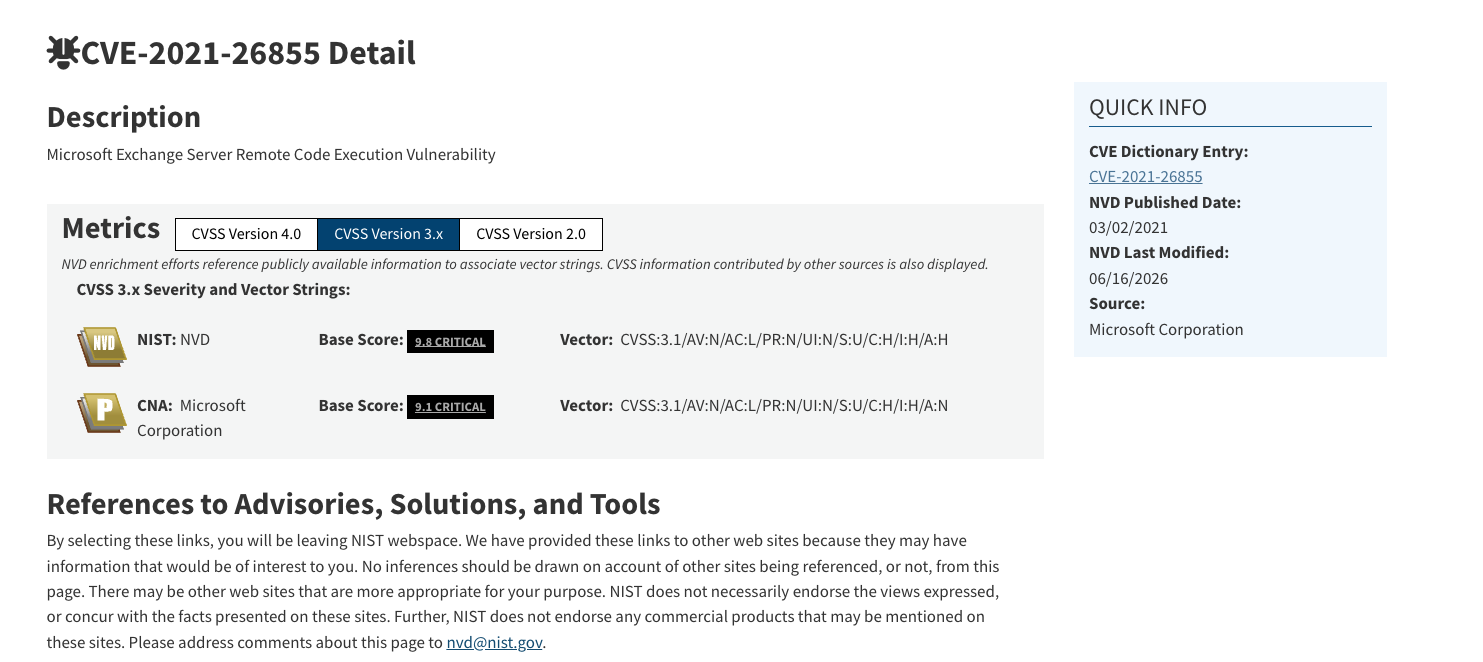
Hands-on CVE triage lab: analyze NVD entries, decode CVSS vectors, map CWE weaknesses, and contextualize risk for high-profile exploits like…

AI-powered CLI tool that reviews code for security vulnerabilities, bugs, and anti-patterns using LLMs. Supports local and cloud providers, git…

Lab materials and practice resources for OSCP certification preparation, including penetration testing exercises and hands-on security training…

Structured evaluation criteria framework for assessing Web Application Firewalls (WAFs), enabling users, vendors, and third parties to compare…

AngularJS 1.x -> Angular 18 migration guidance for GitHub Copilot. Source-of-truth repo for…

OWASP teaching modules covering application security fundamentals including risk management, secure software development, and operations security for…

Intentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…